
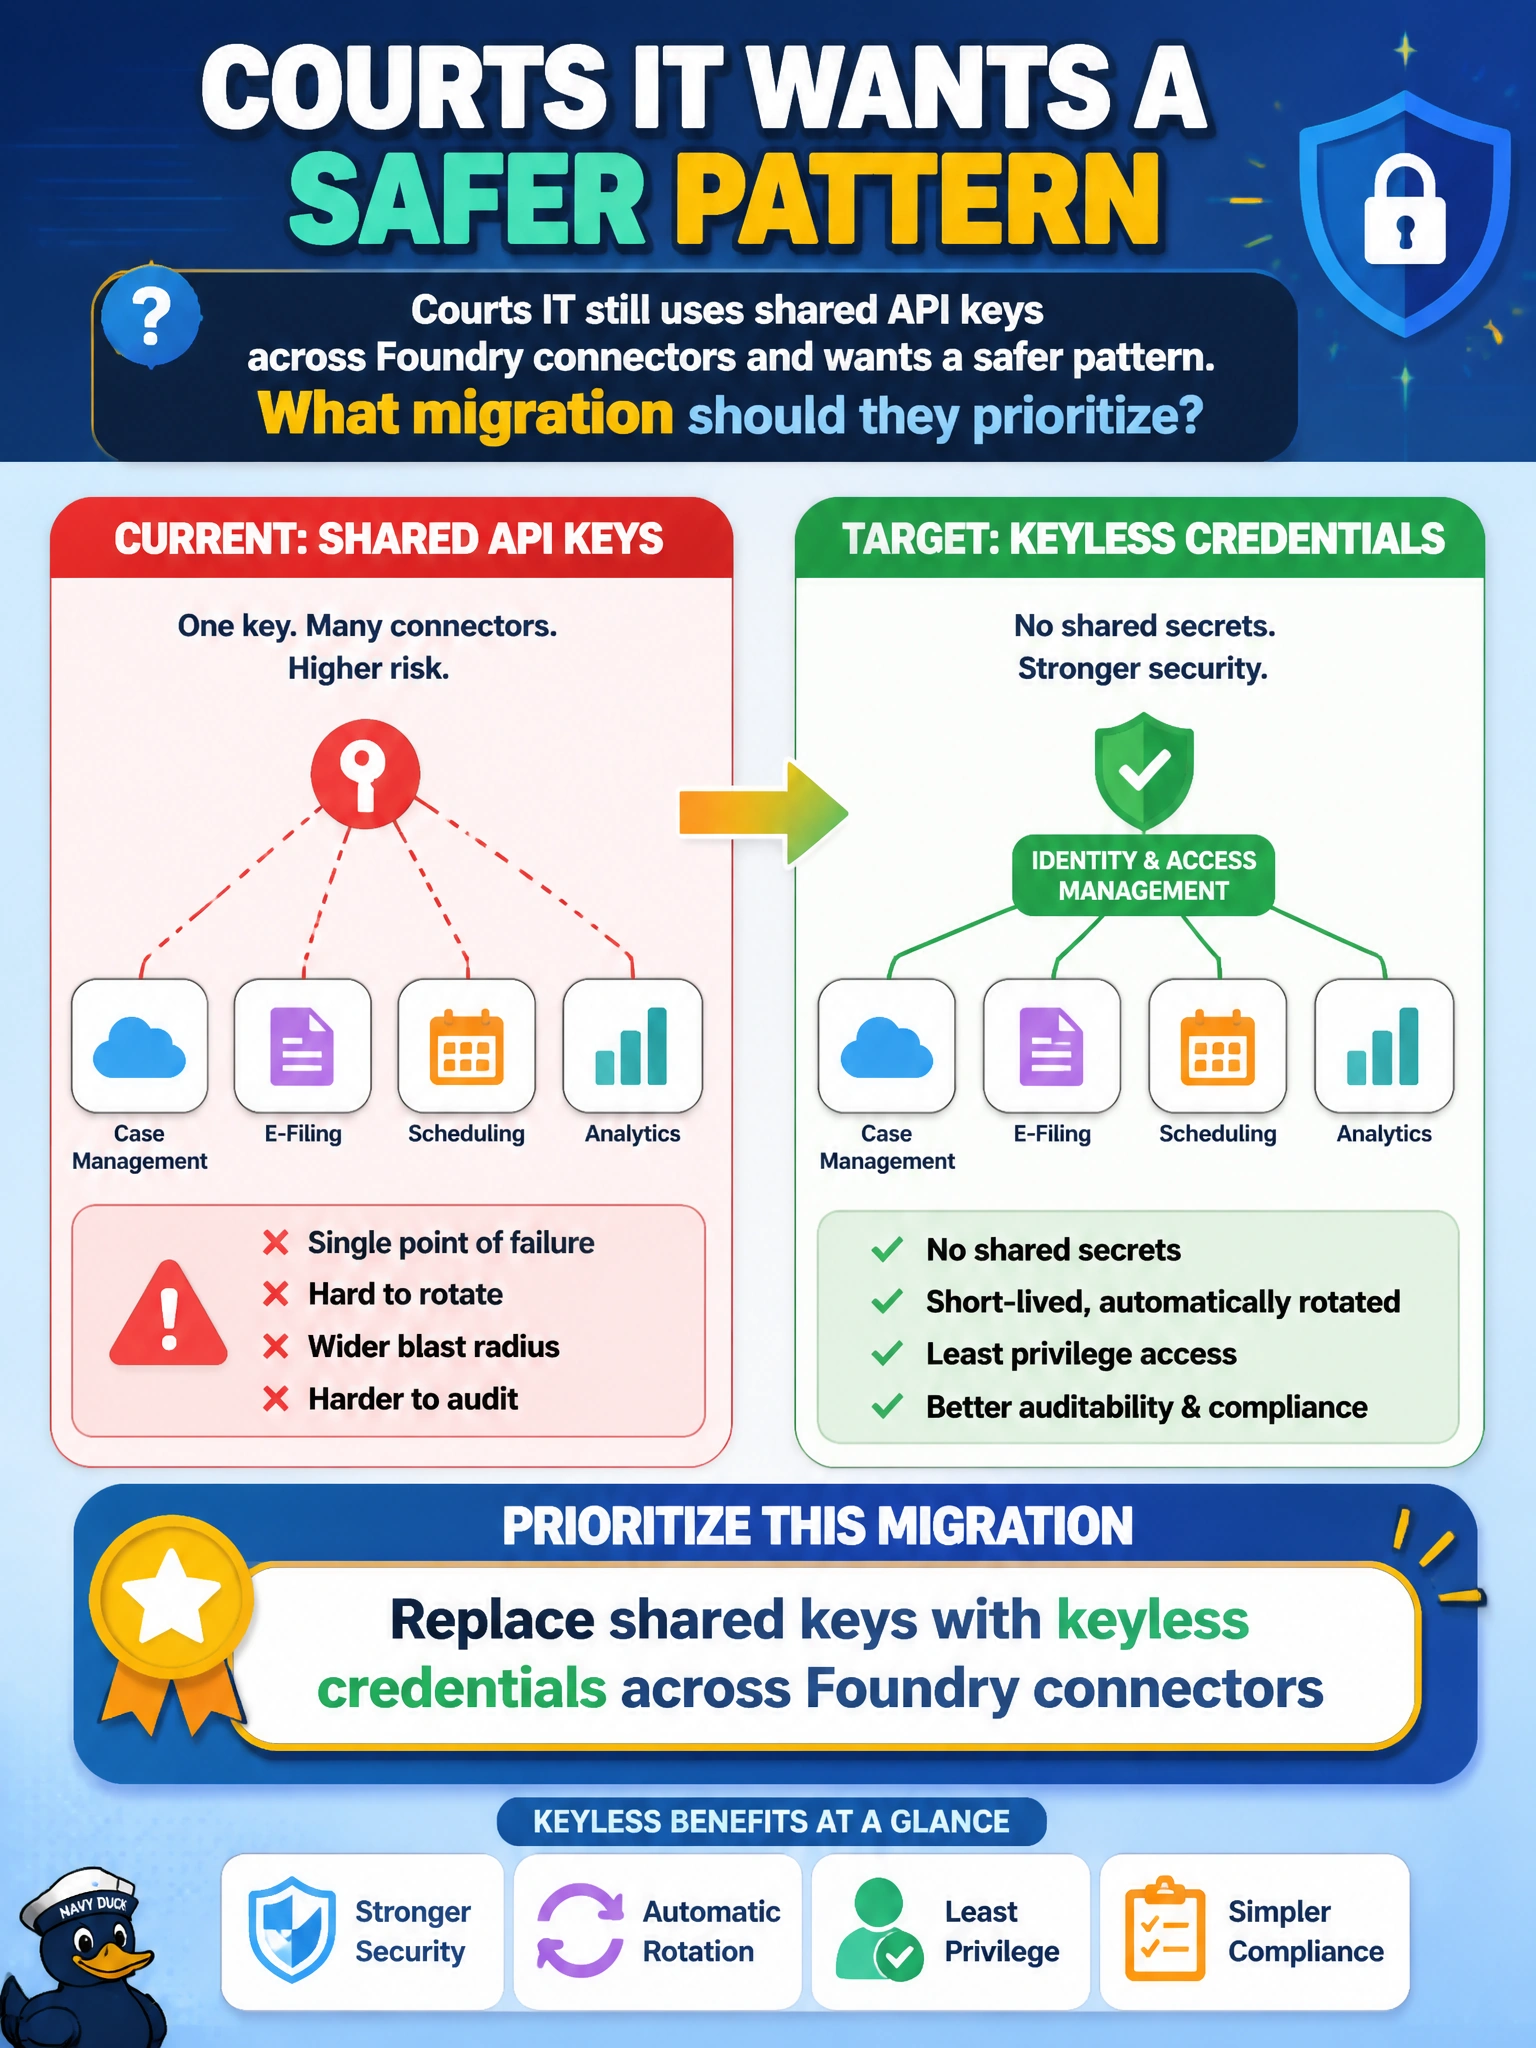
Courts IT still uses shared API keys across Foundry connectors and wants a safer pattern. What migration should they prioritize?
Select an answer to reveal the explanation.
Short Explanation
Shared keys bouncing between connectors are like one master courthouse key left under the mat. Move Foundry connectors to keyless credentials so identities, not copied secrets, open the doors. Rotation and audit get saner for courts IT overnight.
Full Explanation
Courts IT should prioritize replacing shared API keys with keyless credentials across Foundry connectors so authentication uses managed identities or equivalent token-based patterns instead of long-lived shared secrets. The migration works because keyless credentials are issued per workload identity, support RBAC attribution, and remove the need to distribute and rotate static keys among connectors that touch court data. Reducing shared-key coupling is a foundational security improvement for municipal Foundry integrations.
Enabling automated key rotation in Key Vault for Foundry connectors fails the stated goal because the connectors still depend on a shared static secret between rotations, so copied keys, stale configs, and distribution risk persist—only the rotation is automated in the vault, not the underlying credential model. Provisioning separate API keys for Foundry connectors in Key Vault with RBAC fails the migration goal because each connector still relies on a static secret rather than a keyless identity, so vaulting improves storage but secret distribution risk remains without per-workload identity attribution. Centralizing Foundry connector secrets in Key Vault with access policies fails the migration goal because a centrally stored secret is still one shared static credential handed to every connector—secure storage with policies does not replace the need for per-workload keyless identities and RBAC attribution the courts system requires.
Exam caveat: connector migration must be staged—mixed key and identity modes can leave orphan keys still valid after teams believe they are done. Operational check: inventory Foundry connectors still using keys, migrate each to managed identity, revoke old keys, confirm apps function, and add policy or scanner checks that fail builds when new static keys are introduced.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.