
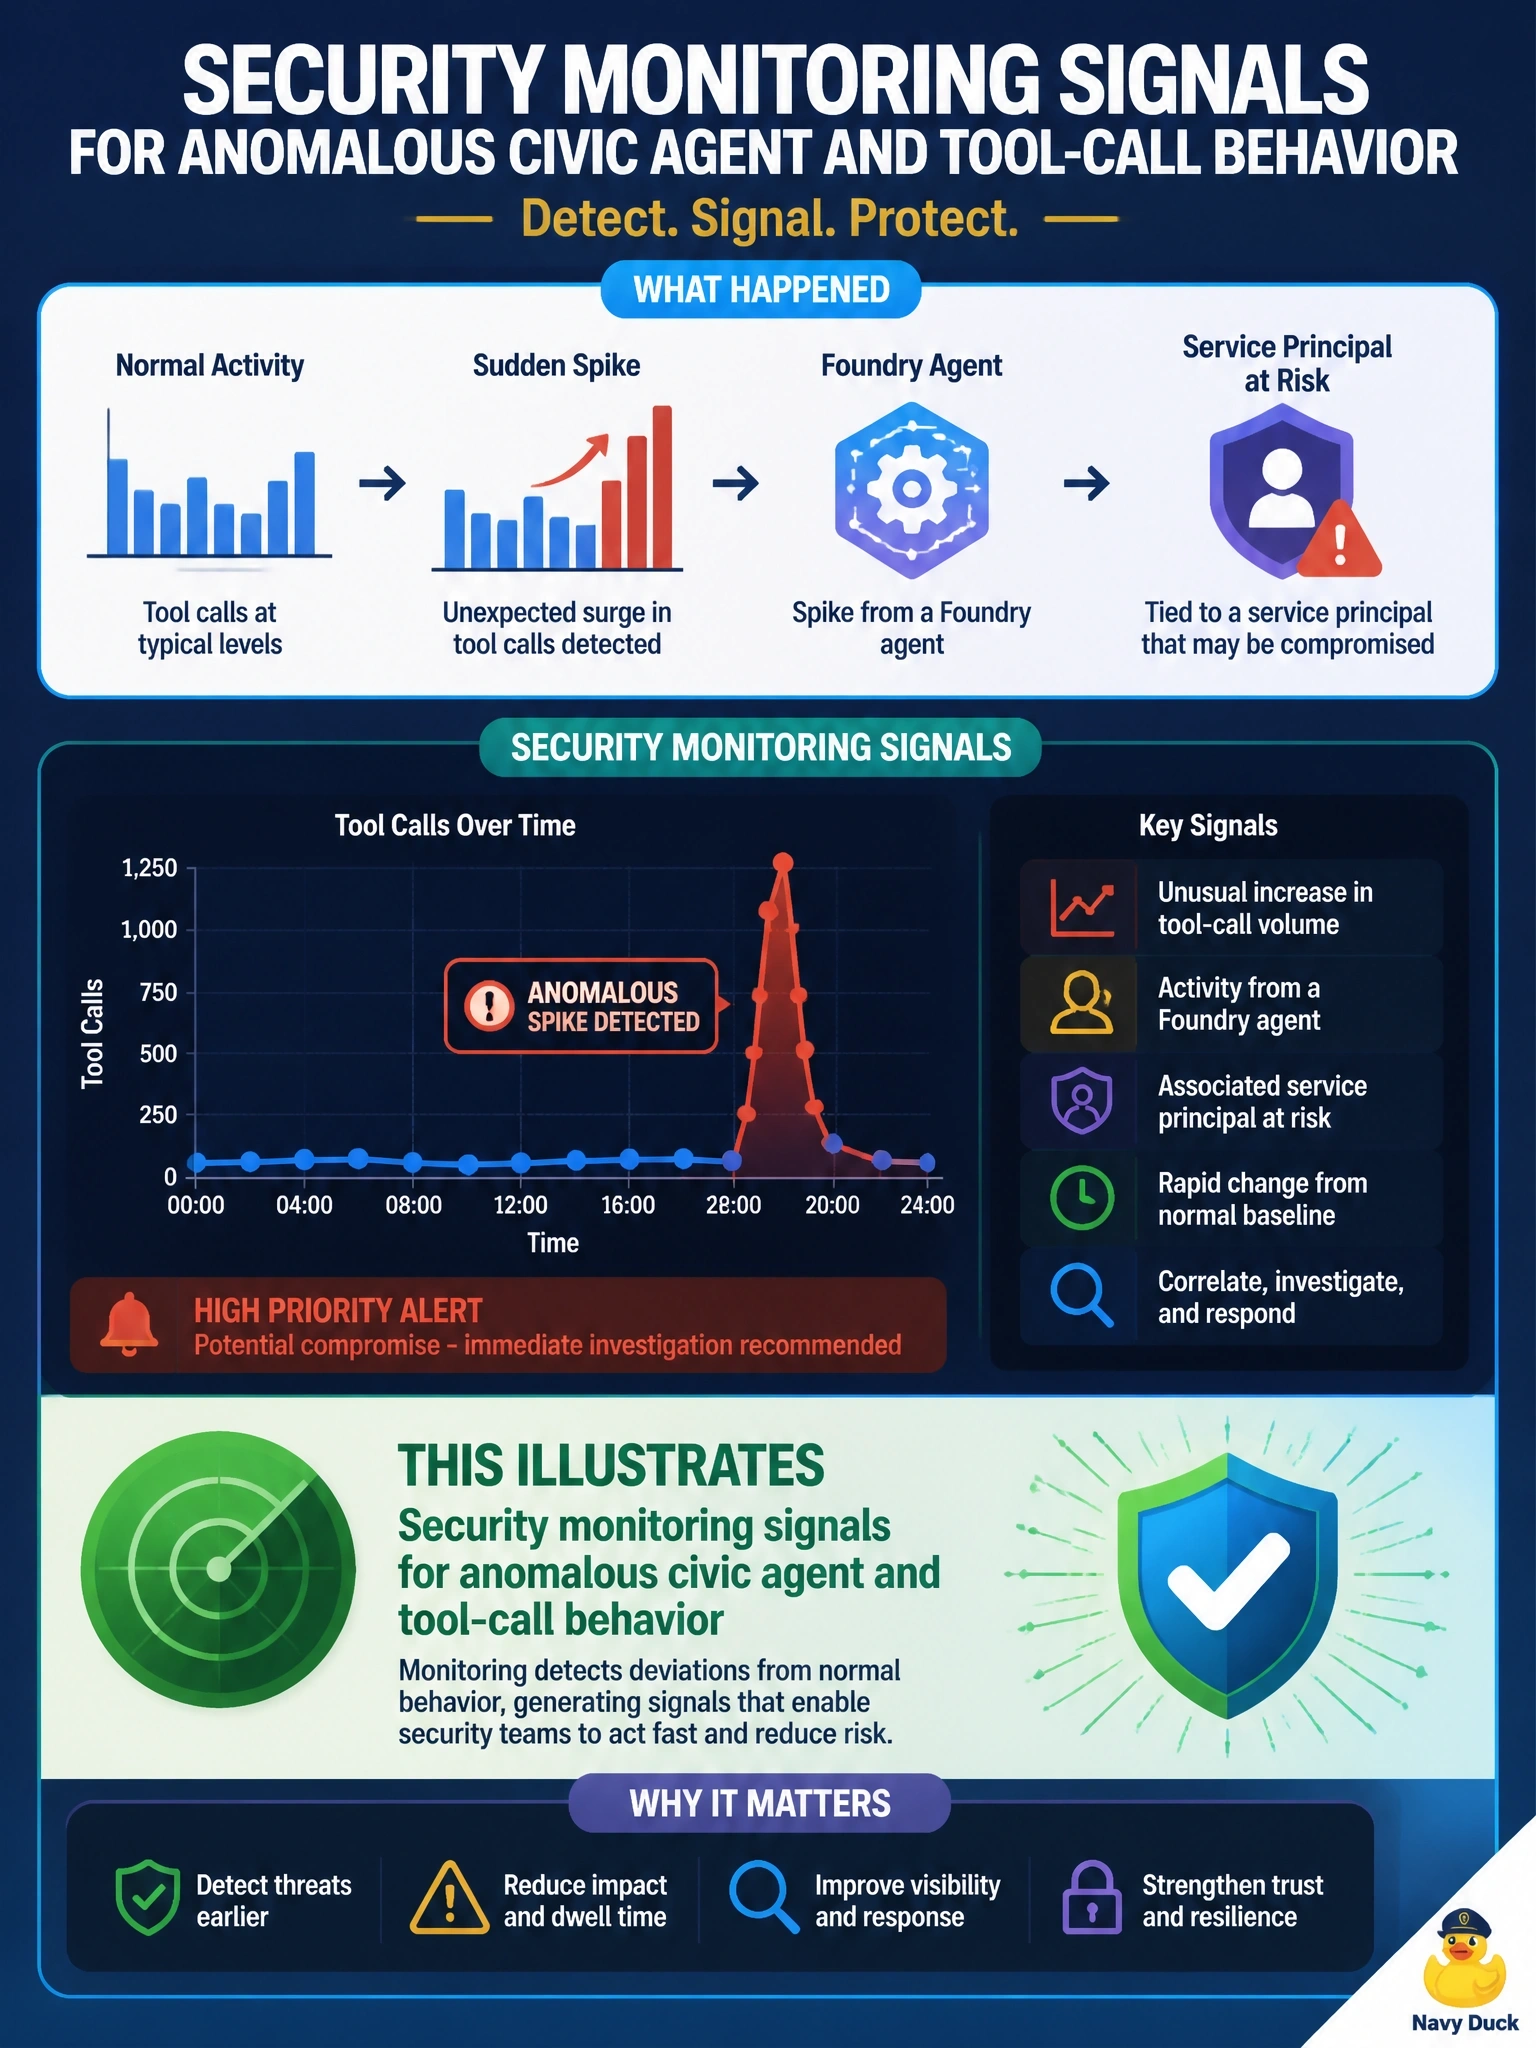
A city SOC sees a sudden spike in tool calls from a Foundry agent tied to a service principal that may be compromised. What capability does this illustrate?
Select an answer to reveal the explanation.
Short Explanation
This weird surge of tool calls is the digital equivalent of hearing footsteps in city hall after hours. Security monitoring on agent workloads flags odd volumes and identities so you'll know to investigate. Catching one wonky service principal early beats cleaning up after it empties the tool cabinet.
Full Explanation
This sudden spike in tool calls from one Foundry agent tied to one possibly compromised service principal illustrates security monitoring signals for anomalous civic agent and tool-call behavior. This capability works because municipal agents act through identities and tools; volume, destination, and identity anomalies are early indicators of credential misuse, prompt-driven tool abuse, or automation gone wrong. Security operations center visibility into those signals enables investigation, credential revocation, and containment before the agent becomes one privileged pivot across city systems. Service principal sign-in log review for interactive user authentication events fails because agent service principals authenticate non-interactively, not via interactive user logins; reviewing interactive authentication events will not reveal tool-call volume or destination anomalies and cannot provide the near-real-time agent behavior signal needed for investigation. Foundry content filter logging for civic prompt injection attempt detection fails because content filtering monitors prompt and completion text for injection or policy violations, not tool-call behavior; it cannot detect an anomalous spike in tool calls from a compromised service principal in time to stop misuse. Tool access allowlist enforcement for approved civic API operations control fails because an allowlist is a preventive control restricting which APIs may be called, not a monitoring signal; it cannot identify or alert on an anomalous spike in calls to approved tools from a compromised service principal quickly enough to enable containment. Exam caveat: volume spikes can also be buggy loops or legitimate batch jobs; correlate with change windows and require identity context before automatic containment. Operational check: forward Foundry/agent tool-call and Entra ID sign-in logs to the security operations center, alert on abnormal rates per principal, maintain one break-glass revoke procedure, and periodically verify that sensitive tools such as payroll and HR writes are not reachable from agents that should never call them.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.