
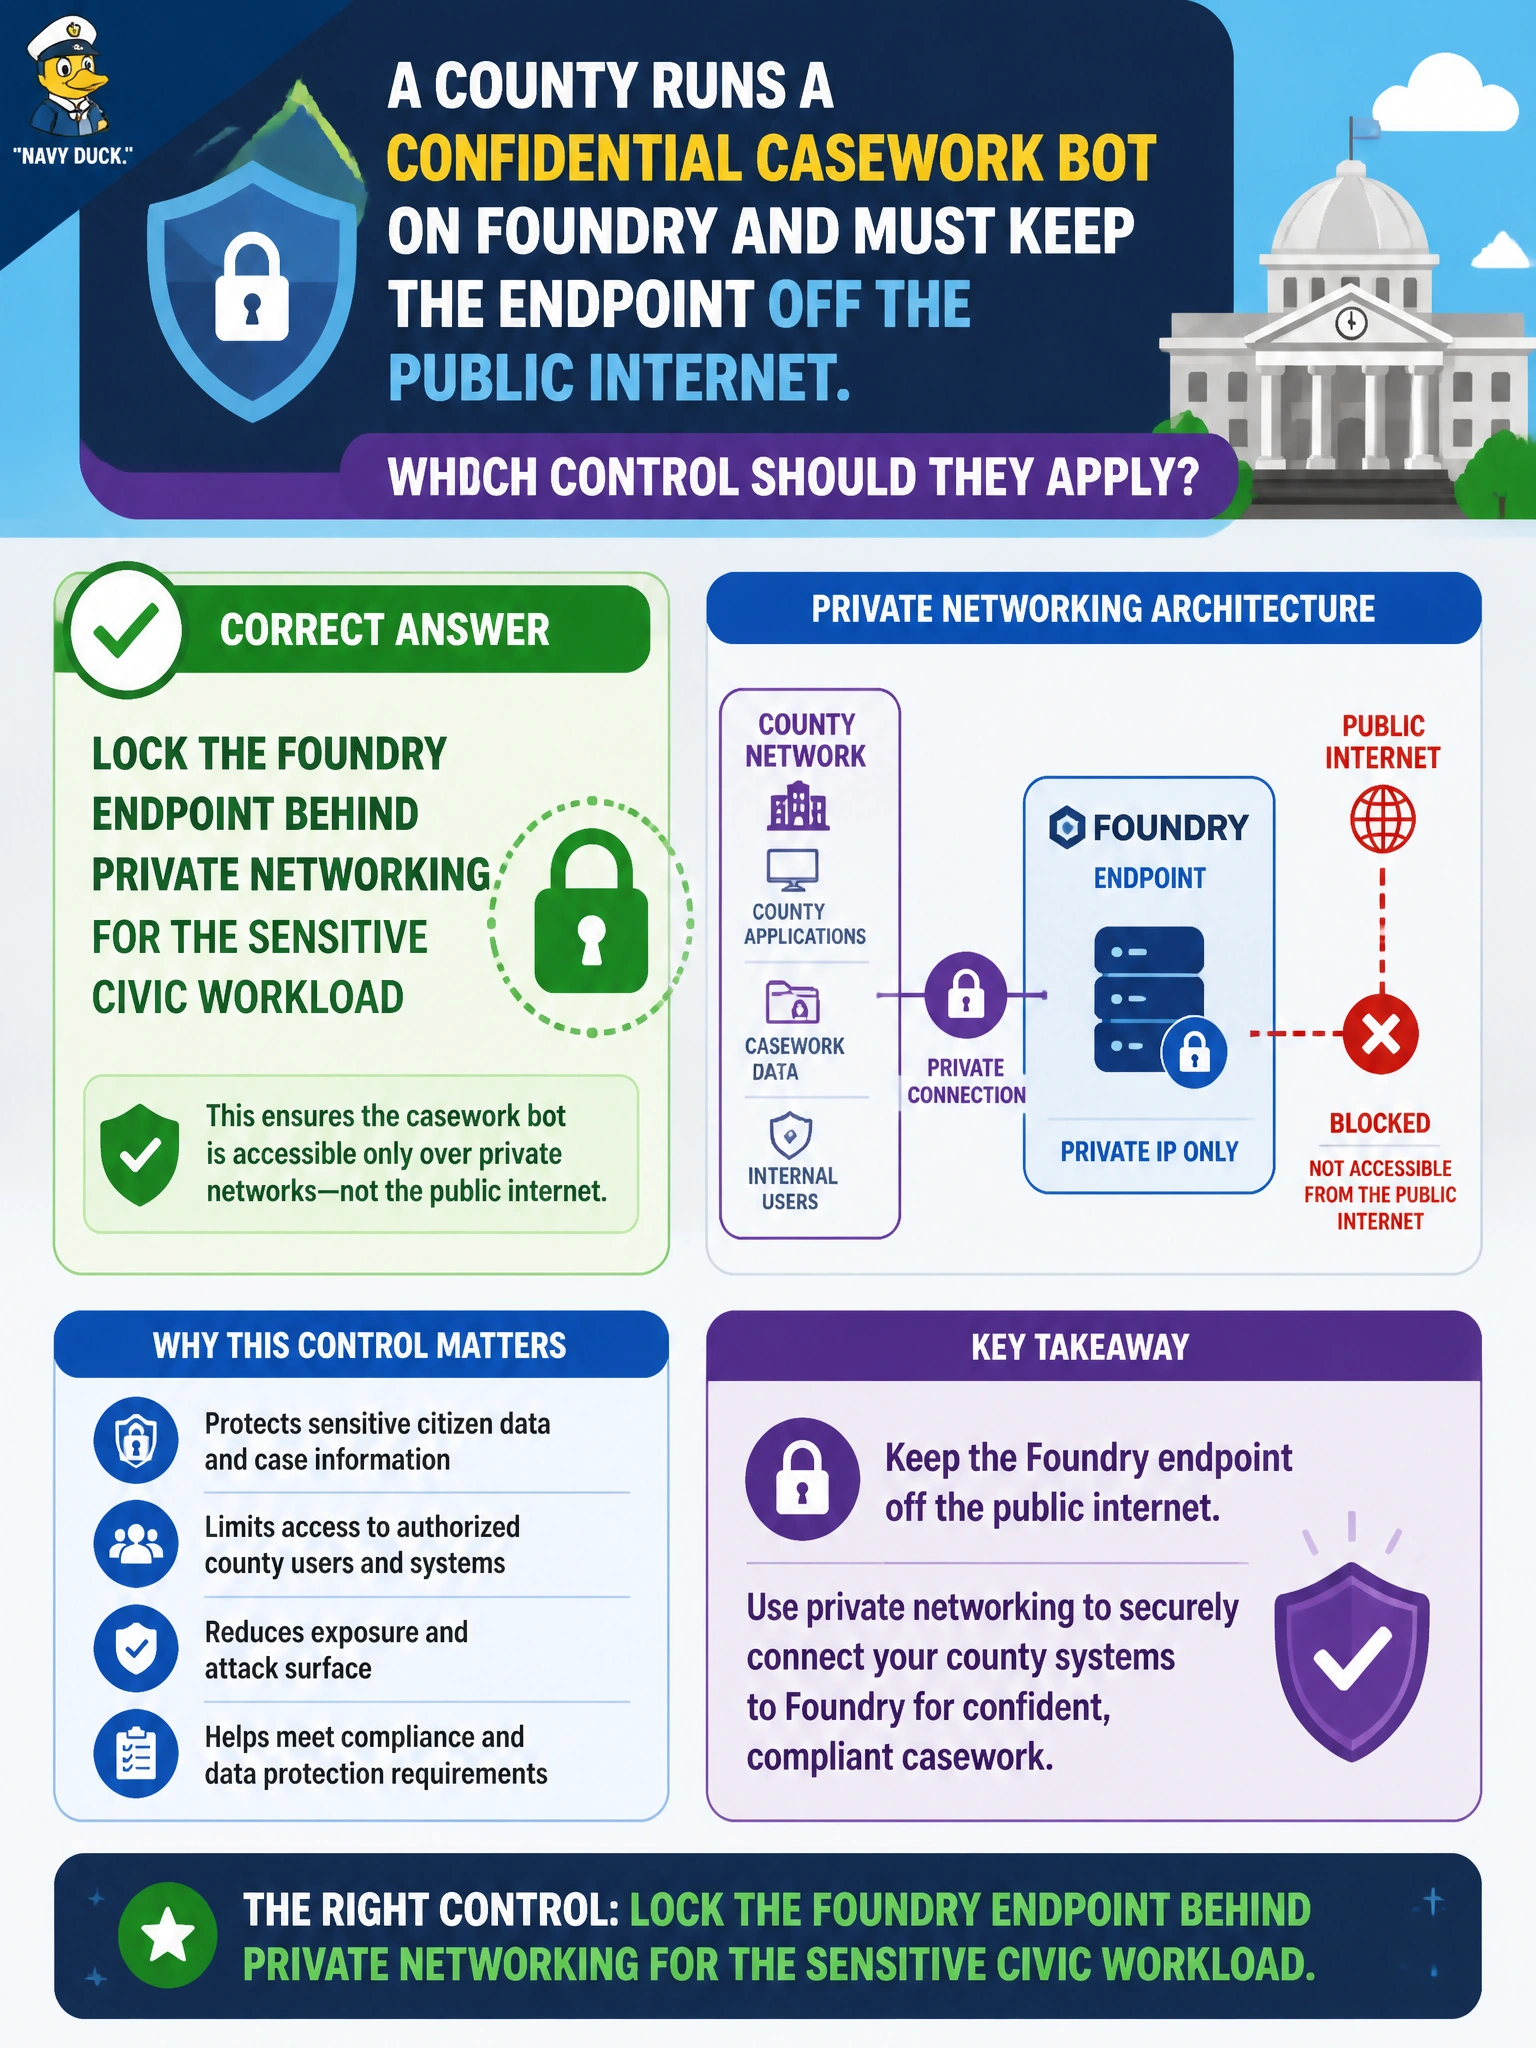
A county runs a confidential casework bot on Foundry and must keep the endpoint off the public internet. Which control should they apply?
Select an answer to reveal the explanation.
Short Explanation
Confidential casework does not belong on a billboard. Putting the Foundry endpoint on private networking keeps only trusted county networks talking to it. That is the difference between a locked evidence room and a kiosk in the lobby.
Full Explanation
For a confidential casework bot, locking the Foundry endpoint behind private networking keeps the sensitive civic workload off the public internet while allowing authorized county networks and services to connect. The control works because private networking (private endpoints, restricted public network access, private DNS) confines the model endpoint to trusted paths appropriate for confidential resident and case data, aligning with government security expectations for non-public AI services. Exposure reduction is a primary design requirement when the content itself is confidential—not merely “internal convenience.”
Isolating the Foundry build compute in a managed VNet for the sensitive civic workload fails because it confines training and build compute, not where the serving endpoint is reachable—the deployment can still sit on the public internet, which is exactly the exposure a confidential casework workload cannot carry. Allow-listing the Foundry endpoint by client IP ranges for the sensitive civic workload fails because IP rules only limit which public clients can connect, not whether the endpoint is on the public internet—the casework workload still needs private networking to keep that path off the open internet entirely. Securing the Foundry data dependency with Private Link for the sensitive civic workload fails because private connectivity to storage or supporting data protects those dependencies, not the network path to the endpoint itself—the endpoint can still be publicly reachable, which is the exposure private networking is meant to remove.
Exam caveat: private networking must cover all related resources the bot calls (storage, search, keys) or data still egresses through public sibling endpoints. Operational check: disable public network access where policy requires it, validate private endpoint connectivity from the casework VNet, deny anonymous access, and penetration-test that the Foundry endpoint is unreachable from the public internet.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.