
A county assessor's office explains activity explorer to auditors as a Purview reporting surface. What should that explanation emphasize?
Select an answer to reveal the explanation.
Short Explanation
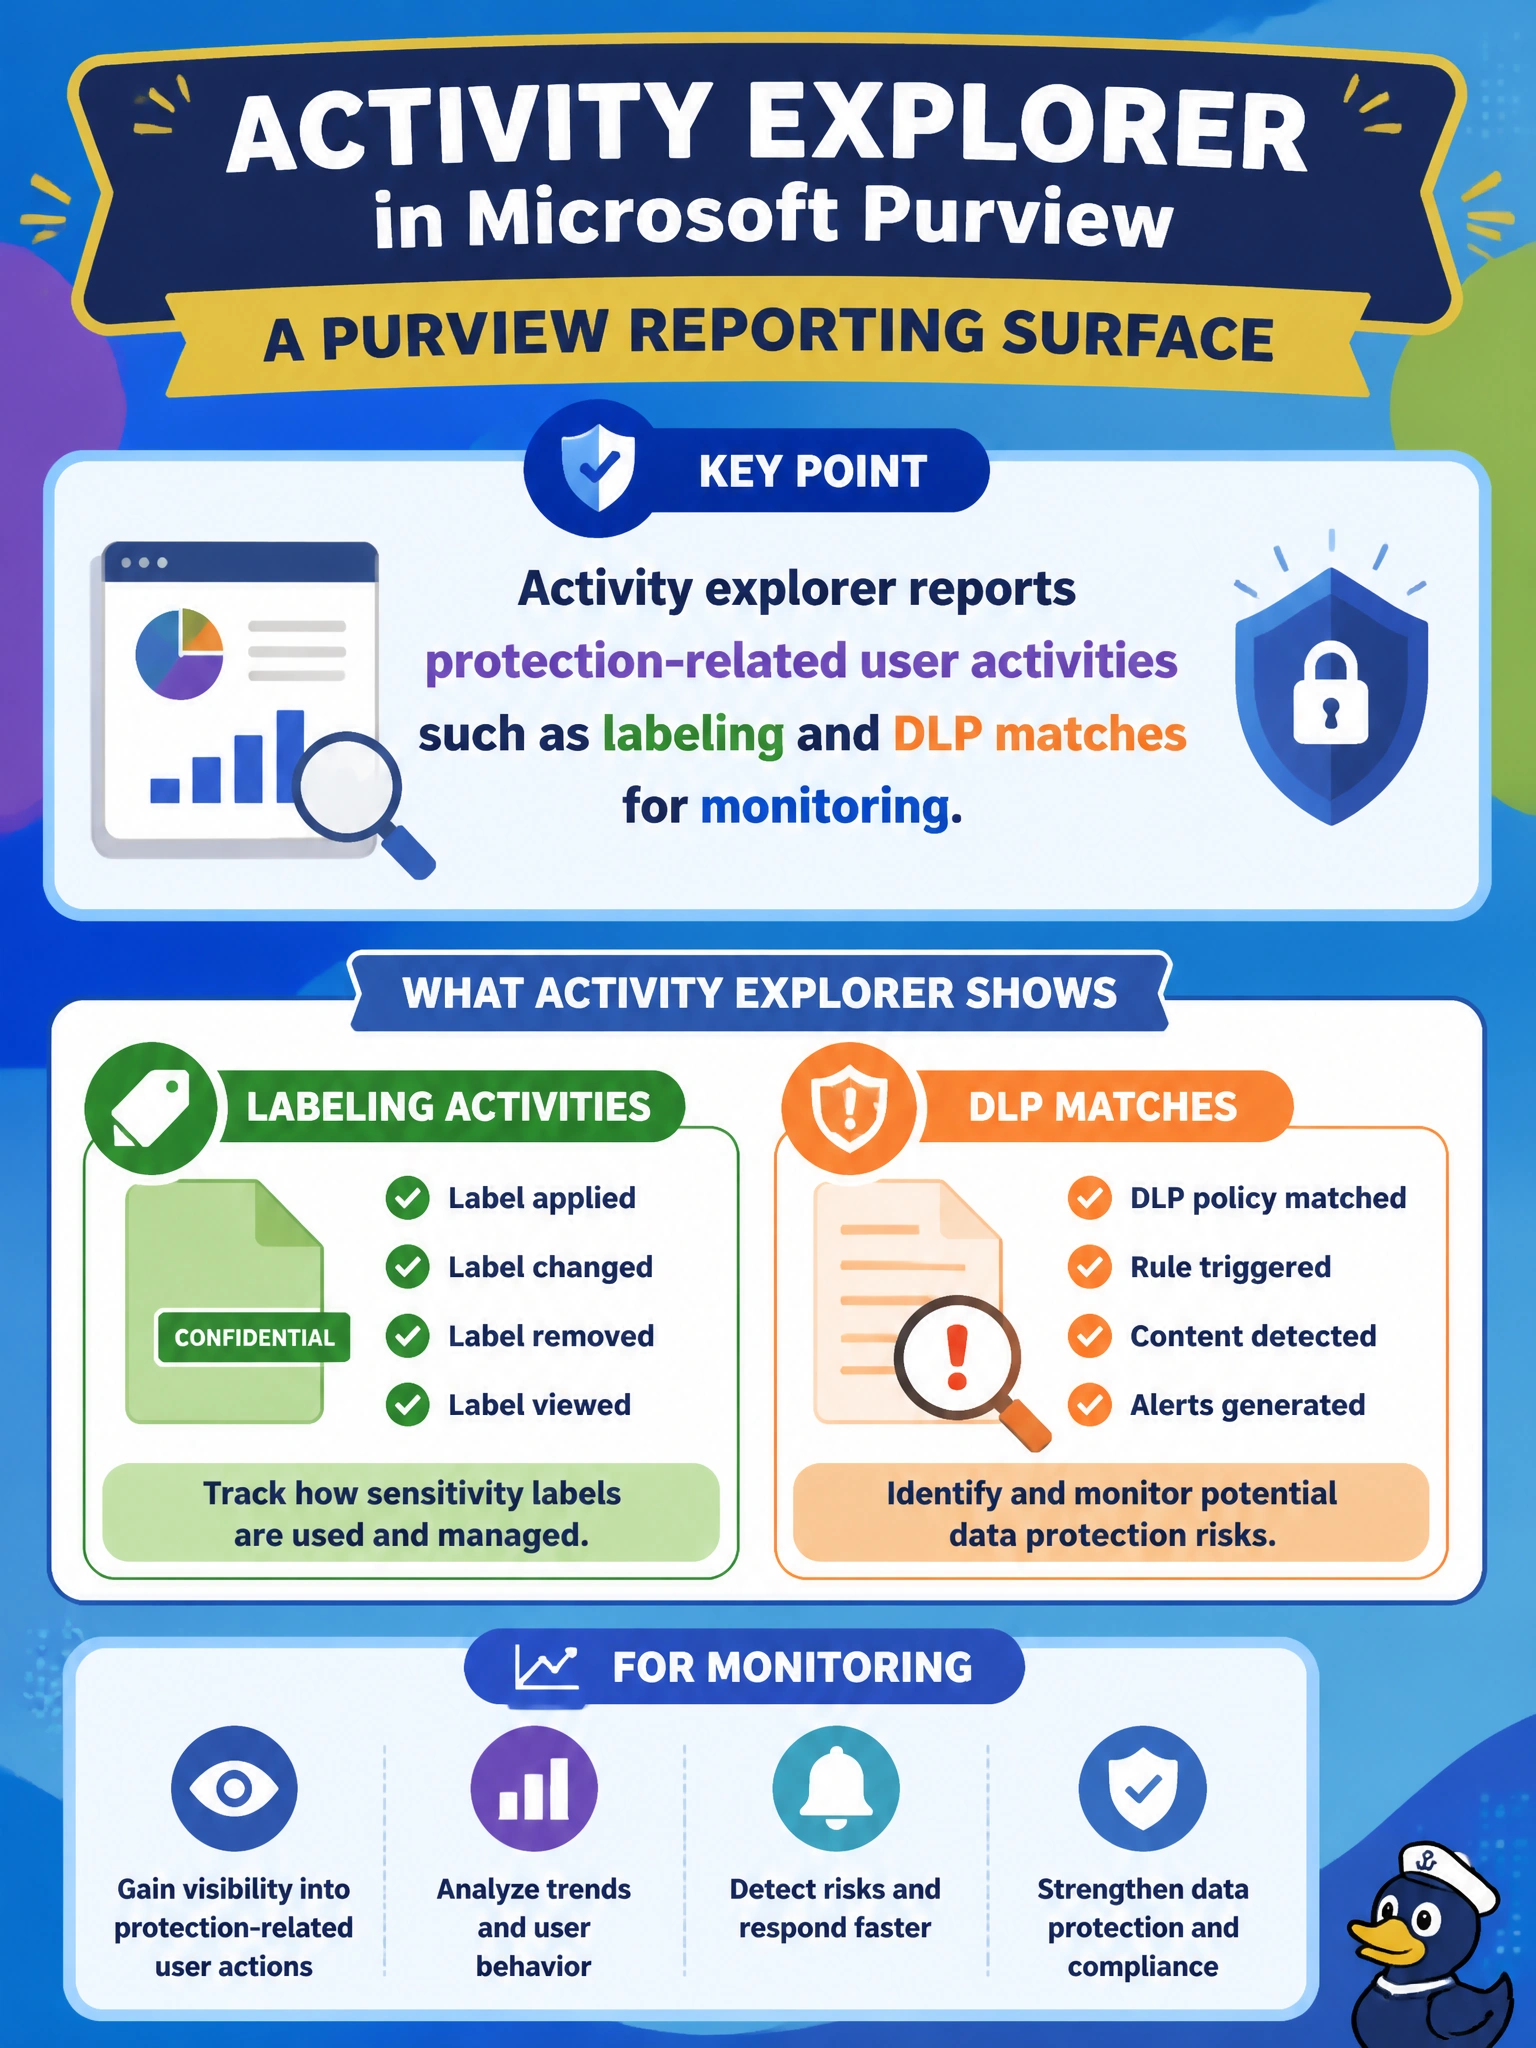
You use activity explorer as the scoreboard for labeling and DLP match activity—not to report labeled content distribution across sites and mailboxes, insider risk signals like exfiltration, or eDiscovery hold operations like custodial holds. It's a reporting tool, so you'll focus on monitoring what users did, not planning coverage or running other Purview reviews.
Full Explanation
When a county assessor’s office briefs auditors, the accurate explanation is that activity explorer reports protection-related user activities—such as sensitivity labeling and DLP matches—so monitoring and investigation teams can see how staff interact with protected municipal records. It is a Purview risk-identification and visibility experience, not a labeled content distribution planner across sites and mailboxes, an insider risk signal reviewer, or an eDiscovery hold operations reporter. That framing matches what auditors need when they ask how the county proves who touched labeled assessor data.
Activity explorer does not report labeled content distribution across locations such as sites and mailboxes for planning; it surfaces individual protection-related user activities such as labeling and DLP matches, while location-based distribution is reviewed in Content explorer. Activity explorer does not report insider risk user signals such as exfiltration and sequence anomalies for review; it reports protection-related user activities after access, while exfiltration and anomaly sequences are reviewed in Insider Risk Management. Activity explorer does not report eDiscovery hold operations such as custodial holds and search exports for review; it provides visibility into protection-activity telemetry, while holds and exports are managed in eDiscovery. Each wrong option fails because it assigns activity explorer an unrelated product role.
Exam caveat: Know the boundary between protection-activity reporting (activity explorer), labeled content distribution by location (Content explorer), insider risk signals (Insider Risk Management), and eDiscovery hold operations (eDiscovery). AB-900 items often tempt candidates to treat every Purview word as interchangeable; activity explorer specifically answers “what protection activities did users perform?”
Operational check: Demonstrate activity explorer to auditors with a filtered sample of labeling and DLP-match events for assessor sites, show user and activity columns, and document that labeled content distribution, insider risk signals, and eDiscovery hold operations remain separately reviewed in their respective Purview surfaces. Capture a screenshot set for the audit binder proving the county can monitor protection activity without claiming the explorer replaces access or identity controls.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.