
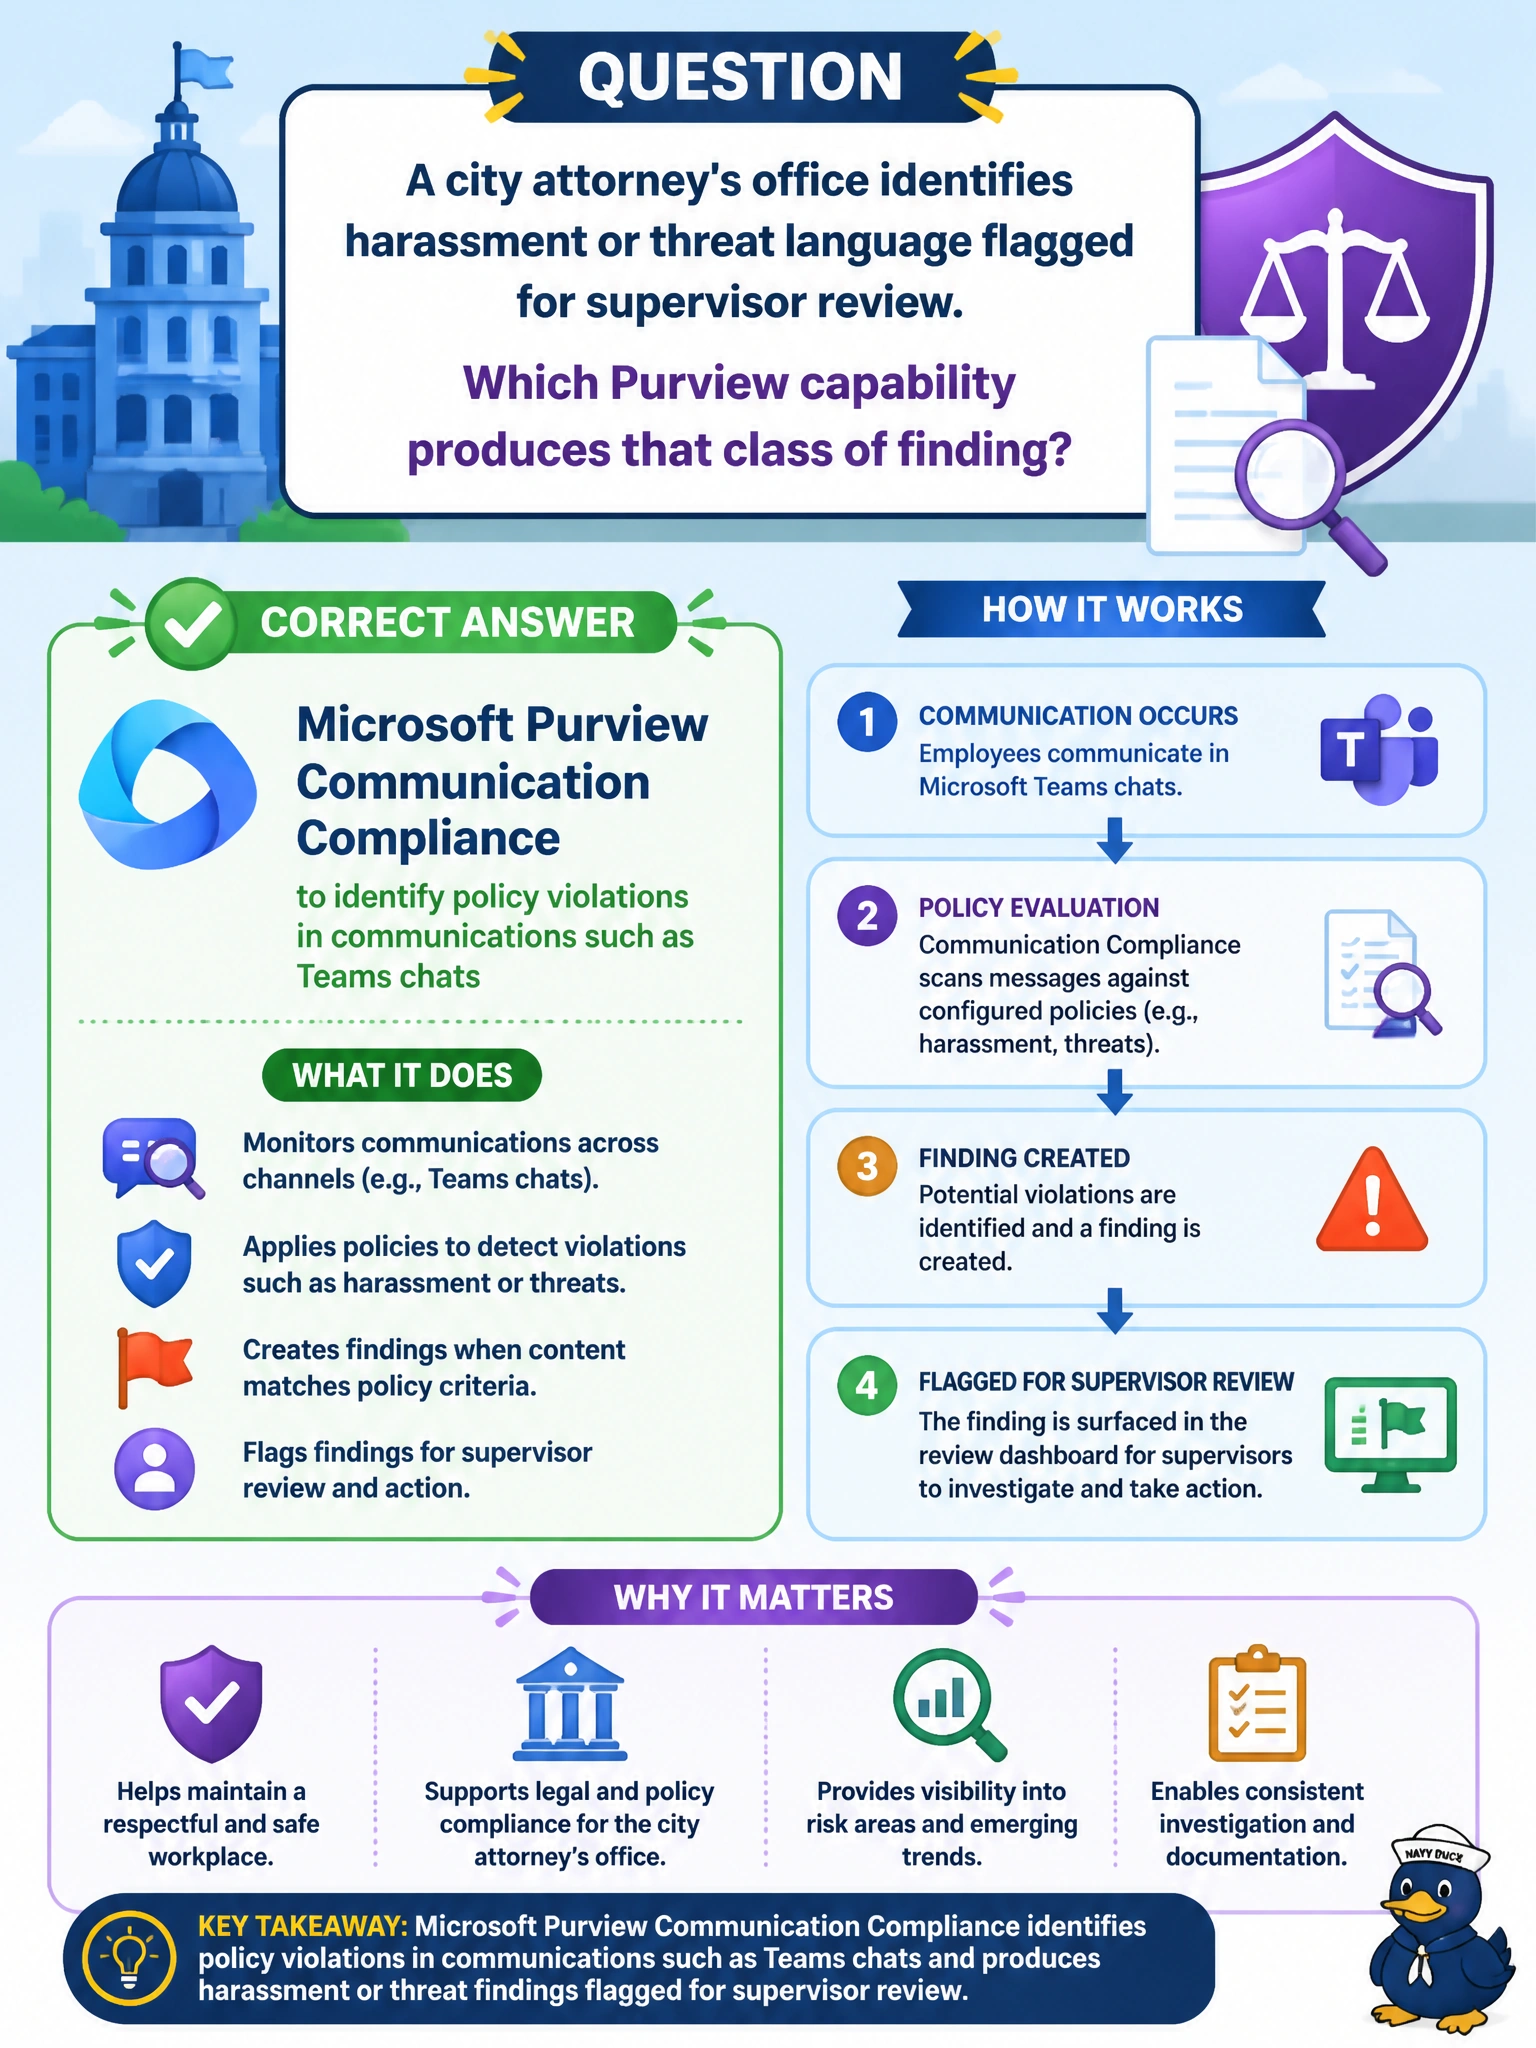
A city attorney's office identifies harassment or threat language flagged for supervisor review. Which Purview capability produces that class of finding?
Select an answer to reveal the explanation.
Short Explanation
Harassment or threat language flagged for a supervisor? That's Communication Compliance. It's not eDiscovery, Audit logs, or Insider Risk Management trends. You should know which Purview capability raises that flag.
Full Explanation
Harassment or threat language flagged for supervisor review is produced by Microsoft Purview Communication Compliance, which identifies policy violations in communications such as Teams chats. City attorneys should map that class of finding to Communication Compliance—not to eDiscovery for legal case collection, Audit for activity timelines, or Insider Risk Management for anomalous activity trends. The capability exists to detect and route policy-relevant communications for review. Microsoft Purview eDiscovery fails as a harassment-detection system: eDiscovery collects Teams chats and mailboxes for legal case review, it does not classify conduct language or route harassment findings. Microsoft Purview Audit fails as a threat-language classifier: Audit logs user and admin activities for investigation timelines, it does not scan chat content for harassment language. Microsoft Purview Insider Risk Management fails as the primary conduct-policy engine here: it identifies anomalous user activity trends across Teams chats and emails, not targeted harassment-or-threat policy violations in communications. Exam caveat: AB-900 identify-level mapping: harassment/threat language in Teams → Communication Compliance. DLP would be the wrong lane if the stem is about conduct language rather than sensitive identifiers. Insider Risk Management may correlate broader risky activities but is not the primary “policy violation in communications” answer here. Operational check: Verify Communication Compliance policies covering harassment/threat categories are in place for relevant Teams workloads, that supervisor/attorney review paths are defined, and that test phrases in a supervised pilot channel produce the expected finding type without relying on eDiscovery, Audit, or Insider Risk Management as the detection source.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.