
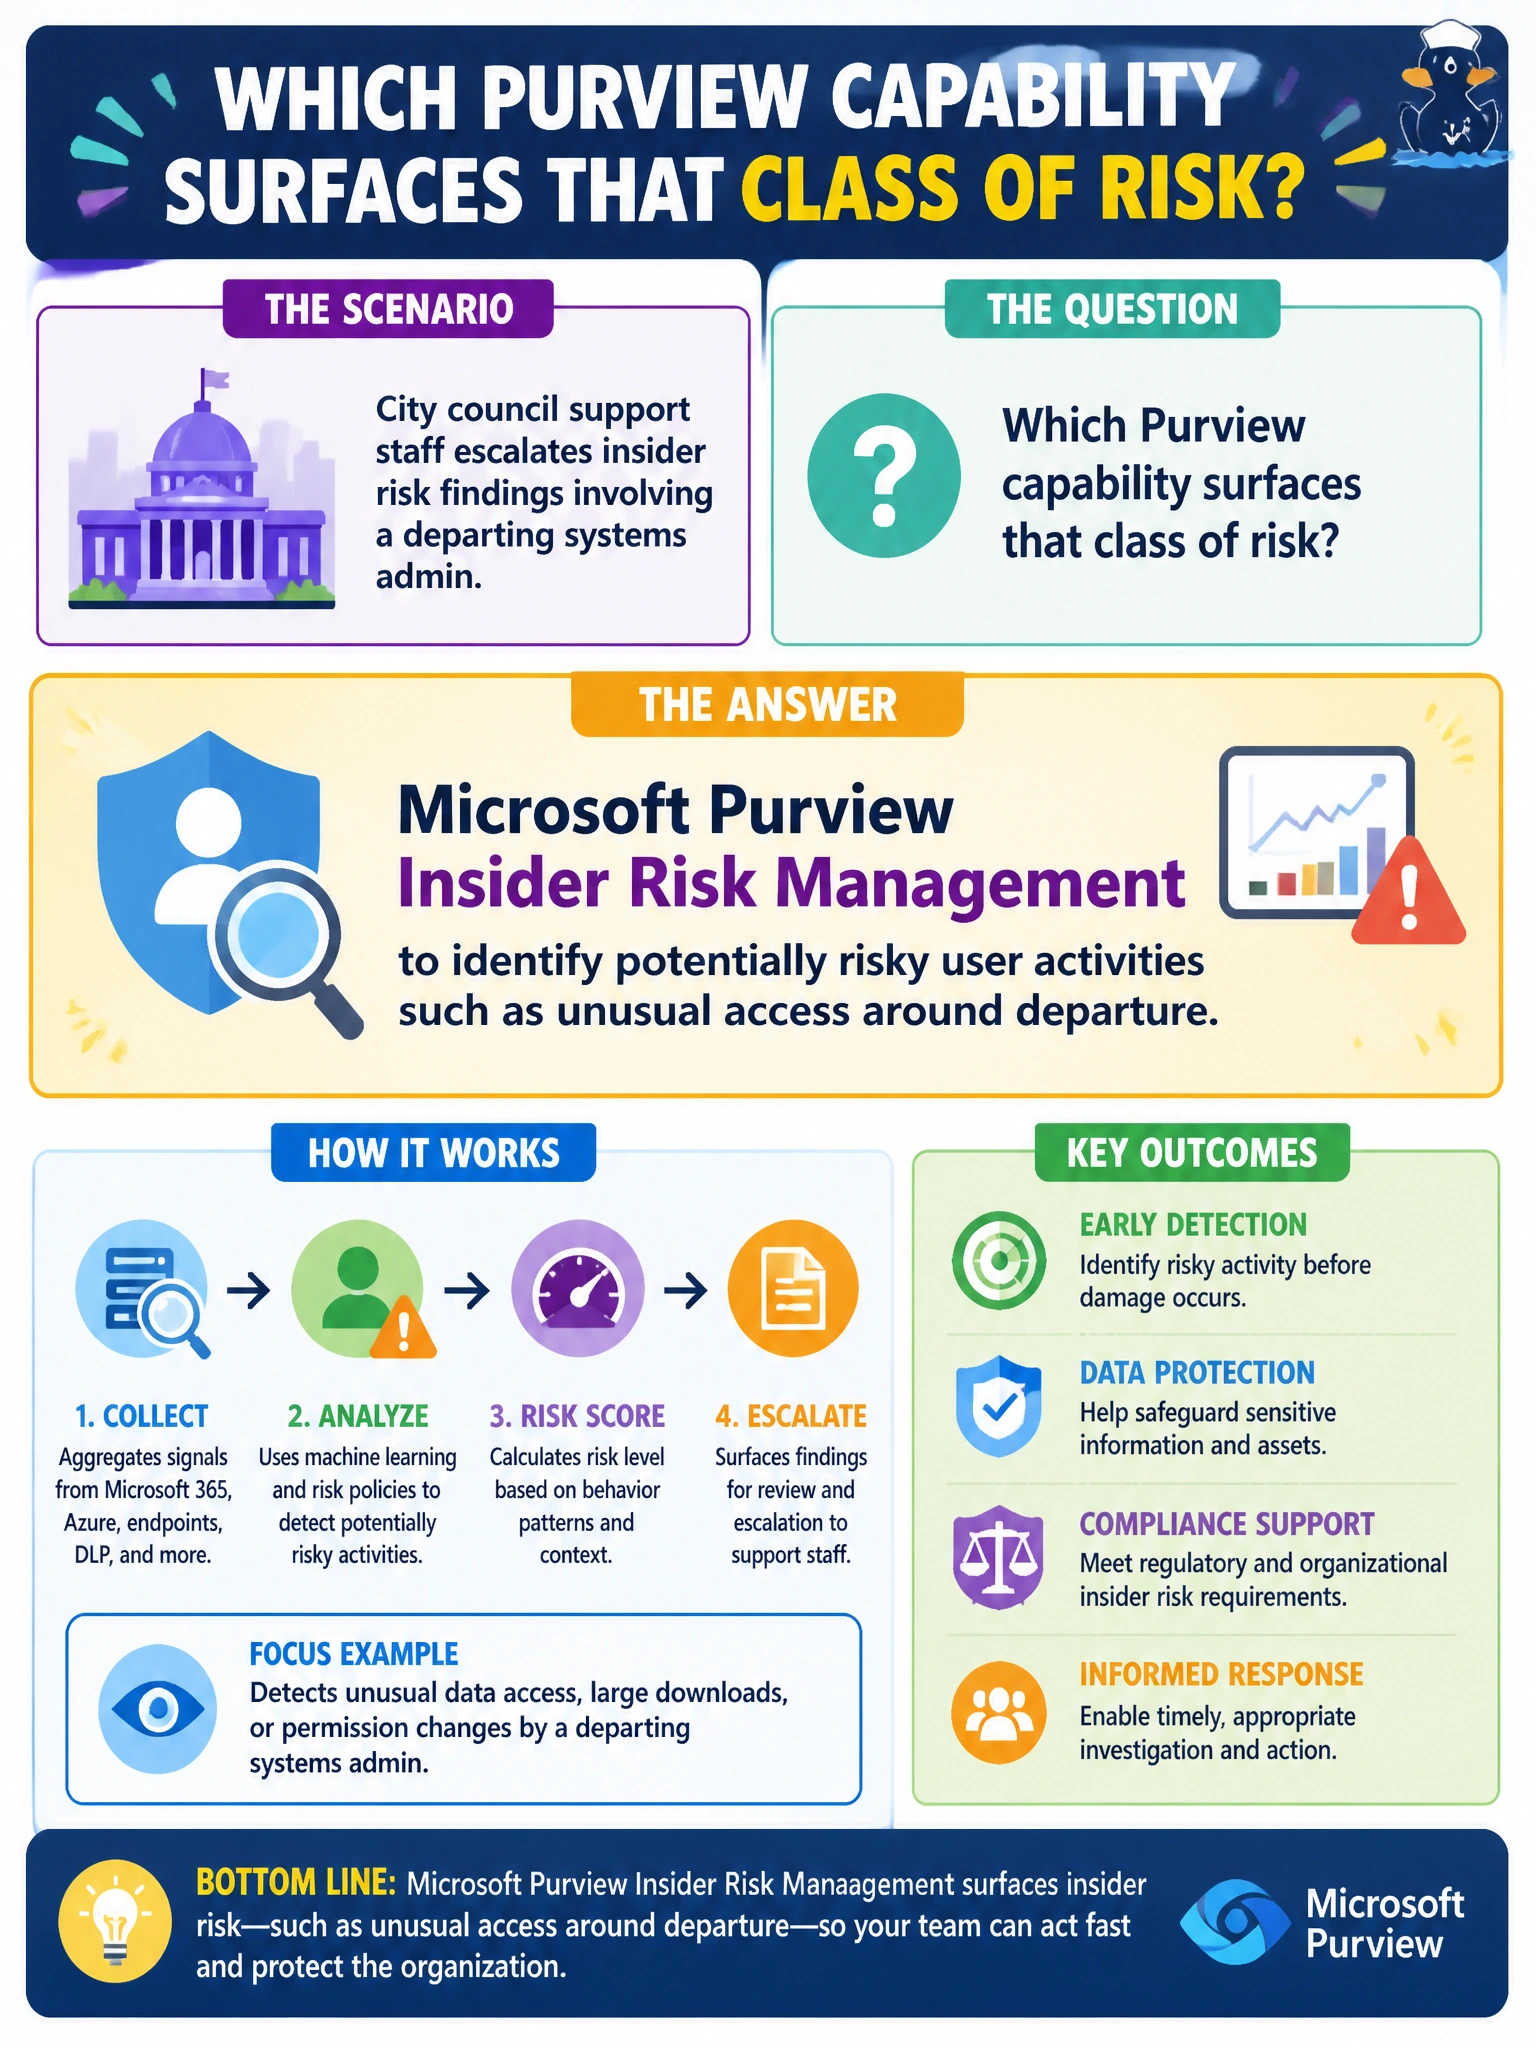
City council support staff escalates insider risk findings involving a departing systems admin. Which Purview capability surfaces that class of risk?
Select an answer to reveal the explanation.
Short Explanation
Departing admins with weird access spikes? That's Insider Risk Management territory. You'll see DLP prevents uploads, eDiscovery handles search and review, and Communication Compliance checks messages, but they don't surface insider-risk activity. Escalate the Purview insider-risk findings.
Full Explanation
City council support staff escalating findings involving a departing systems admin should recognize Microsoft Purview Insider Risk Management as the capability that identifies potentially risky user activities such as unusual access around departure. Departure and resignation windows are classic insider-risk scenarios: elevated downloads, unusual sharing, or access outside normal patterns can signal data risk. Insider Risk Management is built to surface that class of signal for investigation.
Microsoft Purview Data Loss Prevention to prevent potentially risky sharing activities such as sensitive uploads around departure fails: DLP is designed to prevent or block sensitive-content sharing, not to surface insider-risk signals such as unusual access around a departure.
Microsoft Purview eDiscovery to surface potentially risky user activities such as mailbox collections around departure for review fails: eDiscovery is built for content search, legal holds, and review, not for surfacing potentially risky user activity tied to insider risk.
Microsoft Purview Communication Compliance to detect potentially risky user activities such as policy message violations around departure fails: Communication Compliance supervises communications for policy violations, not insider-risk activity analytics around departure.
Exam caveat: AB-900 wants the capability name and purpose—Insider Risk Management for potentially risky user activities, including departure-related patterns. Exact policy templates vary by tenant; the exam tests recognition, not every indicator configuration.
Operational check: Ensure departing-admin offboarding includes review of Insider Risk Management alerts and recent high-volume access/download activity, disable standing privileged access promptly, and retain audit evidence rather than relying on DLP, eDiscovery, or Communication Compliance to surface insider risk.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.