
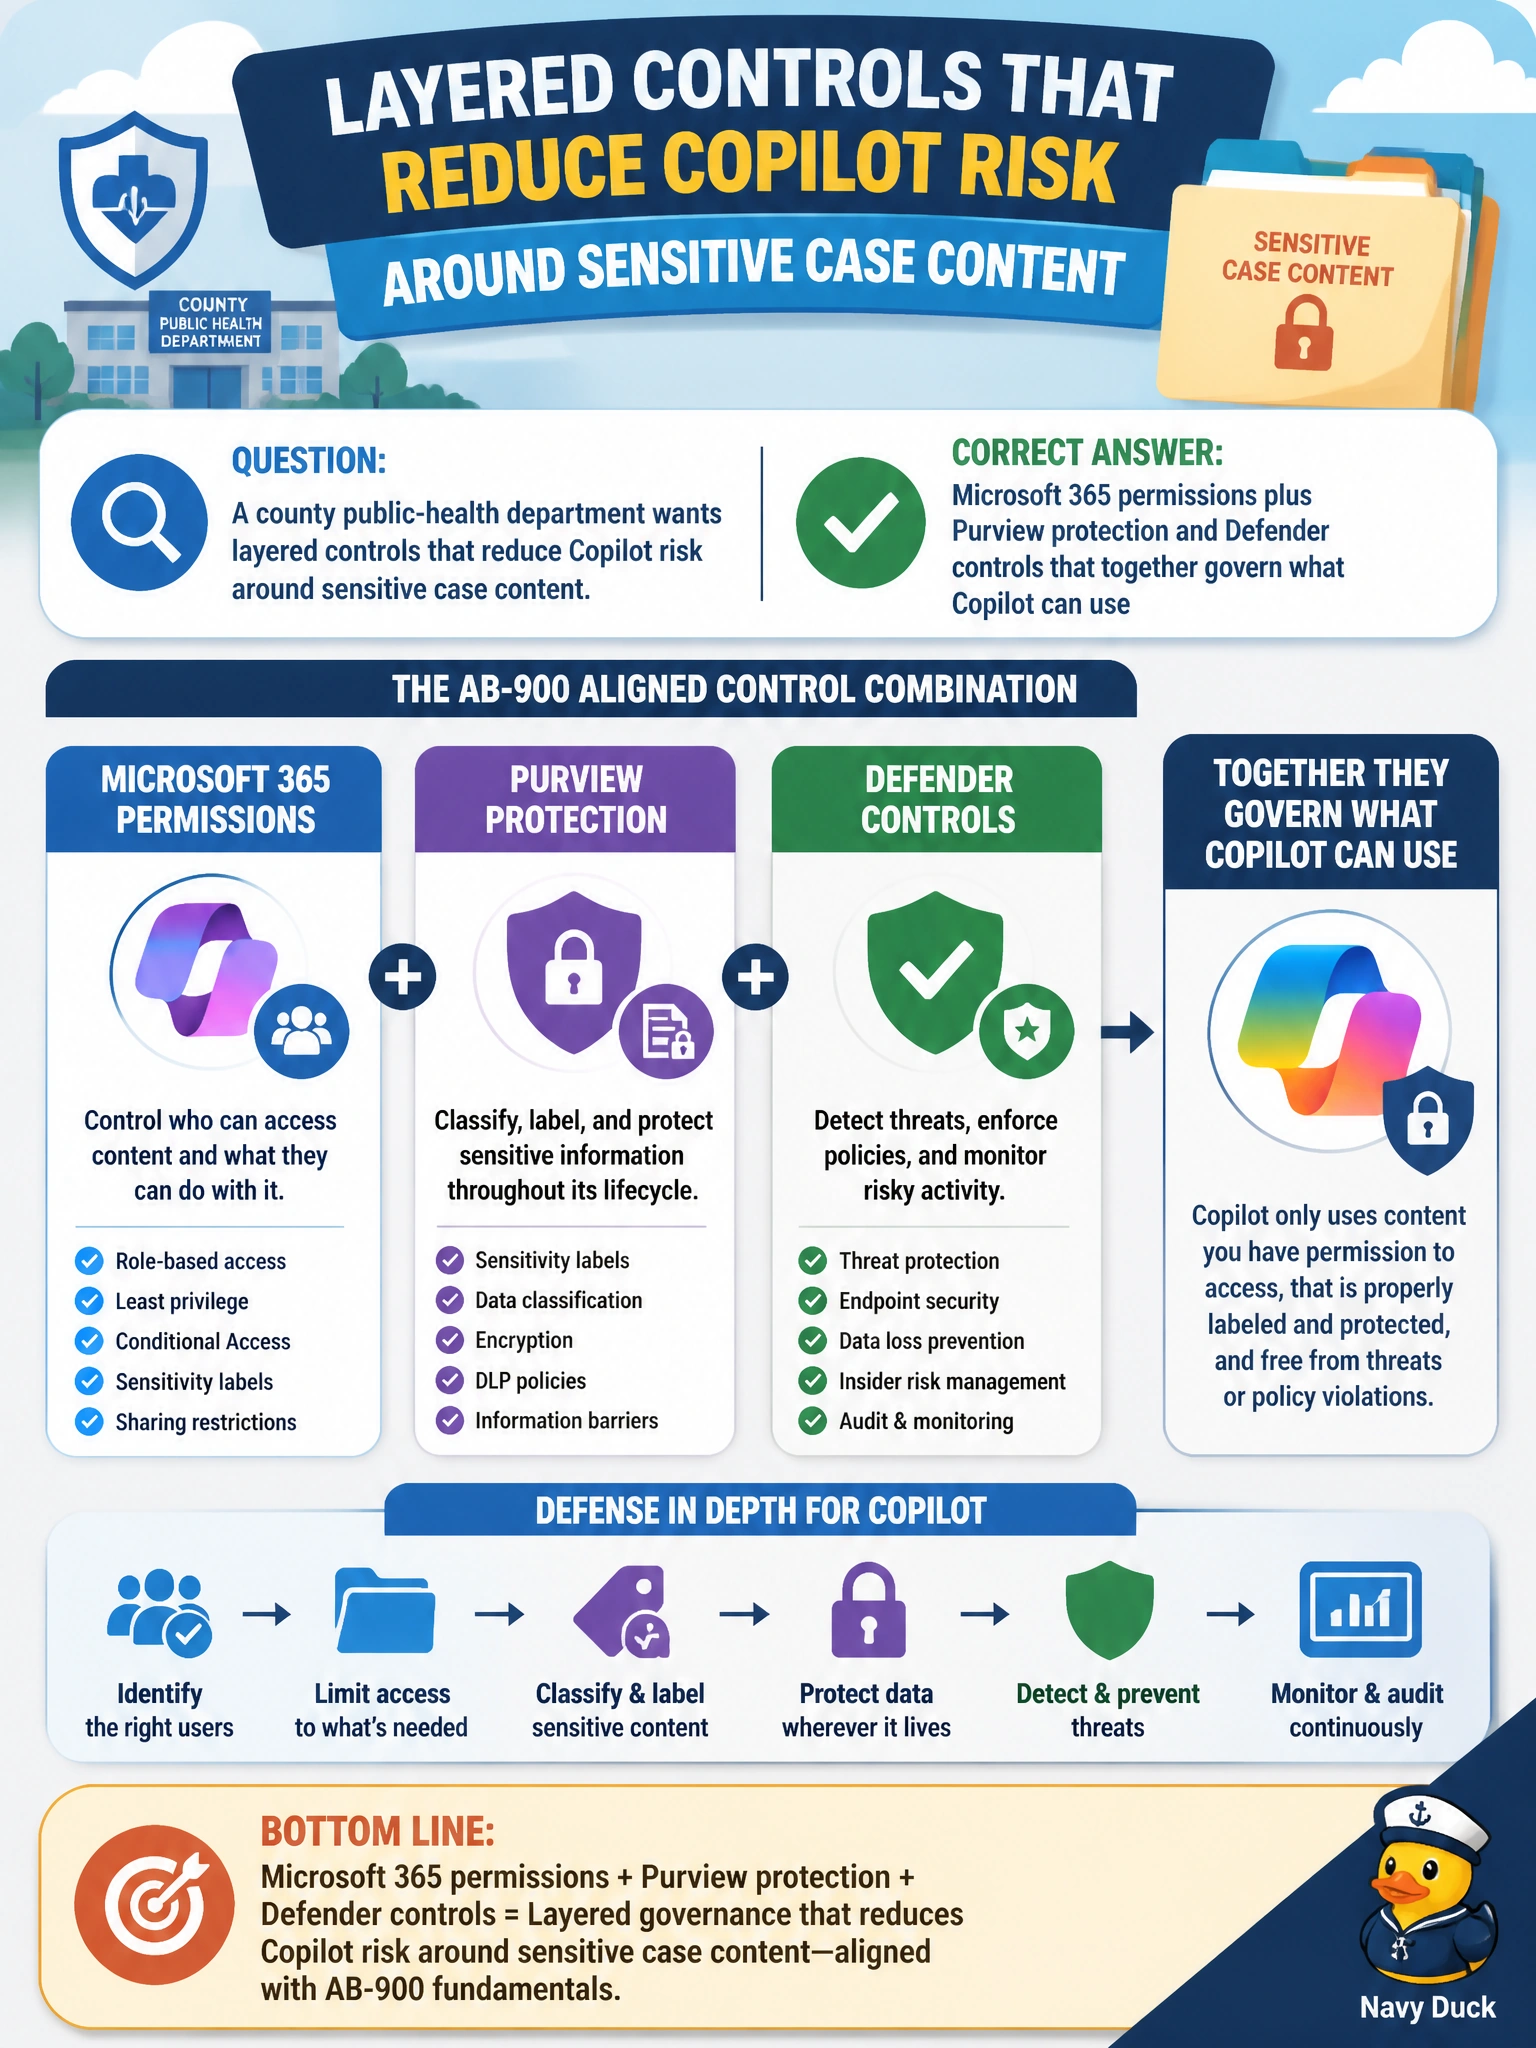
A county public-health department wants layered controls that reduce Copilot risk around sensitive case content. Which control combination fits AB-900 fundamentals?
Select an answer to reveal the explanation.
Short Explanation
Think layers: Microsoft 365 permissions, Purview protection, and Defender controls working together so Copilot isn't roaming free through public-health case files. Any one of those layers alone, without the others, leaves a gap in that control plane.
Full Explanation
Copilot risk reduction for sensitive public-health case content relies on layered Microsoft 365 permissions together with Purview protection and Defender controls that together govern what Copilot can use. A county public-health department seeking layered controls that reduce Copilot risk should identify that combination at AB-900 fundamentals. SharePoint page publishing plus Purview audit logs and Defender exposure scores only publish pages and record activity and score exposure; they don't layer Microsoft 365 permissions with Purview protection and Defender controls to govern what Copilot can use, so sensitive case content remains exposed without that preventive combination. Microsoft Entra guest access plus Purview retention holds and Defender alert queues expand external sharing and preserve content and queue alerts for triage, but they don't provide the layered Microsoft 365 permissions, Purview protection, and Defender controls that govern what Copilot can use. Purview sensitivity labels plus Defender app discovery and Entra guest approvals only classify content and discover apps and approve guest requests, yet they miss the Microsoft 365 permissions foundation and Defender protective enforcement needed to govern what Copilot can use from case content. Exam caveat: AB-900 asks candidates to recognize layered permissions + Purview + Defender governance for Copilot risk—not nickname-only or shared-password "controls." Operational check: review case library ACLs, apply sensitivity labels and DLP where appropriate, ensure Defender protections are enabled for endpoints and cloud apps in scope, and re-test Copilot access after each layer. Layering matters because each control addresses a different failure mode: permissions limit who can reach case files, Purview labels and related protections constrain sharing and classification handling, and Defender reduces endpoint and threat pathways that could expose the same content. Public-health AI readiness is incomplete if any one layer is treated as optional decoration.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.