
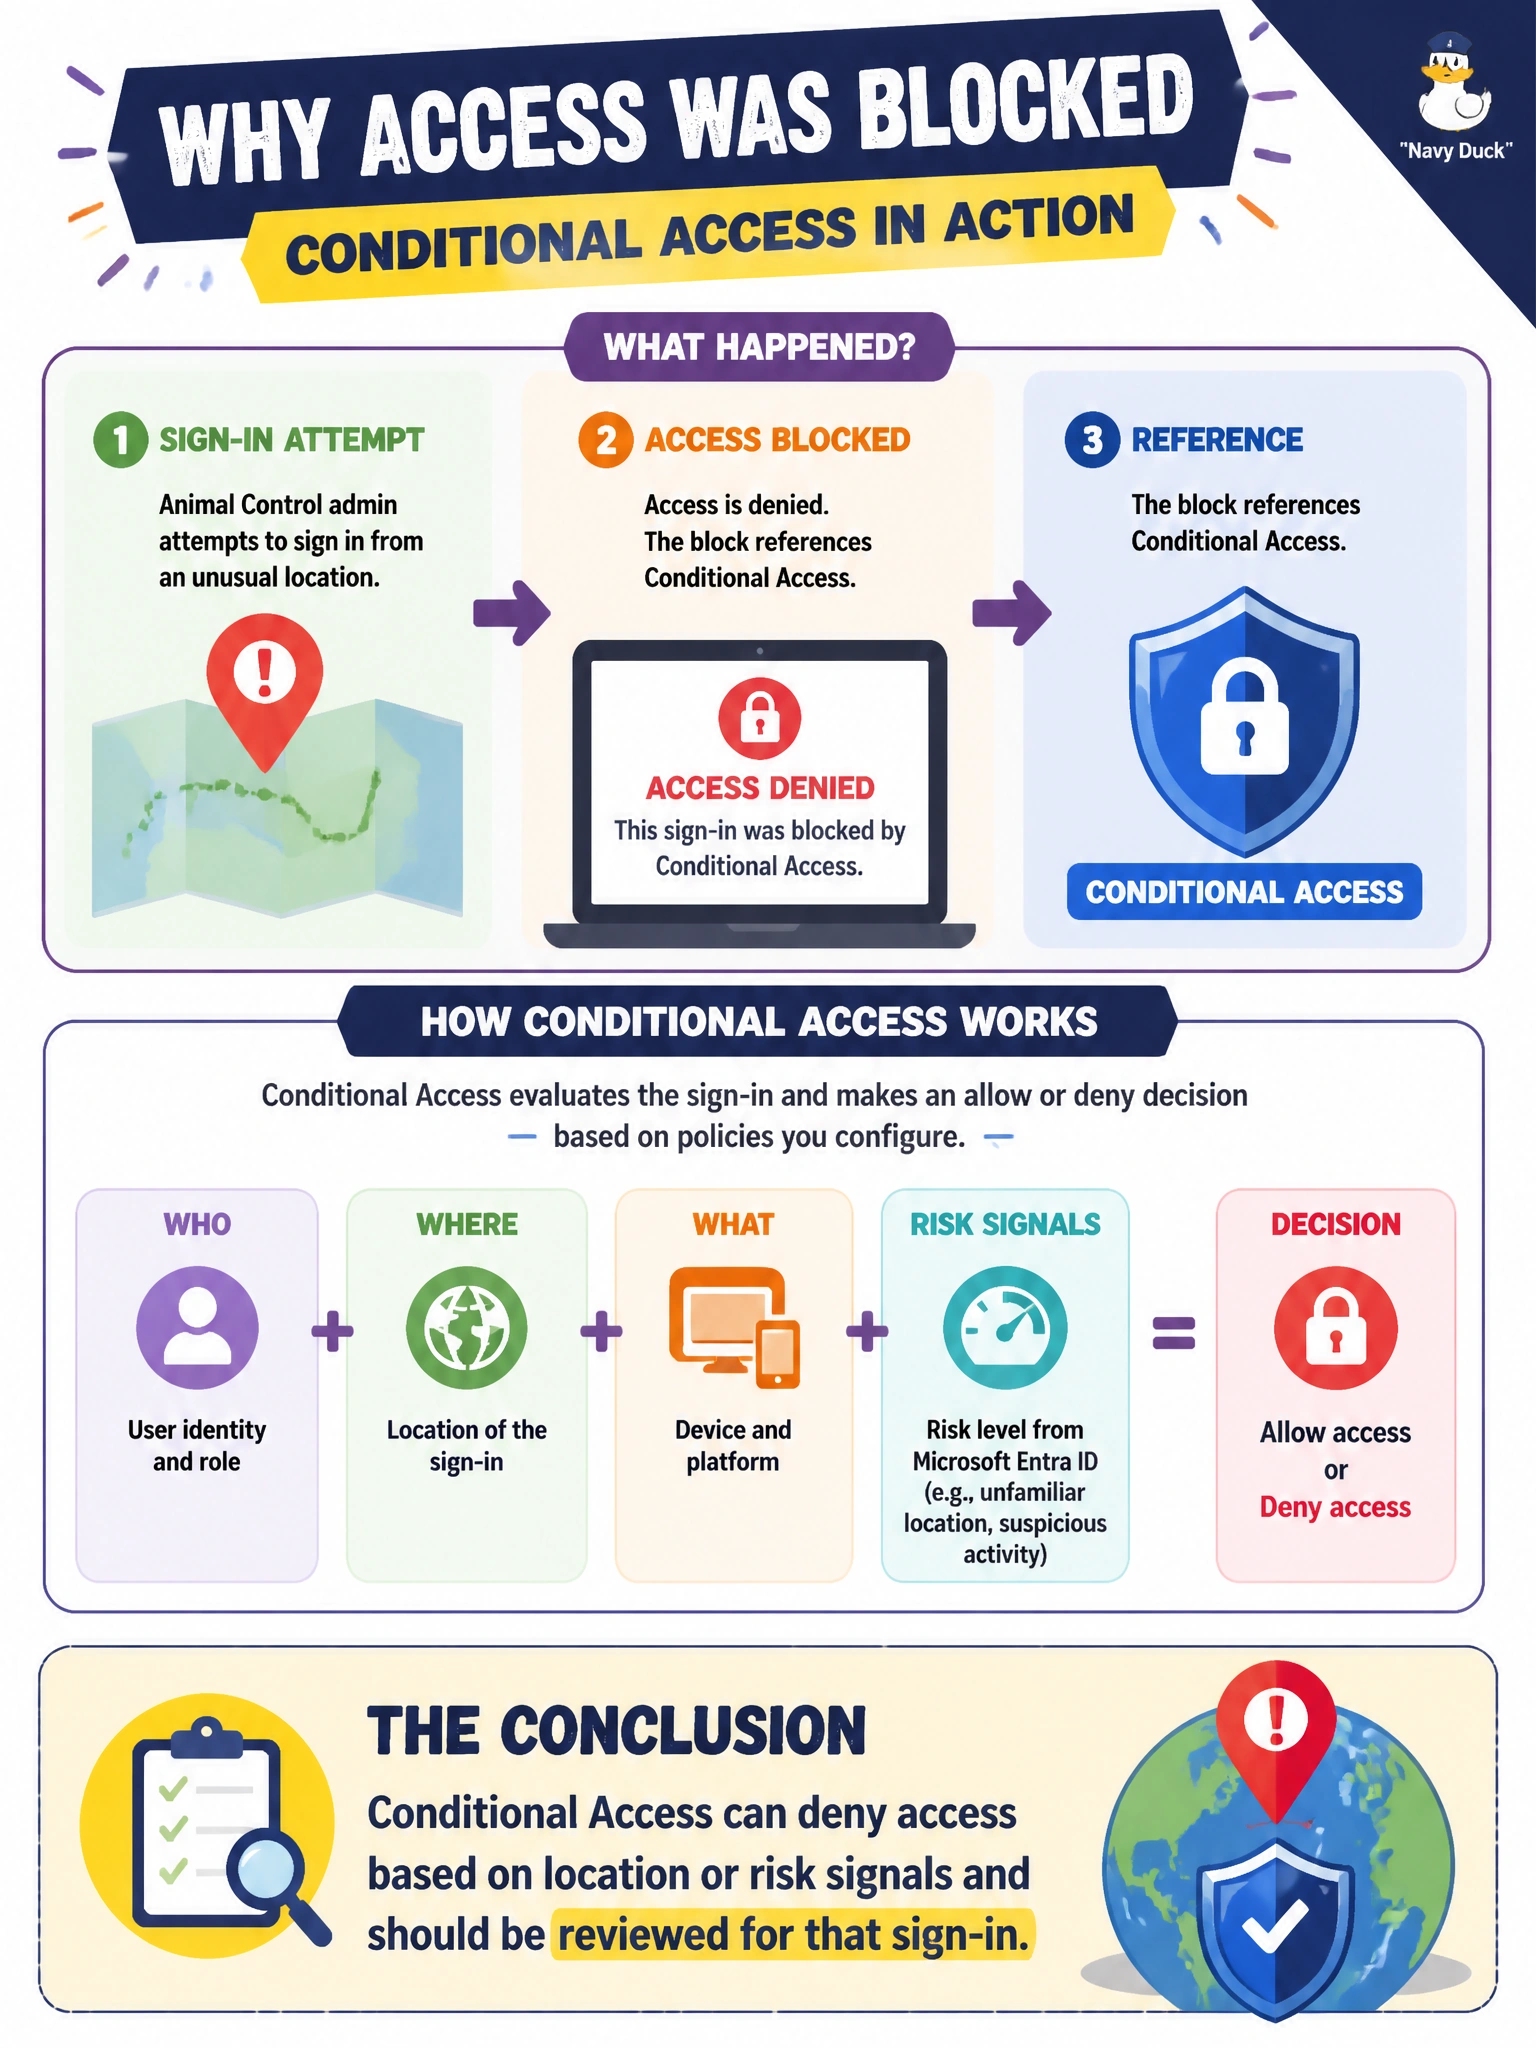
An animal control admin is denied access from an unusual location, and the block references Conditional Access. What conclusion fits?
Select an answer to reveal the explanation.
Short Explanation
Weird location, CA named in the denial — that policy is doing its job or needs a tuned exception. You won't find an allow pending MFA in the log for this block, and adding the spot to named locations won't make your device compliant — you've still hit the location/risk condition. Confirming it as safe in Identity Protection won't resolve the location denial — you'll still have to review the actual condition.
Full Explanation
When an animal control admin is denied access from an unusual location and the block references Conditional Access, the sound conclusion is that Conditional Access can deny access based on location or related risk signals and that the specific sign-in should be reviewed. Adding the unusual location to named locations does not mark the admin's device as compliant, because named locations only define trusted network locations for policy evaluation while device compliance is determined separately by compliance signals. The denial may be correct protection for city systems or may need a temporary trusted-location update for legitimate fieldwork. The sign-in log for this blocked event will not show a Conditional Access allow that granted access pending multifactor authentication; a denied sign-in reports failure with the location or risk condition that enforced the block, and awaiting multifactor authentication does not convert that denial into a grant. Adding the unusual location to named locations does not mark the admin's device as compliant for that policy; named locations only define trusted network locations for future policy evaluation, while compliance requires a separate compliant device state, and the denied sign-in still requires review. Confirming the sign-in as safe in Identity Protection does not resolve the Conditional Access location denial; dismissing user or sign-in risk does not satisfy a location-based condition, which still requires explicit review or adjustment before access is restored. Exam caveat: AB-900 pairs Conditional Access symptoms with the condition family named in the scenario (here, location/risk). Do not invent product overrides (SharePoint, Teams policies, licenses) that supposedly cancel Conditional Access. Review the sign-in before creating broad exclusions. Operational check: Open the animal control admin’s blocked sign-in report, confirm the Conditional Access location or risk condition that failed, verify whether the reported location matches expected field operations, adjust named locations or require stronger controls for high risk, and retest from the legitimate site without disabling Conditional Access tenant-wide.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.