
A police records bureau cites an identity benefit when onboarding seasonal parks employees who must use several Microsoft 365 apps quickly. Which benefit fits?
Select an answer to reveal the explanation.
Short Explanation
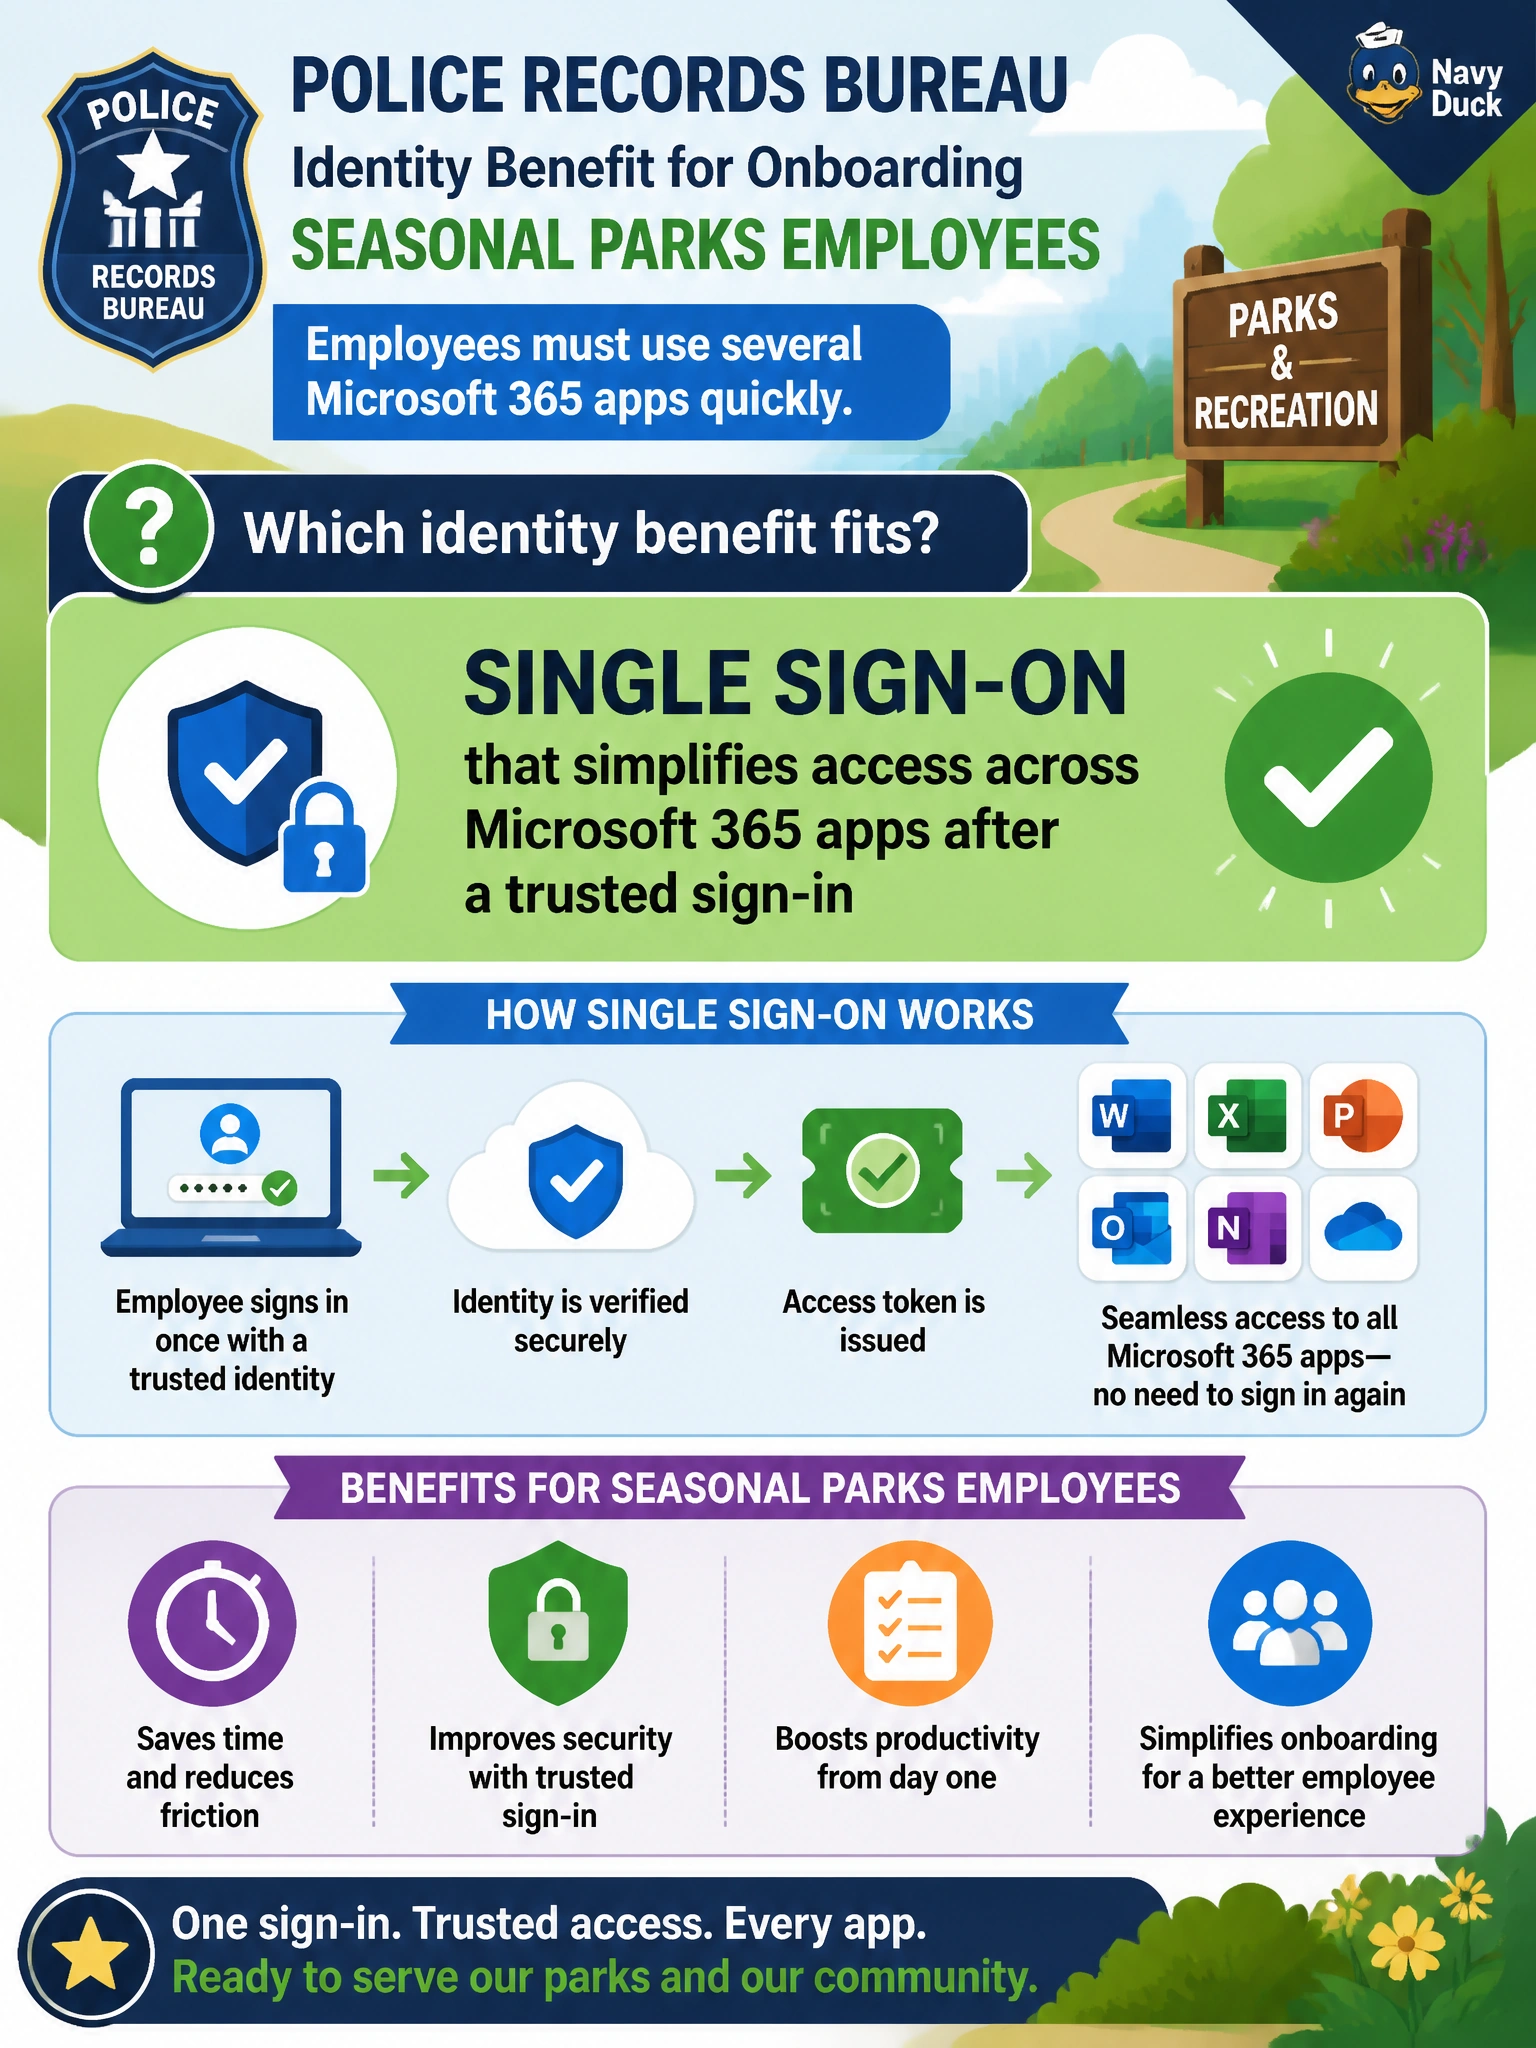
You need seasonal parks staff productive on day one, not stuck memorizing a phone book of passwords. SSO's the 'one badge, many doors' benefit after one trusted sign-in. Multifactor prompts, device-compliance checks, and guided recovery flows add steps instead of giving you that single-sign-on access.
Full Explanation
Single sign-on simplifies access across Microsoft 365 apps after a trusted sign-in, which is the identity benefit a police records bureau should cite when onboarding seasonal parks employees who must become productive quickly across several workloads. After one solid authentication, seasonal staff reach Outlook, Teams, SharePoint, and related apps with fewer repeated credential prompts—improving onboarding speed without sharing privileged secrets.
Multifactor authentication that strengthens sign-in to seasonal accounts with added verification fails by concept because it adds another verification step rather than reducing repeated credential prompts after one trusted sign-in; it improves assurance but does not deliver the single sign-on friction reduction the bureau needs. Conditional Access policy that controls seasonal access based on device compliance signals fails because it gates access by device state rather than letting one trusted sign-in carry forward across apps; it is an access control, not the SSO identity benefit that speeds seasonal onboarding. Self-service password reset that lets seasonal hires regain access through guided recovery prompts fails because it is a recovery tool for lost credentials, not an identity benefit that reduces repeated sign-in prompts across Microsoft 365 apps after one trusted sign-in.
Exam caveat: Fundamentals focus is recognizing SSO's usability and access-consistency value for multi-app municipal onboarding. You are not asked to implement every enterprise app SSO protocol on the exam item. Seasonal accounts should remain least-privilege individual identities—not Global Administrator shares.
Operational check: Provision individual seasonal parks accounts with appropriate licenses and groups, validate SSO across required Microsoft 365 apps after one trusted sign-in, avoid Global Administrator sharing, and use normal joiner-mover-leaver processes instead of making seasonal hires clear device-compliance gates or run guided recovery prompts before their first trusted sign-in.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.