
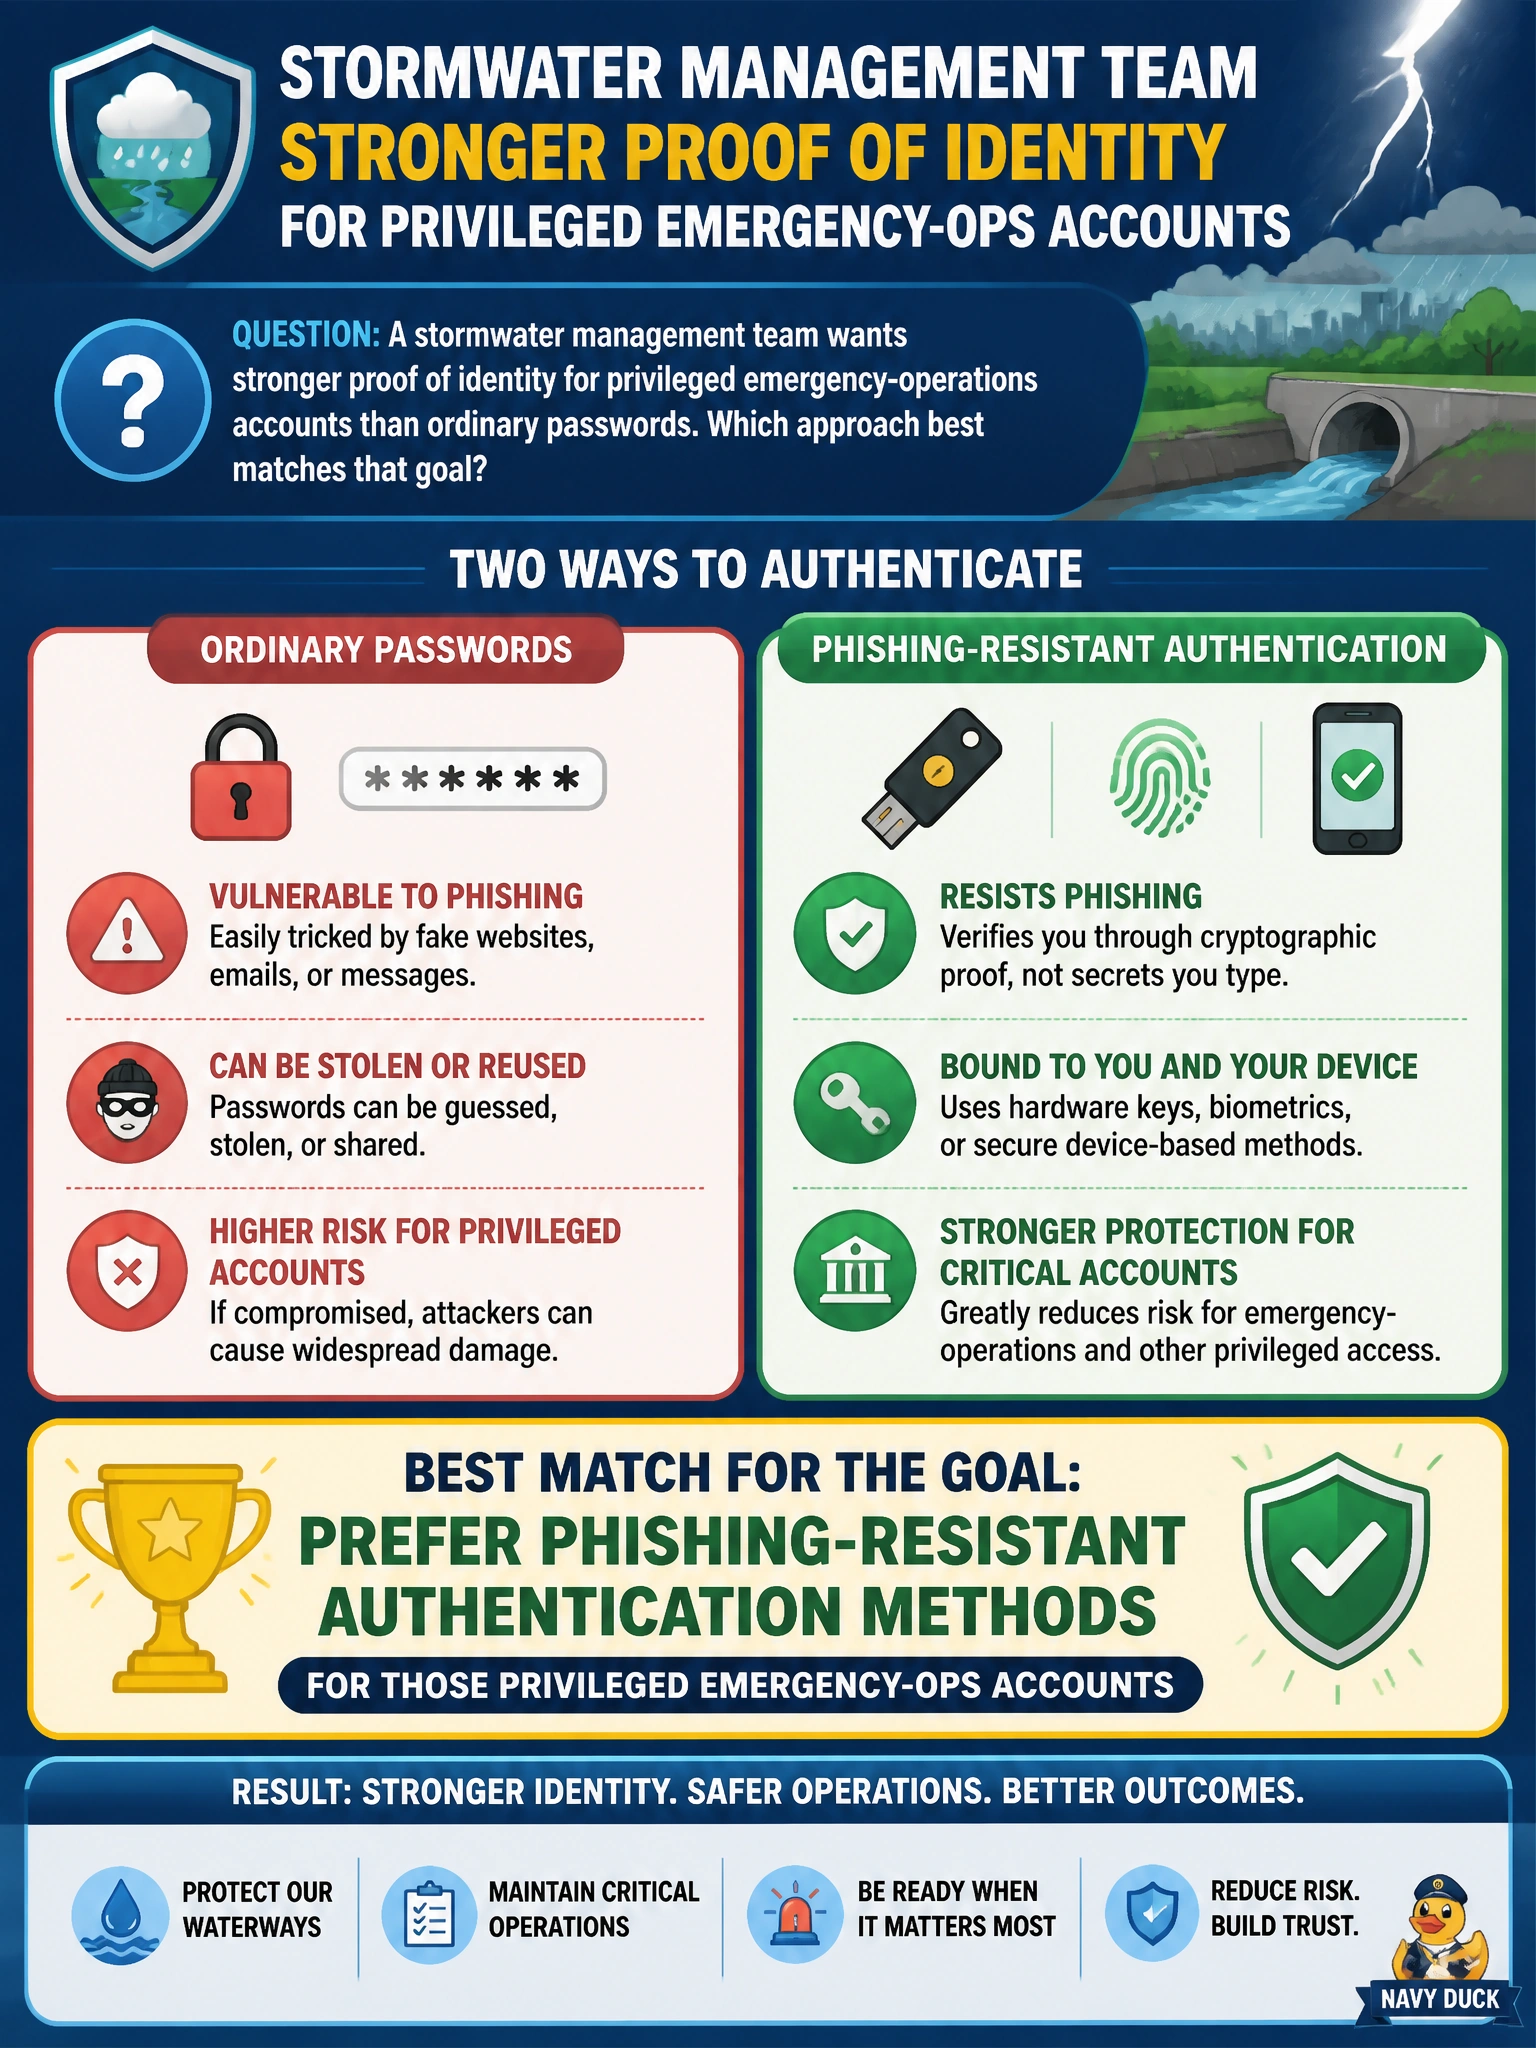
A stormwater management team wants stronger proof of identity for privileged emergency-operations accounts than ordinary passwords. Which approach best matches that goal?
Select an answer to reveal the explanation.
Short Explanation
Privileged emergency accounts are the master keys to the stormwater shop—treat them like keys, not sticky notes. Phishing-resistant methods make it much harder for a fake login page to steal that master key. Sticking with text-message codes, settling for Microsoft Authenticator approvals, or only requiring a compliant device still leaves you with a master key that's easier to steal than it should be.
Full Explanation
Privileged emergency-operations accounts for stormwater response control high-impact municipal systems, so identity proof should be stronger than ordinary passwords. Preferring phishing-resistant authentication methods—such as FIDO2 security keys or platform authenticators where supported—reduces takeover risk from fake login pages, MFA fatigue, and stolen passwords during flood-response windows. Aligning authentication strength with role sensitivity is the fundamentals guidance for privileged municipal identities.
Prioritizing text-message verification codes for those accounts fails because SMS delivery can still be intercepted or socially engineered, so it falls short of the phishing-resistant bar privileged emergency accounts need. Preferring Microsoft Authenticator approvals for those accounts fails because push approvals can still be phished or worn down with MFA fatigue, so they fall short of the phishing-resistant bar privileged emergency accounts need. Preferring compliant-device Conditional Access for those accounts fails to meet the goal on its own because it leaves the underlying authentication method—ordinary passwords—unchanged, which is exactly what the scenario wants strengthened.
Exam caveat: AB-900 asks for the principle—stronger, phishing-resistant methods for privileged accounts—not a full authenticator rollout design. Passwordless and phishing-resistant options may still pair with Conditional Access and privileged-role governance. Do not equate "break-glass" urgency with anonymous or shared-password shortcuts.
Operational check: Inventory privileged stormwater emergency-ops accounts, require phishing-resistant methods where feasible, ban shared privileged passwords, and test sign-in under realistic on-call conditions. Verify each elevation remains attributable to a named identity. Confirm guest or anonymous paths are not used as substitutes for privileged Entra authentication during incident response.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.