
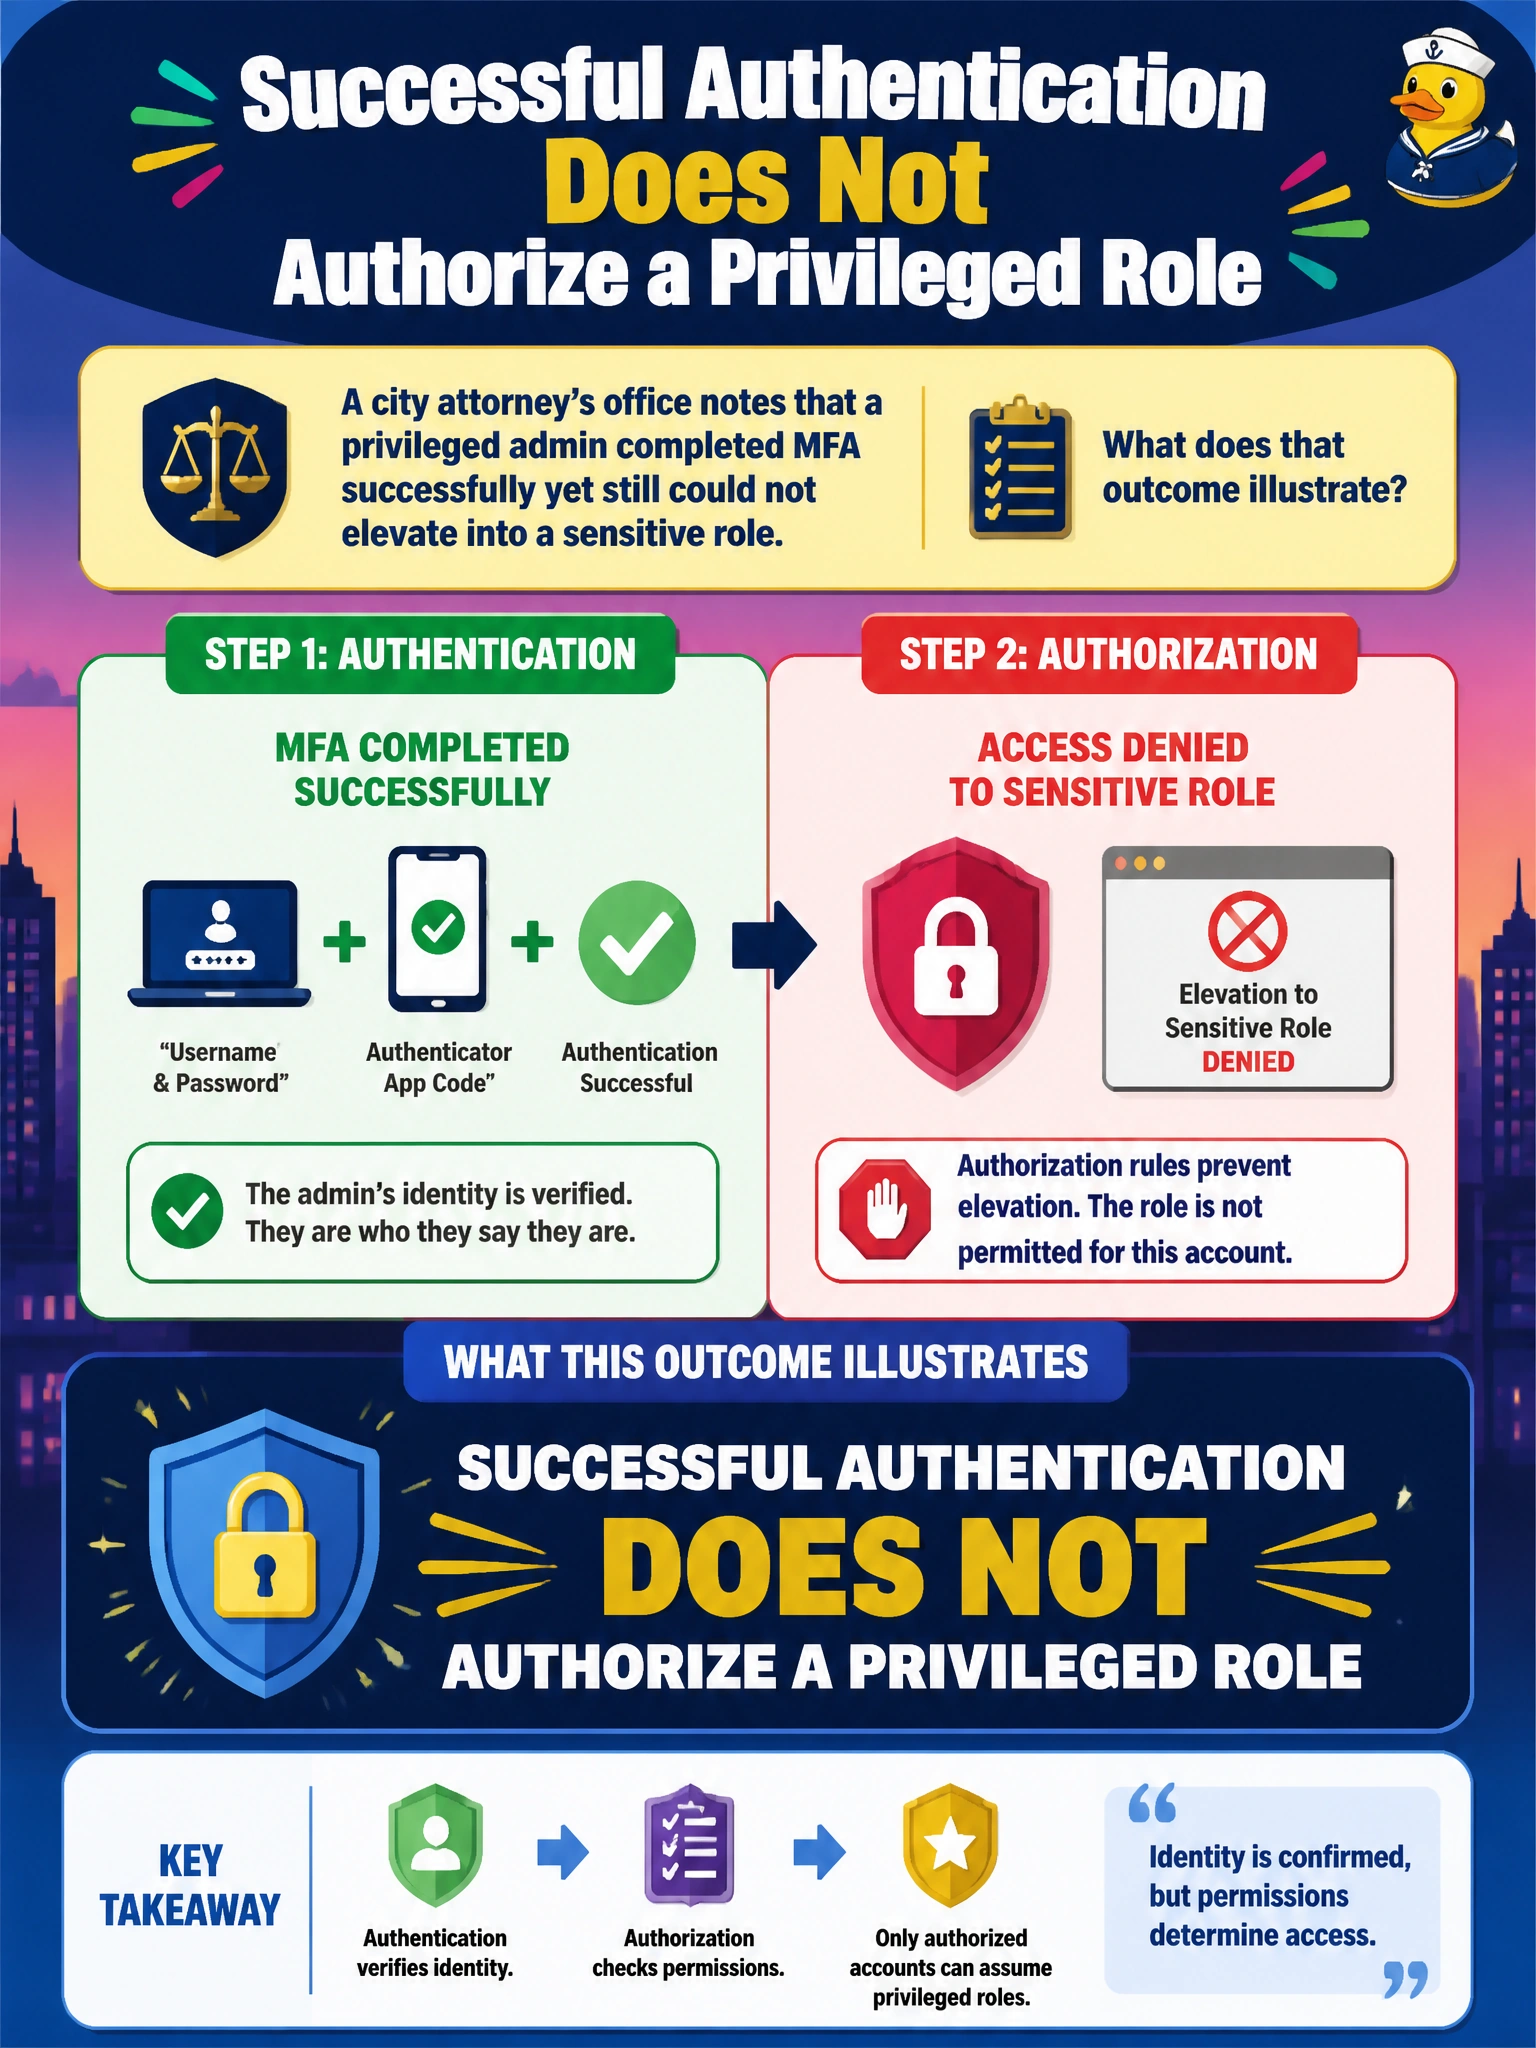
A city attorney's office notes that a privileged admin completed MFA successfully yet still could not elevate into a sensitive role. What does that outcome illustrate?
Select an answer to reveal the explanation.
Short Explanation
Think of clearing airport security and still needing a separate boarding pass for the flight. MFA got the admin through identity check, but the privileged role is a different ticket. Sign-in success is not the same thing as being allowed to wear the admin badge.
Full Explanation
Successful MFA proves the privileged admin's identity during sign-in; it does not by itself authorize elevation into a sensitive role. Municipal attorney-office and emergency scenarios often separate authentication strength from Privileged Identity Management (PIM) or role assignment: the admin may clear MFA and still lack an eligible or active privileged role until an authorization workflow grants just-in-time access. That outcome correctly illustrates that authentication success and privileged authorization are independent control planes in Microsoft 365.
Claiming that privileged role activation does not need separate justification once MFA has already succeeded fails because MFA is an authentication factor, while PIM activation is a separate authorization step that can still require justification, approval, eligible assignment, and Conditional Access before the role becomes active. Claiming that Conditional Access compliance does not need re-evaluation after MFA has already succeeded fails because Conditional Access is evaluated against activation-time conditions, and a prior MFA success does not guarantee those conditions remain satisfied for PIM activation. Asserting that active privileged access does not expire once MFA has already succeeded for activation fails because just-in-time PIM activation is time-limited and expires, so MFA success does not create standing privileged access.
Exam caveat: AB-900 expects you to separate "proved who I am" from "allowed to administer." You are not asked to configure PIM policies in depth; recognize that MFA hardens authentication while privileged roles remain an authorization decision. Do not assume active privileged access persists indefinitely after MFA; expect time-limited activation that expires and requires fresh authorization.
Operational check: Sign in with MFA as a municipal admin who is not assigned the sensitive role and confirm elevation fails. Review Entra role assignments or PIM eligibility for that identity, activate or assign only when justified, then retest. Document that MFA compliance and privileged-role authorization are verified as two checks before emergency-operations or attorney-office admin work proceeds.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.