
Tailspin Toys' compliance team receives a DLP alert in Microsoft Purview showing that an employee emailed a file containing 15 credit card numbers to an external recipient. The alert status is 'Active.' What are the correct next steps for the compliance officer managing this alert in Microsoft Purview?
Select an answer to reveal the explanation.
Short Explanation
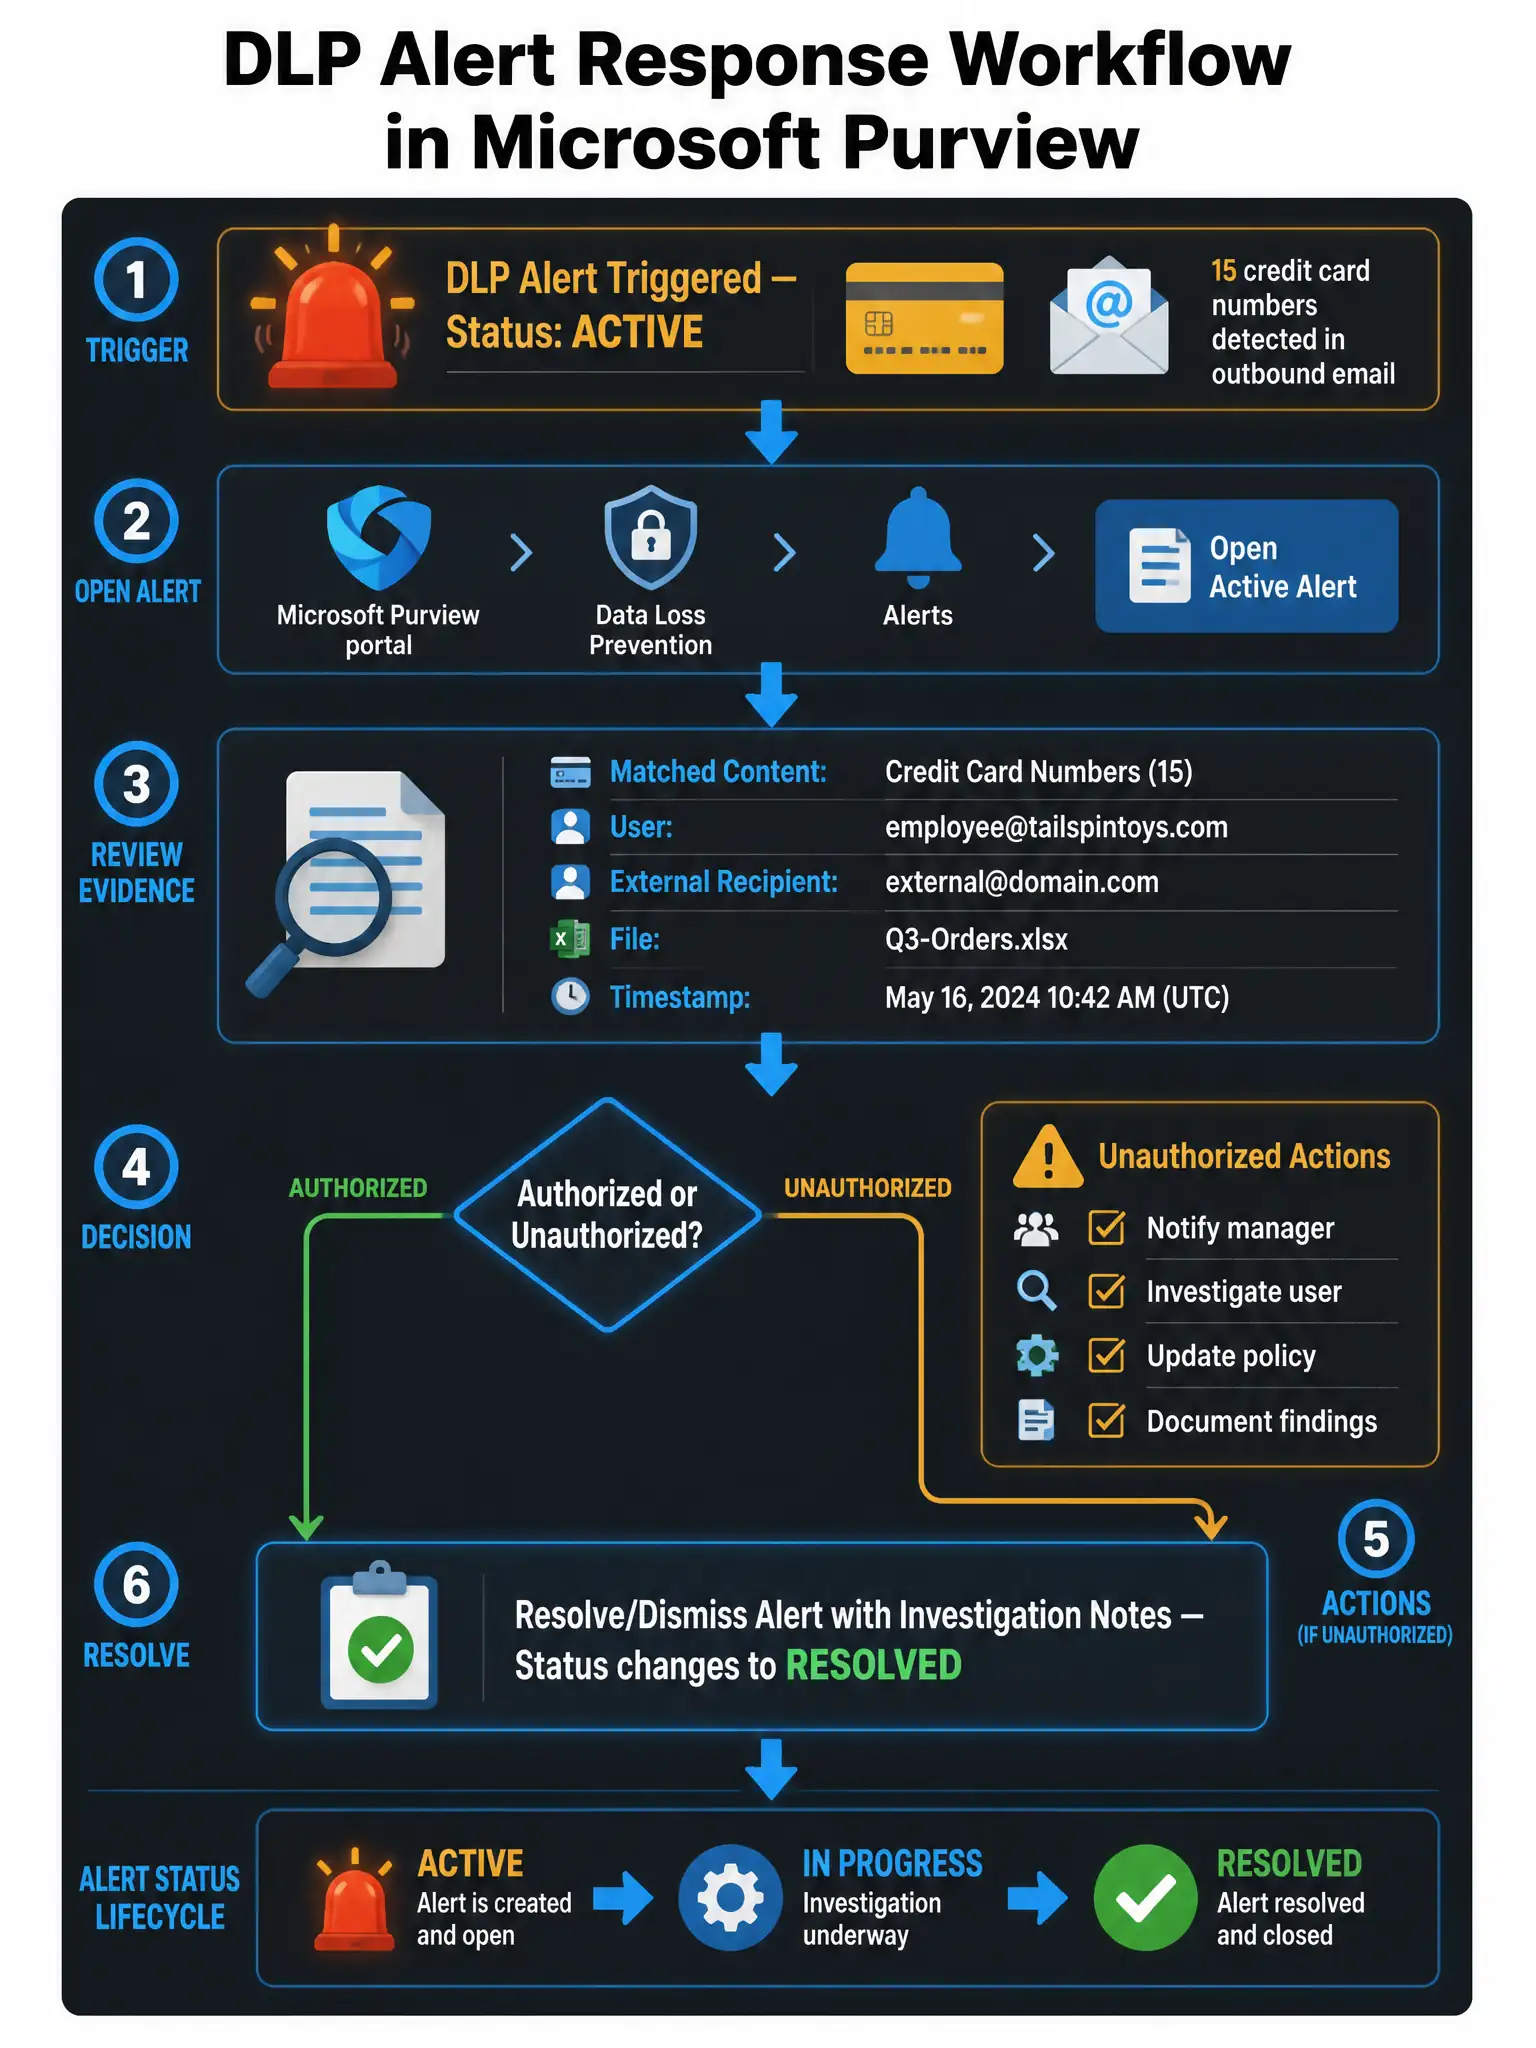
DLP alerts are like fire alarms — they tell you something happened and needs attention. When you see an Active alert, you open it in the Purview Alerts dashboard, review the evidence, decide what to do, then resolve or dismiss it with notes.
Full Explanation
The proper workflow for managing an Active DLP alert in Microsoft Purview is to navigate to Data Loss Prevention > Alerts, locate the alert, and open it to review the full details — including the matched sensitive information types (credit card numbers in this case), the file name, the sender, the external recipient, and the timestamp. The compliance officer then decides on the appropriate response action: this might include reviewing whether the transmission was authorized, notifying the employee's manager, initiating an HR or security investigation, and finally resolving the alert with notes that document the findings and actions taken. This is the standard DLP incident response process.
The Content Search and Purge approach is incorrect. The scenario states the email was already sent to an external recipient. Microsoft Purview Content Search and Purge can remove messages from Microsoft 365 mailboxes that you have access to, but it cannot reach into an external recipient's mailbox (for example, Gmail or Yahoo accounts). Even for internal mailboxes, this action would be appropriate only after confirming the email was unauthorized — and it still wouldn't help for external recipients. This is misleading but tempting.
The retroactive policy change approach is incorrect. DLP policy actions are configured at the policy rule level, not within individual alerts. Changing policy settings from 'Alert only' to 'Block' would affect future email transmissions matching the policy — it cannot retroactively stop email that has already been sent and delivered. Policy changes take effect for new matches going forward, not historically.
The Escalate to Microsoft Support approach is incorrect. There is no 'Escalate to Microsoft' option in the Microsoft Purview Alerts dashboard. DLP alerts are tools for the customer's compliance team to investigate and act upon. Microsoft does not investigate individual tenant DLP incidents on behalf of customers — that is the organization's own responsibility. This answer describes nonexistent feature.
Exam tip: For the exam, know the DLP alert lifecycle: Active (requires review) -> In Progress (being investigated) -> Resolved or Dismissed (with notes). The investigation workflow happens entirely within the Microsoft Purview compliance portal by the customer's compliance team, not by Microsoft Support.