
Woodgrove Bank operates three regional offices: East, West, and Central. Each region has its own IT support team that needs to manage password resets, group memberships, and user account properties — but only for users in their own region. The global IT team wants to ensure that the East IT team cannot accidentally modify a Central region user account. What should the Microsoft Entra administrator configure?
Select an answer to reveal the explanation.
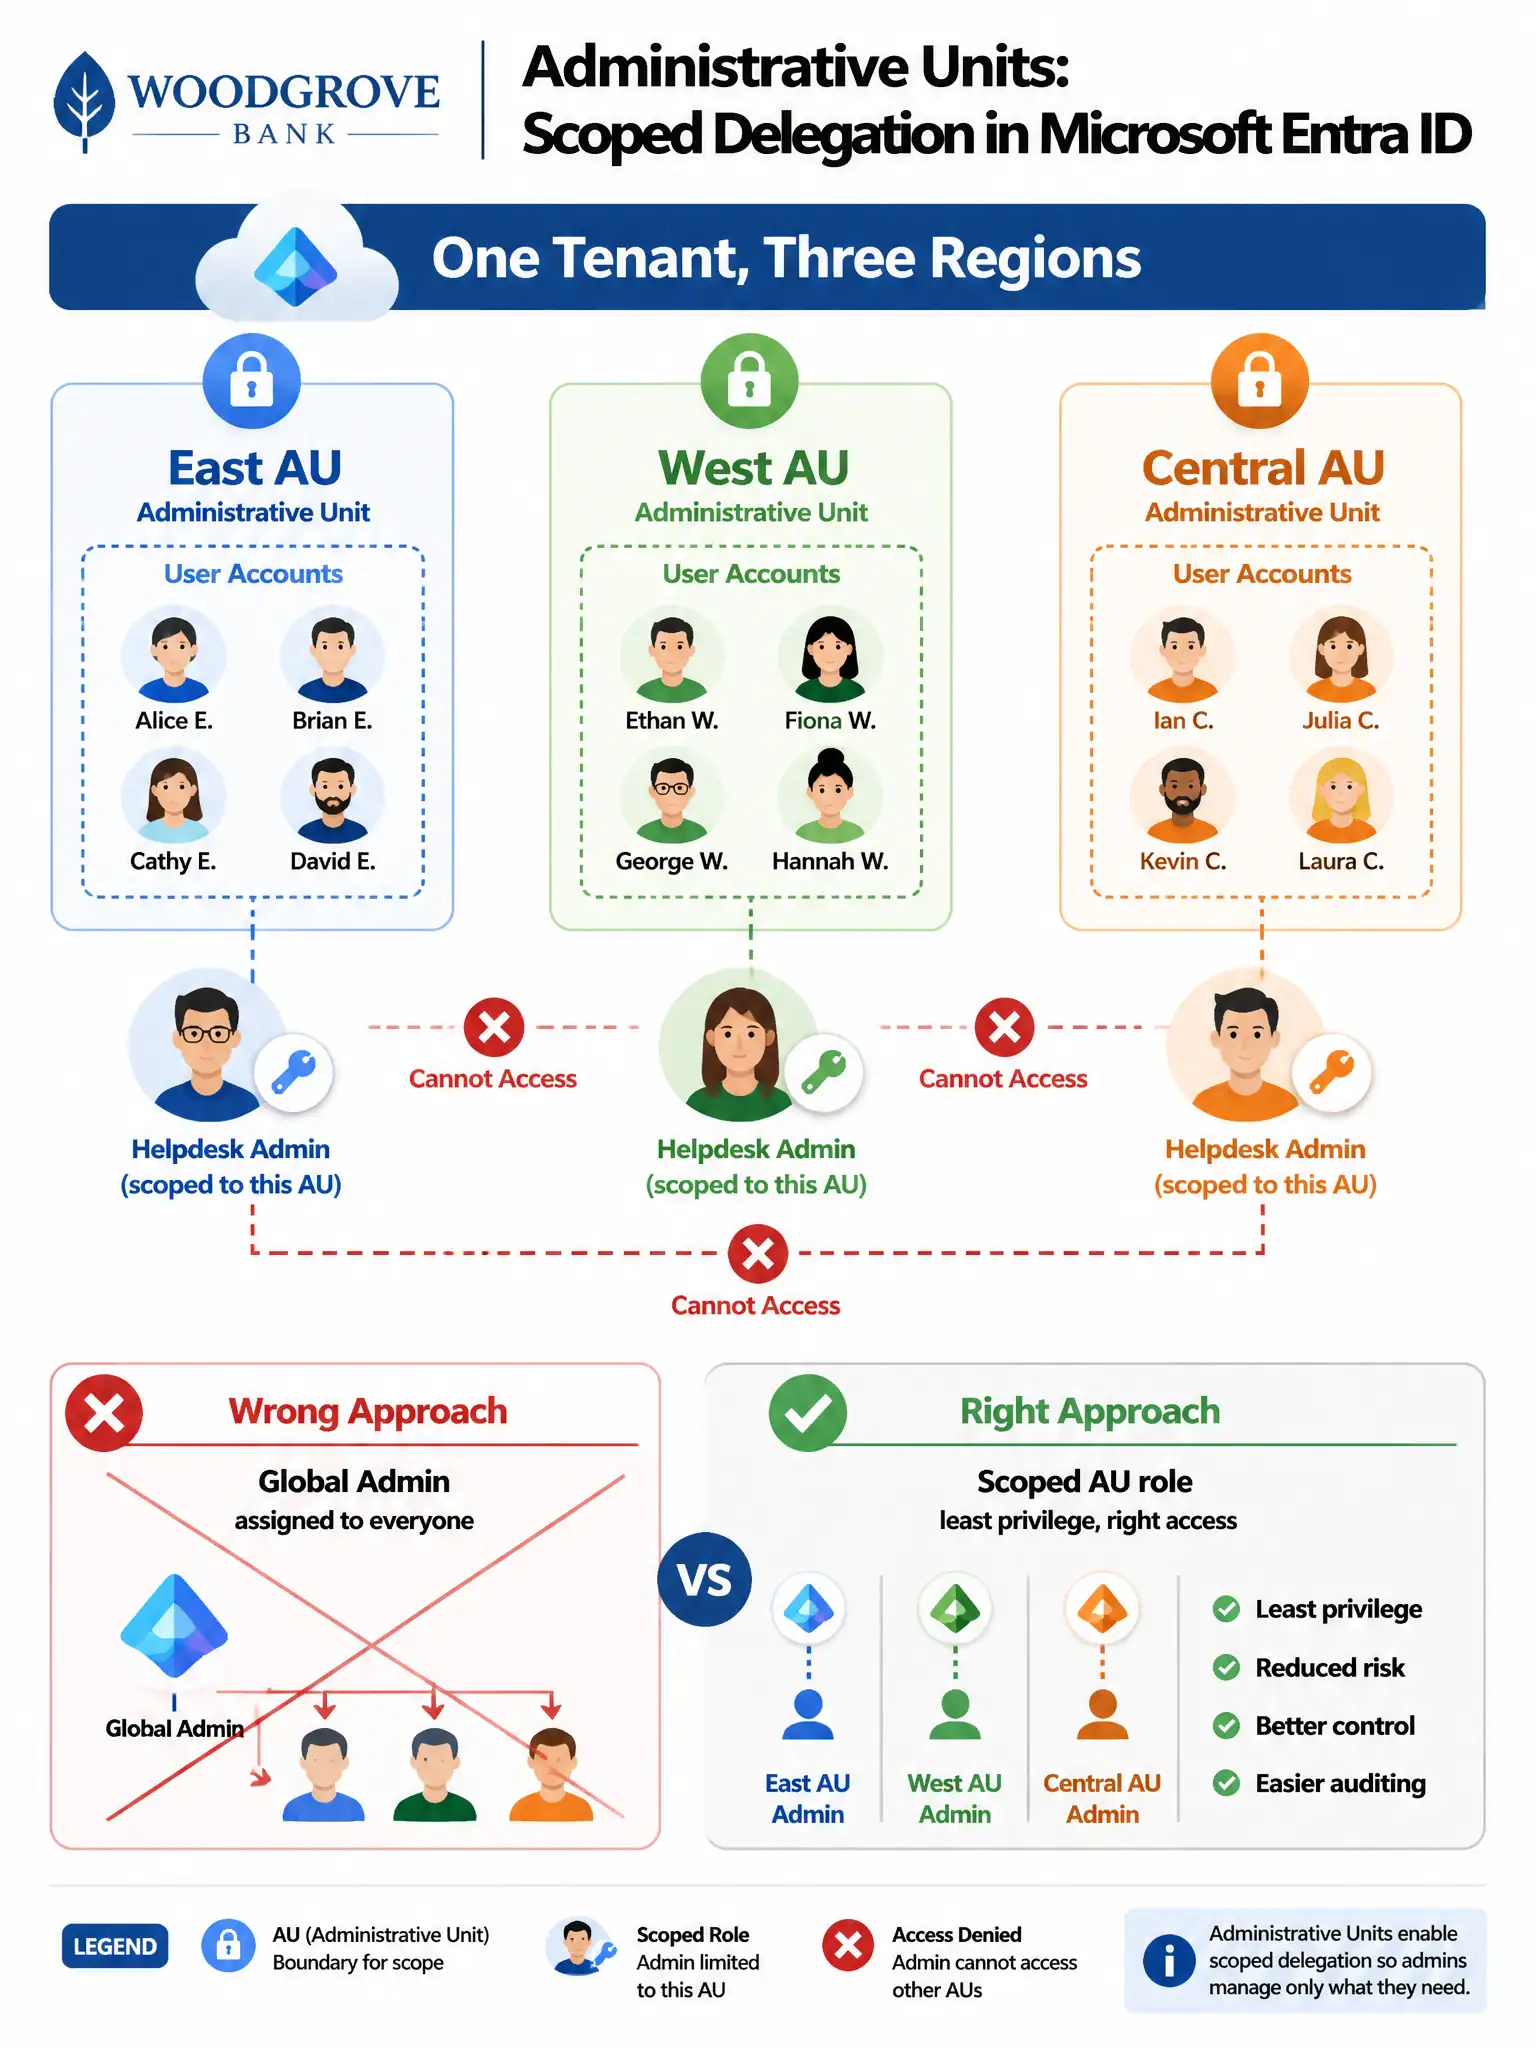
Short Explanation
Administrative units are like department filing cabinets with a lock — only the person with the key for that cabinet can open it. You put each region's users in their own administrative unit, then hand the right IT person only the key to that unit. They can manage everything inside their cabinet but can't even see what's in the others.
Full Explanation
The correct answer is the administrative unit approach: create an administrative unit for each region, assign the regional users to the appropriate administrative unit, and then assign scoped Helpdesk Administrator or User Administrator roles to each regional IT team within their respective administrative unit. Administrative units in Microsoft Entra ID are containers that enable scoped, delegated administration. By placing each region's users into their own administrative unit and assigning directory roles such as Helpdesk Administrator, User Administrator, or Password Administrator scoped to that specific administrative unit, the East IT team's admin rights are limited exclusively to East region users. They cannot accidentally — or intentionally — modify users in other administrative units. This is the purpose administrative units were designed for.
The separate Microsoft Entra tenant approach is wrong because creating separate tenants for each region would create massive management overhead, complicate licensing, and break unified identity. Cross-tenant synchronization is a workaround for multi-tenant scenarios, not a delegation solution within a single organization. The exam tests whether you know the right tool for the right problem.
The security group ownership approach is wrong because group ownership only allows someone to manage the group's membership list — who is in the group. It does not give the IT team the ability to reset passwords, update user profile attributes, enable or disable accounts, or perform other helpdesk tasks that require directory roles. It solves the wrong problem.
The Global Administrator approach is wrong for an obvious but important reason: Global Administrator is the most powerful role in Microsoft Entra, with unrestricted access to everything in the tenant. Assigning it broadly and trusting people to stay in their lane violates the principle of least privilege and would be flagged immediately in any security review. Administrative units exist precisely so you don't have to rely on trust instead of technical controls.
Exam tip: Whenever you see a question about limiting administrative scope within a single tenant by organizational boundary such as region, department, or subsidiary, the answer is almost always administrative units with scoped role assignments.