
A financial services company is deploying a Copilot Studio agent that uses generative AI to answer customer questions about investment products. The compliance team requires that the agent must never generate responses that could be construed as personalized financial advice, must block all responses containing specific competitor product names, and must log every instance where a content filter triggers. Which combination of controls best satisfies all three requirements?
Select an answer to reveal the explanation.
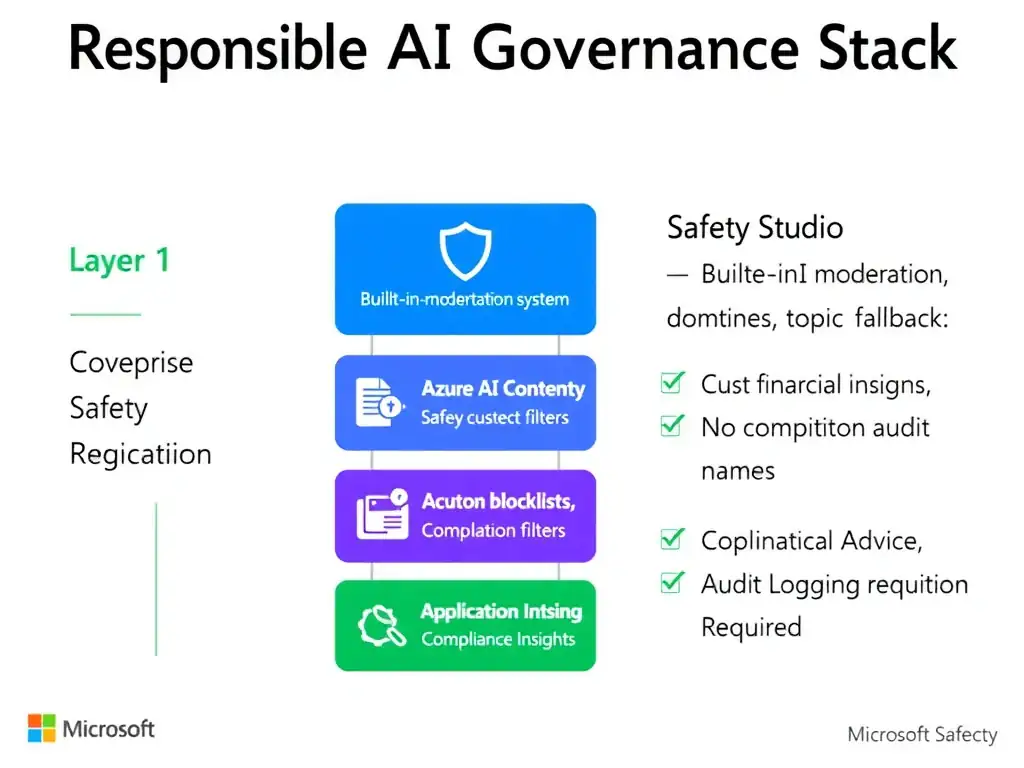
Short Explanation
The bouncer at a club doesn't just check one thing — they check credentials, check the dress code, and write in the log who they turned away. For a regulated Copilot Studio agent, you need a safety system to catch policy violations, a blocklist for specific prohibited content, and auditable logging so compliance can see exactly what was stopped and when.
Full Explanation
This question tests whether you understand that responsible AI governance in production requires multiple complementary controls, not a single mechanism. The compliance requirements map cleanly to three distinct capabilities:
1. Financial advice prohibition: The correct combination uses Copilot Studio's content moderation safety system, plus a custom Azure AI Content Safety resource with a blocklist for competitor names and a custom severity policy for financial/investment advice categories, to apply model-level filtering before content reaches the user. System prompt instructions alone are insufficient because they are guidelines for the model, not enforced filters; sophisticated user prompts can circumvent them.
2. Competitor name blocking: Azure AI Content Safety custom blocklists allow you to define specific terms, phrases, or names that must never appear in responses. This is a deterministic, exact-match control that works independently of the generative model's behavior.
3. Audit trail: Application Insights with custom events is the right mechanism for logging filter triggers in a structured, queryable way. The custom event — such as 'ContentFilterTriggered' with properties including filter type, severity, session identifier, and timestamp — creates the compliance-grade audit trail that can be exported, retained, and reviewed.
The answer that configures Azure AI Content Safety with a custom blocked content list for competitor names, uses Copilot Studio's built-in topic fallback to redirect investment advice questions, and enables Application Insights telemetry to log all session events is partially correct but incomplete. It correctly identifies Azure AI Content Safety and Application Insights, but the topic fallback approach for financial advice is not a content filter — it only catches questions that match a specific topic pattern. Generative responses in other topics could still produce advice-adjacent content.
The answer that writes system prompt instructions prohibiting financial advice and competitor mentions, enables the Copilot Studio safety system prompt, and relies on the generative AI model's training to self-filter inappropriate content is the most dangerous answer. Relying entirely on system prompt instructions and model self-filtering provides no enforcement guarantee and no audit trail — both are hard compliance failures for the financial services firm.
The answer that creates a Power Automate flow that scans every agent response with a text analytics custom classifier before delivery, blocks responses failing classification, and logs failures to a SharePoint list for compliance review is creative but fragile. The synchronous classification call to every response introduces latency and creates the failure mode (what if the flow times out?), and the SharePoint list is not a compliant audit log for most financial regulatory frameworks — it lacks immutability and access controls.
Exam tip: For regulated industries in Copilot Studio exam scenarios, look for answers that combine Copilot Studio's built-in safety system, Azure AI Content Safety as an external enforcement layer, and Application Insights for auditable event logging. All three together constitute the defensible responsible AI posture.