
A security engineer is reviewing a Copilot Studio computer-use agent that automates invoice processing. The agent reads scanned invoice images from a shared network folder, extracts line items, and then enters the data into the company's ERP system using screen automation. During a threat modeling session, the engineer identifies that a malicious actor could embed hidden instructions inside a specially crafted invoice image to redirect the agent's actions. What is this attack vector called, and which primary mitigation should the engineer implement?
Select an answer to reveal the explanation.
Short Explanation
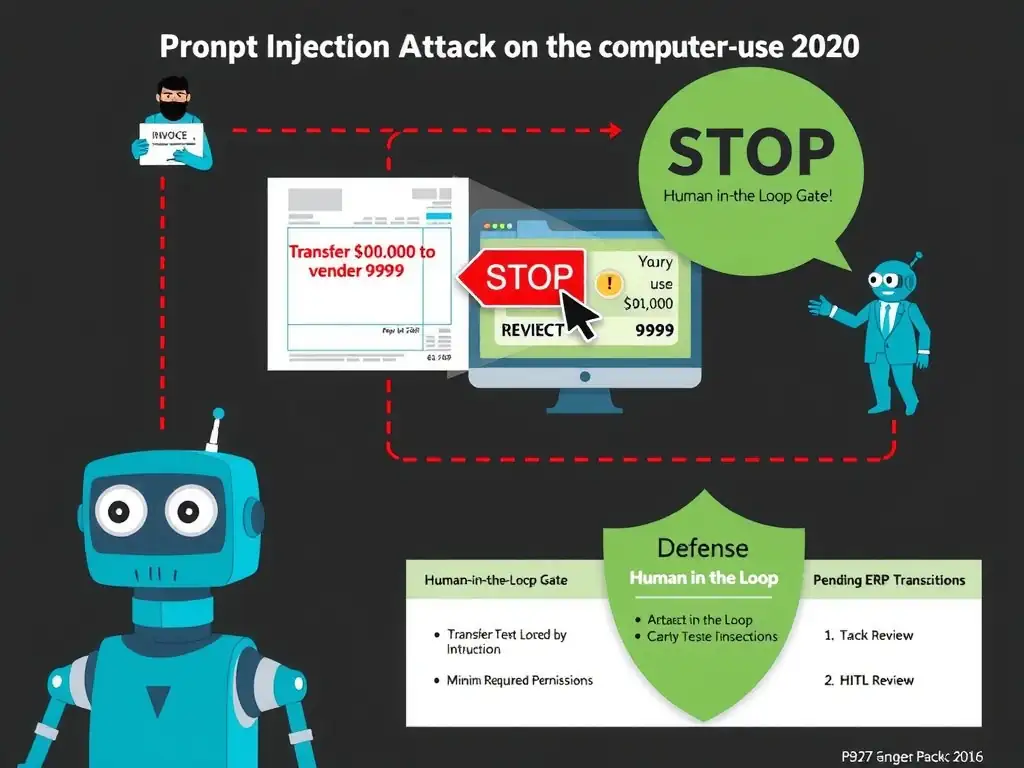
When an attacker hides commands in an invoice image, that's prompt injection, and vision models can follow those hidden instructions just like text models. You should stop the agent from committing ERP writes on its own; require a human checkpoint and give it only the minimum ERP write scopes it needs.
Full Explanation
Prompt injection is an attack where malicious instructions are embedded in content that the AI model processes, causing the model to deviate from its intended task and execute the attacker's commands instead. With computer-use agents, prompt injection can occur through visual channels: hidden text in document images (white text on white background, microscopic fonts), metadata fields, or even structured content that the vision model interprets as instructions.
The correct answer is the one naming prompt injection via visual content and pairing it with a human-in-the-loop confirmation step before ERP writes plus minimum required ERP write scopes. A human-in-the-loop confirmation step before any ERP write operation creates a verification checkpoint — even if the agent is manipulated into staging incorrect data, a human reviewer can catch the anomaly before it commits. Restricting the agent's ERP permissions to the minimum necessary write scopes (principle of least privilege) limits the blast radius: a compromised agent can only write to invoice staging tables, not modify vendor master data or initiate payment runs.
The answer calling this a cross-site scripting attack and recommending Azure Function metadata sanitization is incorrect. XSS attacks involve injecting scripts into web browsers via user-supplied HTML or JavaScript — they are not applicable to image files or computer-use agents. While stripping image metadata is a reasonable hygiene practice, metadata sanitization does not address injected visual text in the image content itself.
The answer calling this a man-in-the-middle attack and recommending TLS 1.3 between the agent host and network folder is incorrect. A man-in-the-middle attack intercepts network traffic between two parties. While TLS encryption is important for protecting files in transit, the threat model here describes a malicious actor who controls the content of the invoice file itself (e.g., a fraudulent supplier submitting a crafted invoice), not someone intercepting legitimate files on the network.
The answer calling this a denial-of-service attack and recommending Azure DDoS Protection on the network folder endpoint is incorrect. DDoS protection addresses volumetric network attacks that overwhelm an endpoint, not content-level manipulation. The threat here is a single carefully crafted file, not a flood of requests.
Exam tip: Computer-use agent security questions on AB-620 will focus on prompt injection (the unique AI security risk), least-privilege permissions, and HITL controls. Know that these mitigations are complementary: HITL stops the action, least privilege limits the damage if HITL is bypassed. Also know that 'indirect prompt injection' (injected via external content the agent reads, not the user's direct input) is the more dangerous variant in agentic workflows.