
A developer has built a Model Context Protocol (MCP) server that exposes inventory lookup tools for a Copilot Studio agent. The MCP server is hosted at https://api.contoso.com/mcp and requires Bearer token authentication. When registering this MCP server in Copilot Studio, which combination of values must be provided during the registration process?
Select an answer to reveal the explanation.
Short Explanation
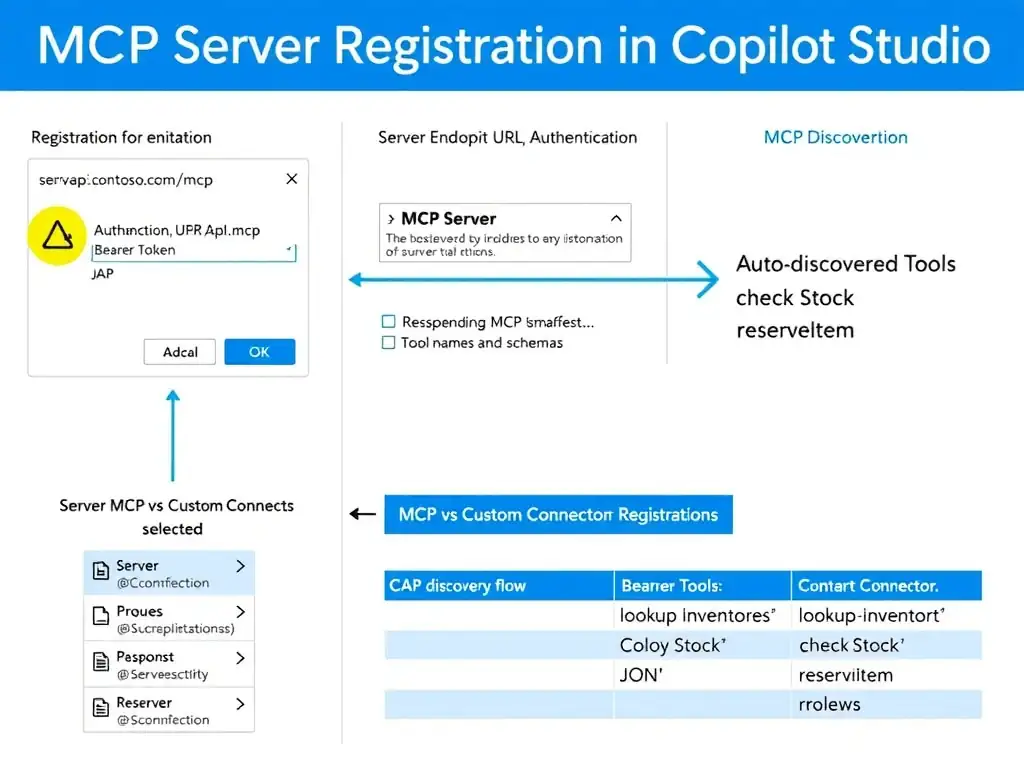
You need the MCP server endpoint URL and the Bearer token authentication setup, including the token value or where Copilot Studio should get it. Copilot Studio discovers the tools automatically from the MCP server, so you don't type the tool list by hand.
Full Explanation
When adding a Model Context Protocol server as a knowledge or action source in Copilot Studio, the platform needs two things: the server's endpoint URL and the authentication method to use when calling it. The endpoint URL tells Copilot Studio where to send its discovery request, which retrieves the tool schema list automatically through the MCP protocol. The authentication configuration tells the runtime how to attach credentials to every subsequent tool call. In this case, that means specifying Bearer token authentication and providing the token value or its source.
Copilot Studio does not require the developer to manually enumerate tool names. The MCP protocol's discovery mechanism, the server manifest, returns all available tools, their schemas, and descriptions automatically when the endpoint is first registered. This is a fundamental design principle of MCP: tools are self-describing.
The option that asks for the server's IP address and port number plus manually entered comma-separated tool names is incorrect because IP address and port are not required; the full URL already contains routing information. Tool names are discovered, not manually entered.
The option that asks for the OpenAPI specification URL for the server and the API subscription key stored in Azure Key Vault is incorrect because MCP registration does not use an OpenAPI specification URL. OpenAPI is used for custom connectors and HTTP actions, not MCP servers. While Azure Key Vault can store secrets, it is not part of the MCP registration form itself.
The option that asks for the Azure resource ID of the MCP server and the managed identity principal ID for role-based access is incorrect because MCP server registration does not use Azure resource IDs or managed identity principal IDs. Managed identity is relevant to Azure-hosted connectors and services but is not the authentication model used in MCP Bearer token authentication flows.
Exam tip: Know the distinction between MCP server registration, which uses the endpoint URL plus authentication configuration, versus custom connector registration, which uses an OpenAPI specification. These are often tested side-by-side as distractors.