
A retail company wants to embed a Copilot Studio customer service agent on their public-facing e-commerce website. The security team requires that the agent can only be reached from web pages the company controls. Which configuration enforces this?
Select an answer to reveal the explanation.
Short Explanation
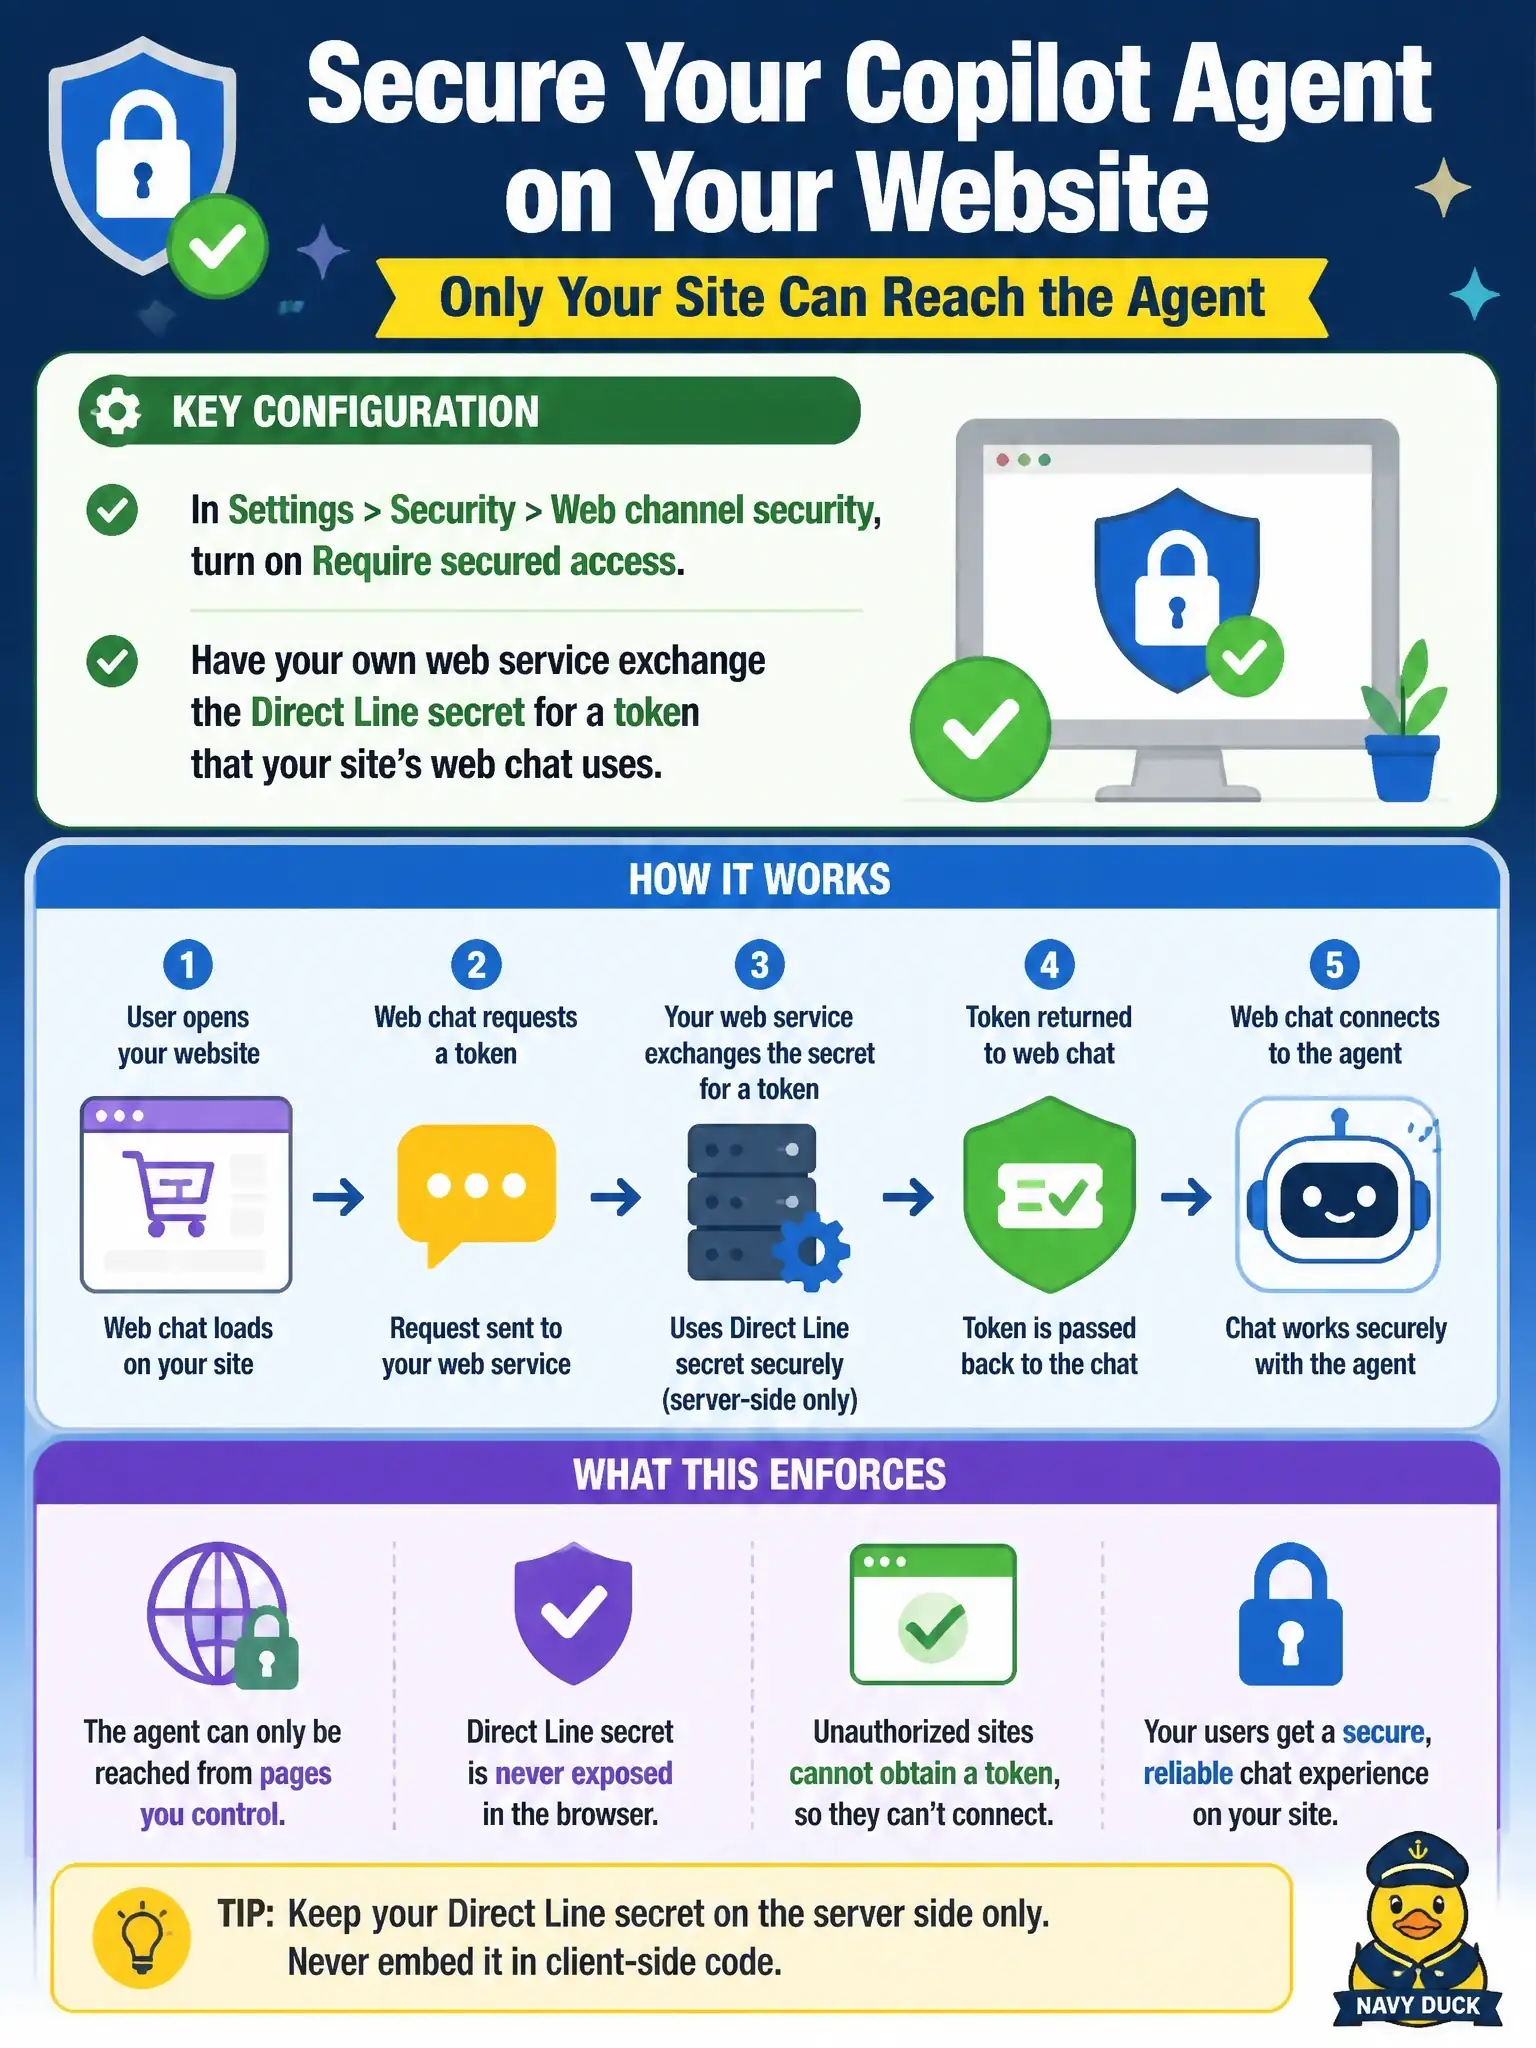
Think of it like a guest list with wristbands: once you turn on Require secured access, the agent only talks to clients that show a Direct Line secret or a token made from one. Your own web service swaps the secret for a short-lived token and hands it to your page, so nobody else's site can just paste in your agent ID and start chatting. There's no domain allowlist to fill in here.
Full Explanation
By default, anyone who knows a Copilot Studio agent's ID can reach it through the Demo website and Custom website channels. Copilot Studio restricts access to locations the company controls through Direct Line-based security: in the agent's Settings, under Security, the Web channel security page has a Require secured access toggle. With it on, every client must authenticate with a Direct Line secret or with a token generated from that secret, and requests without one fail. Because the web chat runs in the browser, the secret must never be placed in page code; the company's own server exchanges it for a token that is valid for a single conversation and must be refreshed before it expires. An Allowed domains list in the Custom website channel sounds plausible, but Copilot Studio documents no domain or origin allowlist, so that setting does not exist to enforce anything. Turning authentication off and adding a Content Security Policy header only controls how the company's own pages may be framed, and it leaves the agent openly reachable by anyone with its ID. Publishing only to Teams abandons the public web experience instead of securing it. Exam caveat: toggling secured access can take up to two hours to propagate, and the previous setting stays in effect until then. Operational check: after the change propagates, confirm the Demo website no longer connects, while the company site still loads a conversation using a server-issued token.