
Developers can edit an agent in the maker portal, but frontline users only need to chat with the published agent in Teams. How should access generally be separated?
Select an answer to reveal the explanation.
Short Explanation
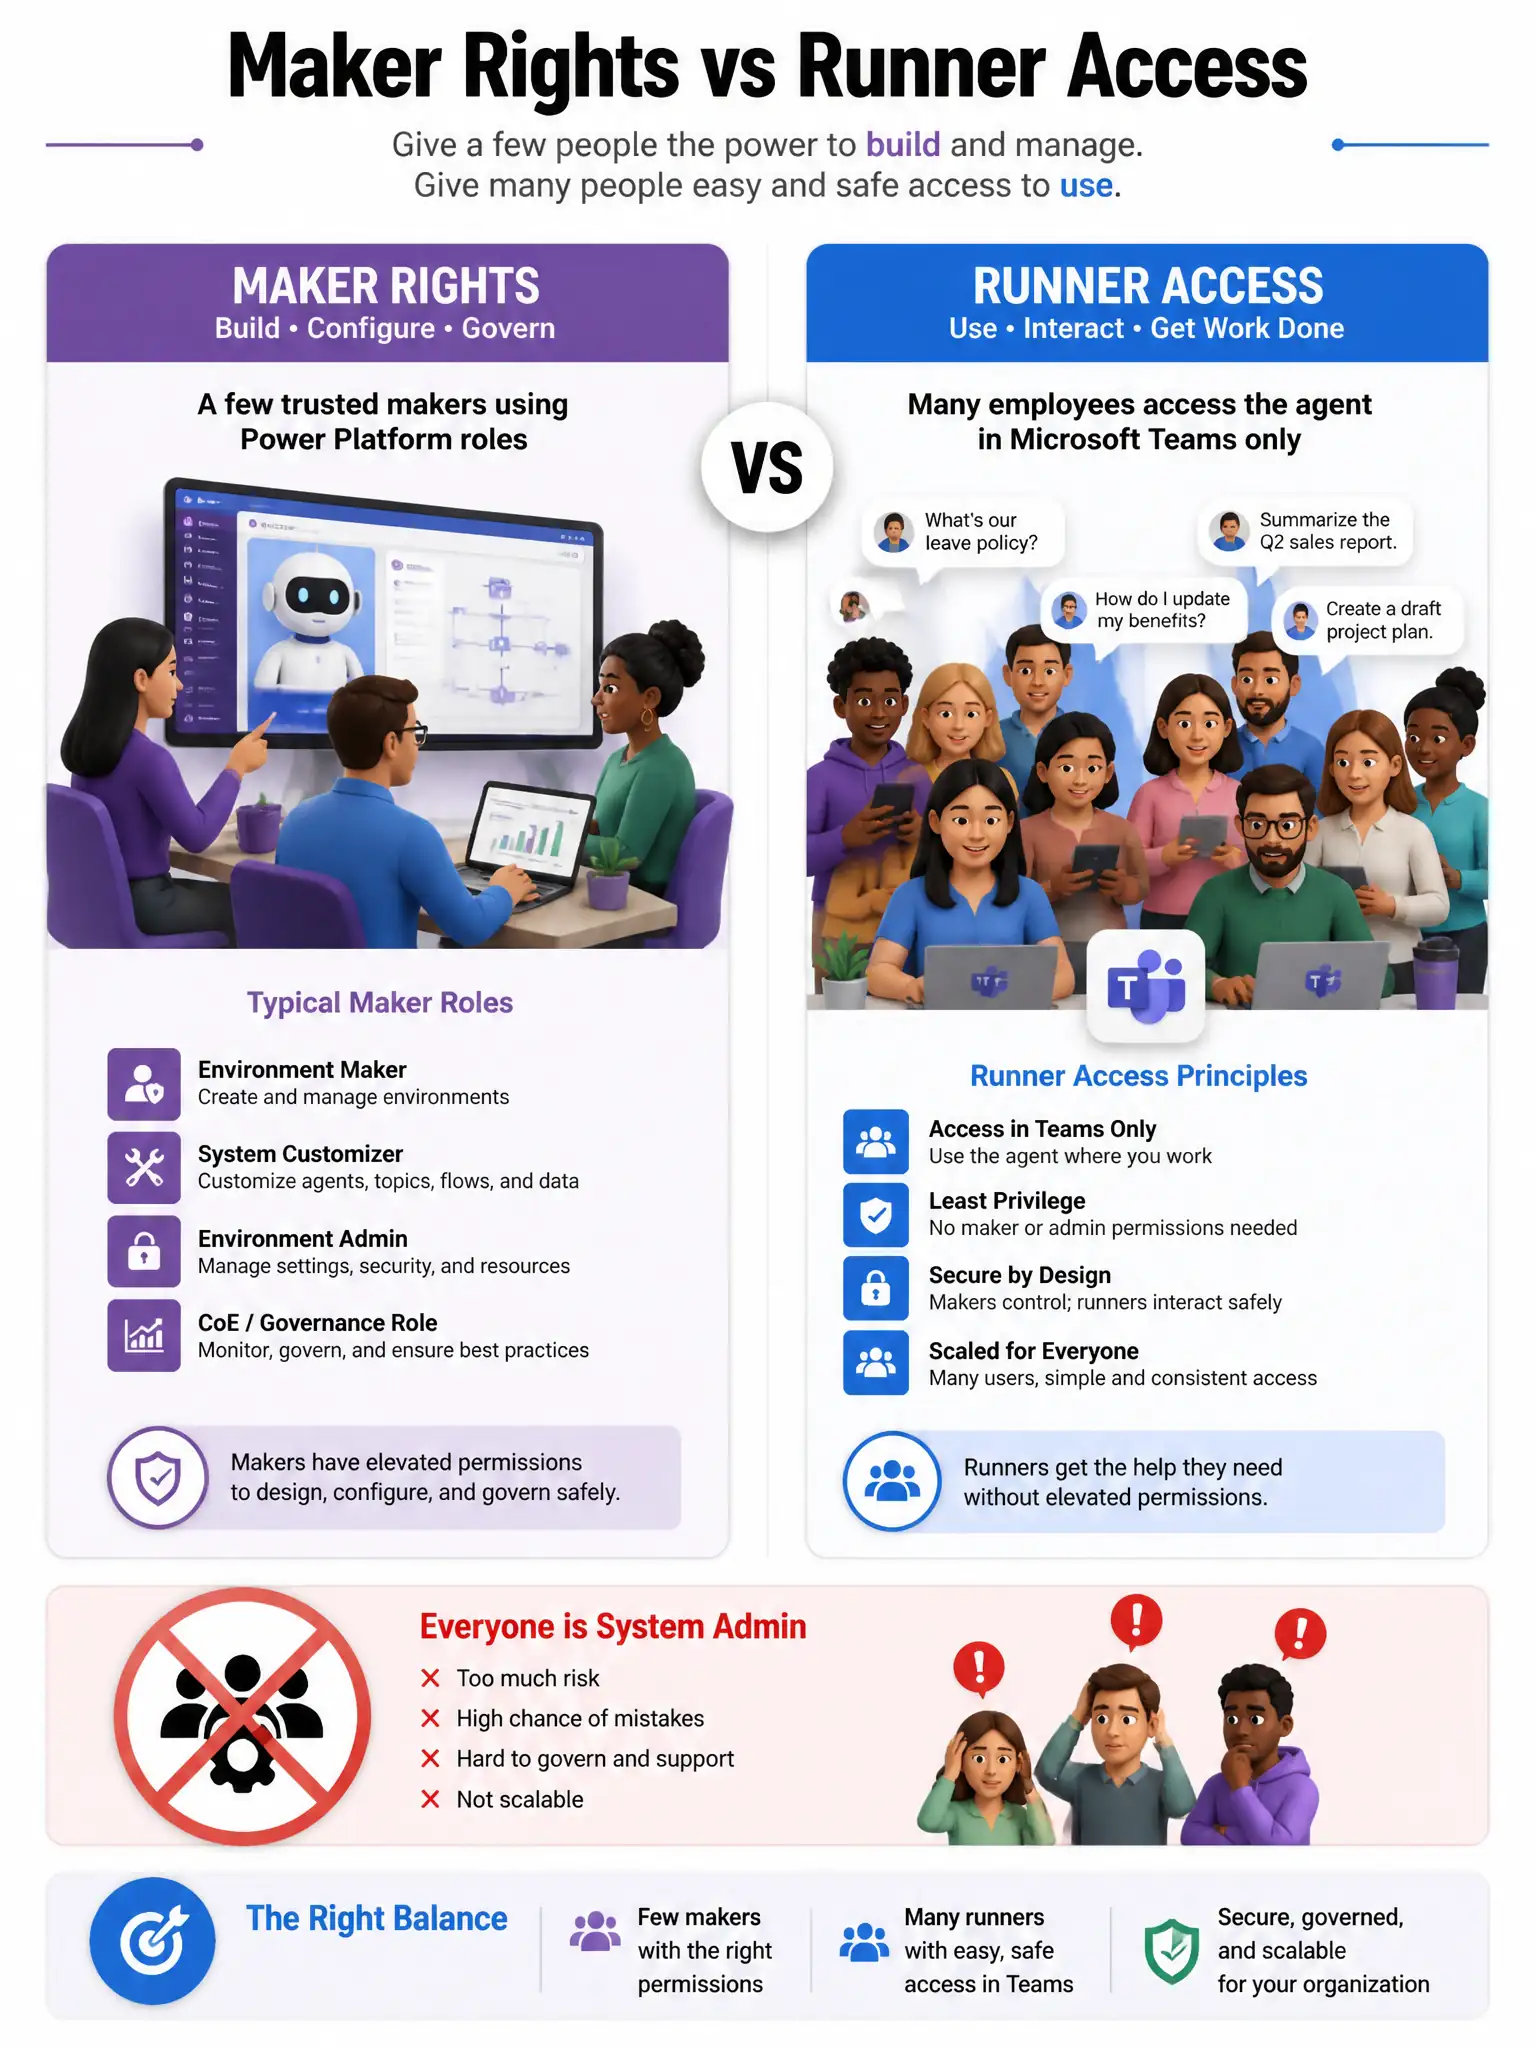
Builders get the workshop keys (maker roles); employees just use the finished robot in Teams. Making everyone System Administrator is how Production gets DIY rewiring.
Full Explanation
Least privilege separates maker rights from runtime channel usage. End users need access to the bot/app, not environment admin roles. Granting maker/admin roles only to builders in the environment, while giving end users channel access to the published agent, is correct. Giving every employee System Administrator on Production violates least privilege. Removing all security roles from makers breaks ALM/authorship. Storing maker credentials in the welcome message is a credential exposure anti-pattern. Exam tip: Environment roles ≠ channel chat permission; design both deliberately.