
Your Copilot Studio agent is deployed on both the public company website (unauthenticated) and the internal Microsoft Teams channel (authenticated). From a security governance perspective, which statement correctly describes a key difference in what these two deployments should be allowed to do?
Select an answer to reveal the explanation.
Short Explanation
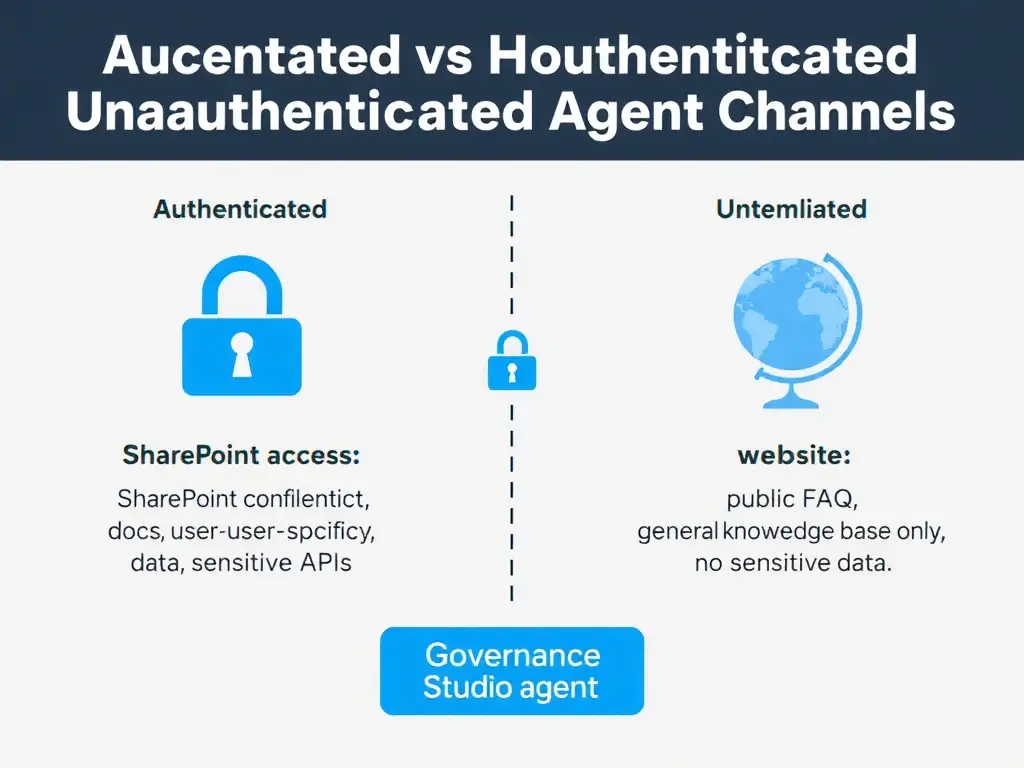
An authenticated channel knows who it's talking to, so it can unlock the filing cabinet. An unauthenticated channel is talking to a stranger at the front desk, so it should only hand over the public brochure. You need different permission scopes for these personas.
Full Explanation
Copilot Studio allows you to publish agents to multiple channels simultaneously. Authenticated channels, such as the internal Microsoft Teams channel, SharePoint internal, or custom deployments with single sign-on, have a verified user identity. That identity enables the agent to access user-specific data, trigger actions on behalf of that user, and retrieve documents the user is authorized to see, such as through delegated authentication to SharePoint. Unauthenticated channels, such as the public company website widget or demo environments, have no identity context. From a governance perspective, these should be configured to access only publicly available information, such as public knowledge bases, frequently asked question content, and generic company information. They should not have access to SharePoint libraries with sensitive content, user-specific records, or sensitive application programming interface actions. The statement that unauthenticated channels can access confidential SharePoint documents because no login barrier exists is a critical misconception. Unauthenticated channels should have less access, not more, precisely because there is no identity verification. The statement that both channels share identical permissions because the agent itself is a single entity is wrong. The governance best practice is to scope each channel's access appropriately to its authentication context. The statement that unauthenticated channels automatically apply data-loss-prevention policies, making them equally secure as authenticated channels, is incorrect. Data-loss-prevention policies apply to connector usage regardless of channel authentication, but they do not make unauthenticated access as secure as authenticated access. Exam governance principle: authentication context determines data access scope. Configure knowledge sources, application programming interface actions, and connector permissions per channel based on the authentication model of that channel.