
An Azure Function uses its system-assigned managed identity to read secrets from Azure Key Vault successfully. Using the same identity, it acquires a token for https://contoso.crm.dynamics.com/.default, but every Dataverse Web API call returns 401 Unauthorized. What is the most likely cause?
Select an answer to reveal the explanation.
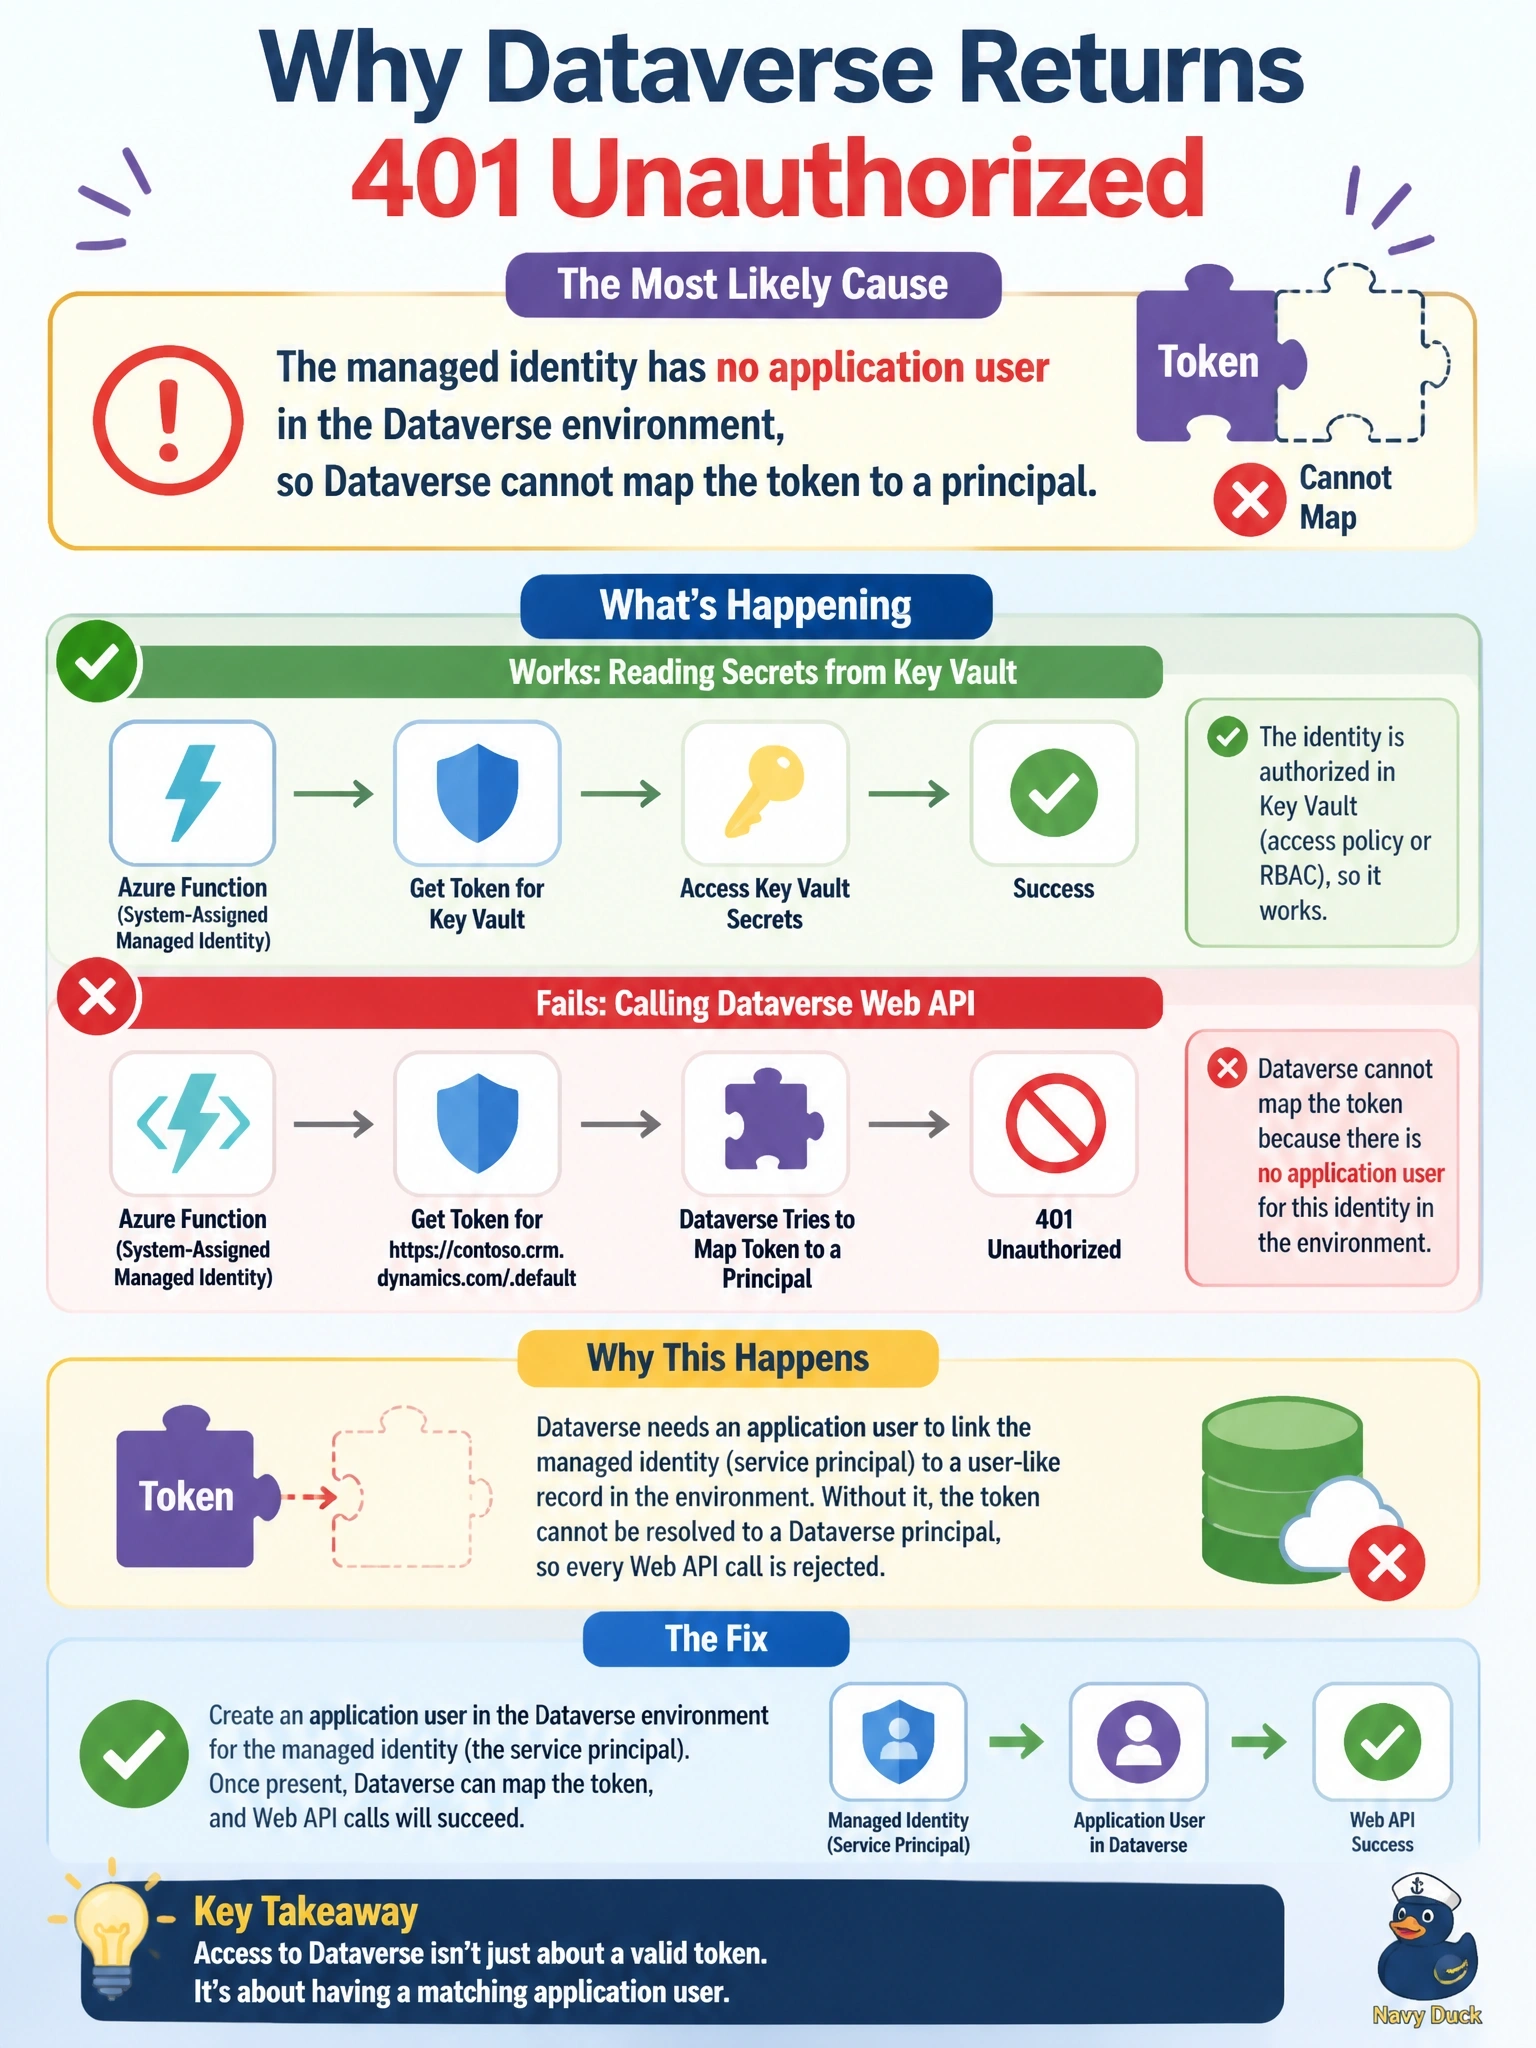
Short Explanation
Key Vault saying yes doesn't mean Dataverse knows who you are. Each service keeps its own guest list, and Dataverse's list is the application user. Add one for the managed identity and the 401s go away; the trap is thinking managed identities just can't talk to Dataverse.
Full Explanation
A managed identity is a service principal in Microsoft Entra ID, and any resource that accepts Entra ID tokens can authorize it. Key Vault grants access through its own access policies or Azure RBAC, which explains why secret reads succeed. Dataverse authorizes requests separately: it maps the application ID in the token to an application user in the environment and evaluates that user's security roles. If no application user exists for the managed identity, Dataverse has nothing to bind the token to and rejects the call even though the token is valid and correctly scoped to the environment URL. Creating the application user with the managed identity's application ID and assigning a security role resolves it. Managed identities are not limited to Azure resource providers; Dataverse supports them, so a separate app registration with a secret is unnecessary. Tokens are not consumed per resource; the identity can obtain tokens for any number of audiences. An Azure Resource Manager token has the wrong audience, and Dataverse does not validate tokens through Resource Manager; the environment URL scope the function already uses is correct. Exam caveat: once the application user exists, missing table privileges show up as privilege errors rather than 401. Operational check: look up the identity's application ID in Entra ID and confirm an application user with the same ID exists.