
Counters on a source leaf show VXLAN packets leaving, but the remote leaf shows no corresponding VXLAN ingress or decap. What troubleshooting approach helps?
Select an answer to reveal the explanation.
Short Explanation
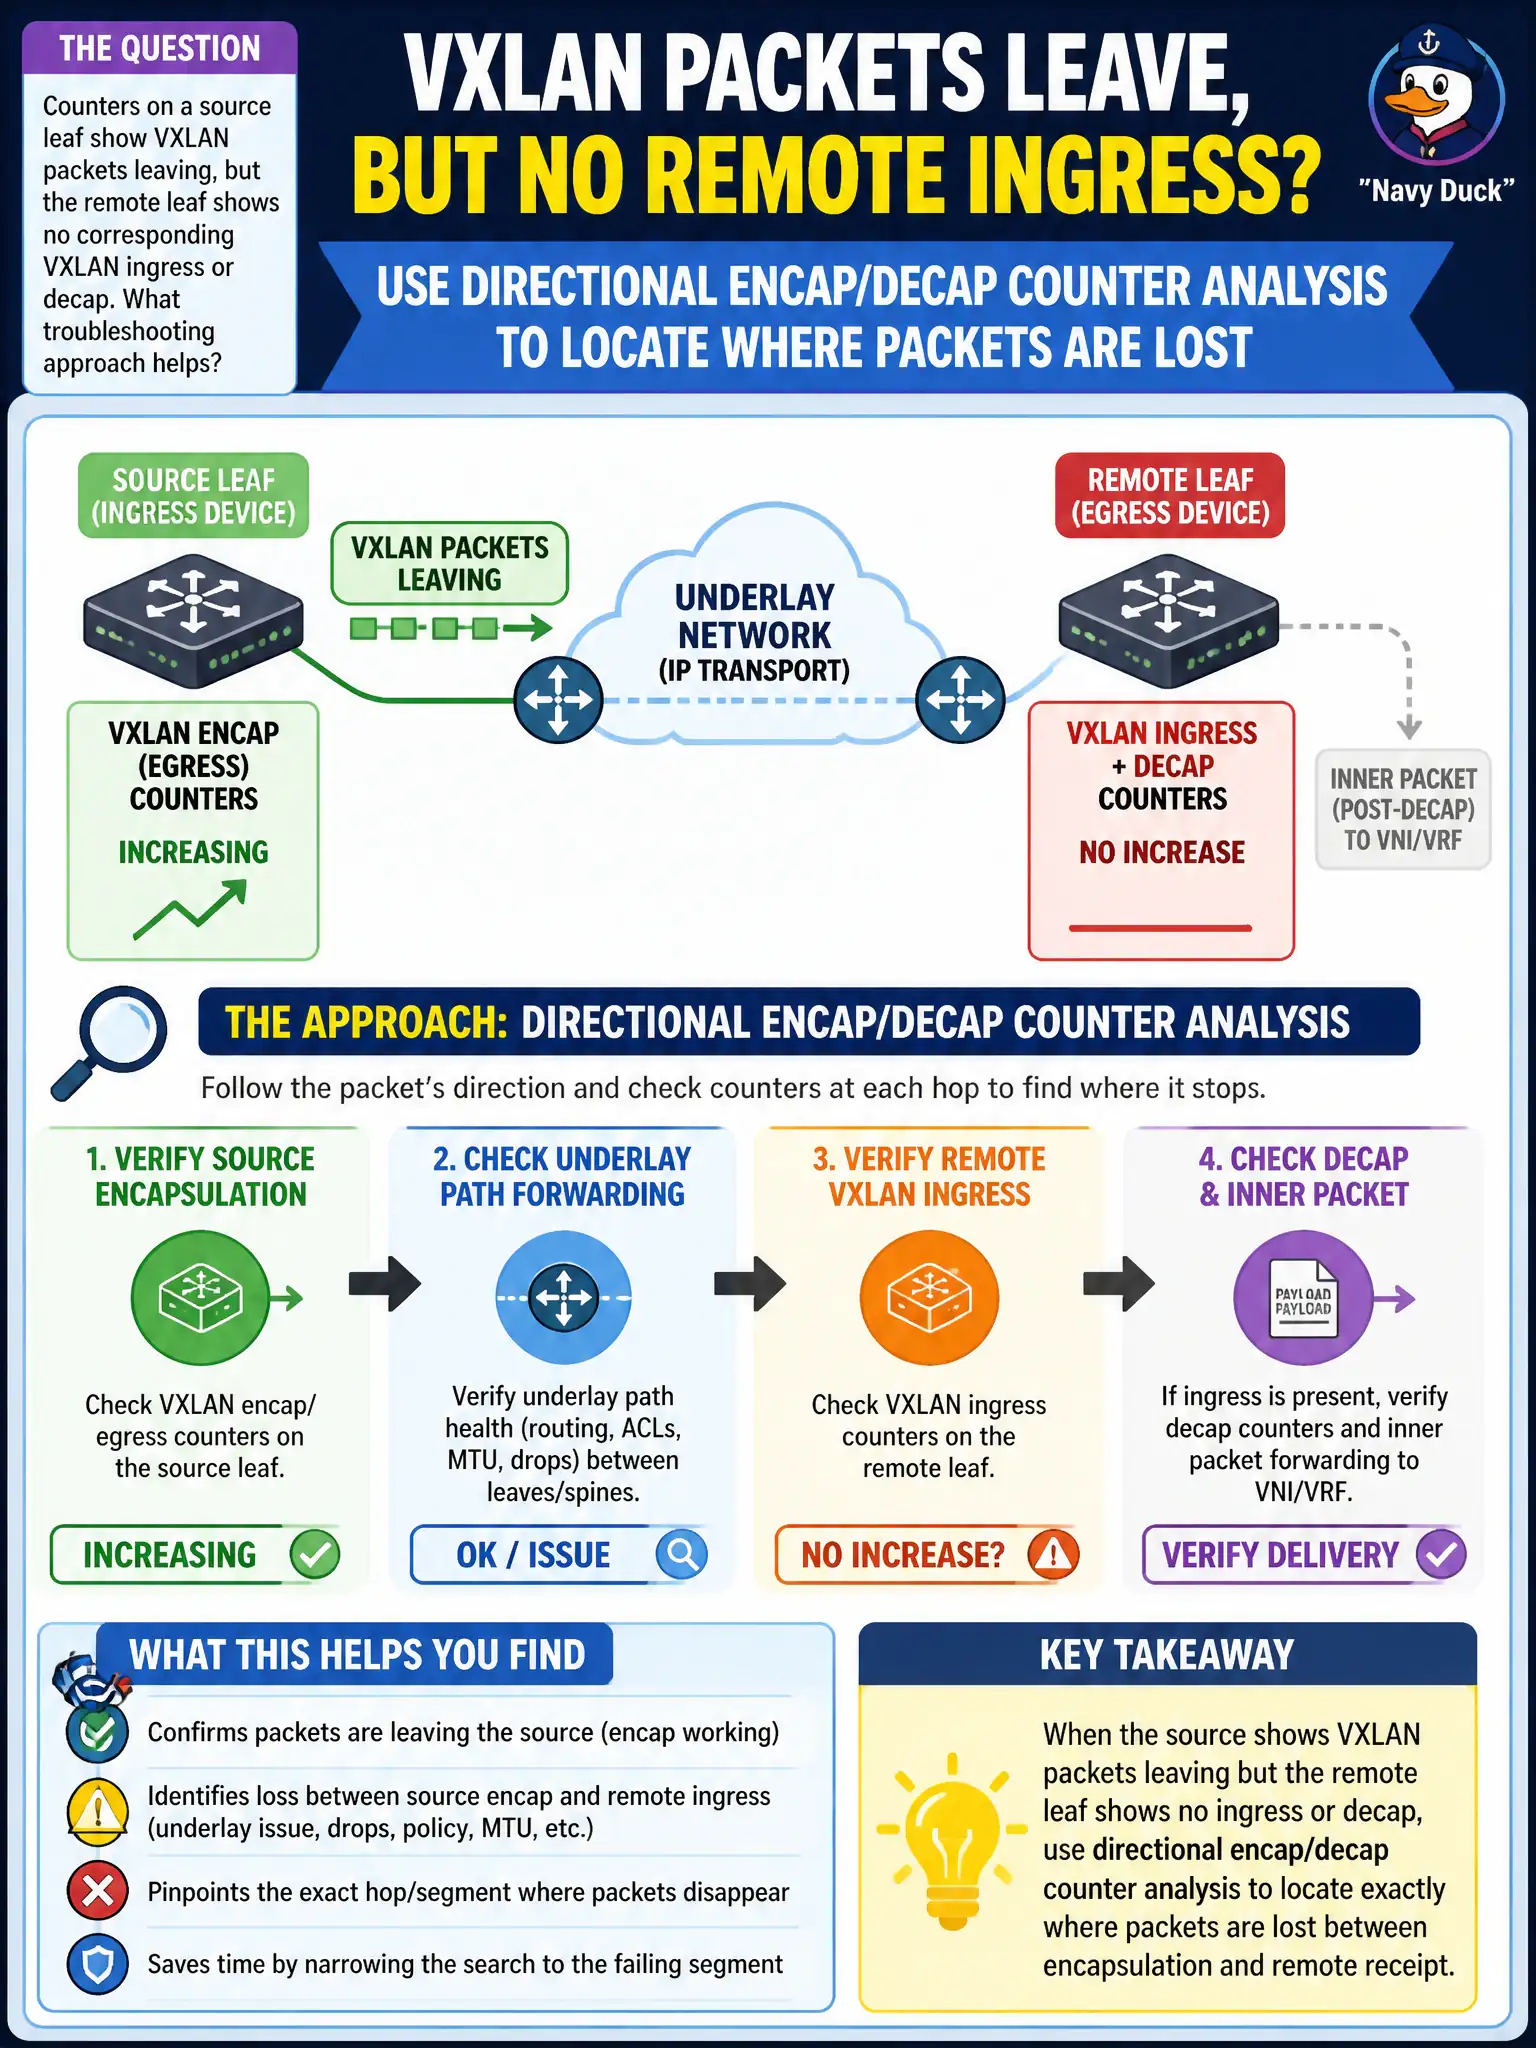
One side says ‘we shipped it,’ the other says ‘never saw it’—that’s a path mystery, not a MAC-flush festival. Compare directional VXLAN counters hop by hop to find where the boxes vanish. Asymmetry points at underlay or mid-path filters.
Full Explanation
Counters on a source leaf showing VXLAN packets leaving while the remote leaf shows no corresponding VXLAN ingress or decap call for directional encap/decap counter analysis to locate where packets are lost between ingress encapsulation and remote receipt. Asymmetric counters suggest loss or misdirection in the underlay path, ACL/firewall filters, or incorrect outer addressing.
Ignoring counters and rebooting every spine on a fixed weekly schedule does not replace methodical correlation. Averaging the two leaves’ CPU temperatures does not estimate overlay loss. Clearing all MAC tables city-wide before reading any interface statistics destroys useful state and skips counter analysis.
Exam caveat: directional VXLAN counter correlation is especially useful in multi-hop civic Clos topologies.
Operational check: record encap on source and ingress/decap on destination, hop along underlay path looking for drops or filters on UDP/4789, fix the loss point, and confirm counters rebalance before clearing MACs. Automate a paired counter poll for VTEP pairs used by critical municipal applications. Preserve counter snapshots in the incident timeline before any disruptive clears. Record the validated outcome in the municipal fabric runbook for the next change window.