
Developers want to add an obscure open-source package, maintained by a single anonymous contributor and last updated four years ago, to a cloud application that handles payments. What should the cloud security professional require before approval?
Select an answer to reveal the explanation.
Short Explanation
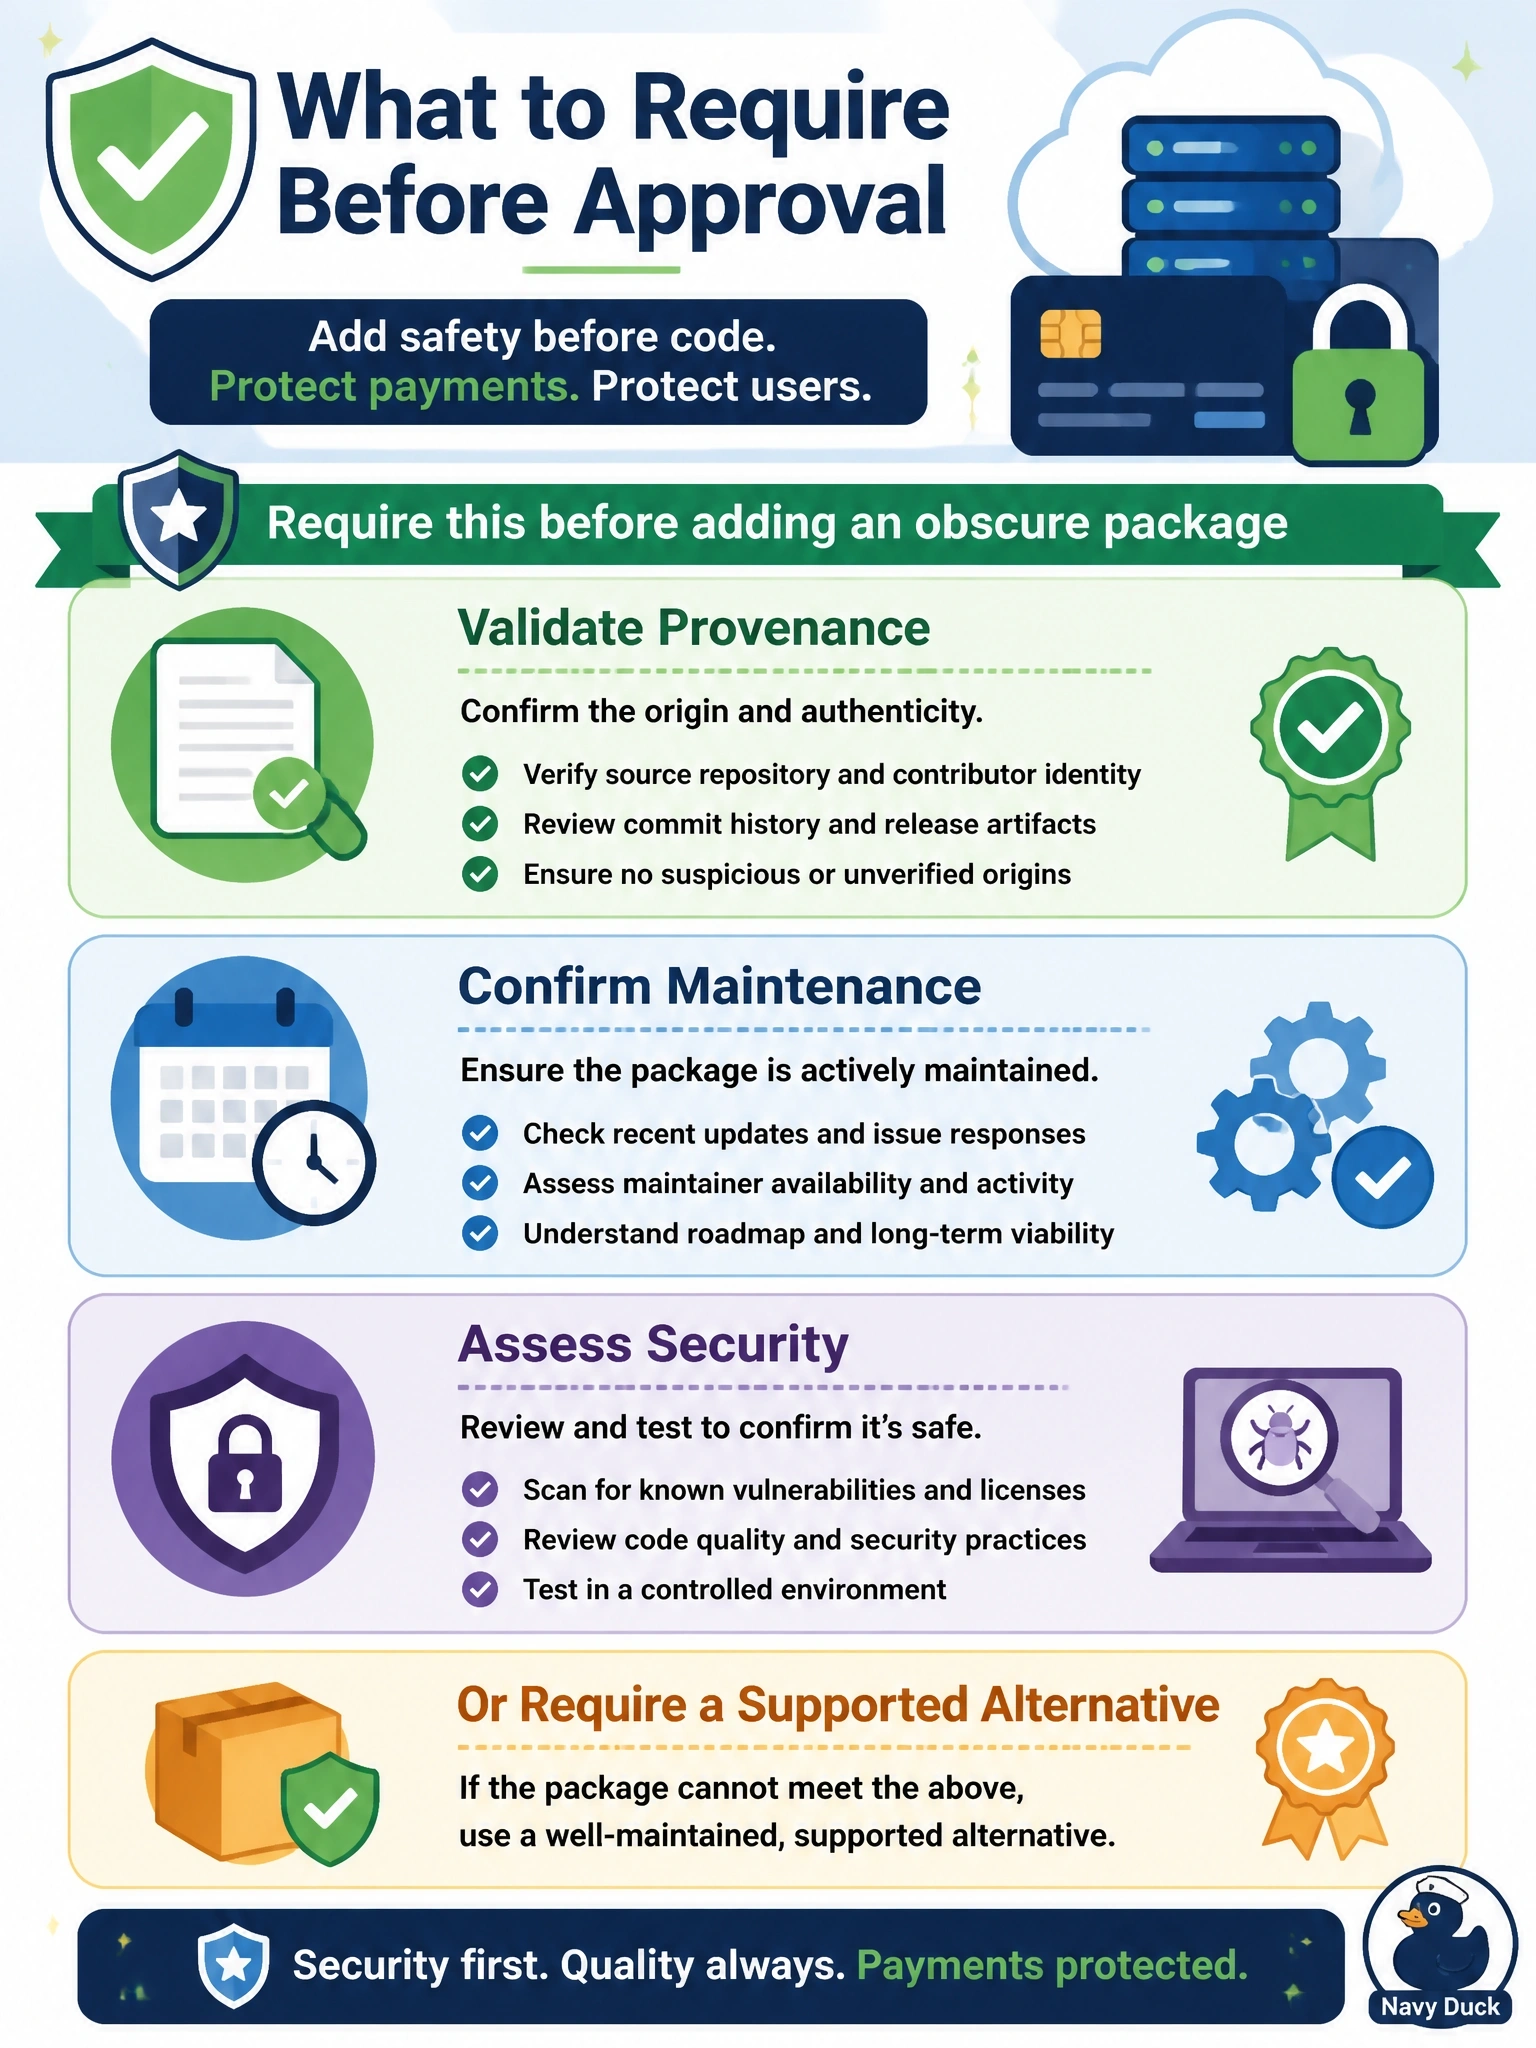
'Anyone can read the code' doesn't mean anyone did. An abandoned package from an unknown author needs you to check where it came from, whether anybody maintains it, and whether it holds up under review and testing, or you pick something supported. No CVEs on a package nobody looks at isn't good news; it's no news.
Full Explanation
Using validated open-source software means confirming that a component is fit for use before trusting it, especially in a payment application. Validation covers provenance, meaning where the package comes from, who publishes it and whether releases are signed; maintenance, meaning recent activity, responsiveness to issues and the number of maintainers; and security, meaning code review, static analysis, software composition analysis of its own dependencies and testing in context. If the package cannot be validated, a maintained alternative, or bringing the needed function in house, is the safer route. The assumption that public code has been widely reviewed is the many-eyes fallacy; obscure packages often have almost no reviewers. A commercial support contract with an anonymous single maintainer is unlikely to be obtainable, and a contract would not by itself establish that the existing code is safe. A clean CVE record is weak evidence for a rarely used, unmaintained package, because vulnerabilities are reported when researchers look and maintainers respond, and neither condition applies here; absence of reports is not evidence of security. Exam caveat: the 2026 outline frames this under using verified secure software, so the exam favors verification and governance over blanket bans or blind trust. Operational check: record the validation results and approval in the component register, pin the reviewed version, and set SCA alerts for the package and its dependencies.