
A machine learning team wants to deploy a pre-trained model file downloaded from a shared internal model repository that many teams can write to. The security architect notes that model files can be tampered with and that some serialization formats can execute code when loaded. What control should be required before the model is deployed to production?
Select an answer to reveal the explanation.
Short Explanation
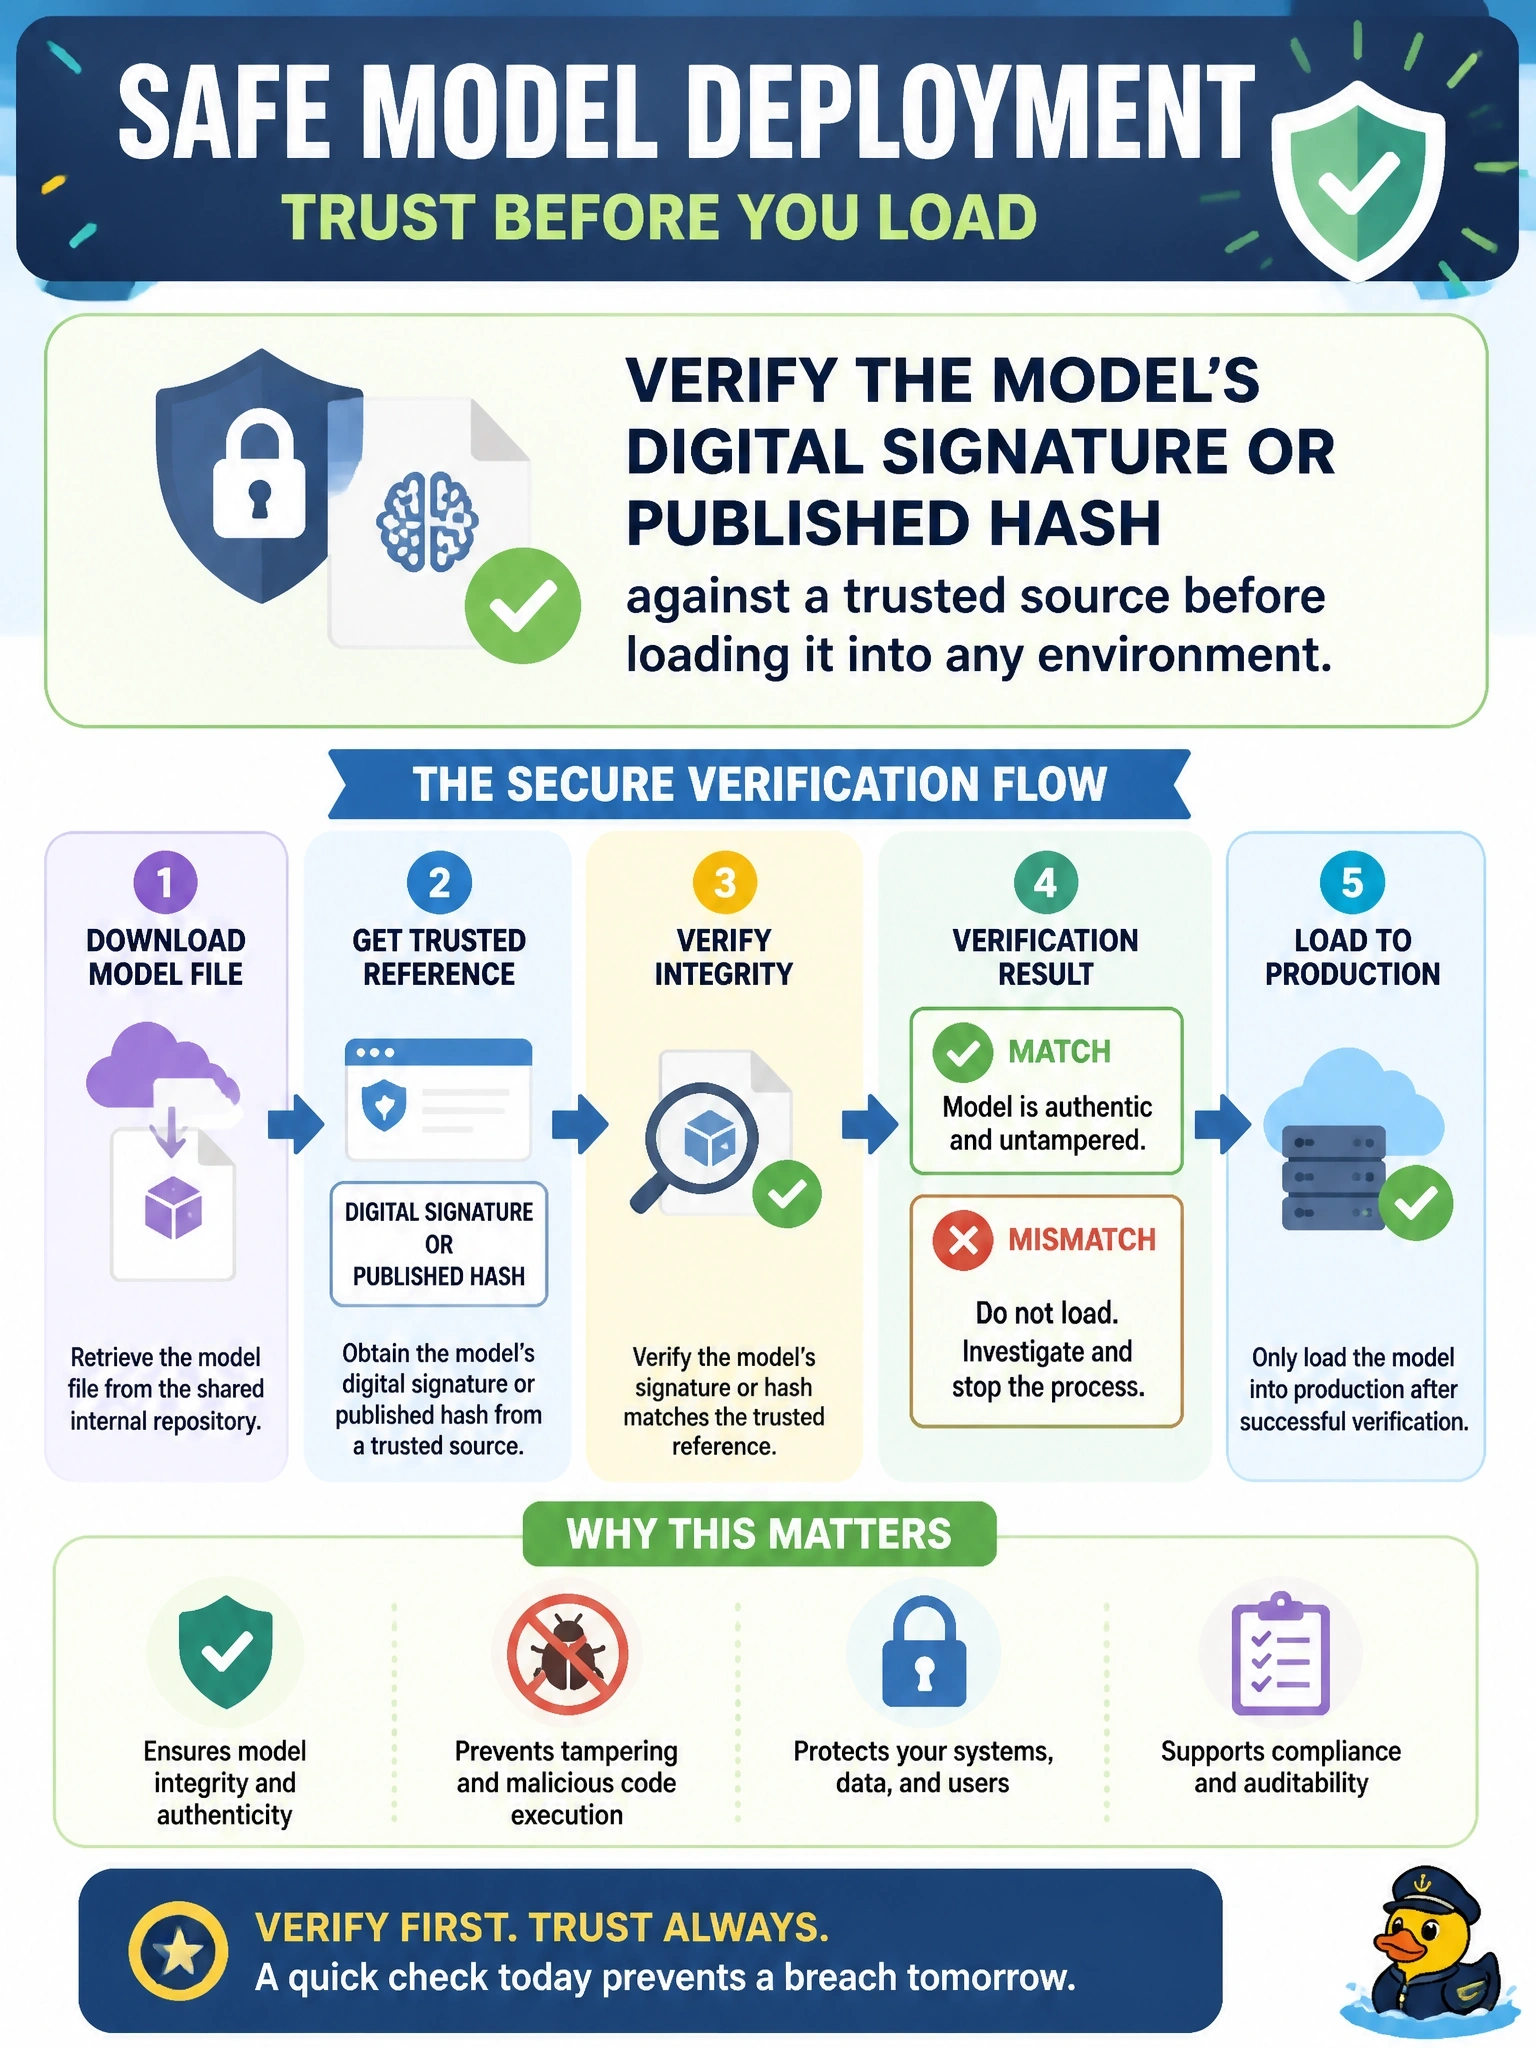
You wouldn't install software from a share anyone can write to without checking the signature, and a model file deserves the same respect. Verify the signature or hash against a trusted source before you load it, because loading is exactly when a booby-trapped file goes off. Antivirus looks only for known bad patterns, and a crafted model isn't on its list.
Full Explanation
Model security includes verifying the integrity and provenance of model artifacts before use. When a repository is writable by many parties, any file could have been replaced or modified. Signing models at the point of creation and verifying the signature, or comparing a hash against a value published through a separate trusted channel, proves the file is exactly what the authorized producer released. This matters doubly because certain serialization formats execute embedded code during deserialization, so a tampered file can compromise the host the moment it is loaded. Antivirus scanning relies on known signatures and heuristics; a malicious payload crafted for a model format is unlikely to match, so a clean scan does not establish integrity or origin. An API gateway with rate limiting protects the deployed inference endpoint from abuse such as extraction or denial of service, but it acts after deployment and says nothing about whether the model itself is trustworthy. Encrypting the file at rest protects confidentiality in storage, yet anyone with write access can still replace it, and an encrypted malicious model is still malicious. Exam caveat: integrity verification belongs to the supply chain for models just as it does for software packages. Operational check: confirm the deployment pipeline rejects any model whose signature fails verification.