
Executives want a framework focused on the governance and management of enterprise information and technology, aligning IT with stakeholder goals, rather than a catalogue of technical controls. Which framework BEST fits this need?
Select an answer to reveal the explanation.
Short Explanation
When the executives say 'governance of enterprise IT,' that's COBIT waving at you. The others are all about which controls to put in place, which is useful, but it isn't what they asked for. The trap is picking the most famous control catalogue just because it's big.
Full Explanation
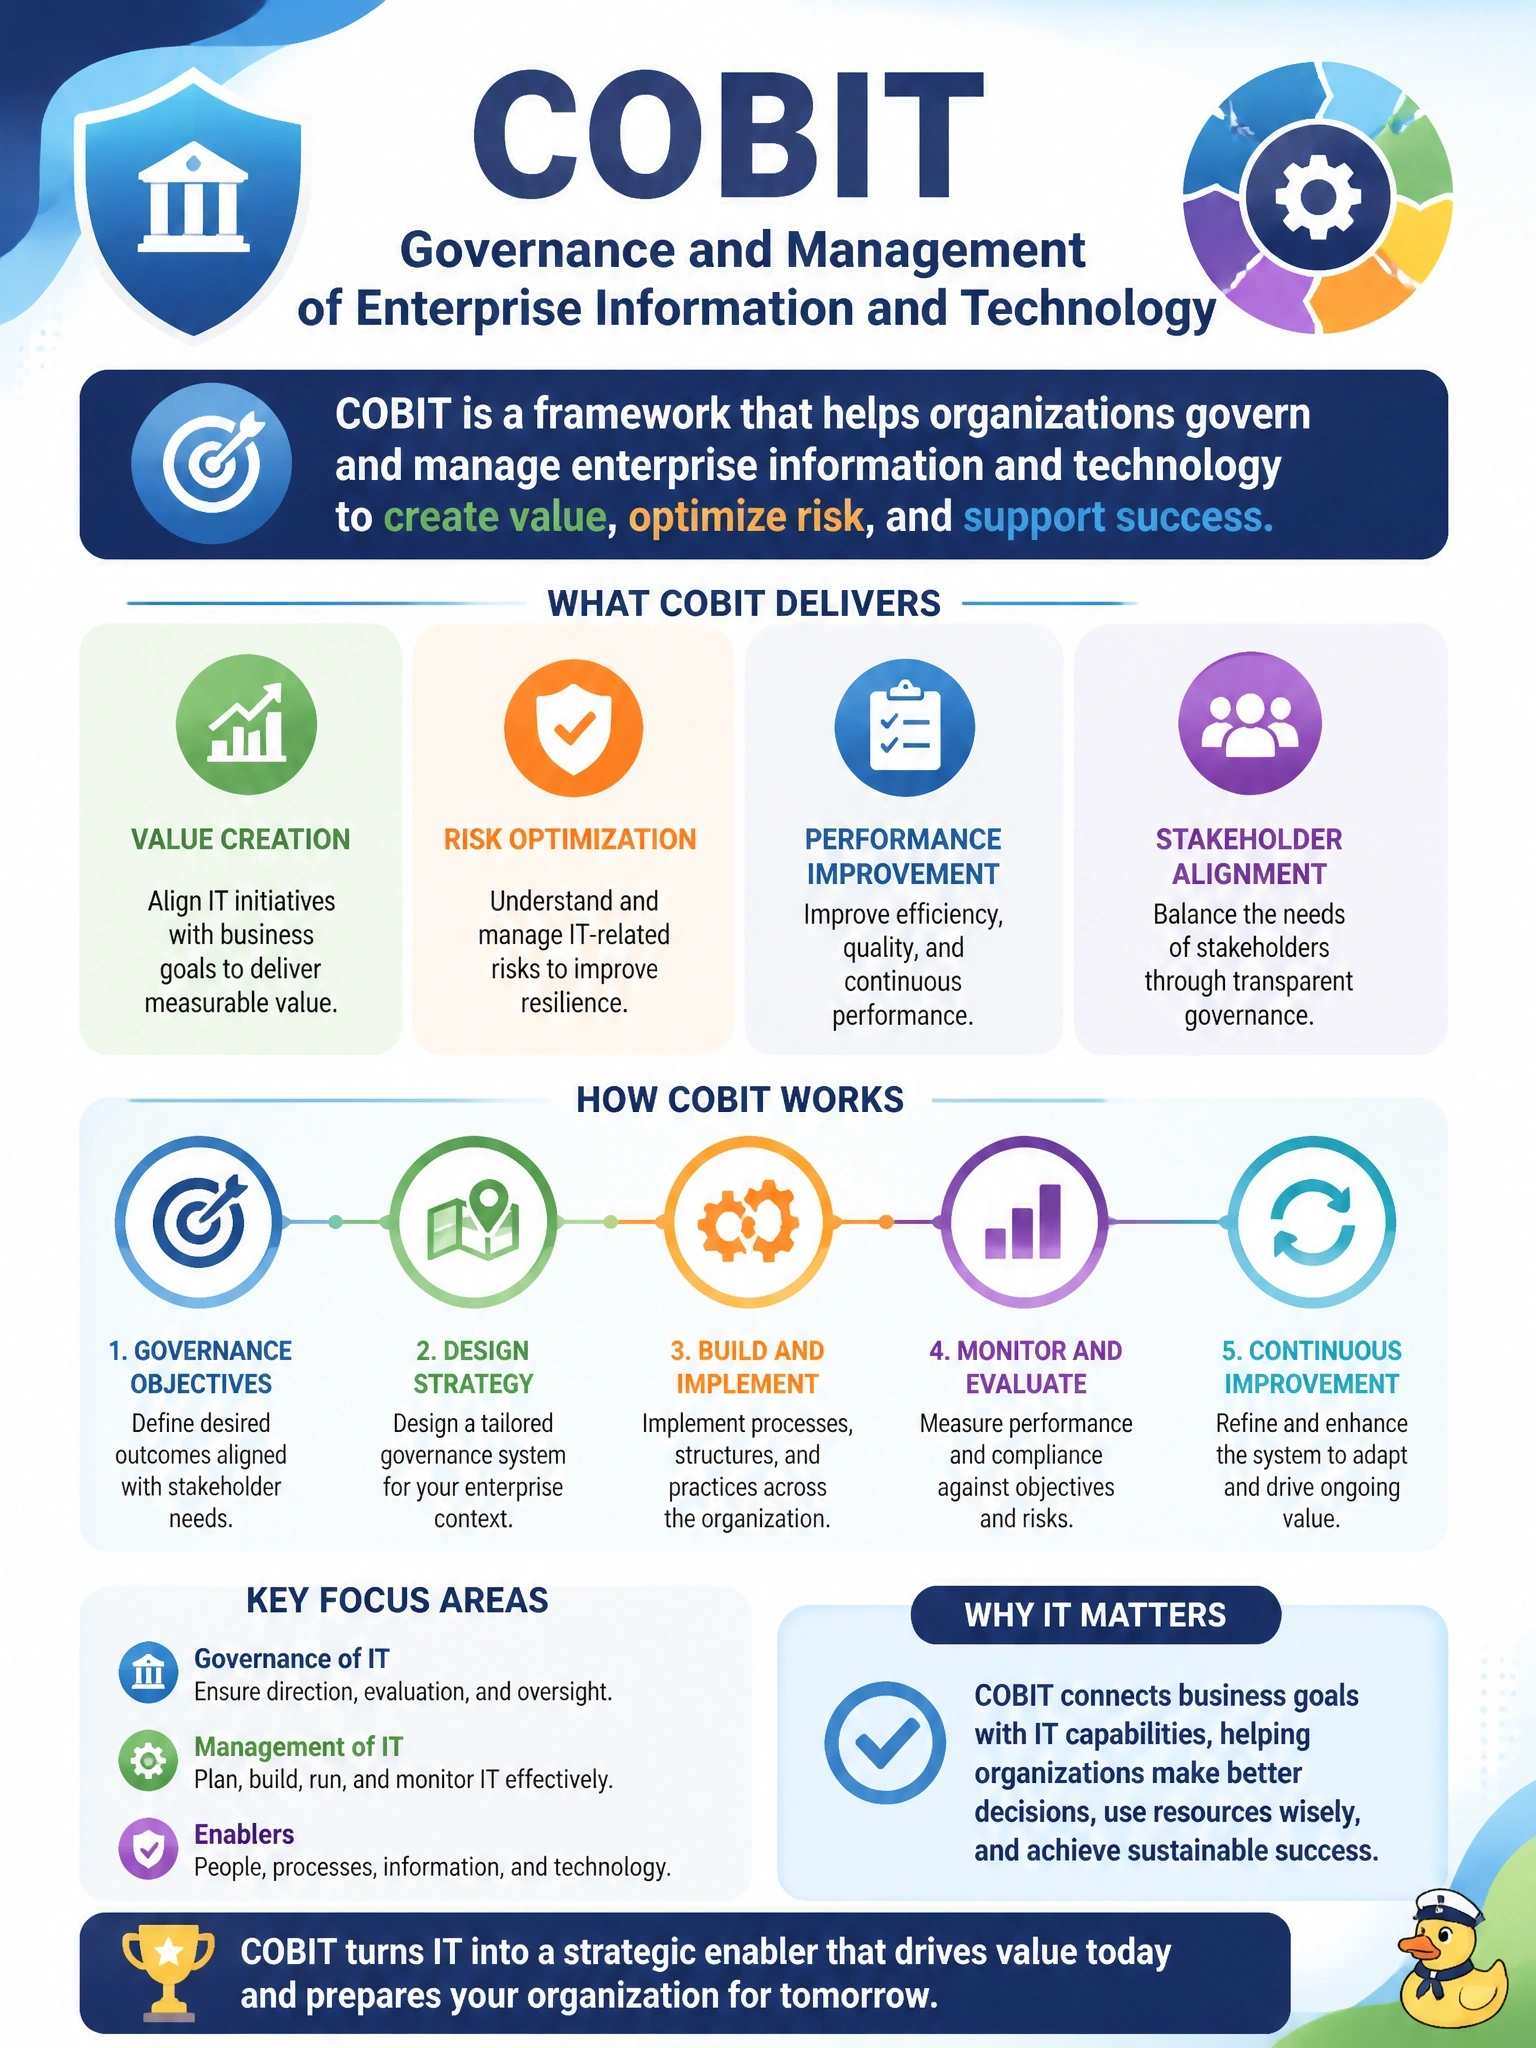
COBIT, published by ISACA, is a framework for the governance and management of enterprise information and technology. It helps organizations align IT with stakeholder needs and enterprise goals, distinguishes governance objectives from management objectives, and covers areas such as benefits delivery, risk optimization and resource optimization, making it a fit for executives who want a governance framework rather than a control list. NIST SP 800-53 is a comprehensive catalogue of security and privacy controls for information systems; it is valuable for selecting and specifying controls but does not provide an enterprise IT governance model. PCI DSS is an industry standard of security requirements for entities that store, process or transmit payment card data; its scope is the cardholder data environment, not enterprise governance. ISO/IEC 27002 offers guidance on information security controls and supports an information security management system, but it is a control reference rather than a framework for governing enterprise IT. Exam caveat: these frameworks are complementary; an organization might govern with COBIT while drawing controls from other standards. Operational check: map the executives' stated goals to the framework's governance objectives and confirm that roles for governance and management are defined before adopting it.