
A project team is preparing for ISO/IEC 27001 certification and keeps confusing it with ISO/IEC 27002. Which statement correctly describes the relationship between the two standards?
Select an answer to reveal the explanation.
Short Explanation
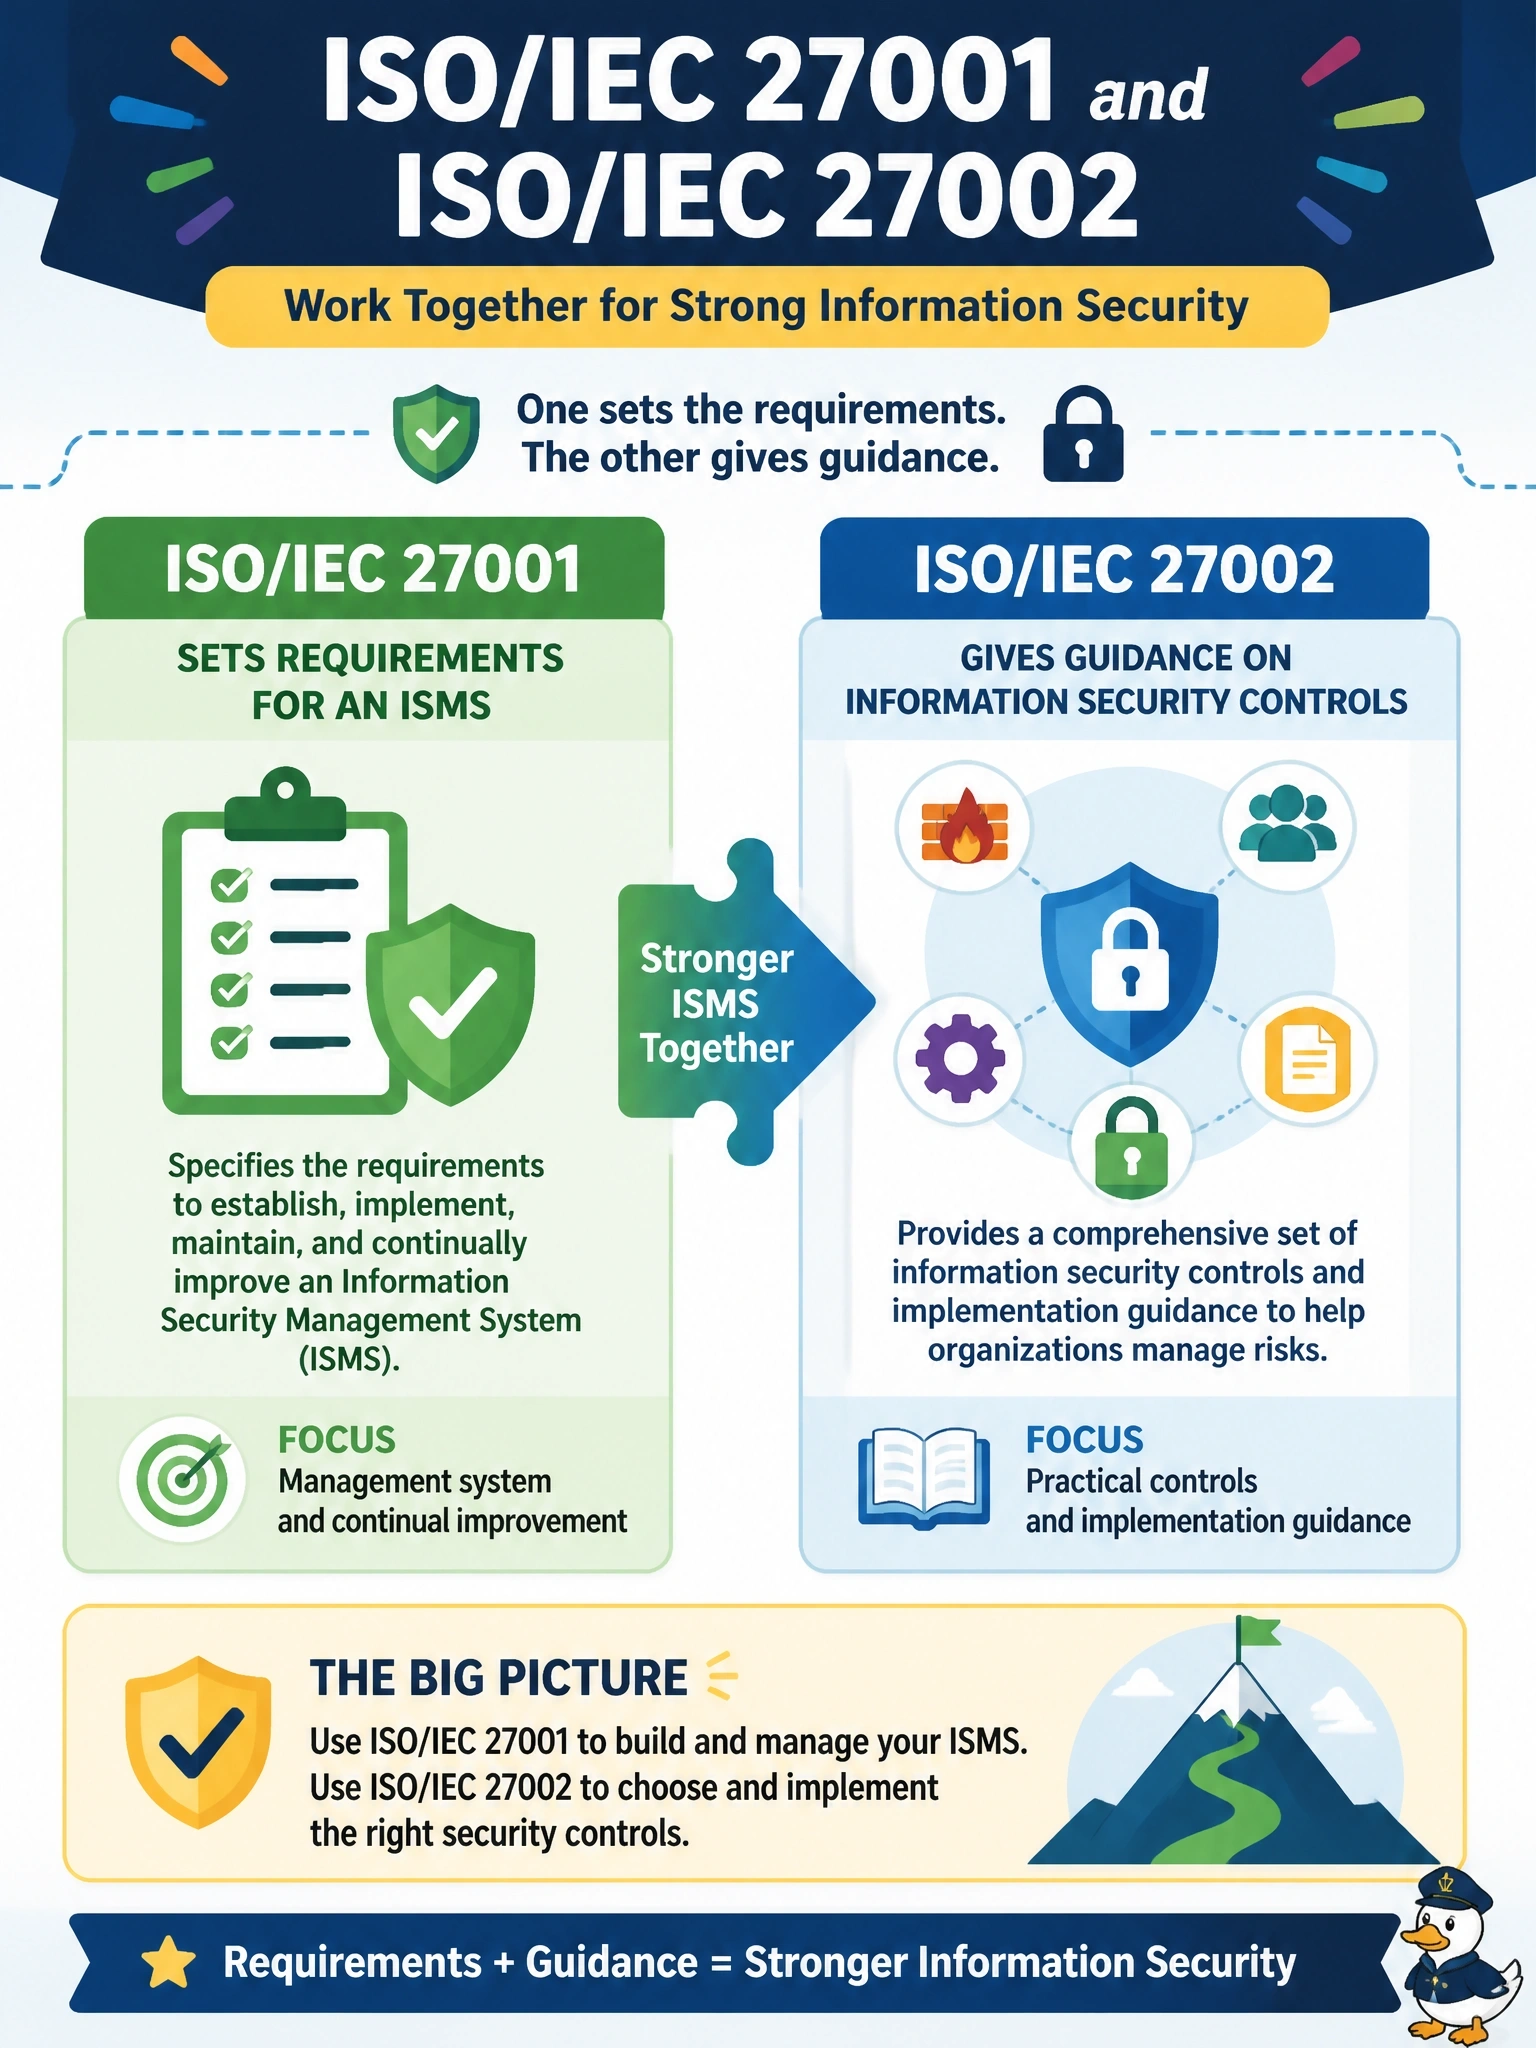
Think of 27001 as the rulebook you get certified against and 27002 as the coaching manual that helps you pick and run the plays. The management system requirements live in 27001; the detailed control guidance lives in 27002. The trap is flipping them around, or assuming both can be certified.
Full Explanation
ISO/IEC 27001 specifies the requirements for establishing, implementing, maintaining and continually improving an information security management system, and it is the standard against which organizations are certified. ISO/IEC 27002 is a code of practice that provides guidance on information security controls, helping organizations select and implement the controls their risk treatment identifies. The two are complementary: the management system determines which controls are needed, and the guidance helps implement them well. Describing 27002 as the certifiable requirements and 27001 as guidance reverses their roles. Claiming both are certifiable is incorrect; 27002 is guidance and is not used as a certification standard, and the split of technical controls versus policies misrepresents both documents. Describing 27001 as a technical control catalogue and 27002 as a risk assessment methodology also mixes up the family; information security risk management guidance is the subject of a separate standard in the 27000 series, and neither is a purely technical catalogue. Exam caveat: on CISM the purpose of each standard matters more than specific clause or control numbers. Operational check: confirm the certification scope statement references ISO/IEC 27001 and that the statement of applicability uses ISO/IEC 27002 as implementation guidance.