
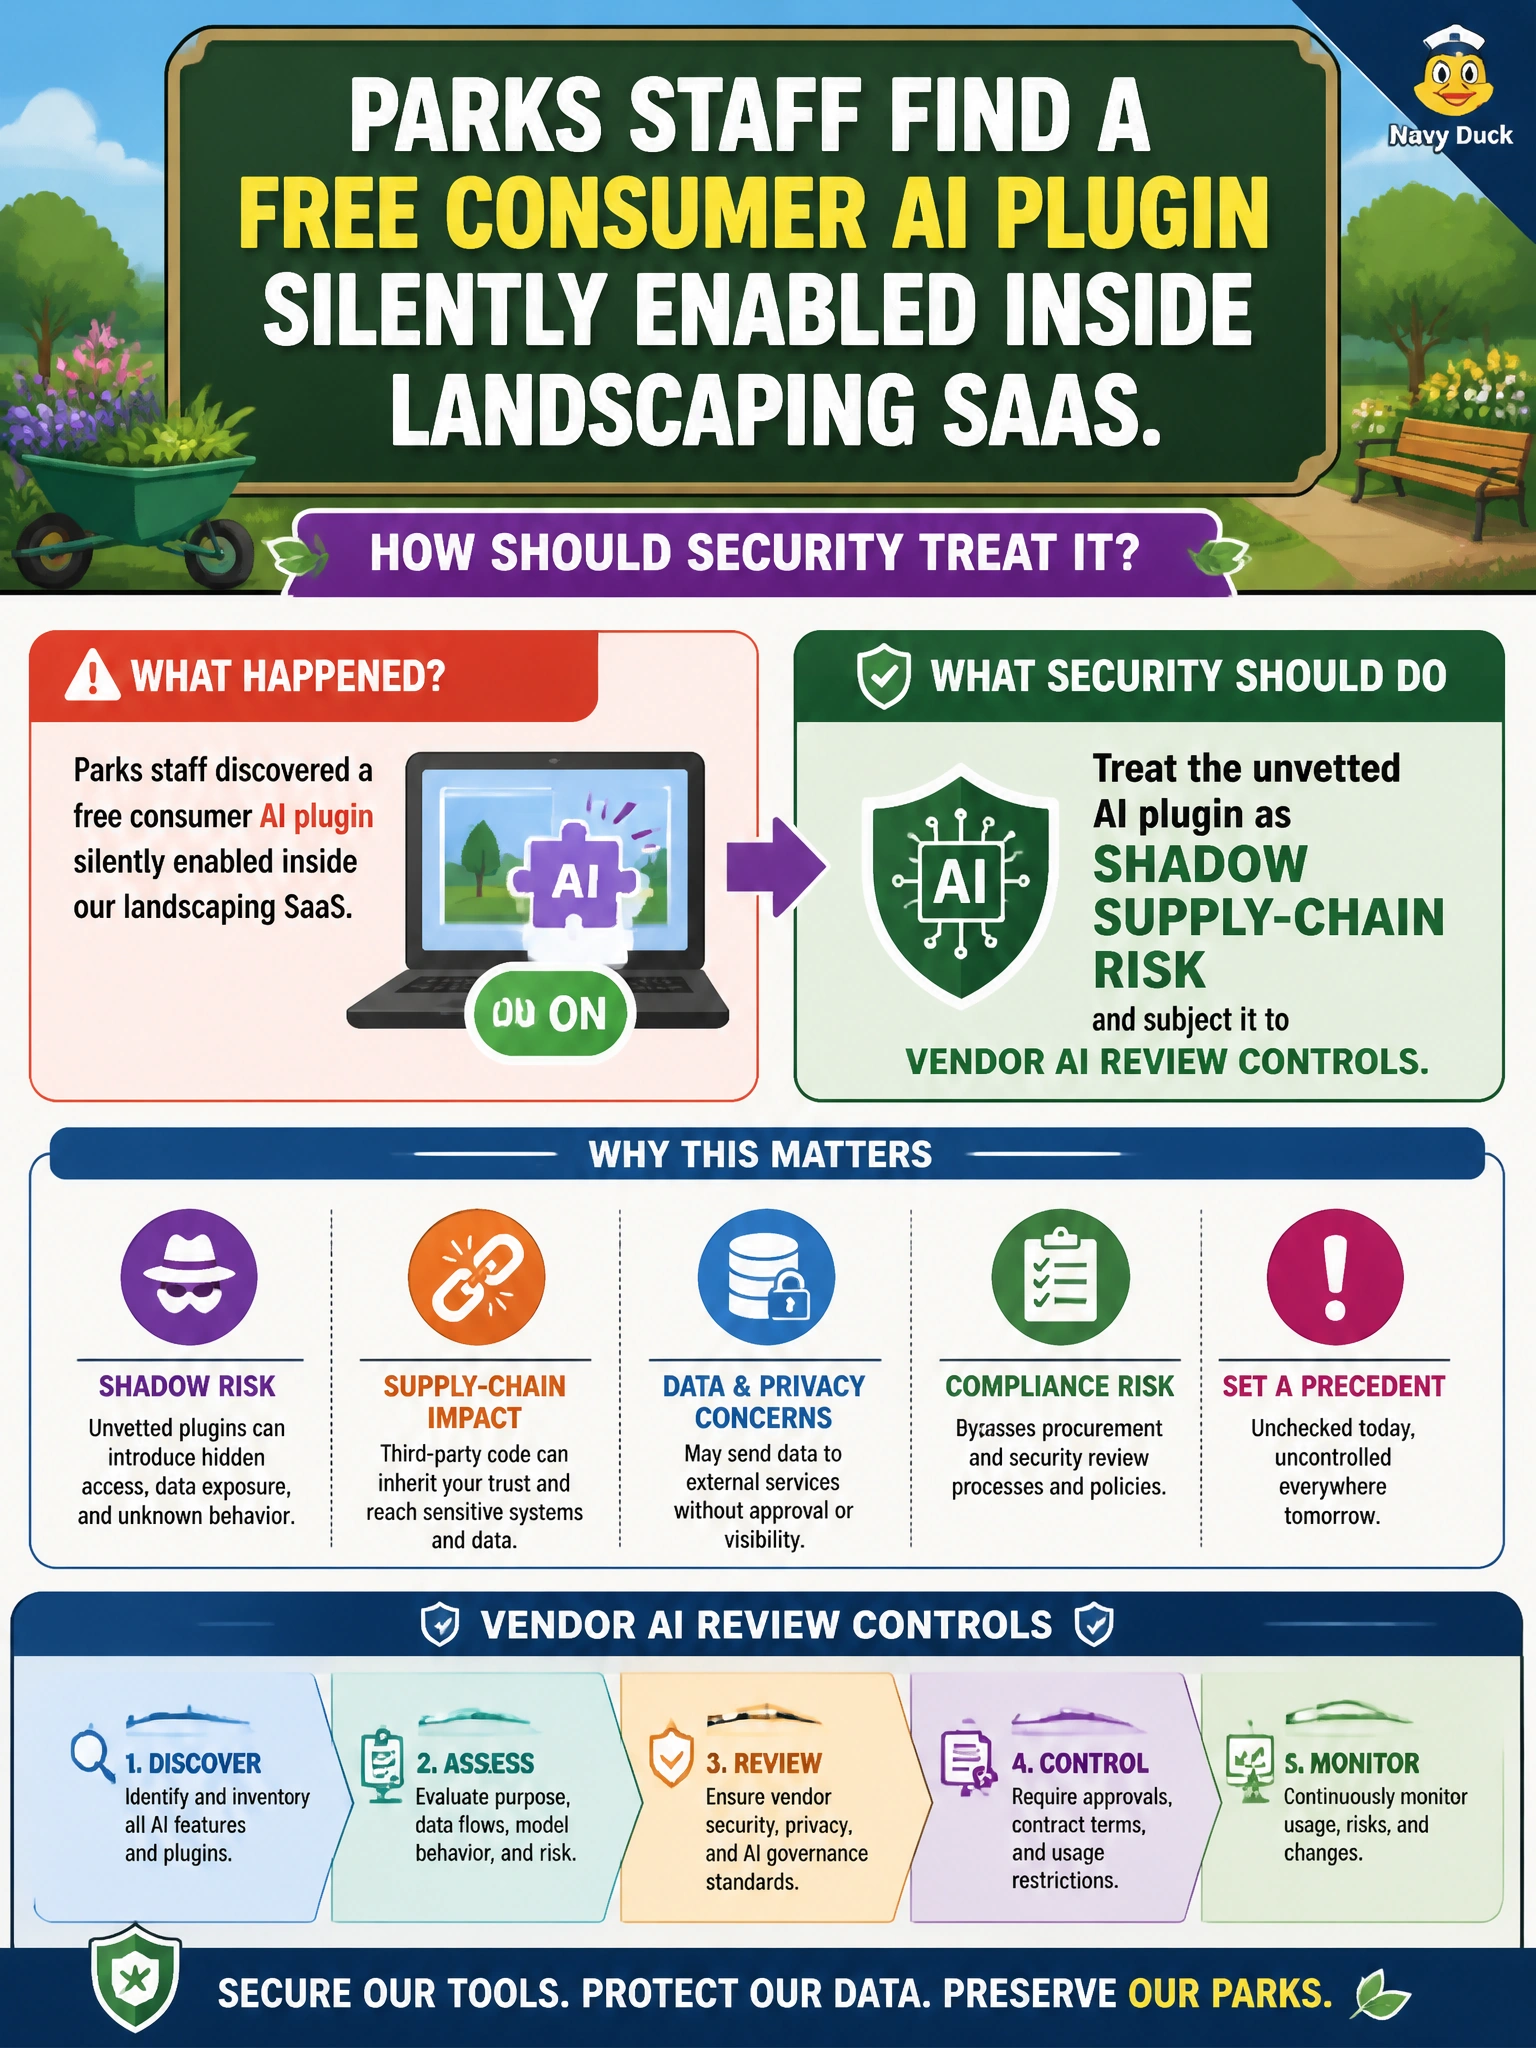
Parks staff find a free consumer AI plugin silently enabled inside landscaping SaaS. How should security treat it?
Select an answer to reveal the explanation.
Short Explanation
A free AI switch flipping on inside approved SaaS is still a new vendor brain you didn’t buy on purpose. Treat it as shadow supply-chain risk and review it. The icon color won’t tell you where the data goes.
Full Explanation
When parks staff find a free consumer AI plugin silently enabled inside landscaping SaaS, security should treat the unvetted AI plugin as shadow supply-chain risk and subject it to vendor AI review controls. That treatment works because features appearing inside an approved product can still introduce new model providers, data exfiltration paths, and training-use terms that were never evaluated. Shadow AI plugins expand the municipal attack and privacy surface without procurement visibility.
Ignoring it because it appeared inside an already-approved SaaS product fails conceptually because prior approval of the parent product does not automatically cover newly enabled AI components or their subprocessors. Celebrating free AI features without security assessment fails because zero license cost does not imply acceptable risk for parks operational data. Only reviewing the plugin’s icon color for brand alignment fails because visual branding is unrelated to data handling, authentication, or model-provider risk.
Exam caveat: some plugins may be toggled by vendor default after an update; monitoring for silent enablement is part of continuous supply-chain hygiene. Operational check: disable the unvetted plugin pending review, inventory data categories it can access, run the standard vendor AI questionnaire, and approve or permanently block before parks workflows resume using it.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.