
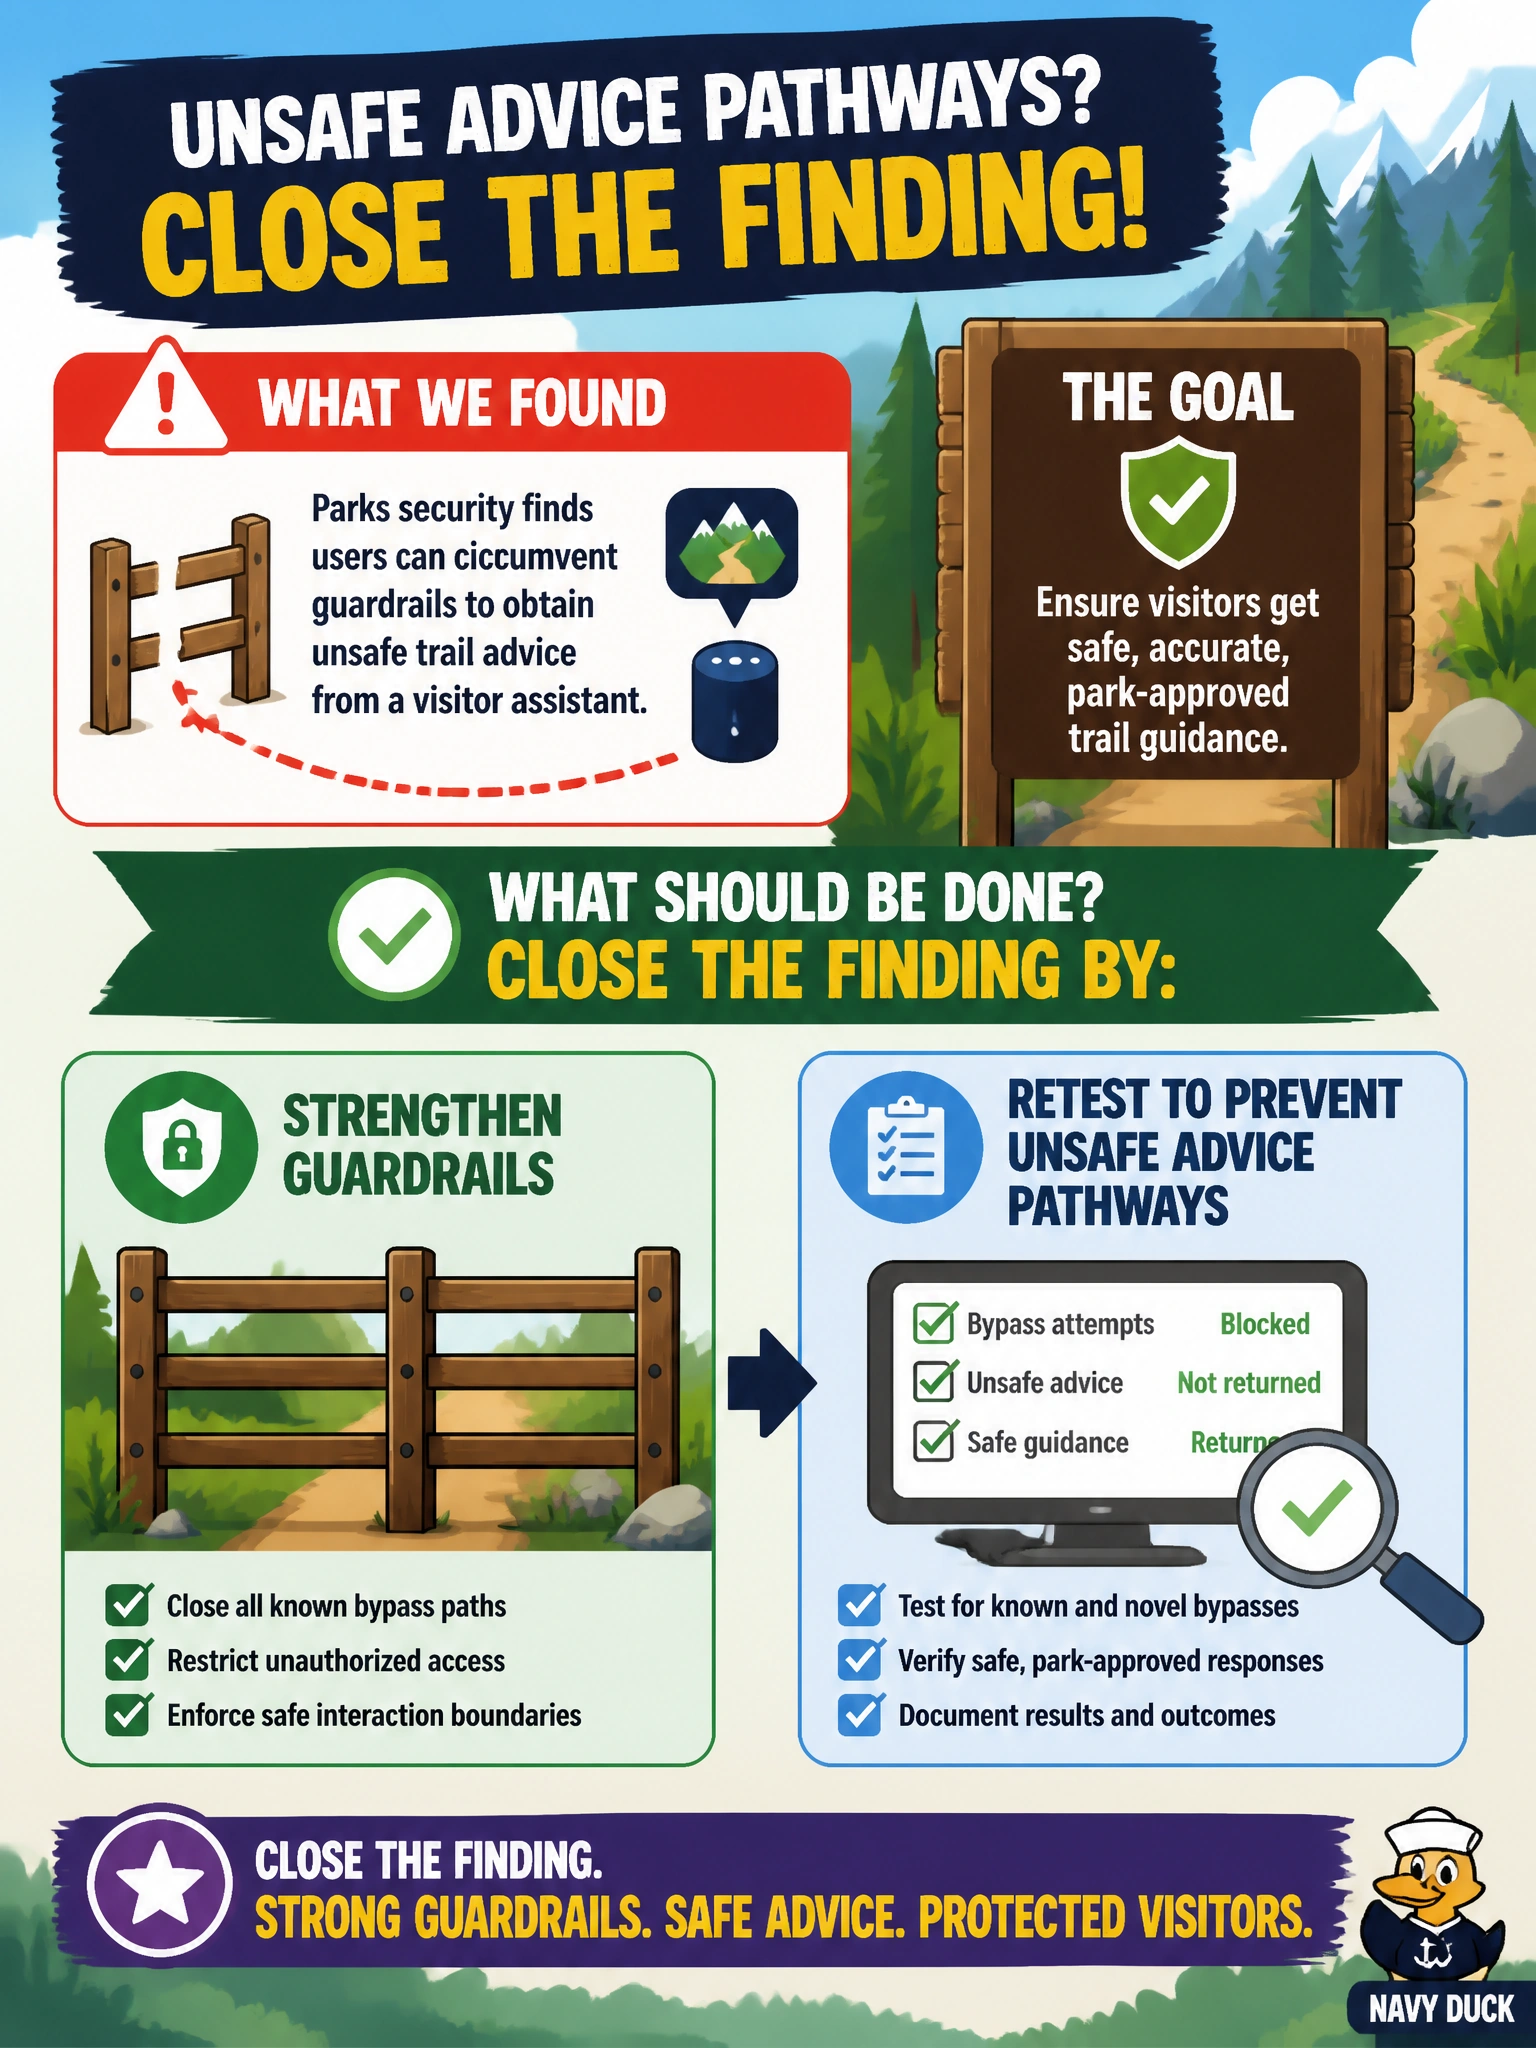
Parks security finds users can circumvent guardrails to obtain unsafe trail advice from a visitor assistant. What should be done?
Select an answer to reveal the explanation.
Short Explanation
If you can wriggle past the safety rails for bad trail advice, you'll need more than tightened input filters and passing routine trail guidance flows to close it. Retest until unsafe paths stay blocked. If you just rotate keys or fine-tune on guides, you'll still leave the bypass open since neither restores the guardrails.
Full Explanation
When parks users can circumvent guardrails to obtain unsafe trail advice, vulnerability management should close the finding by strengthening guardrails and retesting until unsafe advice pathways remain blocked. Guardrail bypass is an AI vulnerability because it defeats intended safety constraints on a civic visitor assistant; remediation must restore the safety property under realistic evasion attempts, not merely document the cleverness of the bypass.
Closing the finding by tightening input filters and retesting routine trail guidance flows fails because routine flows do not exercise bypass paths, so passing them provides no evidence that unsafe advice pathways are blocked under realistic evasion attempts. Closing the finding by enabling access controls and rotating API keys for trail services fails because it addresses authentication and key hygiene, not prompt-level guardrail bypass by authorized users, so unsafe advice pathways remain open. Closing the finding by fine-tuning the model on approved trail guides and redeploying promptly fails because improved trail knowledge does not restore refusal behavior, leaving guardrail bypasses exploitable without layered mitigations and adversarial retesting.
Exam caveat: hardening should include both model-side refusals and application-side filters; single-layer guardrails are routinely bypassed. Operational check: reproduce the bypass in a test harness, deploy layered mitigations (policy model, output filters, topic blocks for hazardous guidance), retest known and variant jailbreaks, and only then close the finding with evidence attached to the parks AI vulnerability record.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.