
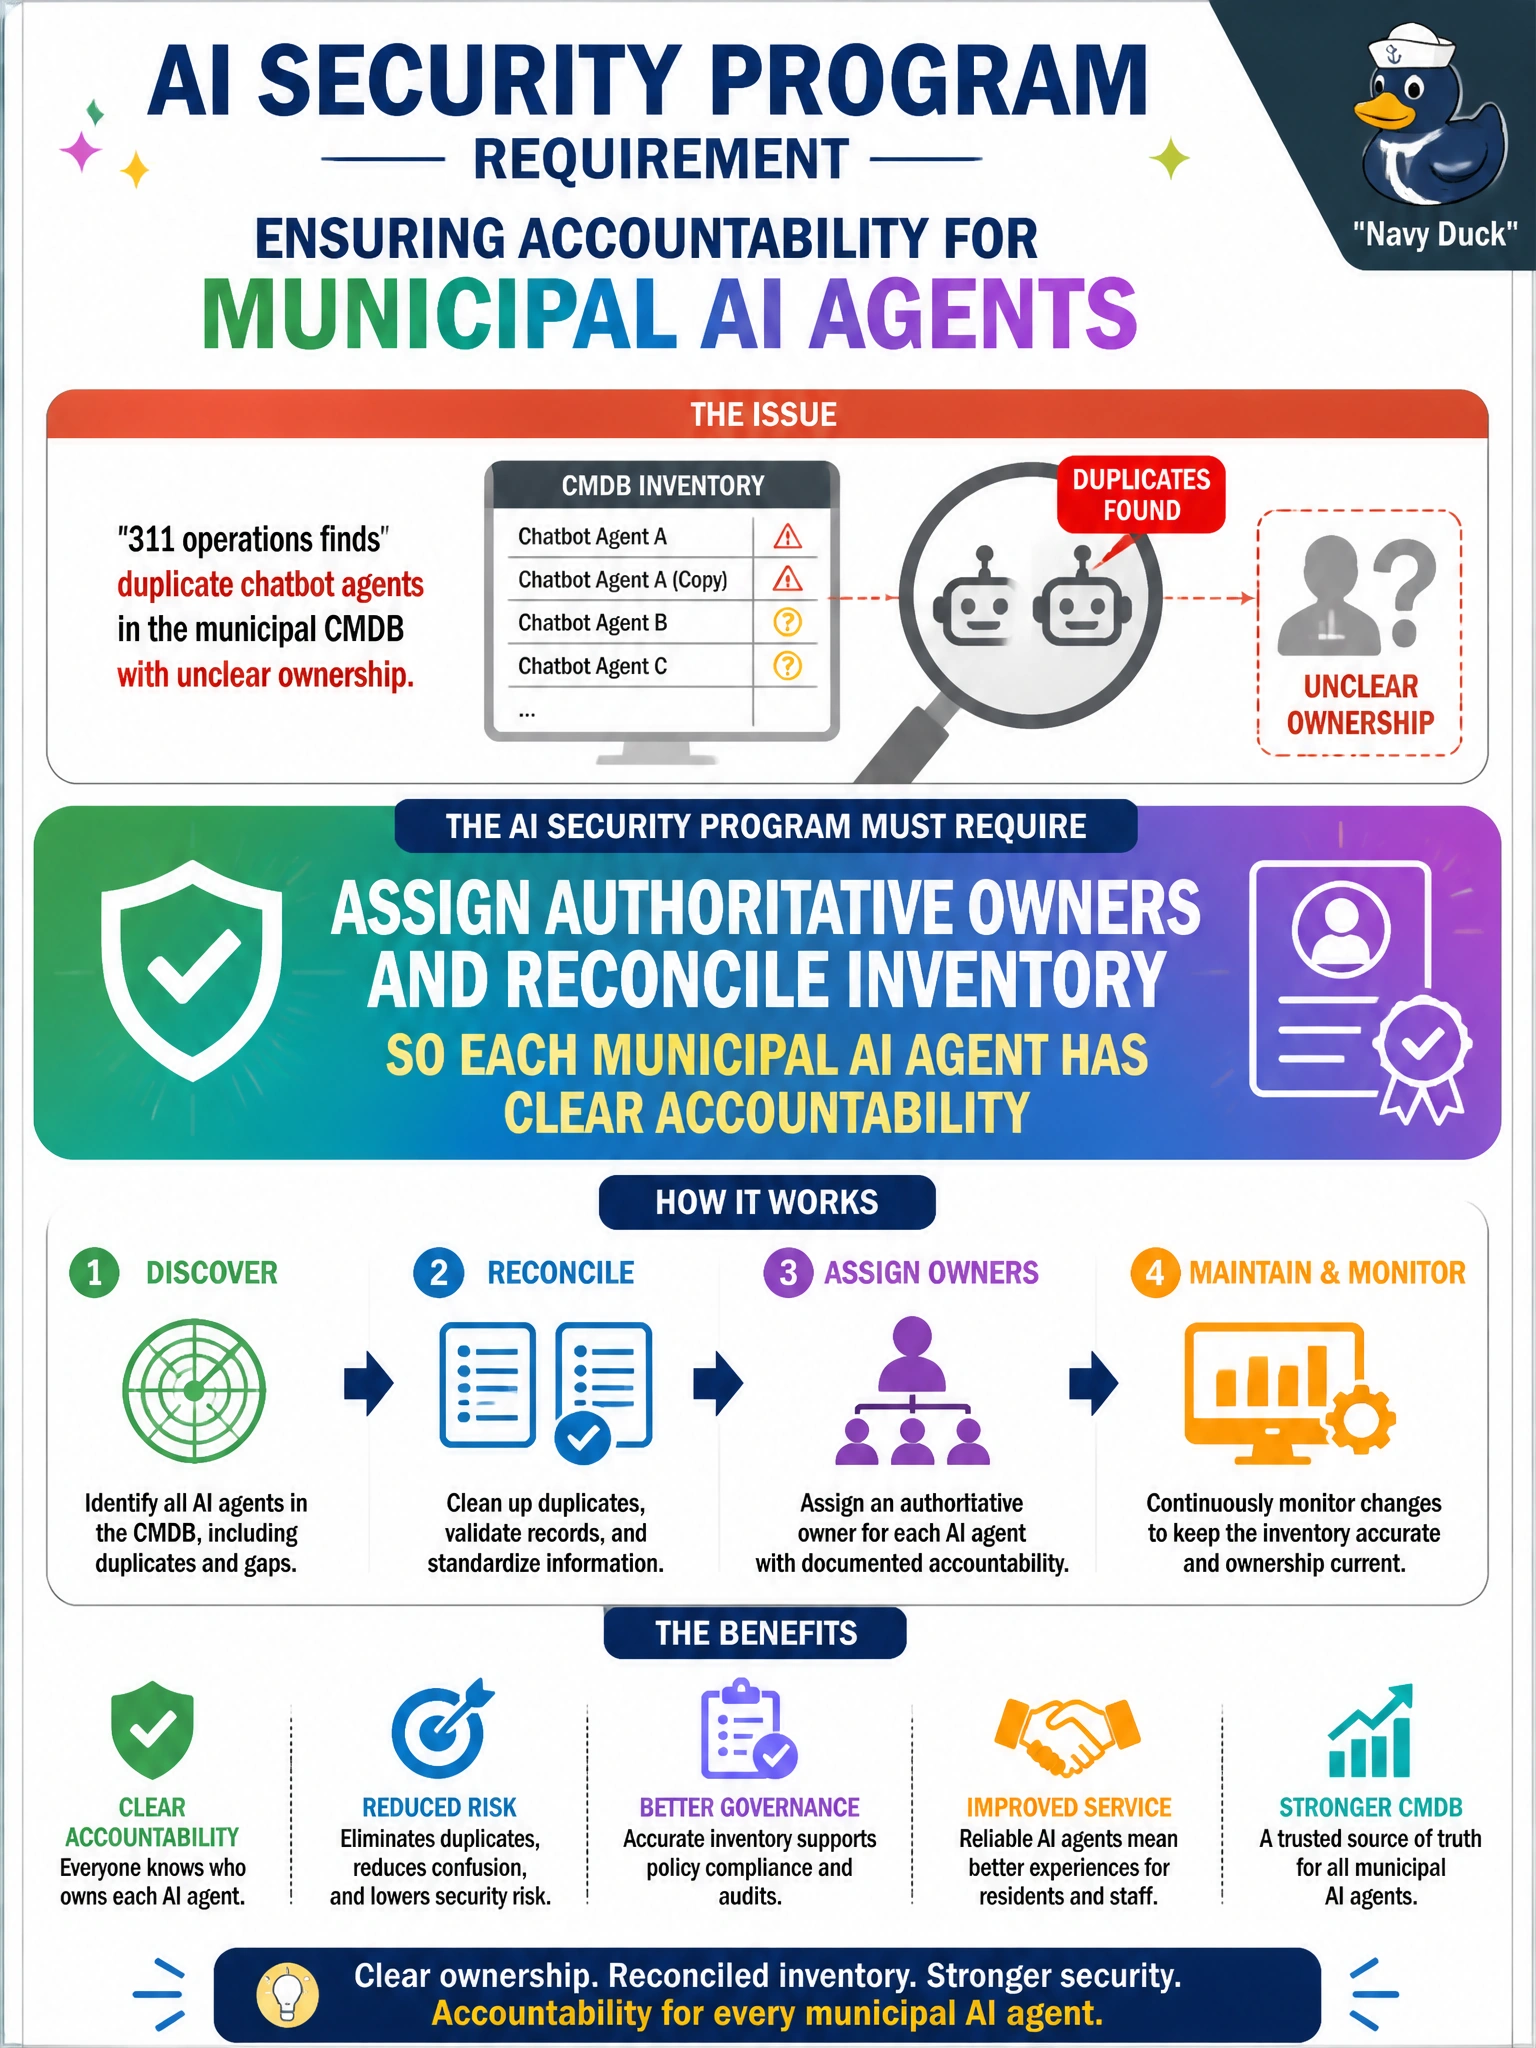
311 operations finds duplicate chatbot agents in the municipal CMDB with unclear ownership. What should the AI security program require?
Select an answer to reveal the explanation.
Short Explanation
Two unlabeled bots are like two sets of city keys with nobody’s name on the ring. Pick owners, clean the inventory, and make accountability obvious. Asset hygiene is how you stop orphaned agents from drifting forever.
Full Explanation
When 311 operations finds duplicate chatbot agents in the municipal CMDB with unclear ownership, the AI security program must assign authoritative owners and reconcile inventory so each municipal AI agent has clear accountability. Ownership is the prerequisite for access reviews, change approval, incident response, and retirement; duplicates without owners become orphaned risk. Reconciling the CMDB removes shadow instances and ensures monitoring and policy attach to real agents. Leaving duplicate agents running as backup personalities increases attack surface, confuses residents with inconsistent answers, and preserves unmanaged credentials. Deleting the CMDB and relying on verbal knowledge among supervisors destroys the authoritative register and guarantees ownership will stay tribal. Assigning ownership only after a resident complaint makes accountability reactive and allows unmanaged agents to operate until harm is visible. Exam caveat: ownership should be a named role with a backup, not a shared mailbox that no one monitors. Operational check: reconcile CMDB AI entries against production endpoints and API gateways, assign a primary and alternate owner per agent, retire or merge duplicates, and schedule periodic ownership attestation.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.