
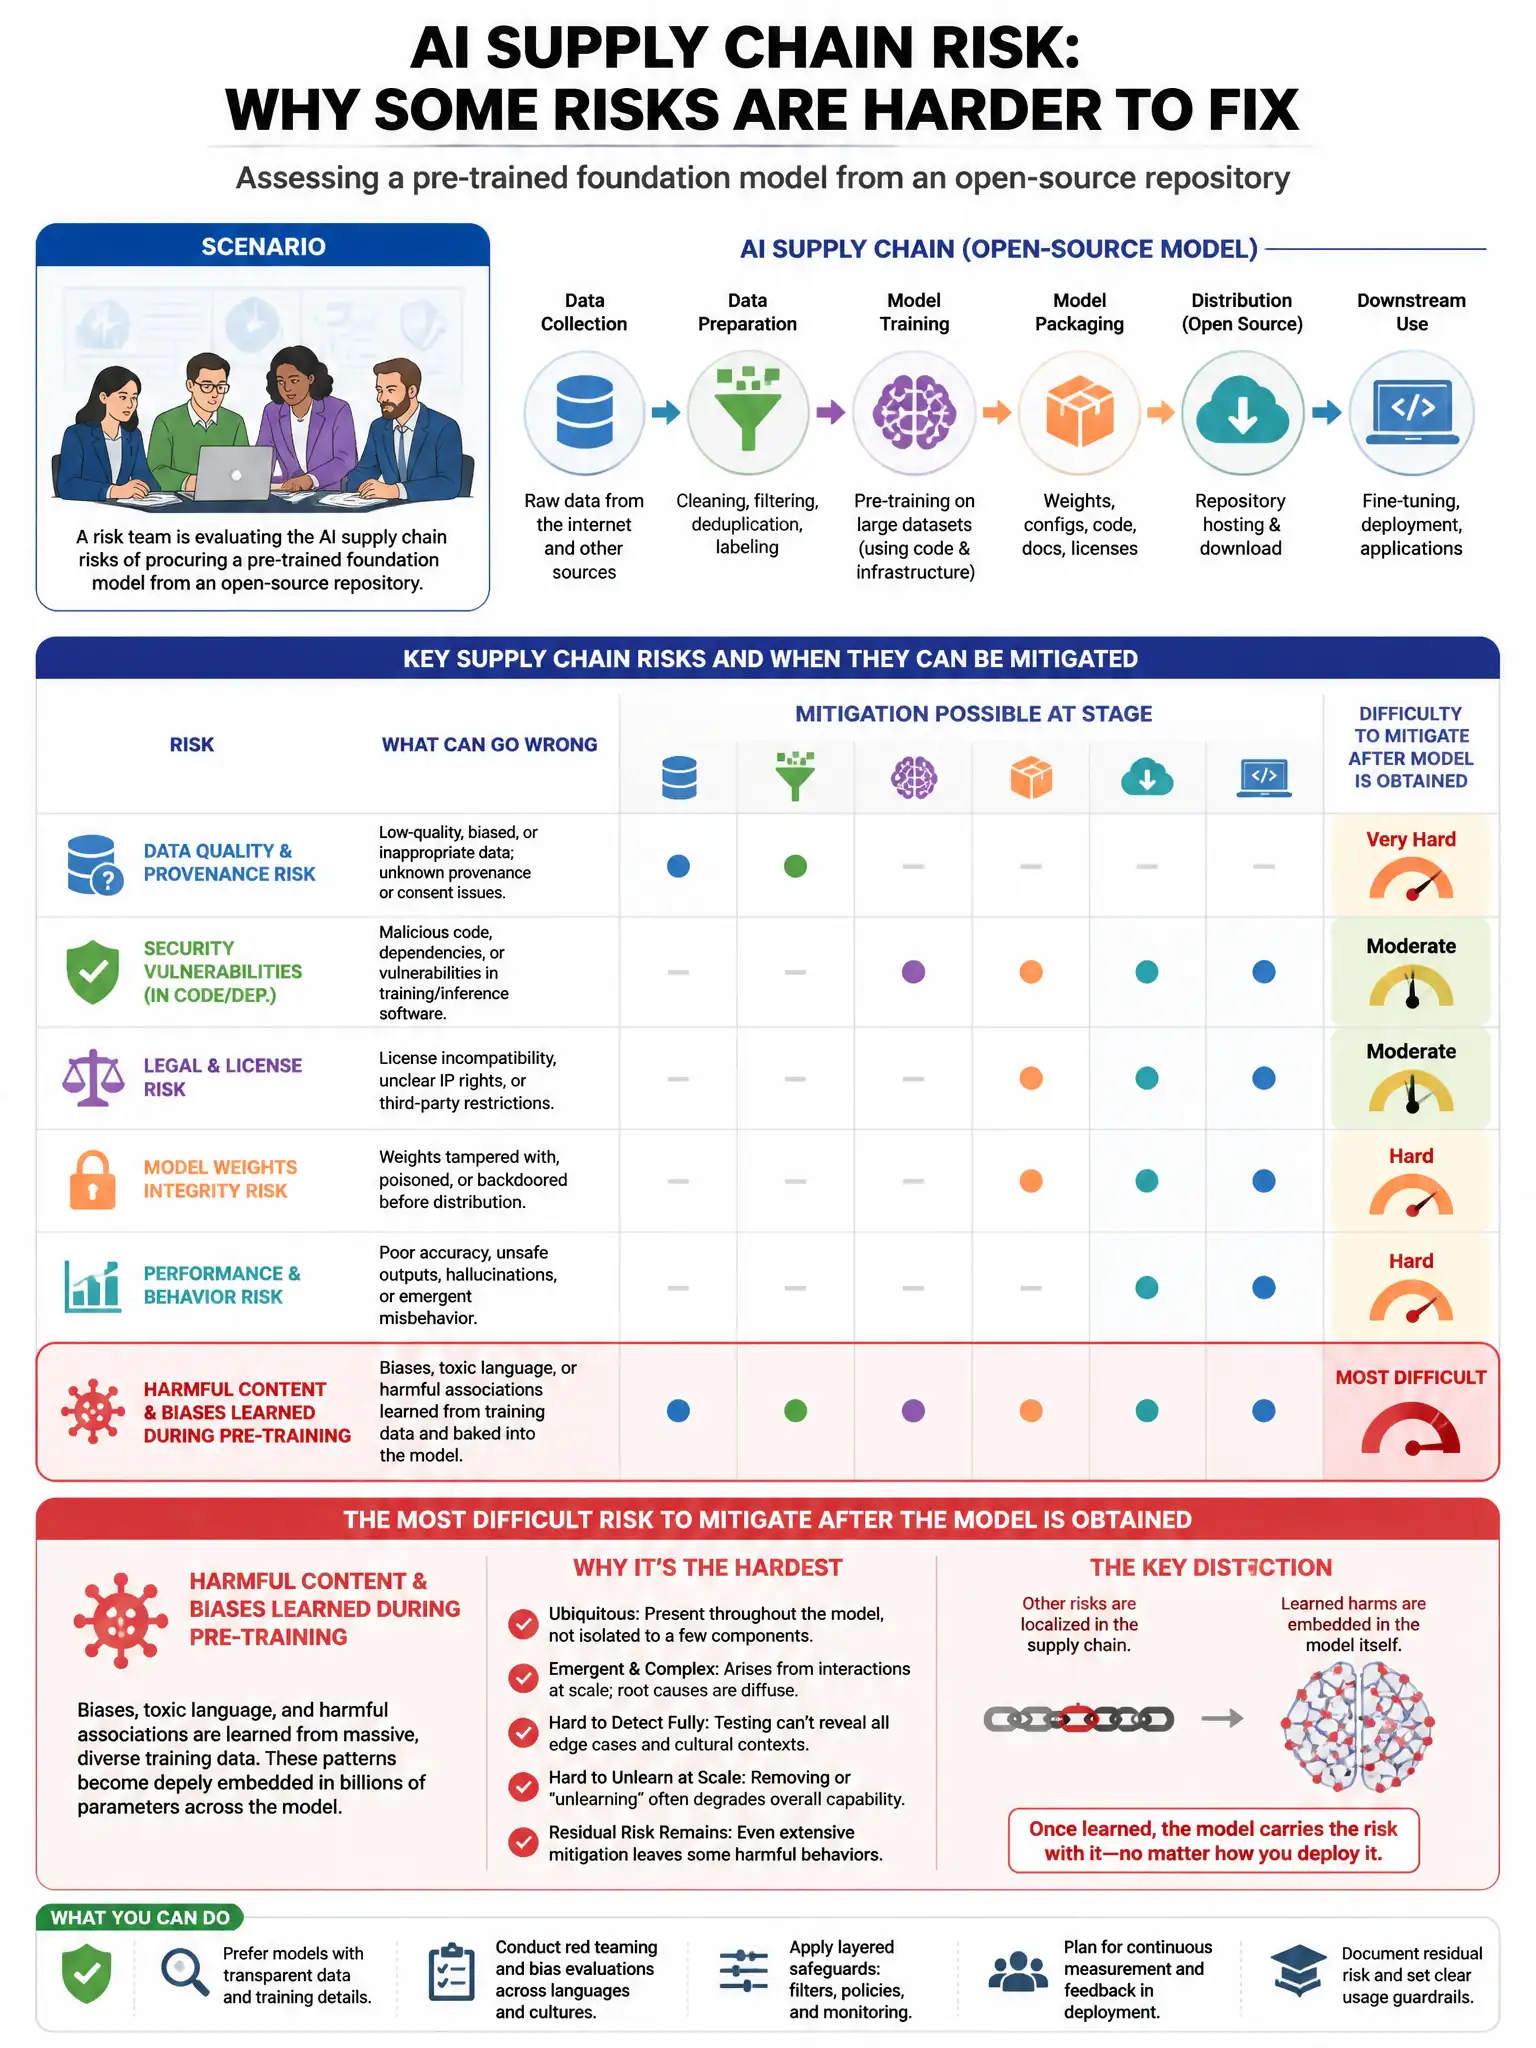
A risk team is assessing the AI supply chain risks of procuring a pre-trained foundation model from an open-source repository. Which risk is MOST difficult to mitigate after the model has been integrated into a production system?
Select an answer to reveal the explanation.
Short Explanation
You should pick the backdoor or Trojan implanted during pre-training because it can stay hidden until a specific trigger input activates it, and after integration you often need full retraining or specialized weight-level detection. The other risks are easier to handle through legal review, documentation fixes, or integration testing.
Full Explanation
The backdoor or Trojan implanted during pre-training is the most difficult risk to mitigate after production integration because it can behave normally until a specific trigger activates malicious behavior. Detecting it may require full retraining or specialized weight-level detection. License compliance obligations can be addressed through legal review. Insufficient hyperparameter and architecture documentation is a documentation gap. Tokenizer incompatibility with the organization's text preprocessing pipeline is a technical integration issue resolved during testing.