
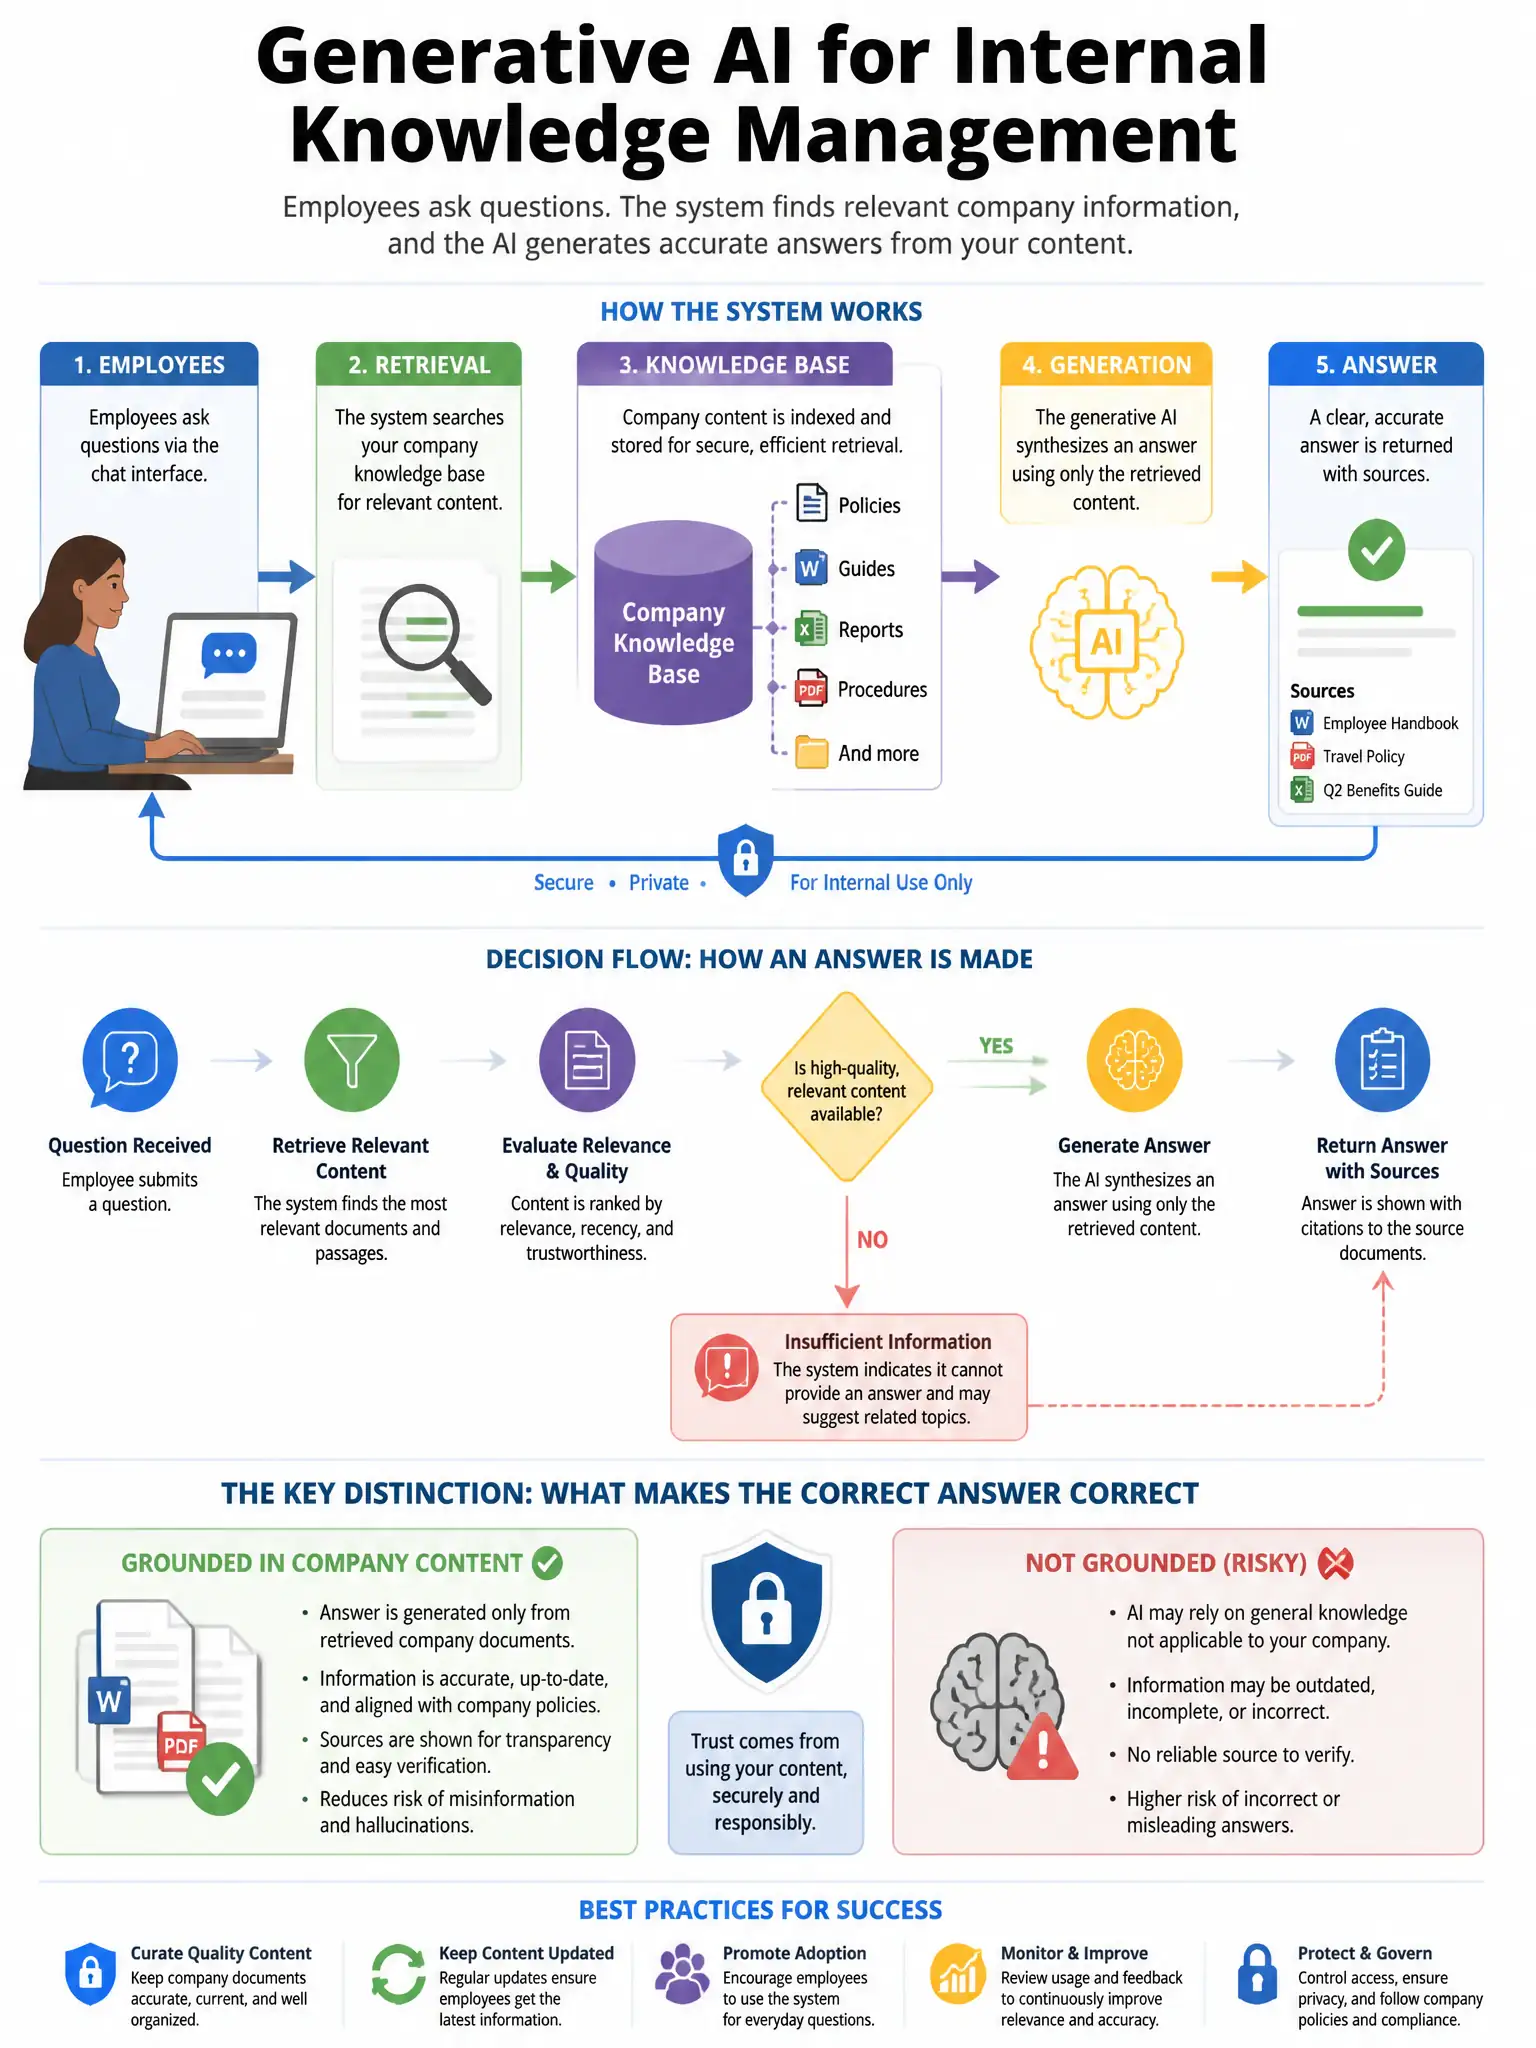
An organization is implementing a generative AI system for internal knowledge management. Employees can ask the system questions and receive answers synthesized from company documents. Which security control is MOST critical to prevent data classification boundary violations?
Select an answer to reveal the explanation.
Short Explanation
You need retrieval access controls that enforce document-level permissions, or the system can pull from documents you're not authorized to see. Training helps, but it won't stop the system from crossing data boundaries.
Full Explanation
The correct control is implementing retrieval access controls that enforce document-level permissions, ensuring the system only retrieves documents the querying user is authorized to access. Without those controls, a RAG-based knowledge system can synthesize answers from unauthorized documents, creating data classification boundary violations at scale. AI awareness training is baseline hygiene but insufficient alone. Logging queries detects violations after the fact. The 500-word response limit is arbitrary and does not address access control.