
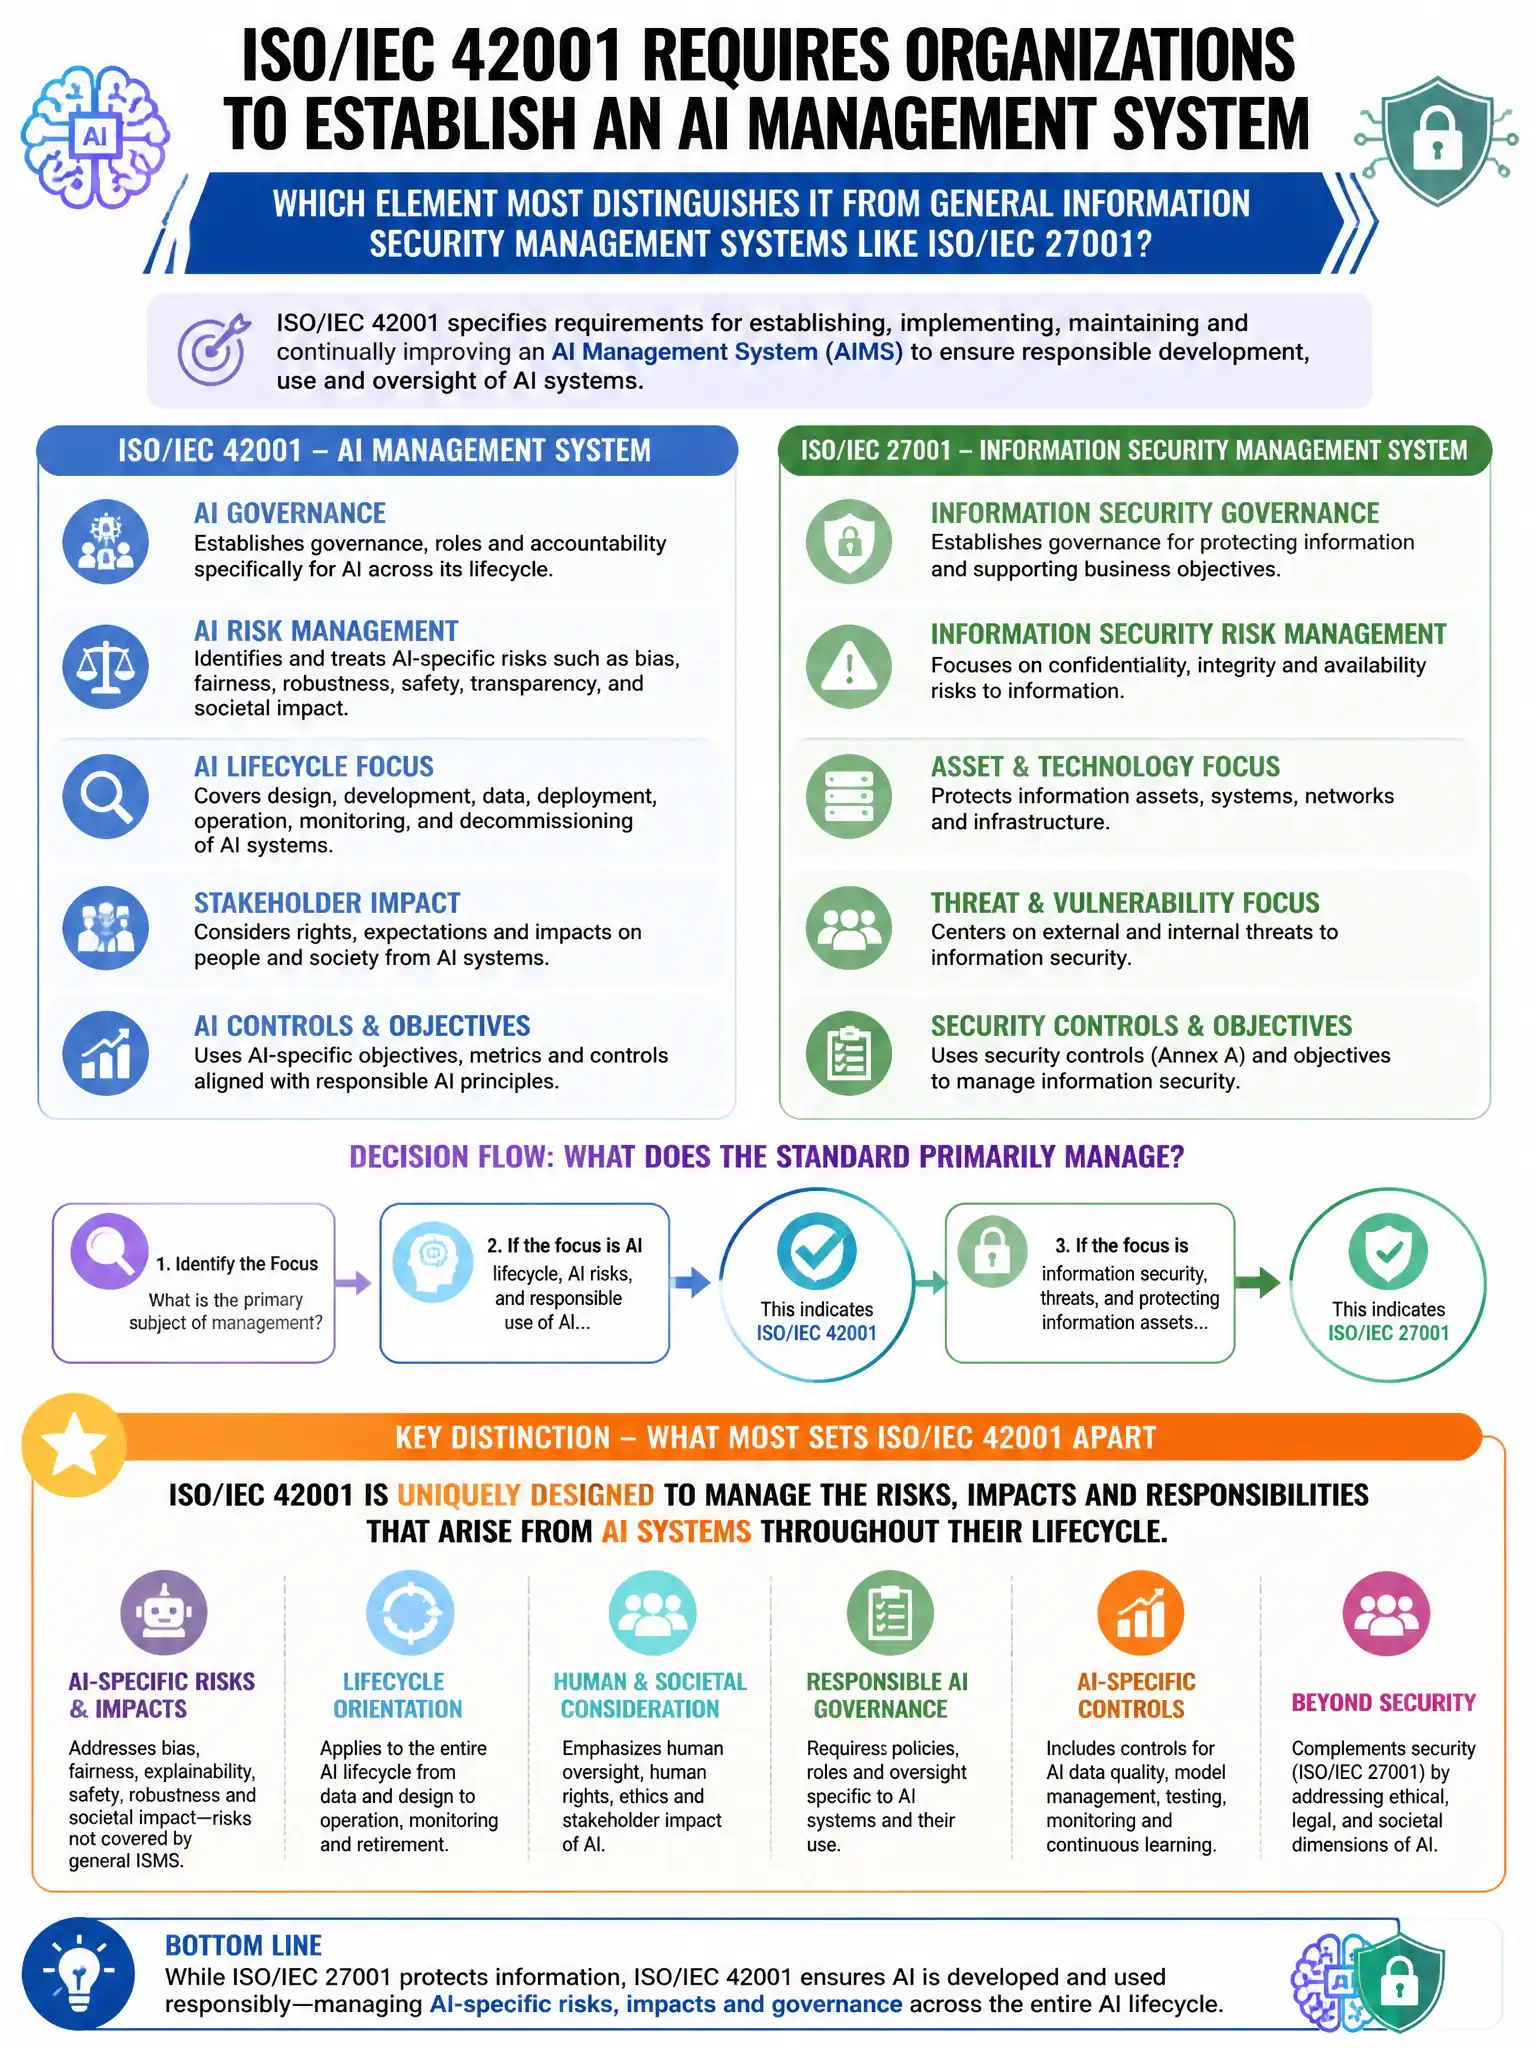
ISO/IEC 42001 requires organizations to establish an AI management system. Which element MOST distinguishes it from general information security management systems like ISO/IEC 27001?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you're right to pick the answer that calls out AI impact assessments and responsible AI objectives. ISO/IEC 42001 is built around AI-specific governance, like fairness, transparency, and accountability, not just general security controls.
Full Explanation
The correct element is the one requiring AI impact assessments and responsible AI objectives, because ISO/IEC 42001 is tailored to AI-specific concerns. It integrates fairness, transparency, and accountability into management system requirements, unlike ISO/IEC 27001. Annual third-party penetration testing of AI models is not required. Blockchain-based audit trails for all AI decisions have no basis in the standard. Publishing all AI training datasets publicly contradicts typical data protection obligations.