
An AI governance audit finds that an organization's AI risk assessments are performed once at model inception and never updated. What is the MOST significant risk this practice creates?
Select an answer to reveal the explanation.
Short Explanation
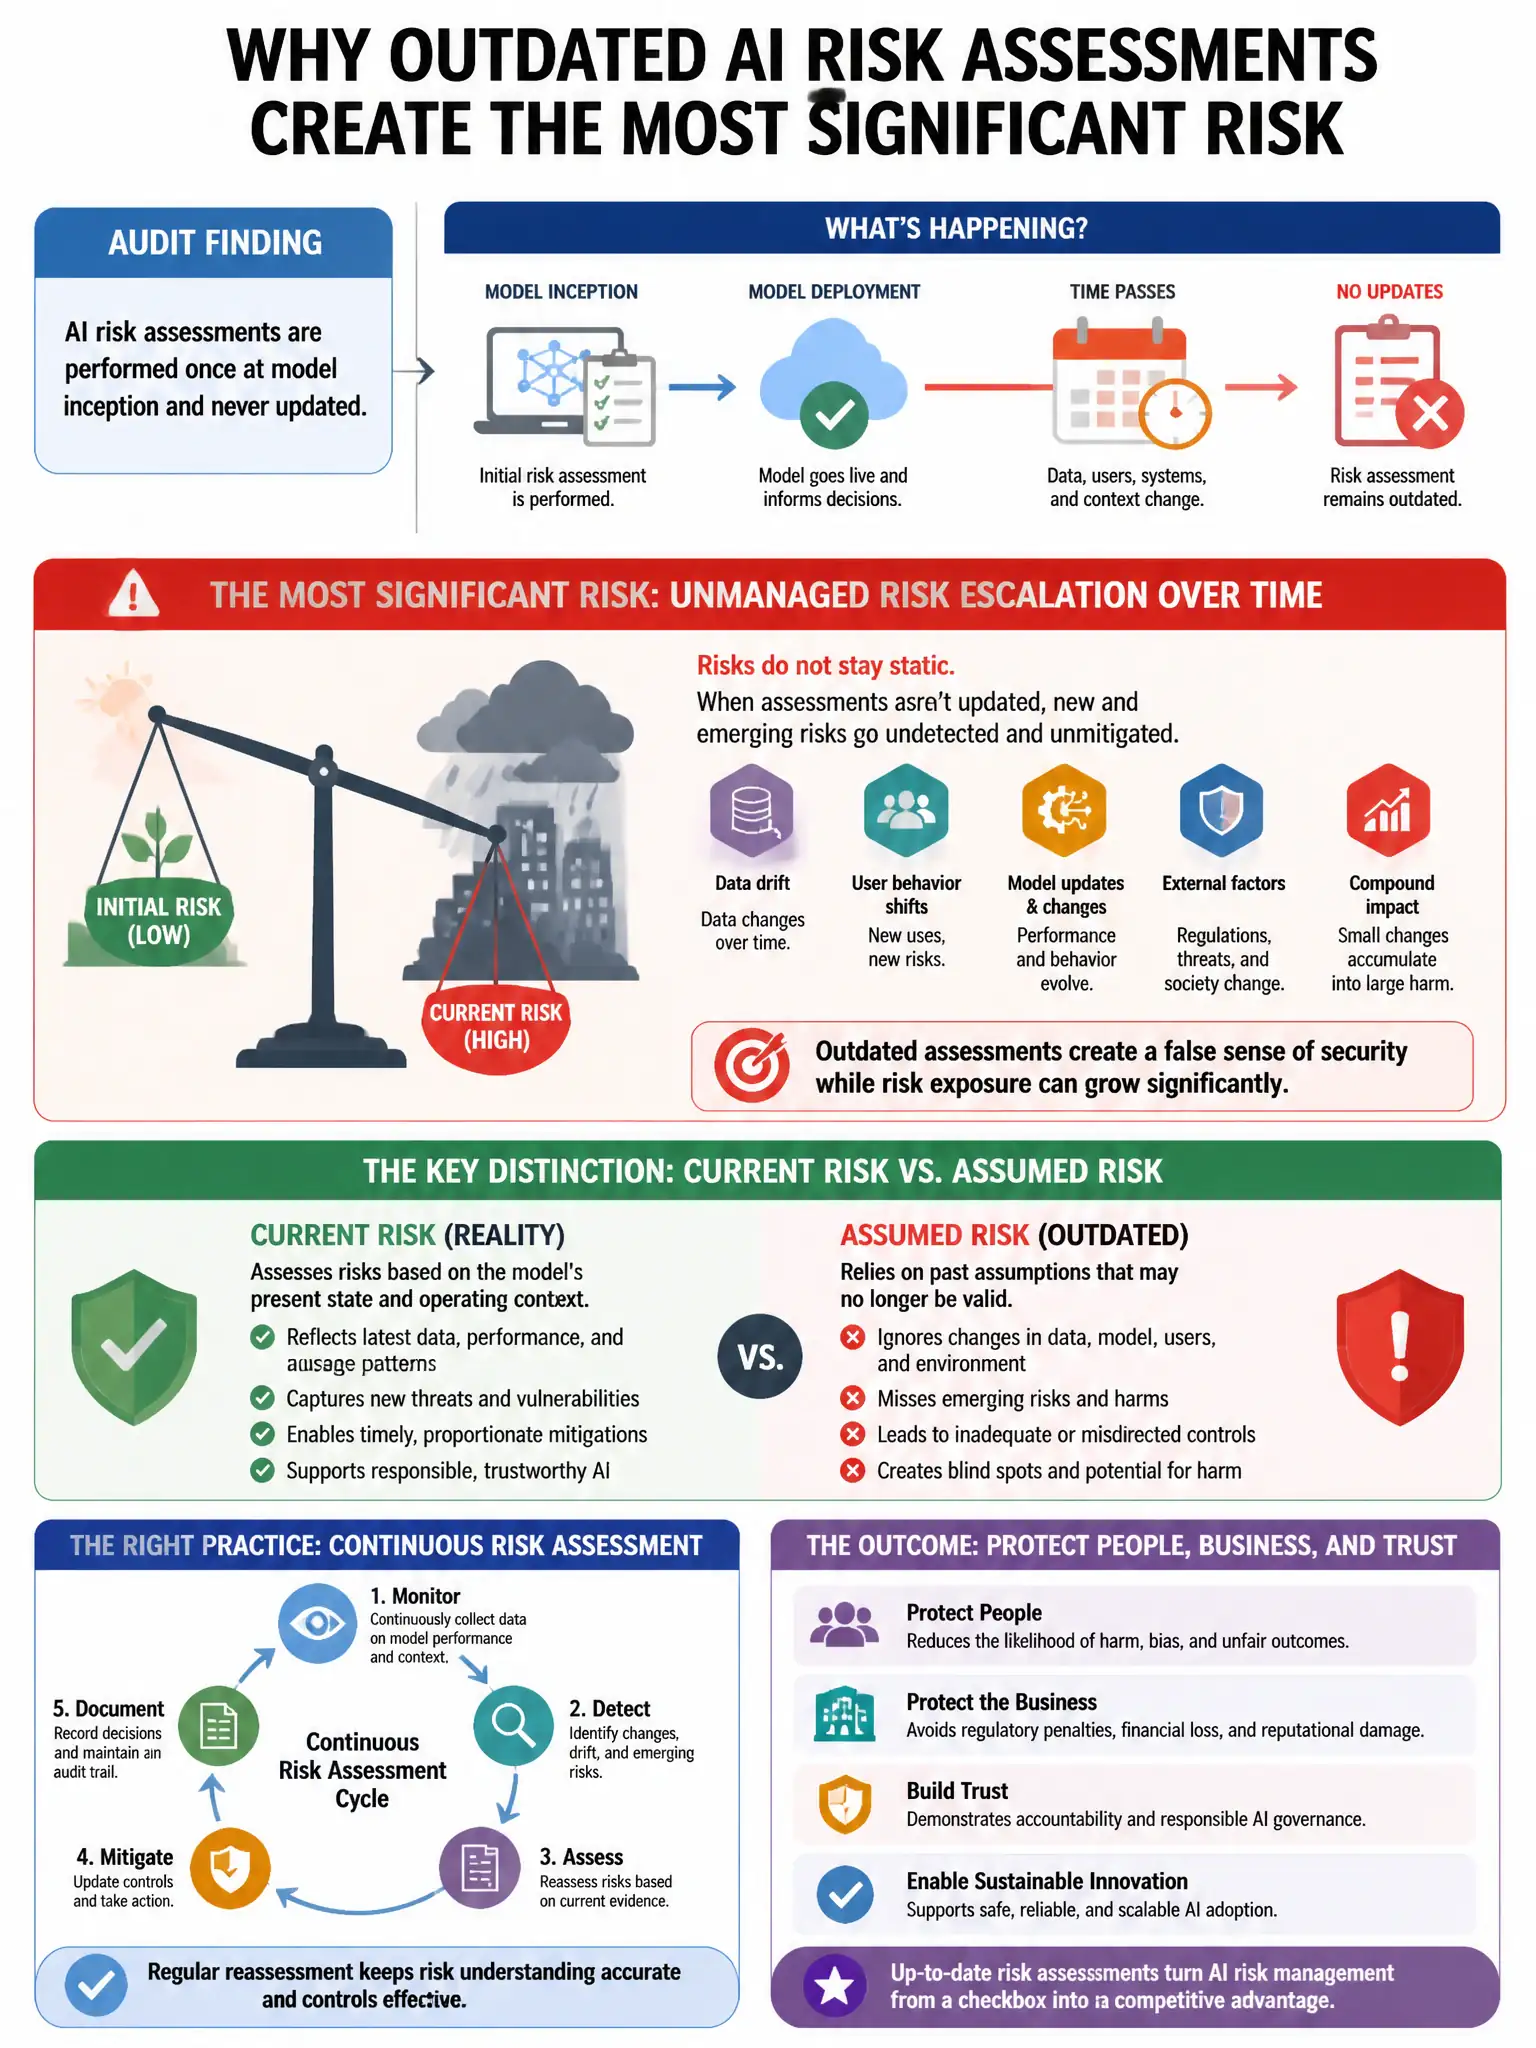
Here's the deal — you need ongoing artificial intelligence risk assessments because risk is dynamic. Models drift, use cases expand, regulations evolve, and the threat landscape changes, so one-time assessment goes stale fast.
Full Explanation
The correct answer is the option about failure to identify emerging risks from model drift, new use cases, regulatory changes, or changes in the operating environment after the initial assessment. Artificial intelligence risk is dynamic: models drift, use cases expand beyond original scope, regulations evolve, and the threat landscape changes. One-time risk assessment becomes stale almost immediately and fails to capture these evolving risks. Periodic or event-triggered updates are essential to maintaining current view of artificial intelligence risk. The methodology-inconsistency option is quality concern orthogonal to assessment frequency. The computational-cost option is negligible and not relevant risk. The documentation-compliance option is minor administrative concern compared with substantive risk management failure.