
A risk officer conducts a vendor assessment for a third-party AI fraud detection system. The vendor claims the model has been independently audited. Which follow-up question is MOST important?
Select an answer to reveal the explanation.
Short Explanation
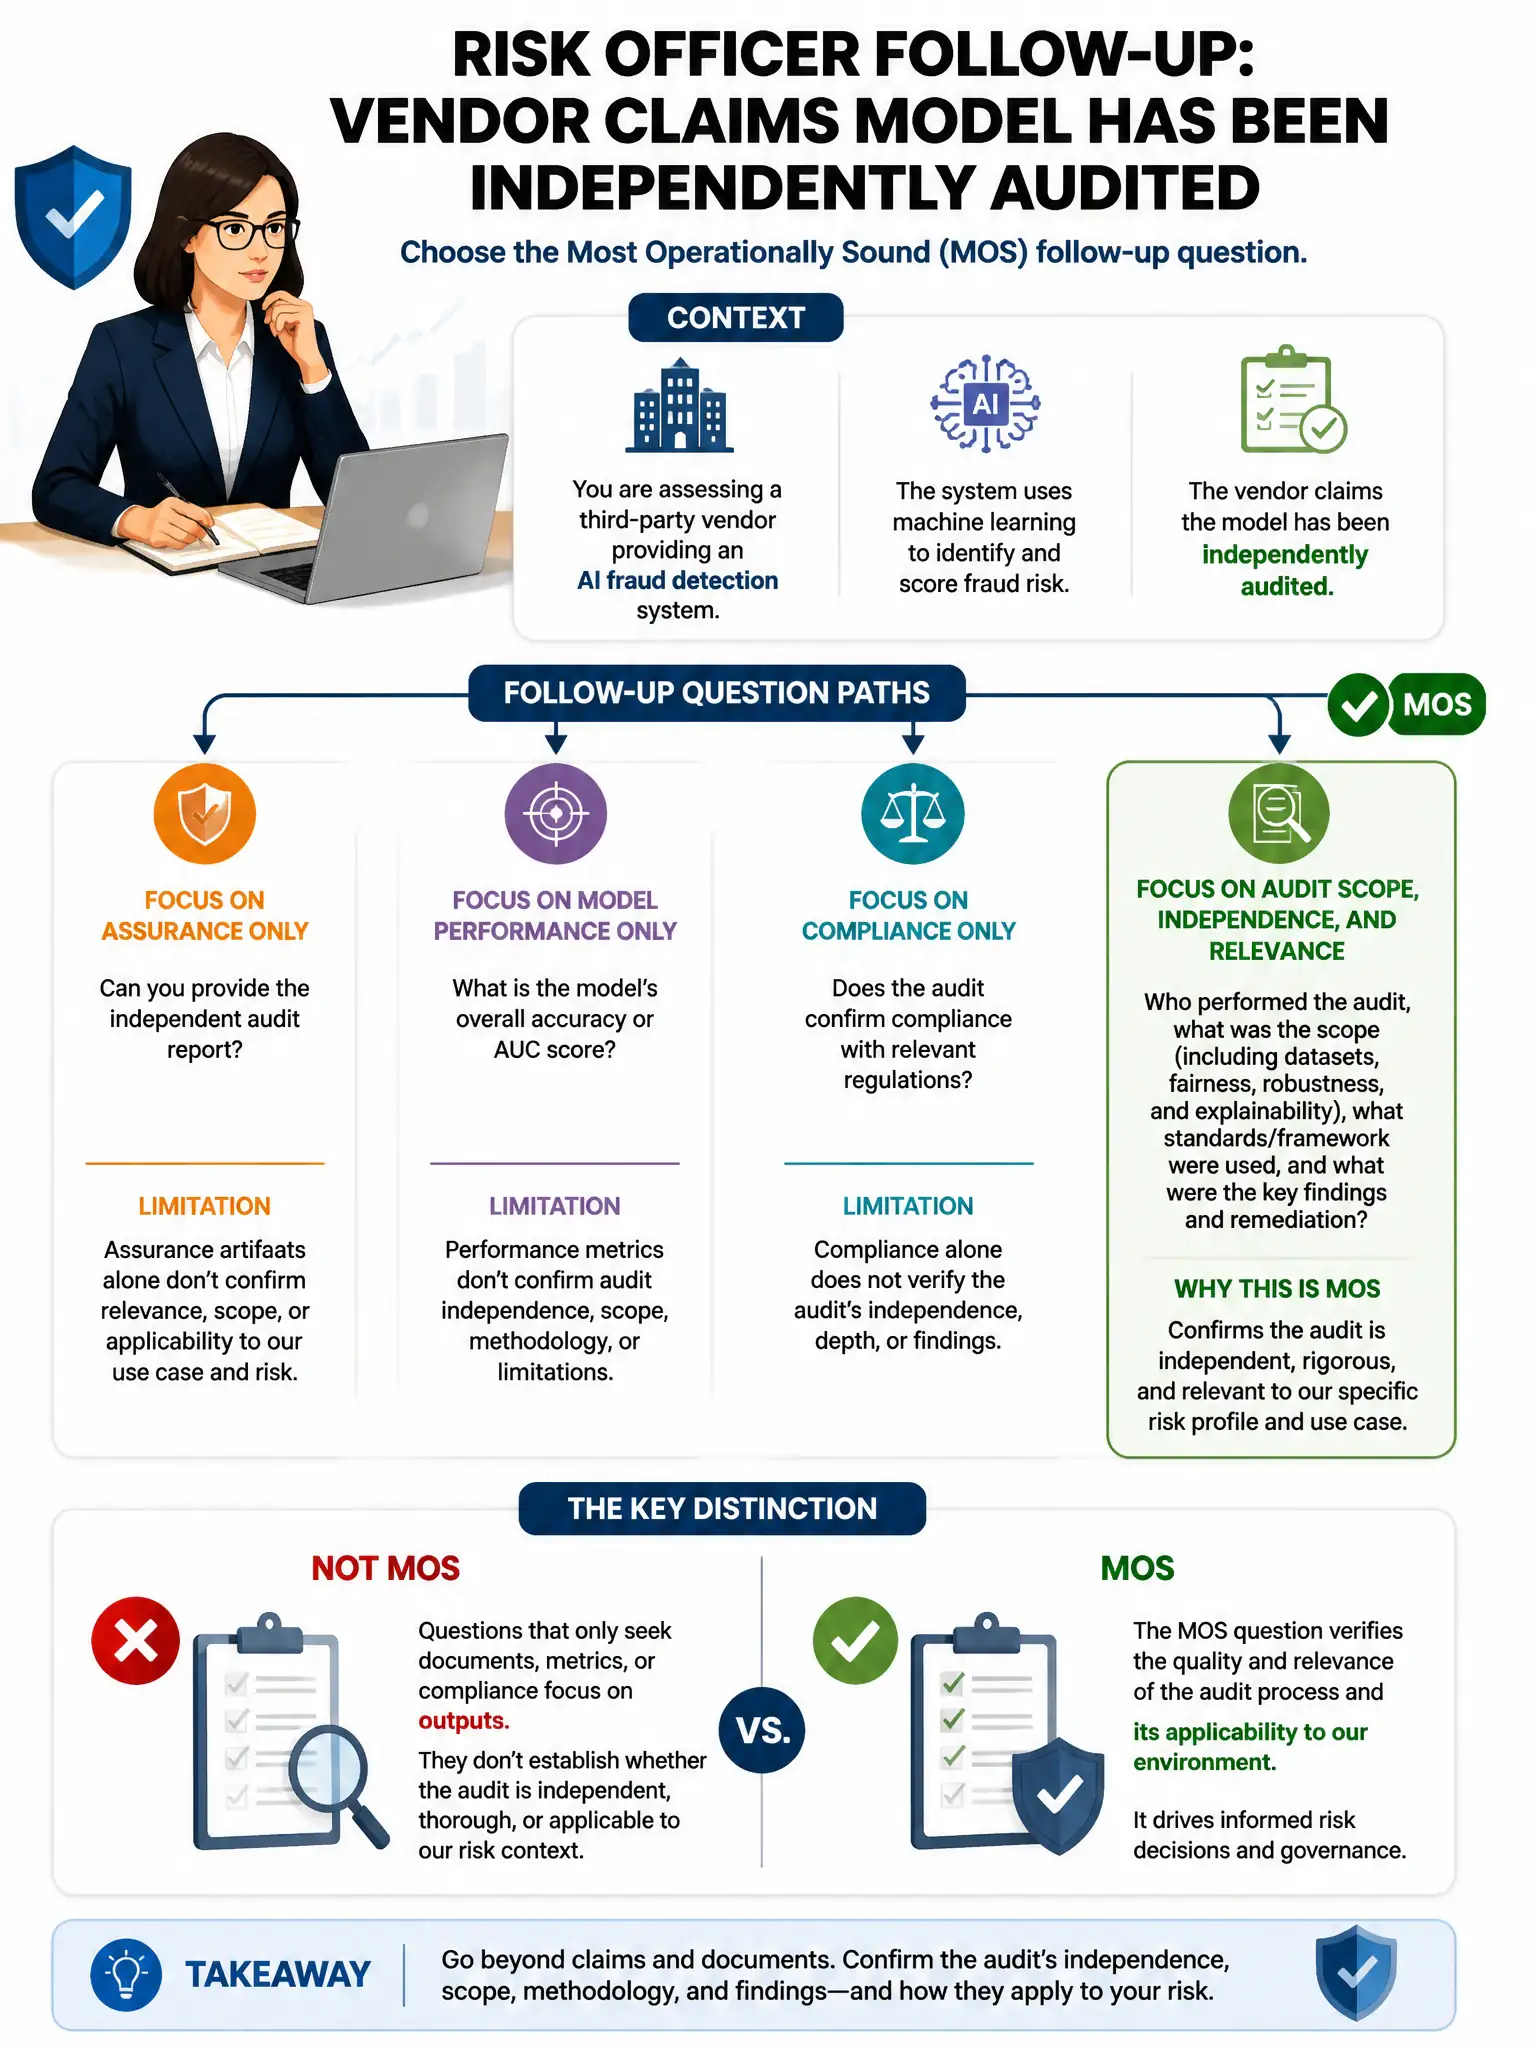
Here's the deal — you need to know what the audit actually covered, who did it, what standards they used, and whether you can review the report under NDA. An independent audit claim means little without that detail.
Full Explanation
The audit scope question is correct because an independent audit claim is only meaningful if the audit was conducted by a qualified, truly independent party, applied recognized standards such as ISAE 3000, SR 11-7, or NIST AI RMF, and covered the relevant risk dimensions including performance, fairness, security, and data governance. Without the audit report, the claim cannot be assessed. The programming language question is irrelevant to risk assessment. The question about how many other financial institutions use the same model is a market reference, not a risk control. The question about the total number of fraud cases detected since inception is a vendor marketing metric without statistical context.