
A proprietary trading firm operates an AI-driven high-frequency trading system that executes up to 40,000 orders per second. During a stress simulation, risk managers identified that human operators could not react fast enough to manually halt the system before it could breach position limits in an adverse scenario. Under MiFID II RTS 6 algorithmic trading requirements, what is the firm's primary obligation regarding this finding?
Select an answer to reveal the explanation.
Short Explanation
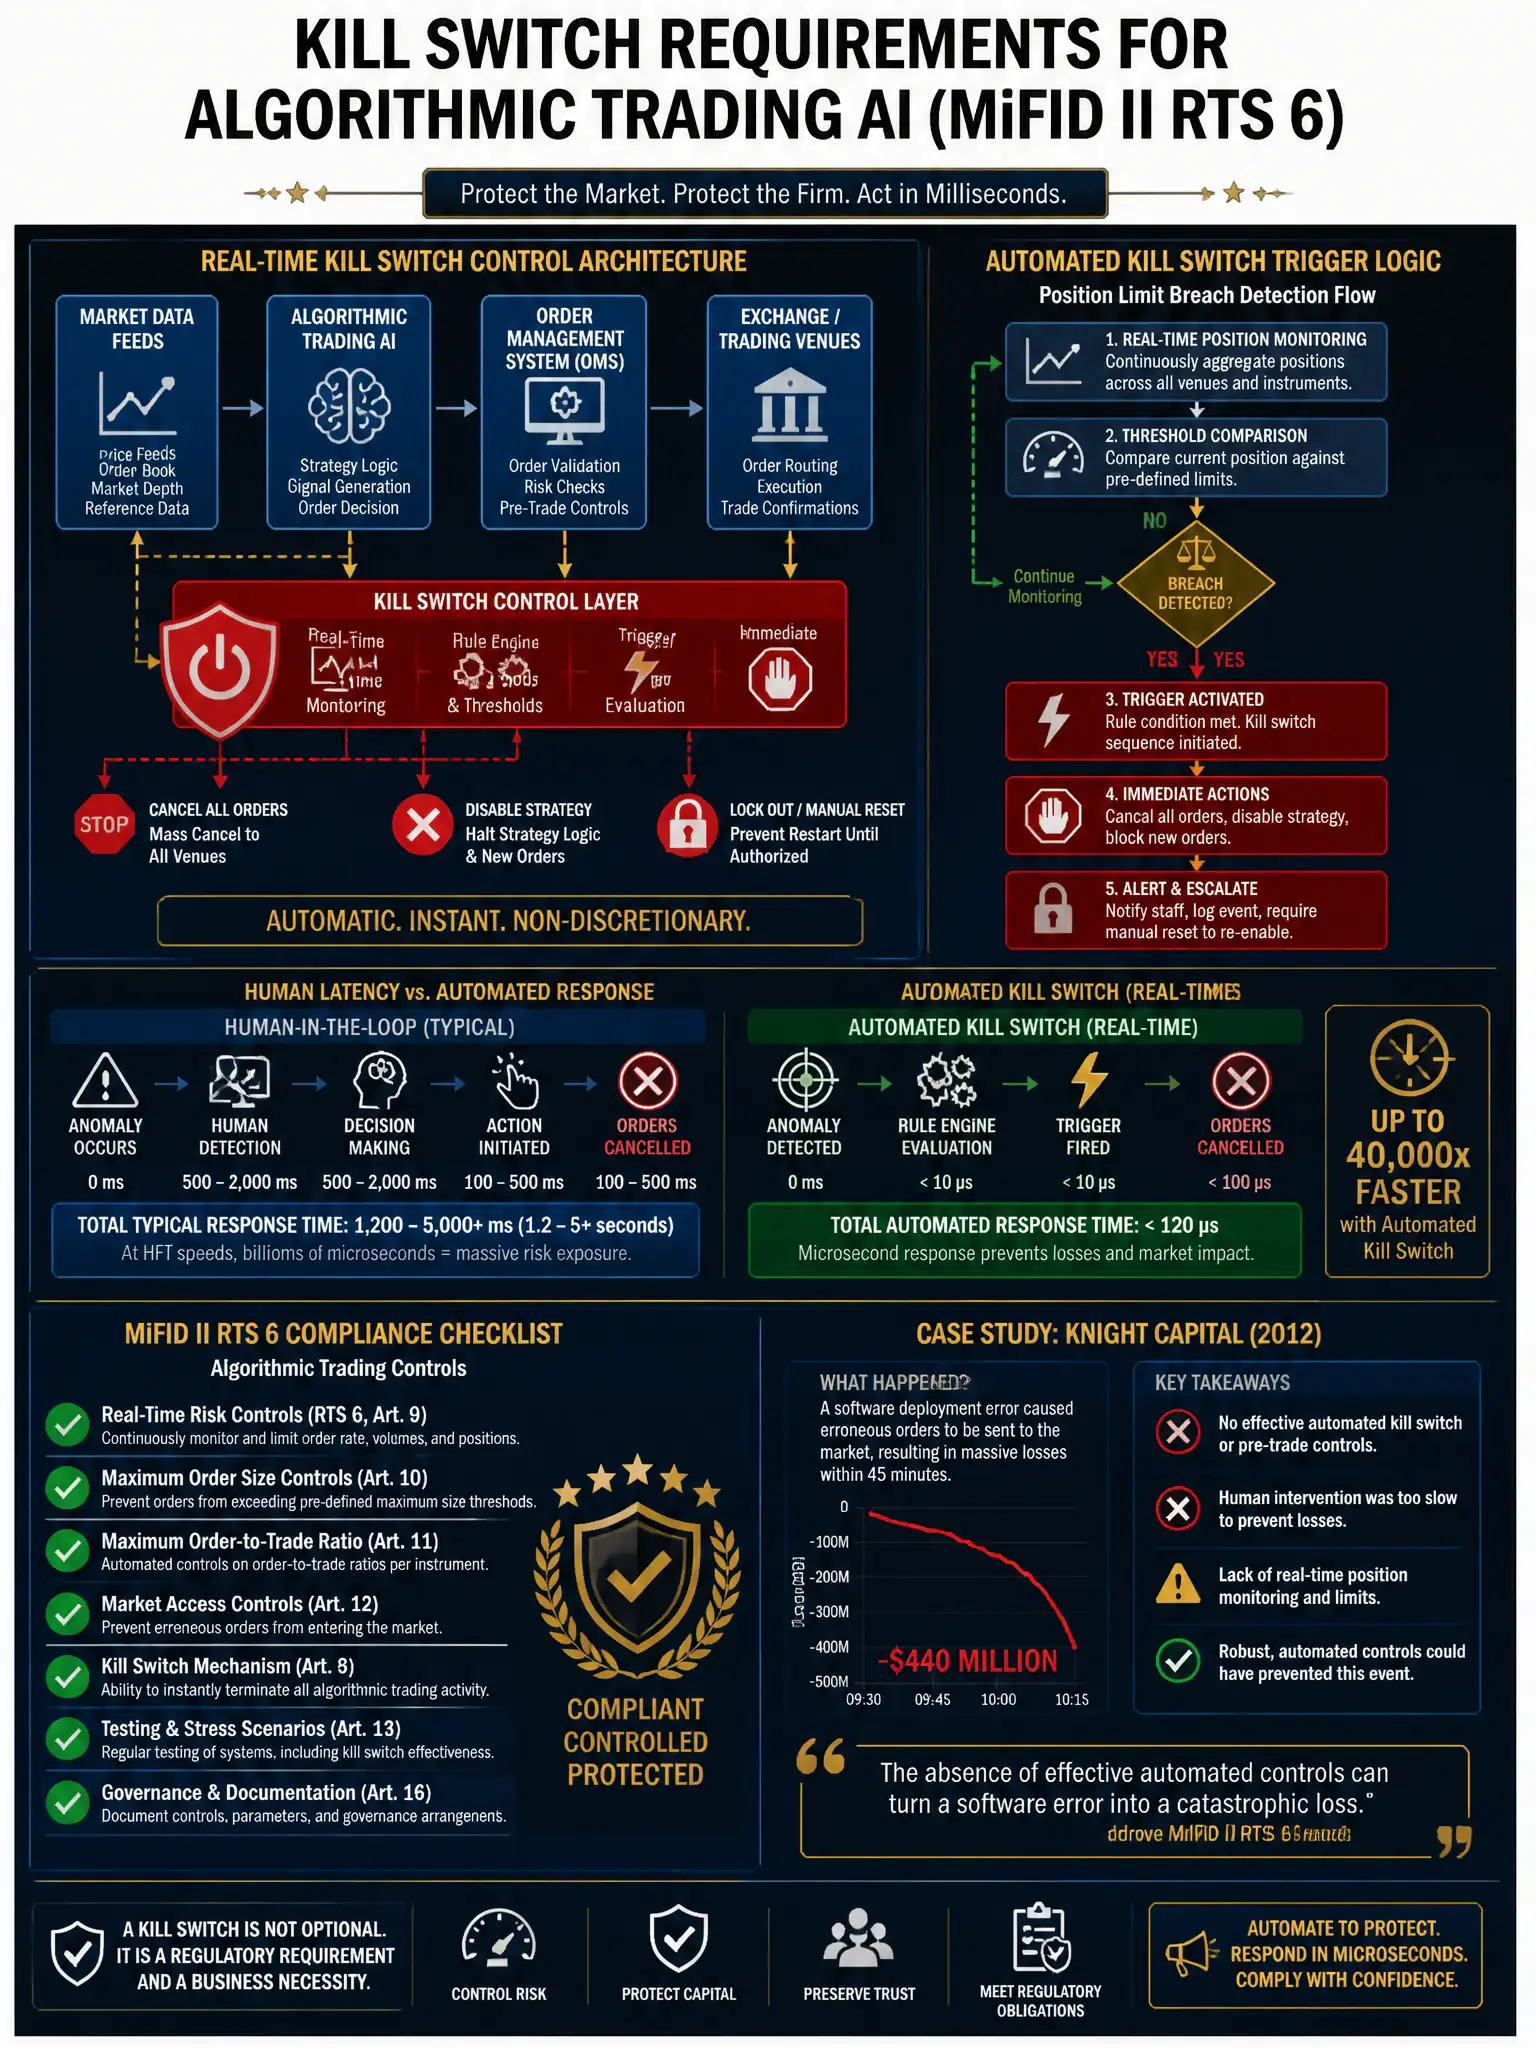
You've got to implement an automated kill switch that can immediately halt all or part of the algorithmic trading activity without human latency dependency, and test it under realistic market conditions. If your stress test shows humans can't stop the machine in time, you've documented a compliance gap that needs an engineering fix, not a training program or a regulator's permission slip.
Full Explanation
MiFID II's Regulatory Technical Standard 6 (Commission Delegated Regulation 2017/589) sets out organizational requirements for firms engaged in algorithmic trading. Article 12 explicitly requires that algorithmic trading systems include kill switch functionality capable of canceling all or part of outstanding orders and halting trading activity immediately. The standard further requires that this capability be tested regularly and that it be capable of operating without dependency on manual human reaction time. The stress simulation finding is significant precisely because it demonstrates a design gap: the kill switch, if it exists in only manual form, is ineffective at the speed the system operates. RTS 6 compliance requires that the kill switch be automated — capable of triggering based on predefined risk parameters such as position limits, loss thresholds, and order rate anomalies — without waiting for human initiation, and that it be tested under realistic trading conditions, not just documented. The specification for kill switch systems under RTS 6 and related European Securities and Markets Authority guidelines includes automated triggering based on quantitative risk thresholds; ability to operate at the latency of the trading system itself; cancellation of open orders across all venues simultaneously; audit logging of all activations; and regular testing in a simulated production environment. The content about documenting the finding in the firm's risk register and scheduling enhanced training for risk operators to improve manual intervention speed does not address the control gap — the problem is architectural, not operational. The content about reducing the system's maximum order rate to a level where human operators can reliably intervene within five seconds of detecting an adverse condition may be a complementary measure but does not fulfill the kill switch requirement and would fundamentally alter the firm's trading strategy. The content about notifying the relevant national competent authority and awaiting regulatory guidance before modifying the system's control architecture inverts the regulatory obligation — the firm is responsible for maintaining compliant controls at all times, and awaiting permission to fix a known gap during which the system remains deployed would compound the violation. The Knight Capital incident of 2012 — where a software deployment error caused an algorithmic system to generate $440 million in losses in 45 minutes — remains the defining case study for why automated kill switches with human-speed-independent operation are non-negotiable in high-frequency trading environments.