
A prime brokerage deploys an AI-driven margin call system that monitors 50,000 client accounts in real time. During a sudden market dislocation, the model enters a degraded inference state — producing erratic margin calculations — while the firm's human oversight team is offline for a scheduled maintenance window. Under DORA (EU Digital Operational Resilience Act) and operational resilience principles, which control failure is most significant?
Select an answer to reveal the explanation.
Short Explanation
You need a fallback mode that kicks in automatically when the AI's confidence drops. DORA expects critical functions to stay within impact tolerances when a component fails, so an erratic margin model with no safe-state is the real control failure.
Full Explanation
The EU's Digital Operational Resilience Act (DORA, Regulation 2022/2554), effective January 2025, imposes specific requirements on financial entities' ICT risk management frameworks, including AI systems that support critical or important functions. The margin call system processing 50,000 accounts in real time clearly qualifies as a critical ICT function under DORA's taxonomy.
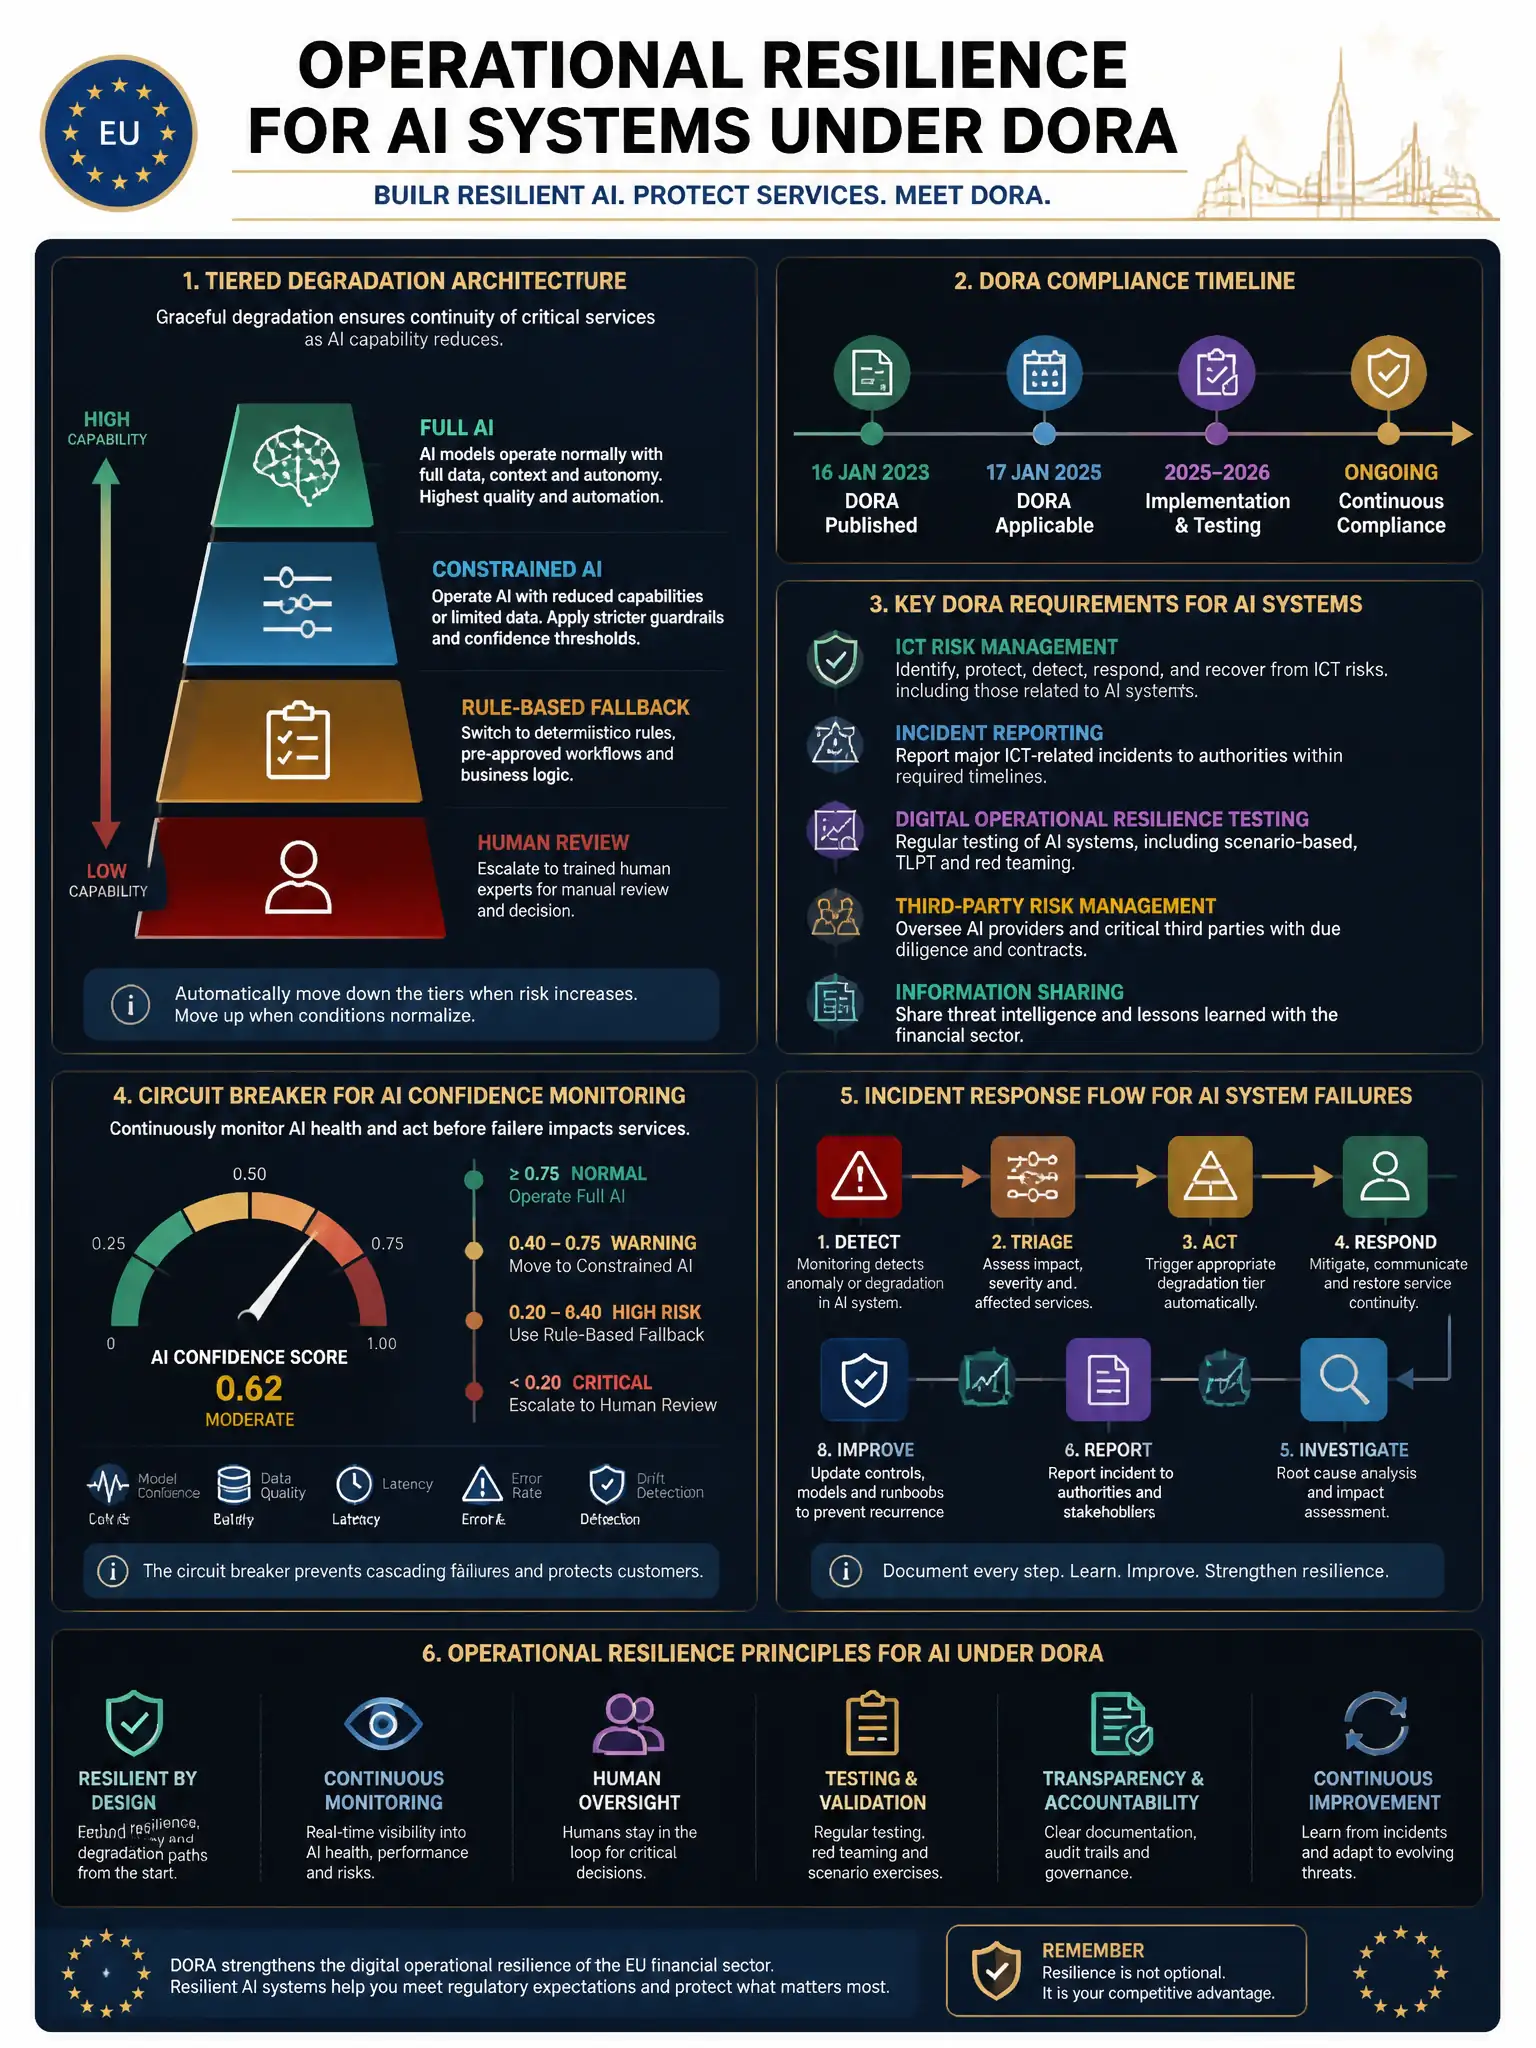
DORA's resilience principles require that critical functions remain operational within defined impact tolerances even when individual components fail. This requires pre-defined fallback mechanisms — not reactive improvisation during an incident. For an AI inference system, operational resilience standards require: confidence score monitoring with automated circuit breakers; fallback to a simpler, more interpretable computation method, such as rule-based margin calculations, when the AI model's outputs become unreliable; human-in-the-loop escalation paths that are not contingent on scheduled availability; and regular testing of these fallback paths under simulated stress conditions.
The scenario describes a double failure: the AI system degraded without a failsafe, and human oversight was unavailable. The architectural failure is the absence of a pre-defined fallback operating mode that activates automatically when AI model confidence scores fall below acceptable thresholds, maintaining service within impact tolerances. The human availability gap is a secondary compounding factor, not the root cause.
The annual penetration testing of the AI system's API endpoints before deployment is a DORA requirement, but it addresses ICT security rather than operational continuity. The insufficient documentation of the AI model's training data provenance in the firm's ICT asset register relates to the ICT asset register, which is a DORA obligation but administrative rather than operational. The failure to notify the relevant NCA within 24 hours of detecting the degraded state addresses incident reporting; DORA does require reporting major ICT incidents to national competent authorities, but the timing threshold is generally four hours for initial notification of major incidents, not 24 hours, making that response doubly incorrect.
From a design standpoint, the firm should implement a tiered degradation architecture: full AI inference in normal state, constrained AI with confidence floor, rule-based fallback, and human review queue, each with defined activation thresholds and escalation protocols.