
A European asset manager is deploying an AI system that continuously monitors retail clients' emotional states through voice analysis during advisory calls, then dynamically adjusts portfolio recommendations to exploit detected anxiety signals in order to increase product sales. Under the EU AI Act, how should a compliance officer classify this system?
Select an answer to reveal the explanation.
Short Explanation
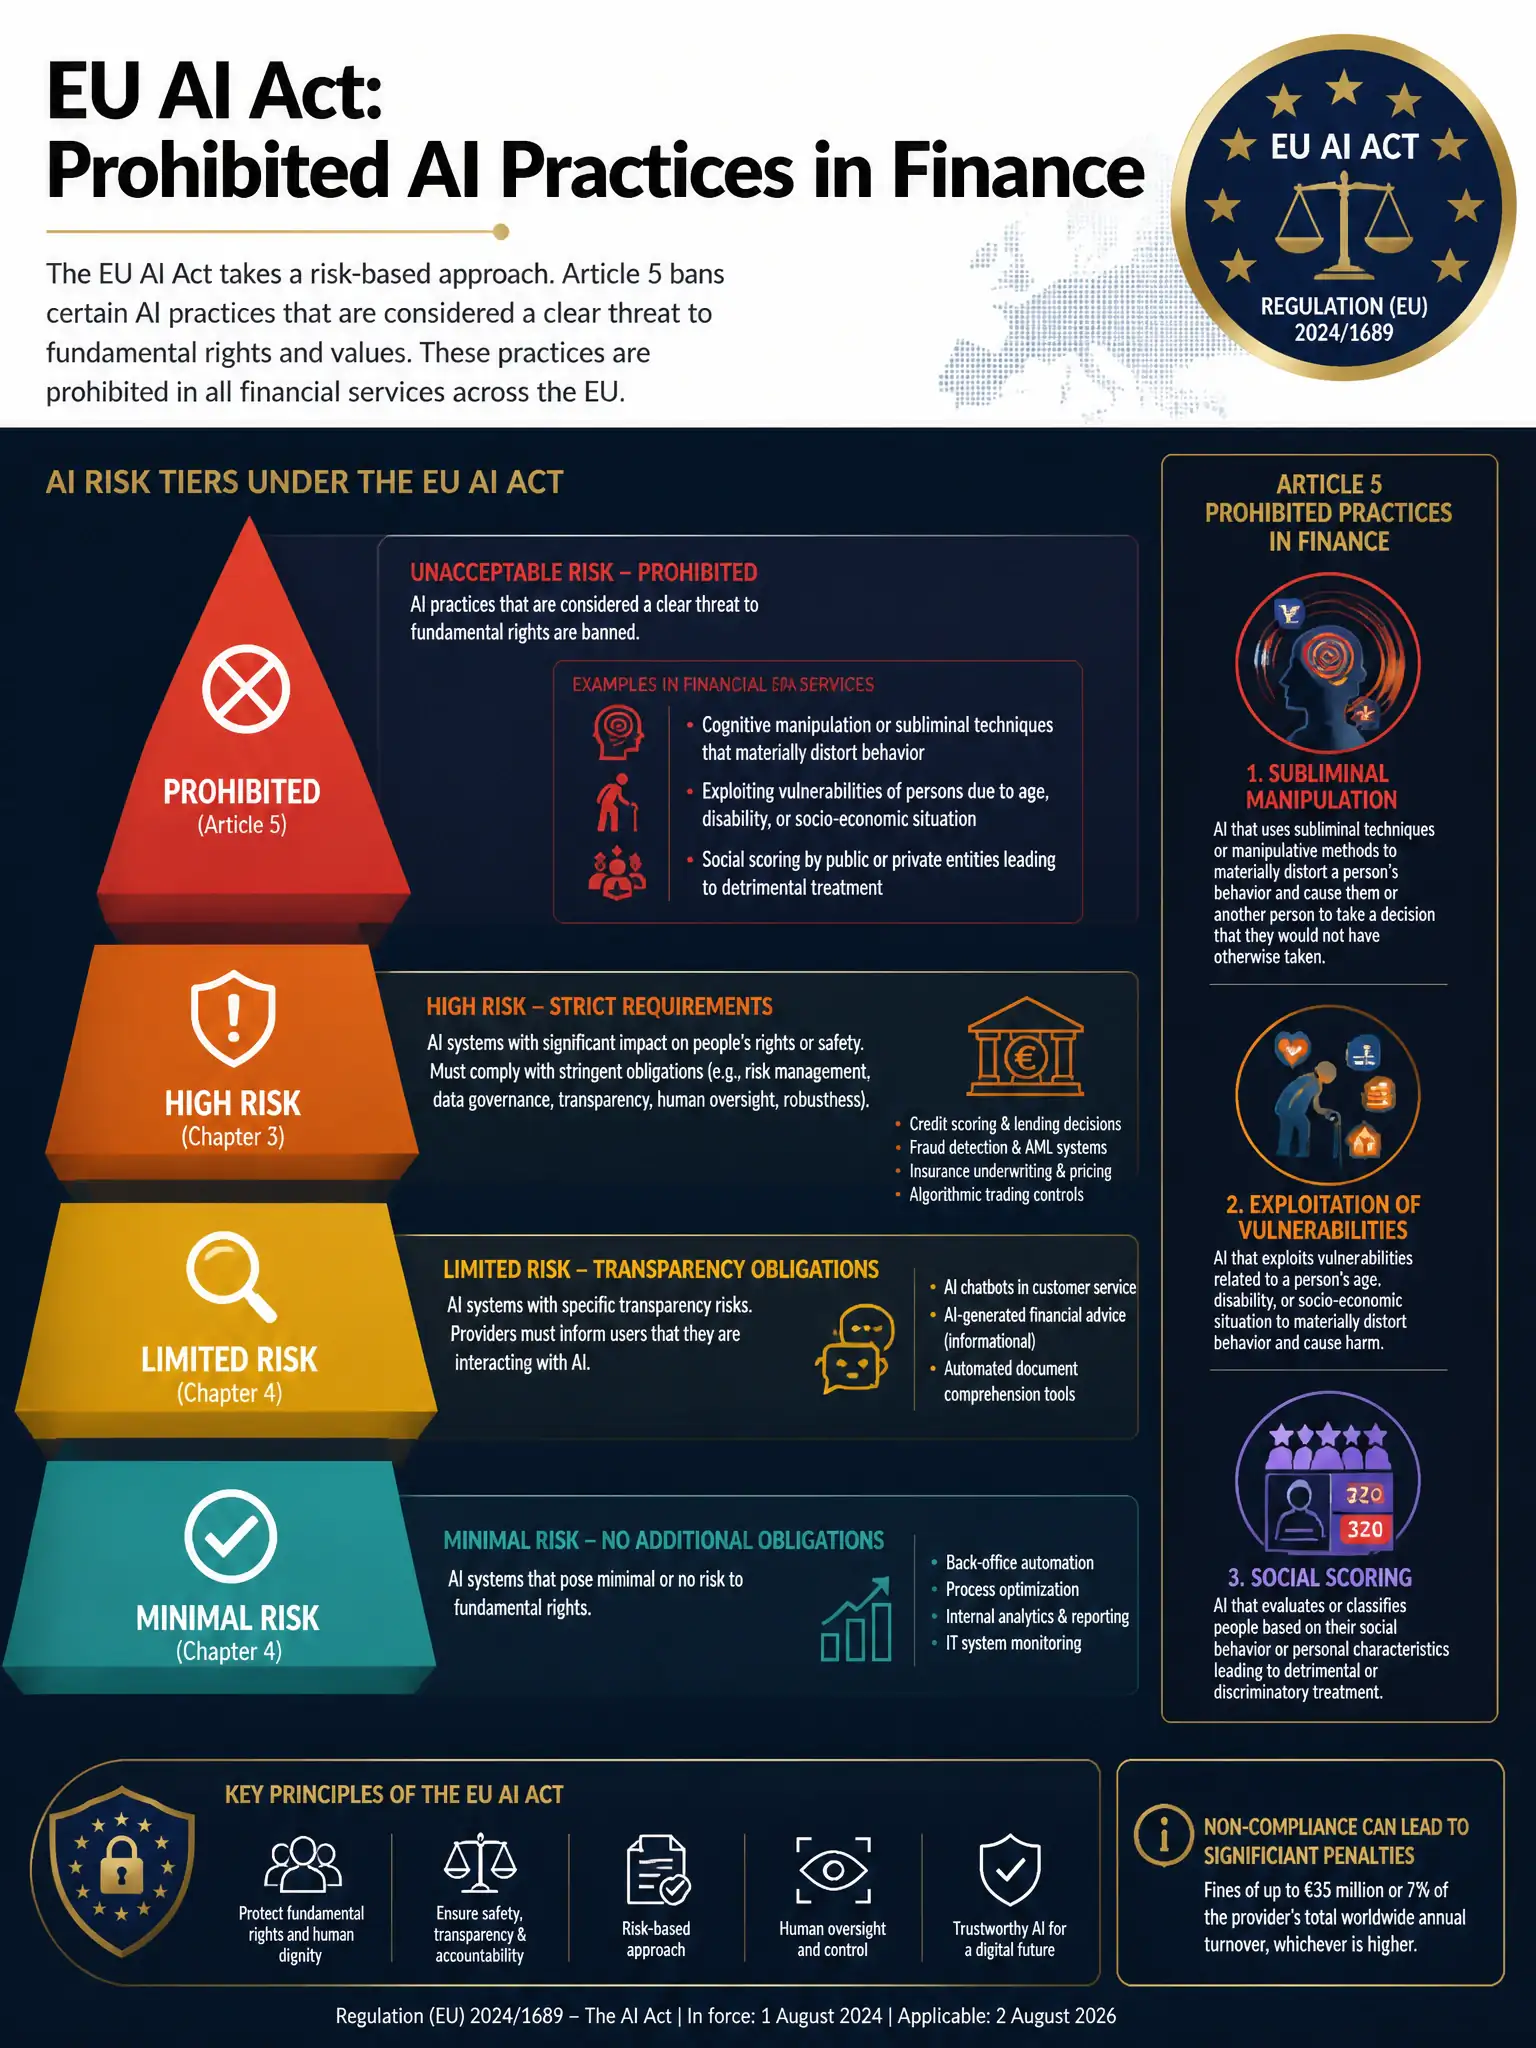
Think of it this way — the EU AI Act's prohibited list is the 'absolute no-fly zone,' and if you exploit emotional vulnerabilities to manipulate financial decisions, you're squarely in that zone. This system does exactly what the Act forbids: it uses subliminal techniques targeting psychological weaknesses to override a person's rational financial judgment. No amount of disclosure or conformity assessment makes this legal — it's simply banned.
Full Explanation
The EU AI Act (Regulation 2024/1689) establishes a tiered risk framework with four levels: unacceptable risk (prohibited), high risk, limited risk, and minimal risk. Article 5 enumerates AI practices that are entirely prohibited across the EU, regardless of the operator's intent or any safeguards implemented. The system described triggers at least two of Article 5's prohibitions simultaneously. It deploys subliminal techniques — voice-based emotional analysis operating below clients' awareness — to influence behavior. More critically, it exploits psychological vulnerabilities (anxiety) to distort financial decision-making in a manner that causes or is likely to cause harm. This is the definitional core of manipulative AI the Act was designed to prevent. Financial services receive no carve-out from Article 5 prohibitions. The fact that the system is used in an advisory context, or that sales outcomes are a legitimate business goal, is legally irrelevant. The mechanism of action — covert emotional exploitation to override rational choice — is what triggers the prohibition. The high-risk classification requiring conformity assessment and registration in the EU database before deployment would apply to legitimate AI systems used in credit scoring, insurance risk assessment, or employment decisions, which do require conformity assessments. The limited-risk classification subject only to transparency obligations requiring disclosure to clients applies to chatbots and AI-generated content requiring disclosure. Neither classification is available for systems that fall under Article 5 prohibitions — classification into any permitted category is foreclosed. The minimal-risk classification with no specific regulatory requirements under the EU AI Act framework is also wrong because the system is not merely low-risk; it falls within the prohibited-practices category. Compliance officers should conduct Article 5 screening as the first gate in any AI deployment review, before assessing risk level. Any system touching emotional or biometric inference in a client-facing financial context warrants heightened scrutiny against the prohibited practices list.