
With budget for only one risk-identification pass before launch, a proof of concept is being converted into a governed production system. What should that pass cover?
Select an answer to reveal the explanation.
Short Explanation
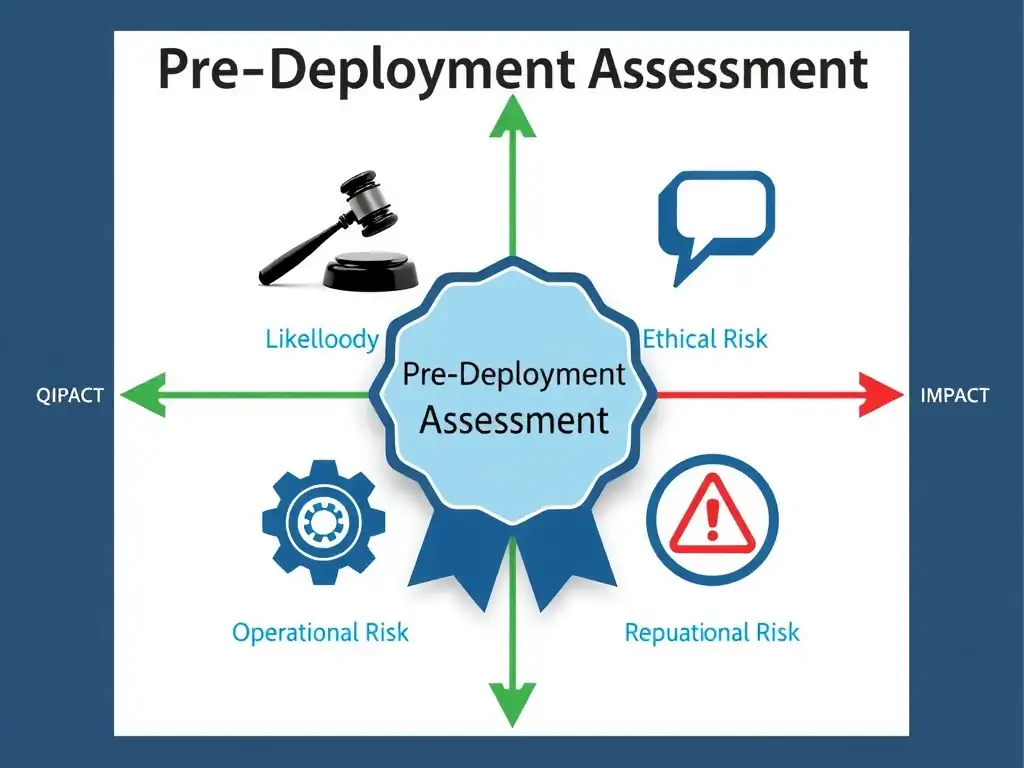
With only one pass, you need to cover all four risk categories together, not just one. Going deep on a single category leaves the other three unassessed.
Full Explanation
The correct answer is the approach that assesses regulatory, ethical, operational, and reputational risk together in one pass. When resourcing is limited, breadth across the four risk categories catches more of the exposure that actually threatens the launch than depth in a single category ever will.
A deep-dive on operational risk only is incorrect because a system can be operationally solid while still causing ethical or reputational harm that operational analysis alone would not surface.
A deep-dive on regulatory risk only is incorrect for the same reason; regulatory exposure being quantifiable does not make it the only category worth assessing.
Scoping the assessment to whichever single category the project lead's own background makes them most confident assessing is incorrect because that is not a risk-based rationale at all.
For the exam, default to covering all four categories, even briefly, over exhaustively covering one.