
Which statement about programmatic access to watsonx.data is correct?
Select an answer to reveal the explanation.
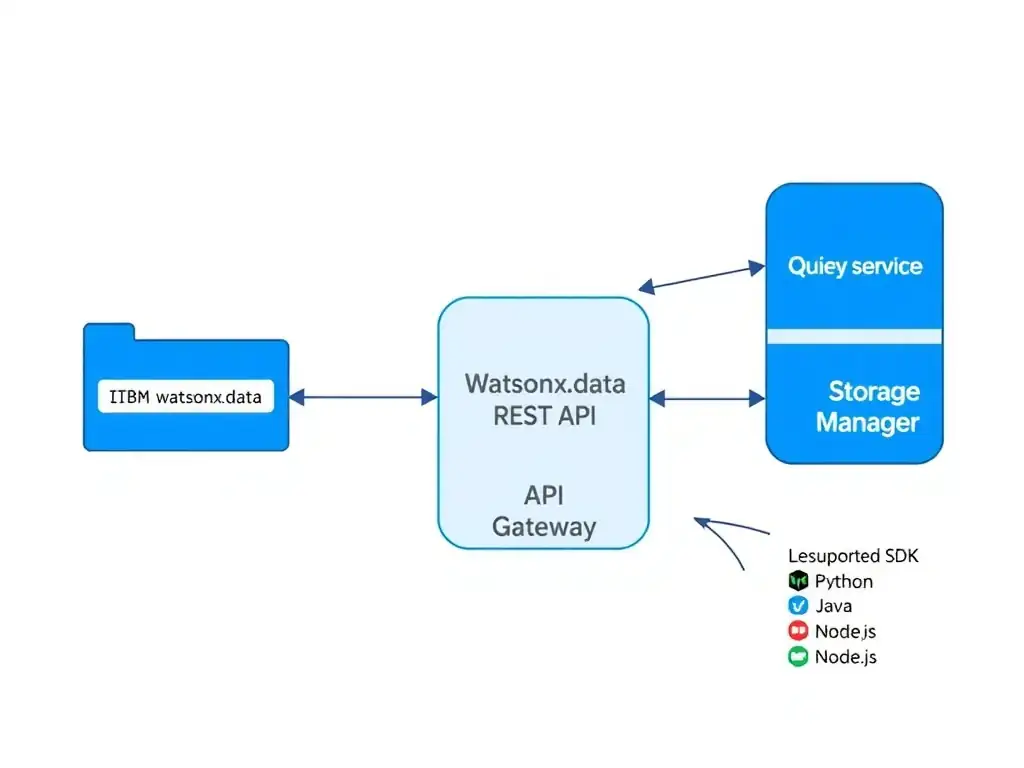
Short Explanation
You connect programmatically through supported clients and APIs, authenticate as the application's own identity, and stay under the same governance as interactive users. If an answer skips the supported interface, the app's own identity, or the same governance, it's wrong.
Full Explanation
Applications should use supported clients and APIs authenticated as their own identities, and remain subject to the same governance as interactive users. Programmatic access uses documented drivers and APIs, authenticates as a service identity belonging to the application, and is governed identically to interactive access because policy is evaluated per request against the identity.
Direct storage-layer access, since APIs are intended for administration only, is incorrect because data access APIs and drivers exist precisely so applications need not touch storage, and direct storage reads bypass governance.
Reusing an interactive user's session where a service identity is unavailable is incorrect because it is a credential-sharing failure that destroys attribution and grants the application a person's full rights.
Bypassing catalog metadata and reading table definitions from developer-supplied configuration is incorrect because table resolution goes through the catalog. Developer-supplied definitions would drift from the actual schema immediately.
For the exam, hold the three requirements together: supported interface, own identity, same governance.