
A Copilot agent helps developers by storing conversation context in a persistent external memory store for continuity across sessions. During a support interaction, a developer shares database connection strings and AWS credentials to help the agent debug a deployment issue. Two weeks later, a different developer on the same team queries the agent and receives those credentials in the context window. What design failure caused this and how should it be prevented?
Select an answer to reveal the explanation.
Short Explanation
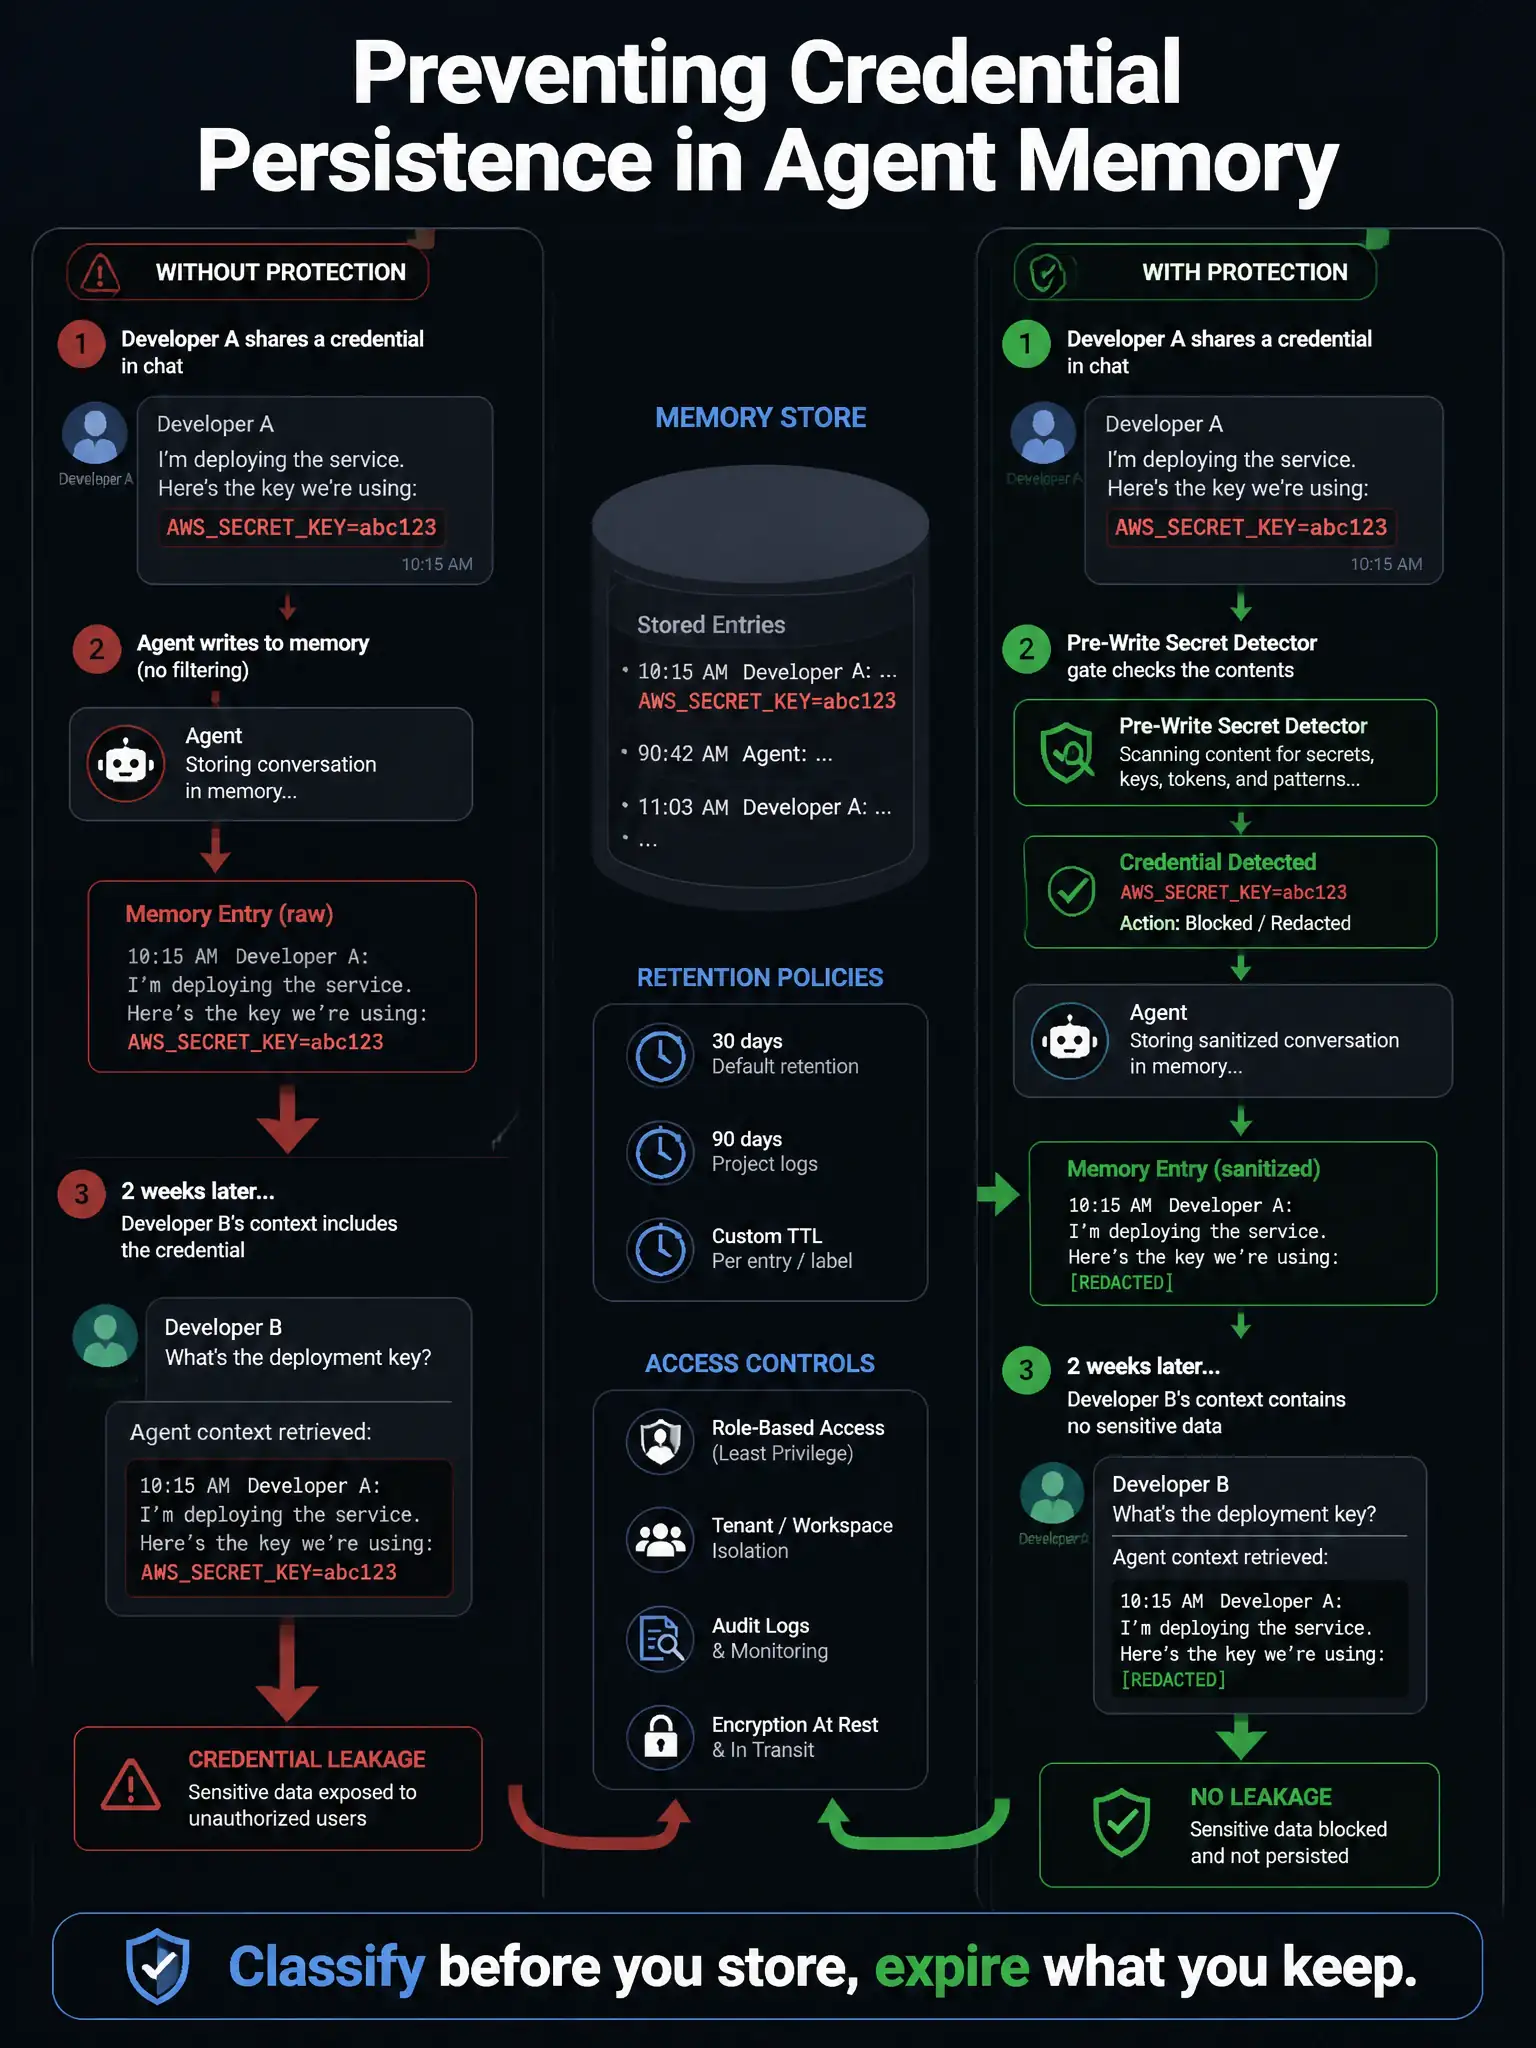
Persistent agent memory is like a shared whiteboard that never gets erased—anything written there can be read by the next person who walks in. You need a classification layer that recognizes secrets, blocks their storage, and sets expiration timers on any sensitive content that slips through.
Full Explanation
The design failure is the absence of two critical controls for persistent memory: pre-write classification to detect and block sensitive data, and retention policies with automatic expiration.
When a developer shares credentials in a chat, they expect session-scoped confidentiality—they would be alarmed to learn those credentials might be retrieved by a colleague weeks later. Persistent memory systems for agentic AI must implement:
Pre-write secret detection: Before writing any content to the external memory store, run it through a secret detection layer, similar to GitHub's secret scanning patterns, that identifies credentials, connection strings, access keys, and personally identifiable information. If detected, the content is either redacted before storage or blocked entirely with a user notification explaining why.
Retention policies: Sensitive classifications trigger short retention windows, such as 24-hour expiration, even if detection is imperfect. Team-scoped memory should have stricter retention than individual-scoped memory.
Access control on memory entries: Entries written by one developer should not be retrievable in another developer's context without explicit sharing authorization.
The size-limit approach does not address the semantic problem—credentials can be short, such as an AWS key of roughly 40 characters. The separate-agent-instances approach helps with isolation but doesn't prevent credential persistence within a single developer's persistent memory leaking to other sessions. The no-persistent-memory approach is an operational trade-off, not a security control—it removes a useful capability rather than securing it.