
A Copilot agent that was managing dependency updates is being retired because a third-party solution is replacing it. The agent had a GitHub App installation, a stored fine-grained PAT, a secrets manager entry, an MCP server running on an internal host, and a webhook configured on 15 repositories. What is the correct order of decommission steps to avoid security gaps?
Select an answer to reveal the explanation.
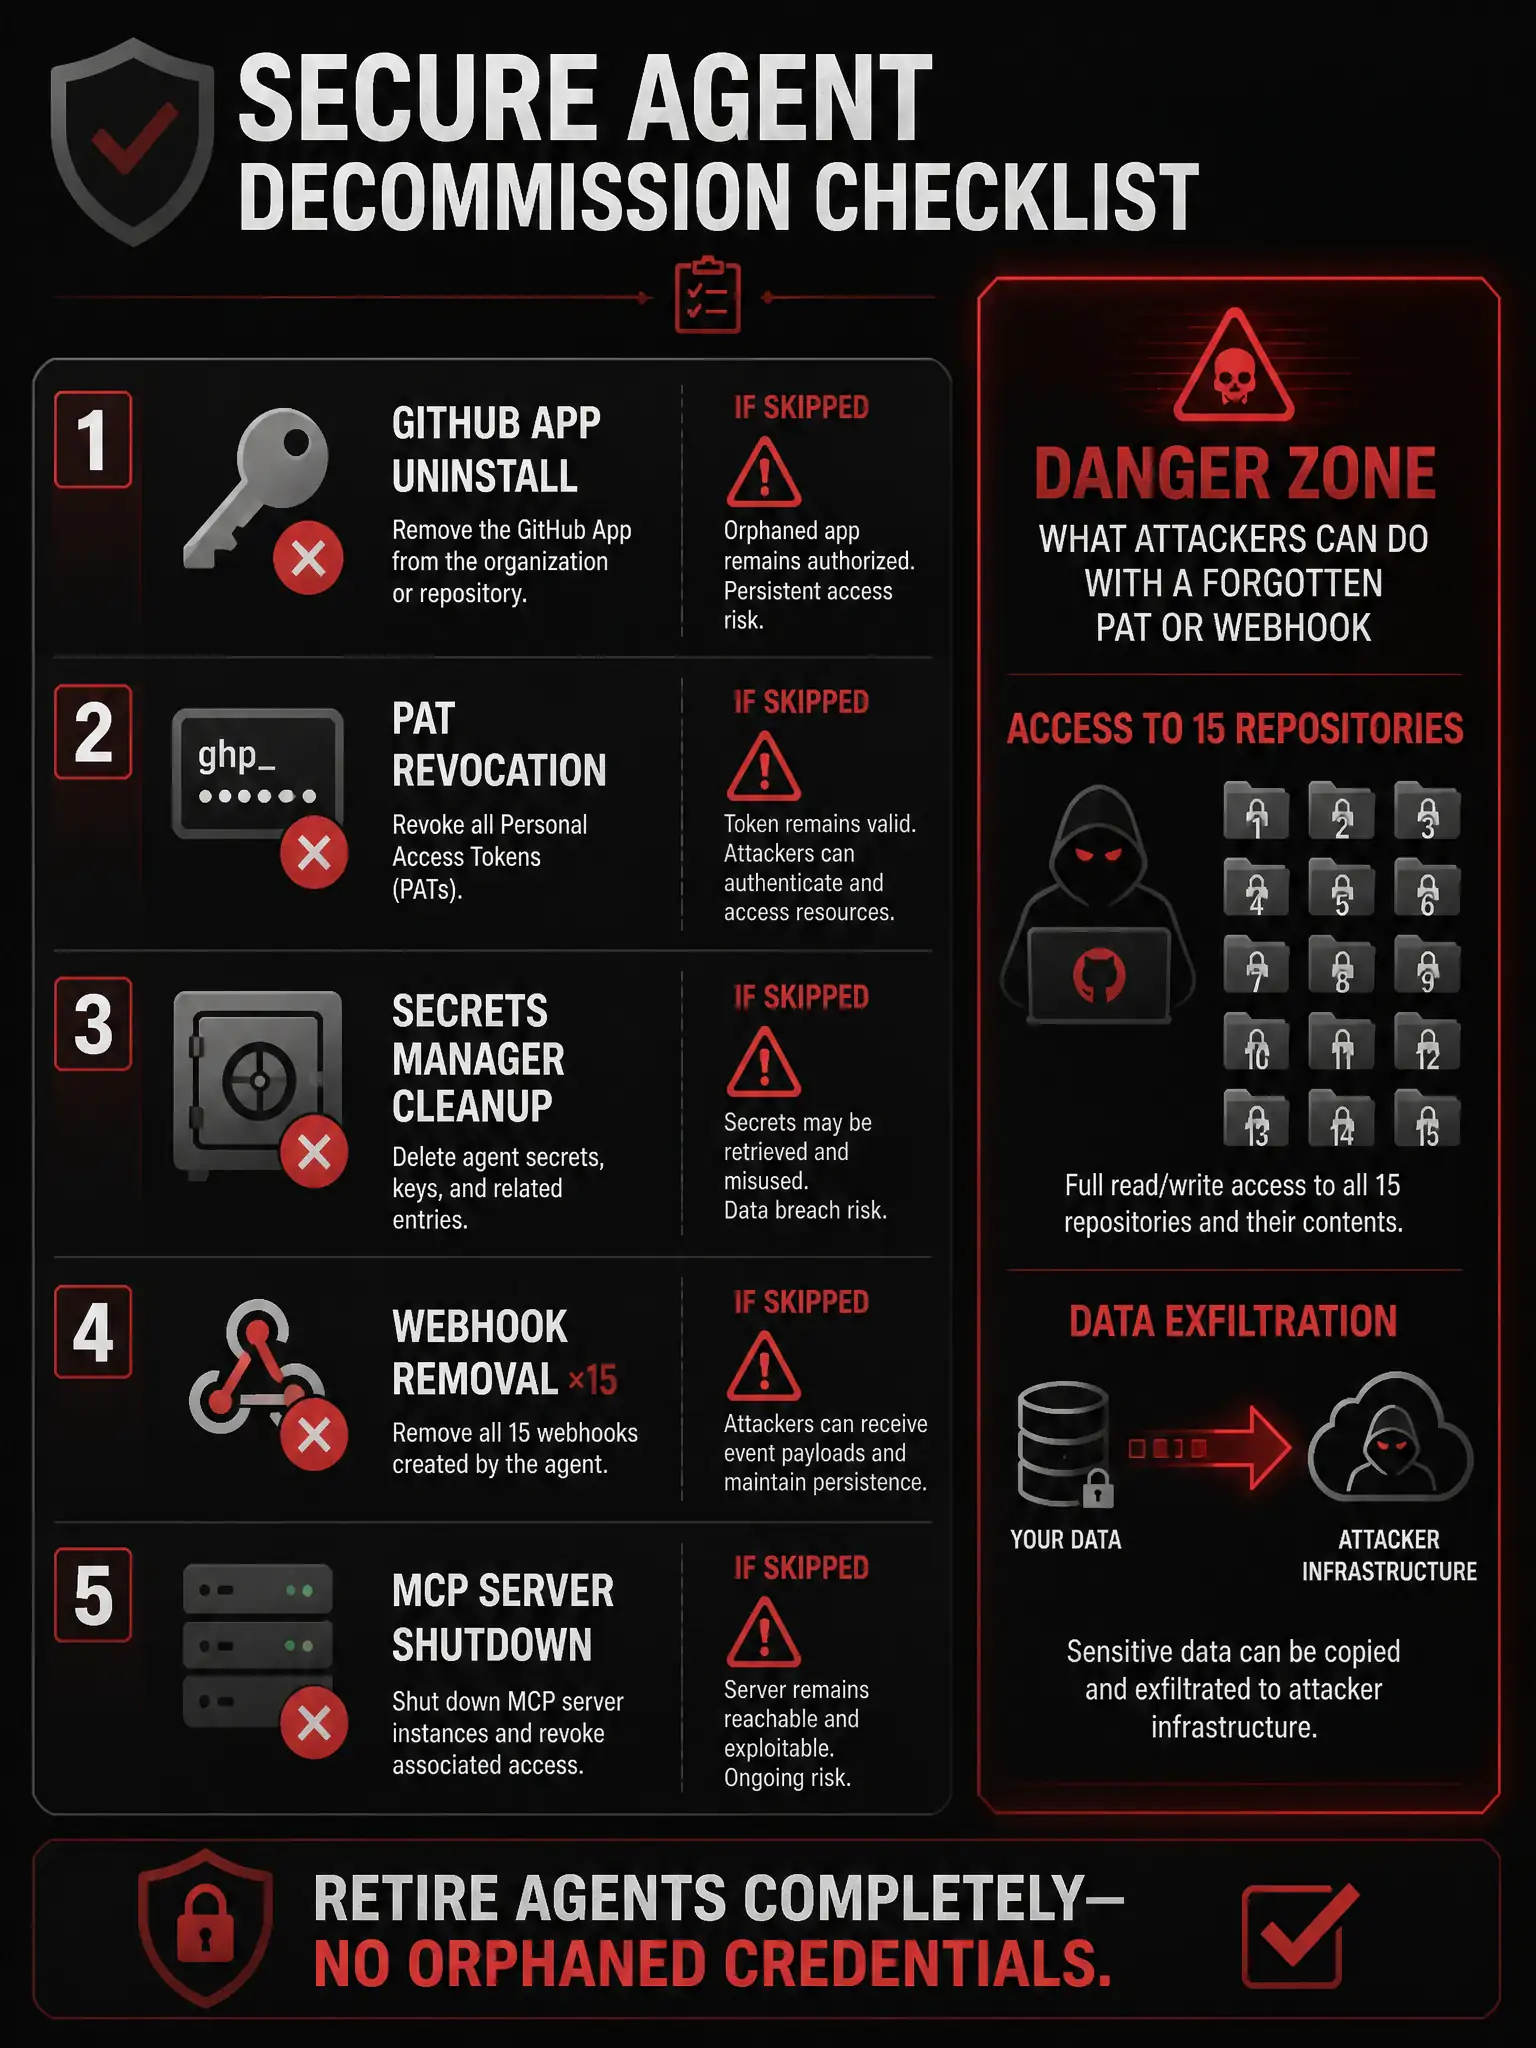
Short Explanation
When you retire an agent, you revoke its access first—GitHub App and PAT—then clean up secrets and webhooks before taking the MCP server offline. Don't leave orphaned credentials or webhook endpoints sitting around for attackers to grab.
Full Explanation
The secure agent decommission procedure must address every attack surface the agent had, in an order that minimizes the window of vulnerability. The correct sequence is to revoke the GitHub App installation and the fine-grained PAT, delete secrets from the secrets manager, remove webhooks from all repositories, and then shut down the MCP server. Begin by revoking the GitHub App installation: this immediately removes the agent's ability to authenticate to any GitHub API and closes the highest-impact credential. Uninstalling, rather than merely disabling, the App also removes all associated webhooks at the platform level. Then revoke the PAT: fine-grained PATs are separate credentials that must be explicitly revoked, and waiting for expiration can leave weeks or months of active access. Next, delete secrets from the secrets manager: removing the credentials from the secrets store ensures no other process can retrieve them and no future misconfiguration can resurrect them. After that, remove webhooks from all 15 repositories: if the App uninstall didn't remove all webhooks, such as manually configured ones, they must be removed to prevent continued webhook delivery to the now-defunct MCP server endpoint, which could be taken over by an attacker. Finally, shut down the MCP server: this ensures webhook deliveries don't fail noisily while the server is still up, and that no in-flight requests are dropped mid-processing. The approach that deletes the source code repository and then notifies the team leaves all credentials and webhooks active. The approach that shuts down the MCP server first, archives the source code, and lets credential expiration handle token cleanup leaves active credentials that could be exploited. The approach that disables the agent's GitHub App rather than uninstalling it to preserve audit history is insufficient—a disabled App can be re-enabled and may still hold webhook subscriptions.