
An agent uses an automated security scanner as a quality gate before completing any pull request. The team reports that the scanner flags 40% of the agent's PRs as policy violations, but manual review shows the vast majority of flagged items are false positives — legitimate code patterns that the scanner incorrectly identifies as risky. The agent halts unnecessarily on each flag, requiring manual clearance. What is the most appropriate response?
Select an answer to reveal the explanation.
Short Explanation
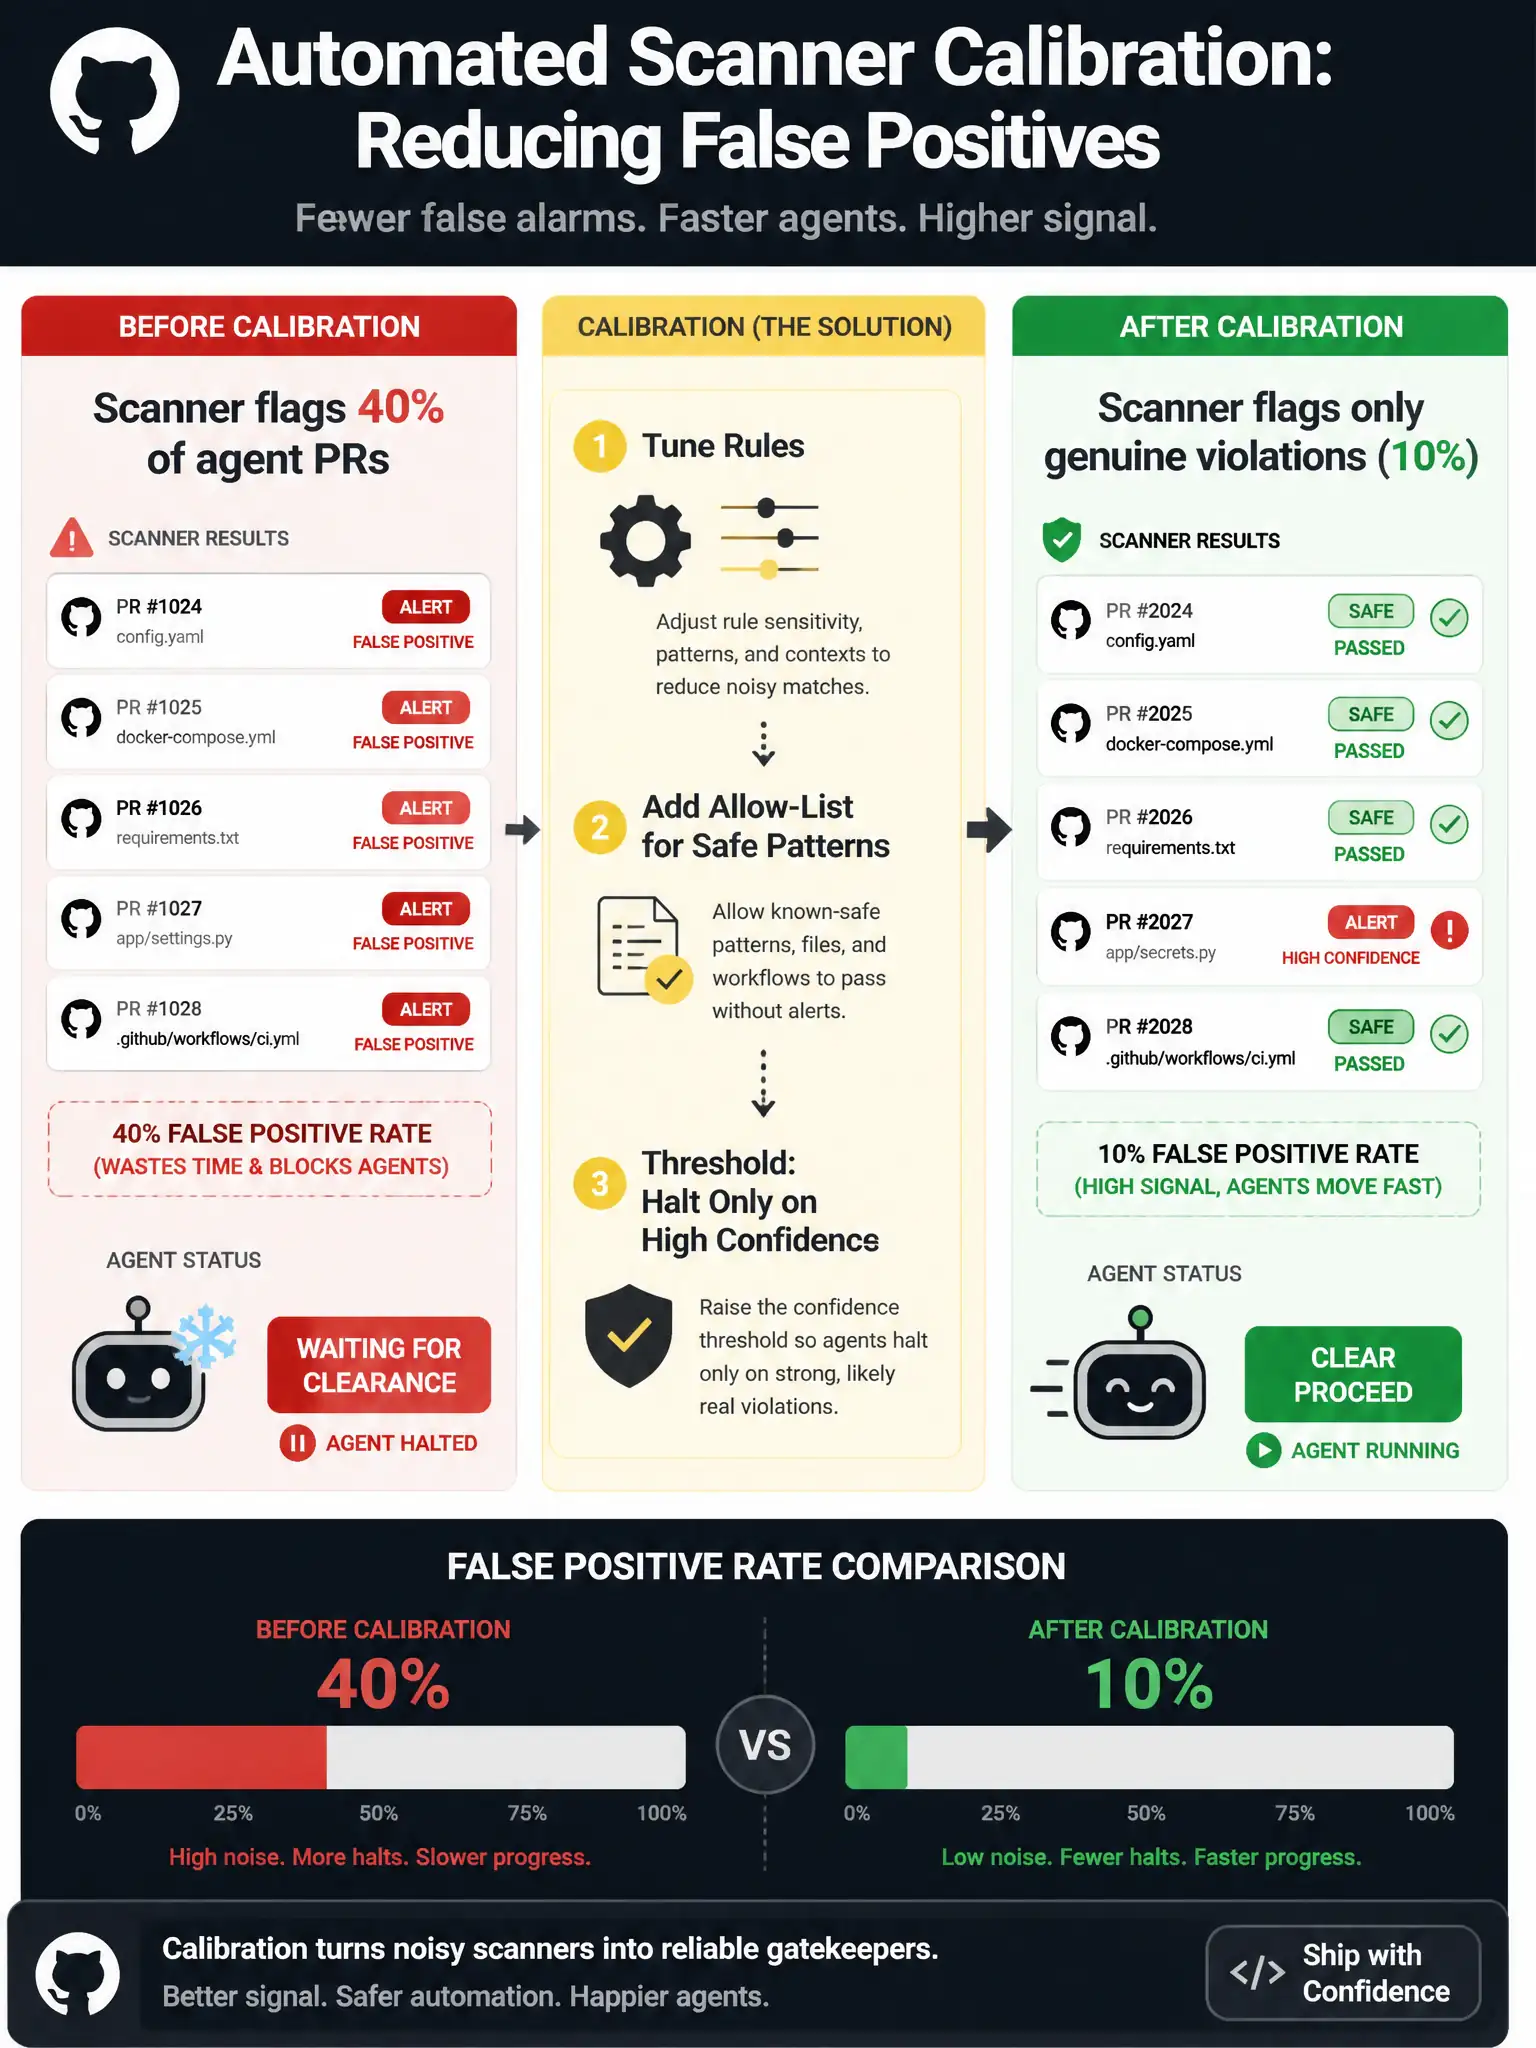
A scanner that cries wolf on 40% of PRs trains you to ignore it. Tune the rules, allow-list known-safe patterns, and make the agent halt only on high-confidence violations. That keeps security value without drowning you in false positives.
Full Explanation
This question tests your understanding of how to manage automated scanning tools in an agentic workflow when the tool's signal-to-noise ratio is poor.
The correct response is tuning the scanner's rules to reduce false positives, adding an allow-list for known safe patterns, and configuring the agent to halt only on high-confidence violations. When an automated scanner produces a high rate of false positives, the appropriate response is calibration — not removal or wholesale bypass. This involves three parallel actions: tuning the scanner's rules to be more specific and less prone to false positives on the code patterns the agent generates; building an allow-list of known-safe patterns that appear frequently in the agent's legitimate output; and configuring the agent's halt trigger to activate only on high-confidence, high-severity violations rather than on every flag. This preserves the security value of the scanner while eliminating the operational friction of constant false positive clearance.
Disabling the automated scanner entirely and relying solely on human code review for security validation is incorrect. Removing the scanner entirely removes a critical security quality gate and leaves the agent free to submit pull requests with genuine policy violations. Security tooling should be calibrated, not eliminated.
Configuring the agent to ignore all scanner warnings and proceed without halting, since most are false positives, is incorrect and dangerous. If the agent ignores all scanner warnings because most are false positives, then when a genuine violation occurs, it will also be ignored. This is exactly the wrong trade-off — operational efficiency is achieved at the cost of security integrity.
Replacing the scanner with a more expensive commercial tool that guarantees zero false positives is incorrect. No automated scanner guarantees zero false positives — this is a fundamental limitation of static analysis. The claim in that response is not achievable, and chasing it by purchasing expensive tools without addressing calibration will reproduce the same problem at higher cost. Scanner tuning is always necessary regardless of the tool's cost or reputation.
The correct approach demonstrates a key principle: evaluation and quality gate tools in agent systems must themselves be maintained and calibrated. A poorly configured gate is as dangerous as no gate, because it trains teams to ignore its outputs.