
A team wants their Copilot agent to autonomously implement small bug fixes: create a branch, commit the fix, and open a pull request without any human steps. Which two GitHub token permissions are minimally required for the agent to complete this workflow?
Select an answer to reveal the explanation.
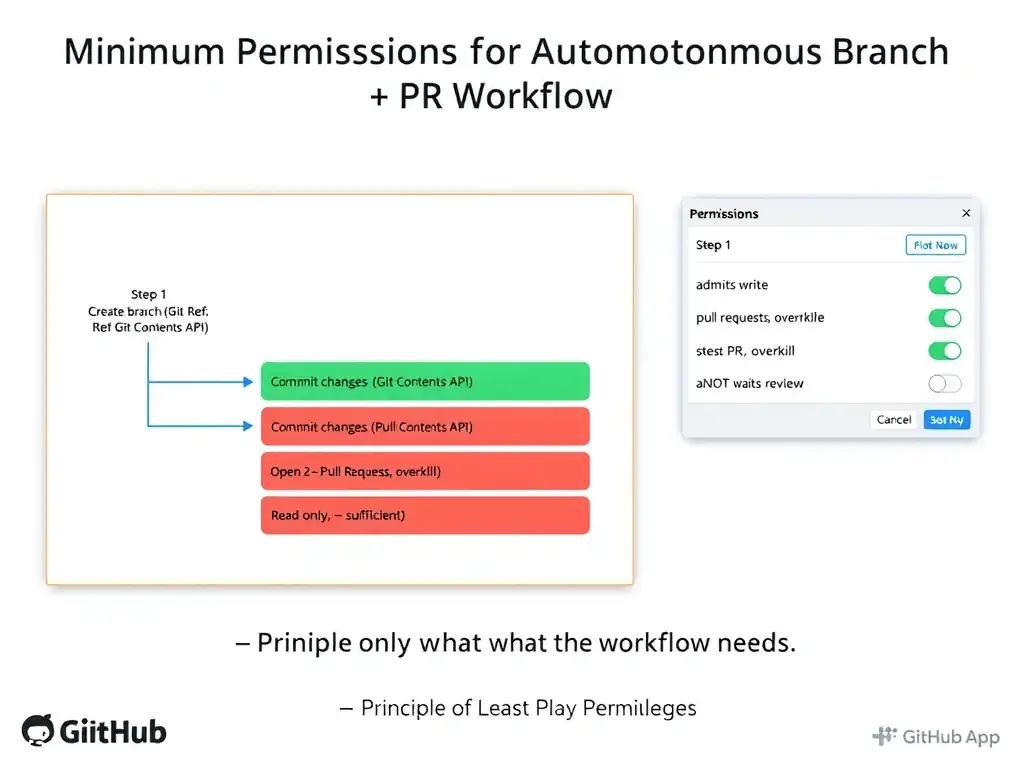
Short Explanation
Autonomous branch-create-commit-PR is a two-permission job: write to contents lets you create a branch and push commits, and write to pull-requests lets you open the PR. Read-only access won't let you modify anything, and admin access is overkill and dangerous. Think of it as giving someone a pen and a mailbox key, not the master key to the whole building.
Full Explanation
When a Copilot agent needs to autonomously create a branch, commit changes, and open a pull request, it must interact with two GitHub API resource categories. First, write access to contents is required because the Git Contents API is used to create and update files in a repository, and creating a branch is a ref operation under the Git Refs API, which falls within the contents scope. The agent needs write access to create the branch ref and to push commits, including creating or updating blobs and trees. Second, write access to pull-requests is required because opening a pull request requires calling the Pull Requests API, specifically POST /repos/{owner}/{repo}/pulls. Without write access to that scope, the API call returns a 403 Forbidden error. These two write permissions represent the minimum viable set for this workflow. The read-only combination is incorrect because read-only access to contents and pull-requests allows the agent to list files and list pull requests, but not to create or modify either. The agent would be able to inspect the repository but could not create a branch, commit code, or open a pull request. The admin-access approach is incorrect because admin access is far more than what is needed and introduces significant security risk. Admin access includes capabilities like deleting the repository, modifying branch protection rules, and managing webhooks, none of which are required for this workflow. The principle of least privilege is a core security best practice for agent permissions. The actions-and-checks approach is incorrect because actions write access, used to trigger workflow runs, and checks write access, used to create check runs and test annotations, are unrelated to the branch-create-commit-PR workflow. Those permissions would be needed for separate CI orchestration scenarios, not for the basic autonomous commit and pull request flow. The correct permission set is contents write plus pull-requests write, which is the minimal, least-privilege permission set for this autonomous workflow.