
During an incident where a GitHub App's private key or high-privilege credentials may be leaked, what should administrators do first?
Select an answer to reveal the explanation.
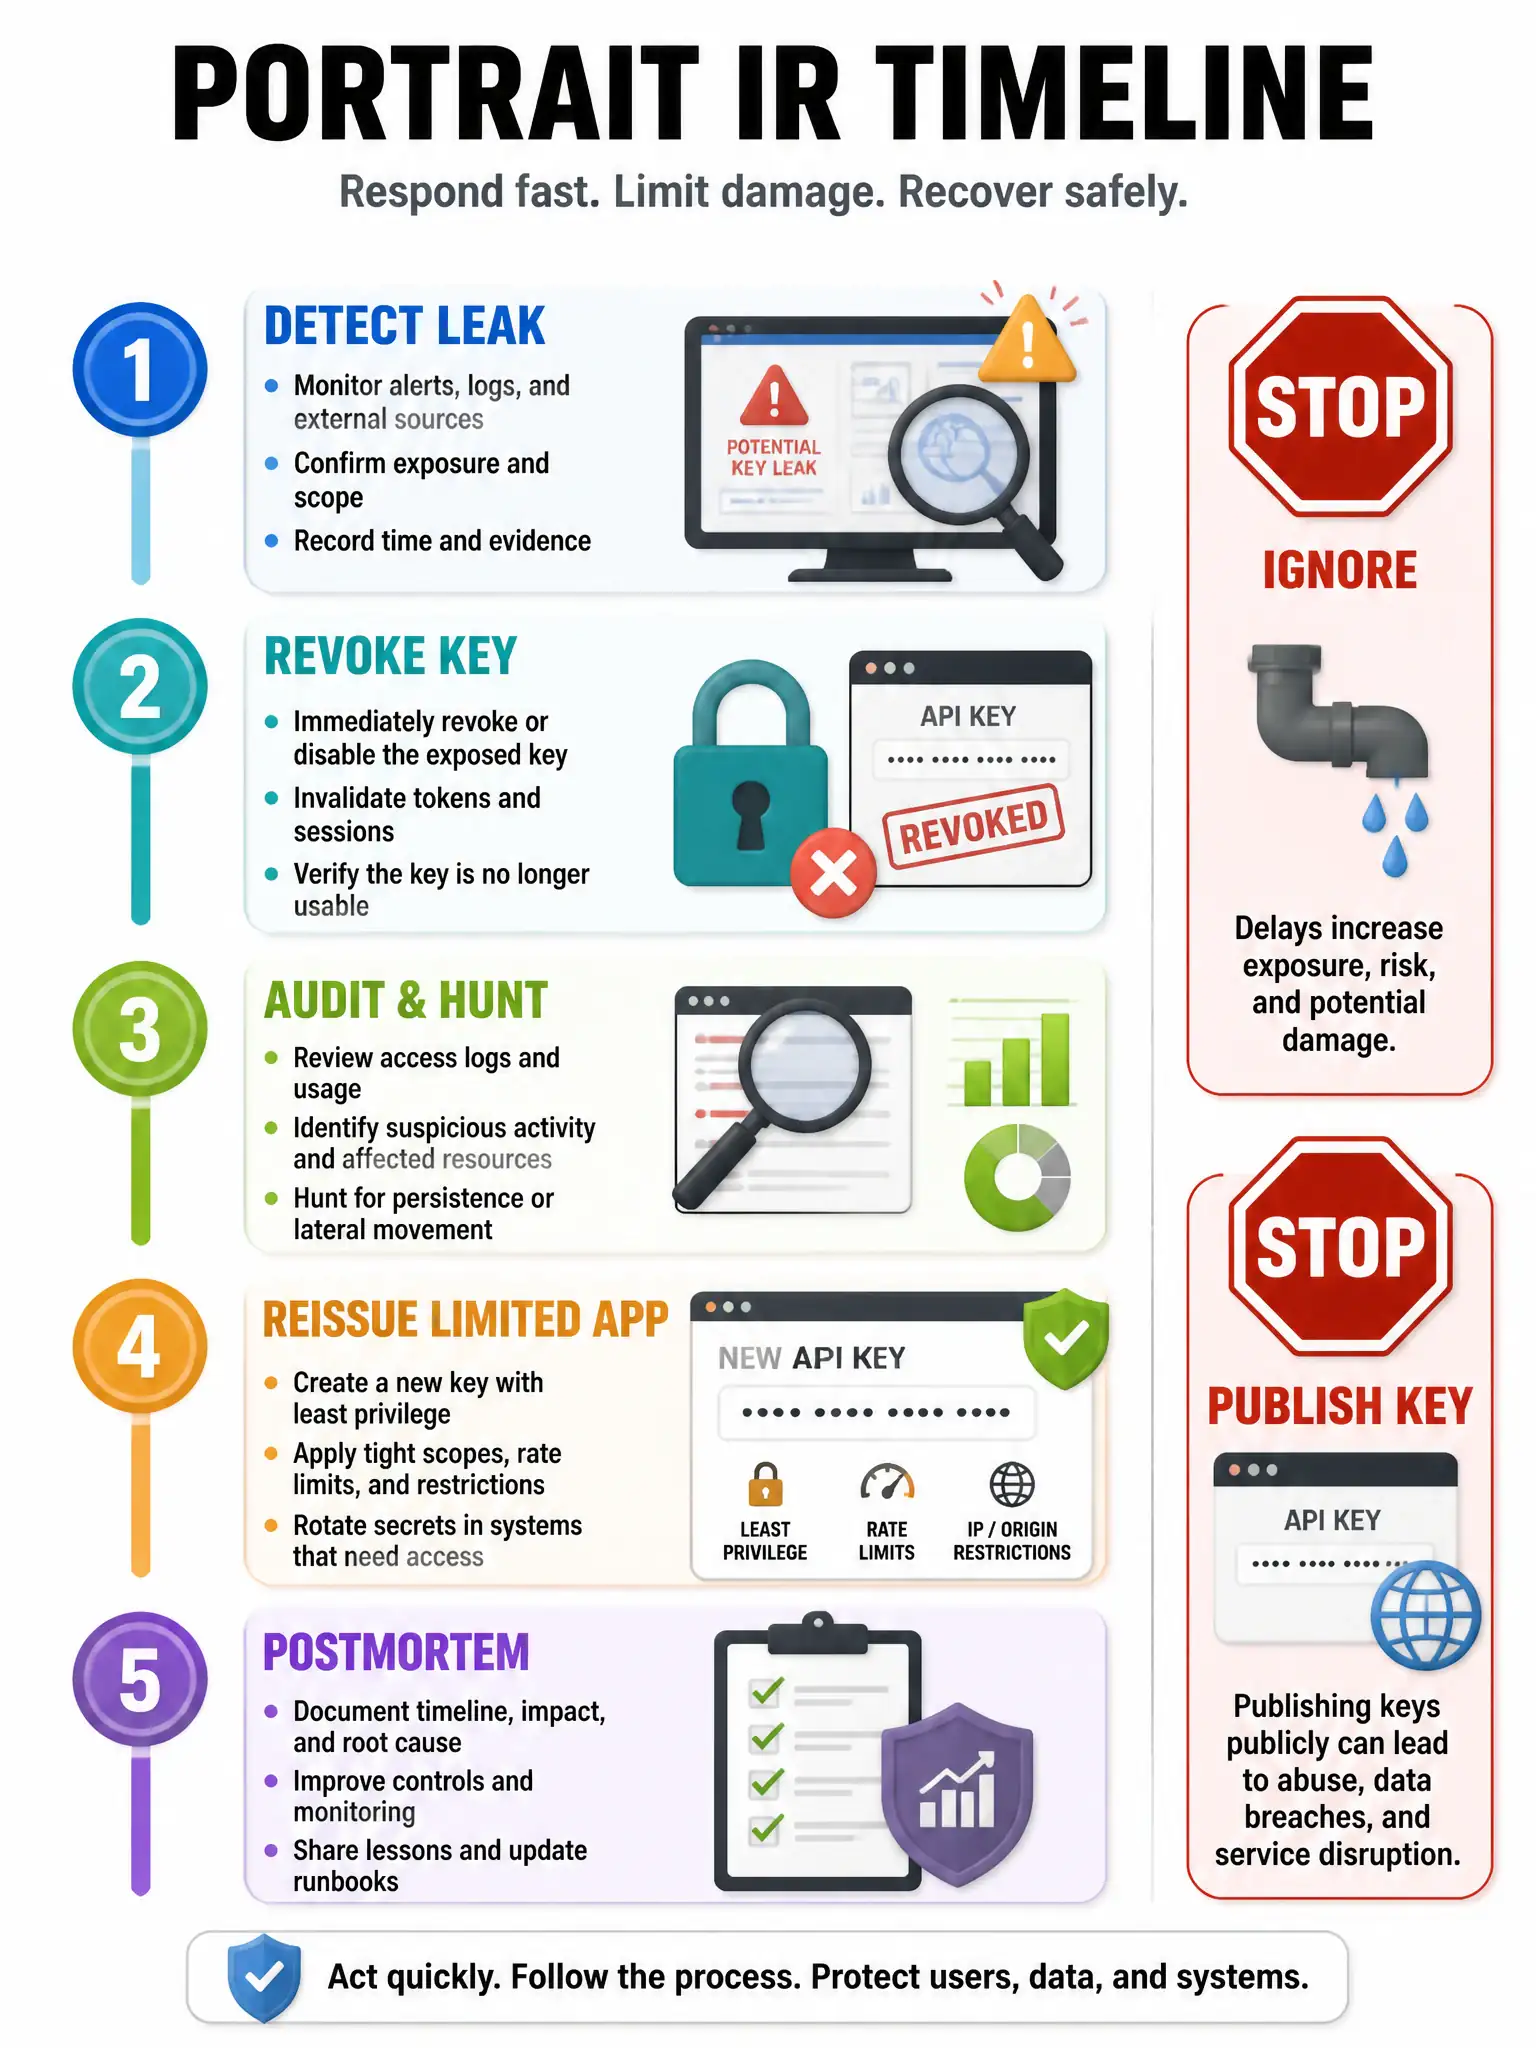
Short Explanation
If a GitHub App private key or high-privilege credential may be leaked, you revoke or rotate it immediately, then hunt through audit and app activity for abuse. After that, you reissue access with least privilege so the incident doesn't turn into a bigger breach.
Full Explanation
The correct response is to revoke or rotate the compromised credentials, review audit logs for abuse, and reissue access with least privilege. Incident response for GitHub credentials prioritizes containment, then investigation and recovery. Ignoring the leak because no public blog post exists, posting the private key for crowdsourced analysis, or celebrating it as chaos engineering are all irresponsible. Follow enterprise IR runbooks, notify affected repo owners, enable additional detections, and consider short-lived credentials and IP allow lists to reduce future impact. Capture a timeline of when the key was generated, last rotated, and first suspected exposure so you can bound the abuse window in audit evidence for leadership and customers.