
Which two GitHub artifacts commonly support external compliance audits? (Choose two)
Select all correct answers, then click Submit.
Short Explanation
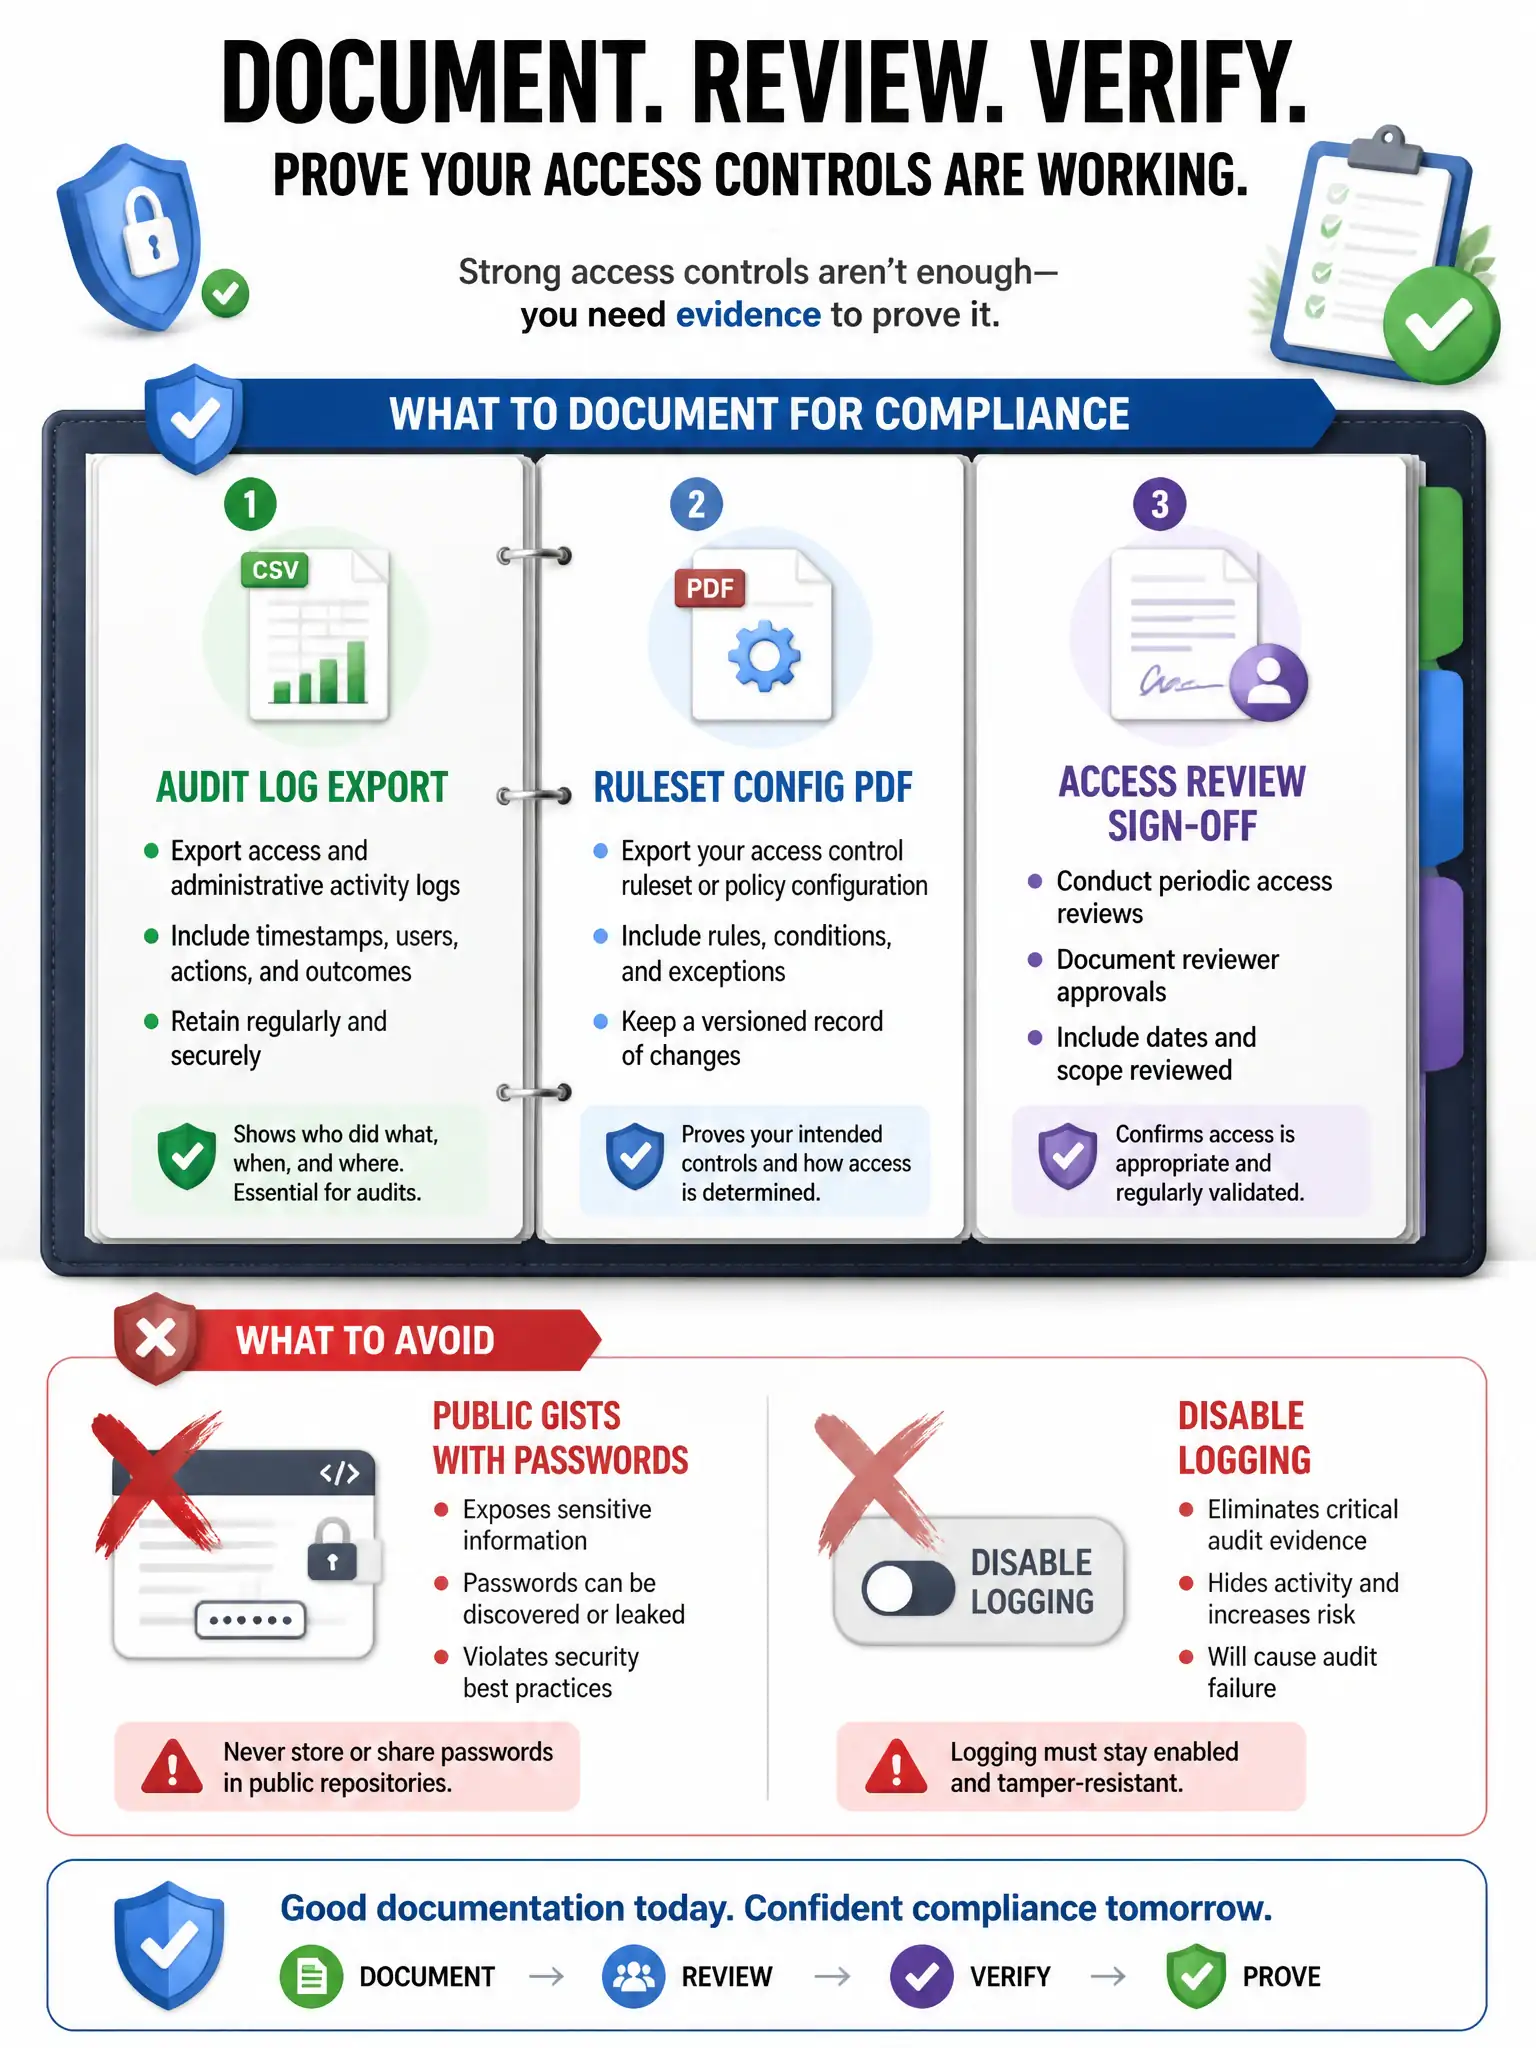
Auditors want proof your controls exist and worked, so audit logs and repository ruleset and protection configurations are the evidence you need. Public gists with production passwords are findings, not evidence. Never disable logging to save storage before an audit.
Full Explanation
Audit logs showing administrative and security-relevant events and repository ruleset and protection configurations demonstrating control design are correct because they provide evidence that controls exist and operated. Audit logs show who changed what, while documented protection and ruleset configurations show branch and tag policies exist. Untracked production passwords stored in a public gist are a control failure, not audit evidence. Disabling all logging to reduce storage destroys evidence and undermines operating-effectiveness testing. Map GitHub controls to frameworks such as SOX, ISO, and FedRAMP customer responsibilities, retain exports per policy, and screenshot or export settings baselines. Streaming audit events to immutable storage strengthens operating-effectiveness evidence when auditors ask whether controls ran continuously, not only on the day of sampling.