
What is a primary benefit of configuring audit log streaming to an external destination?
Select an answer to reveal the explanation.
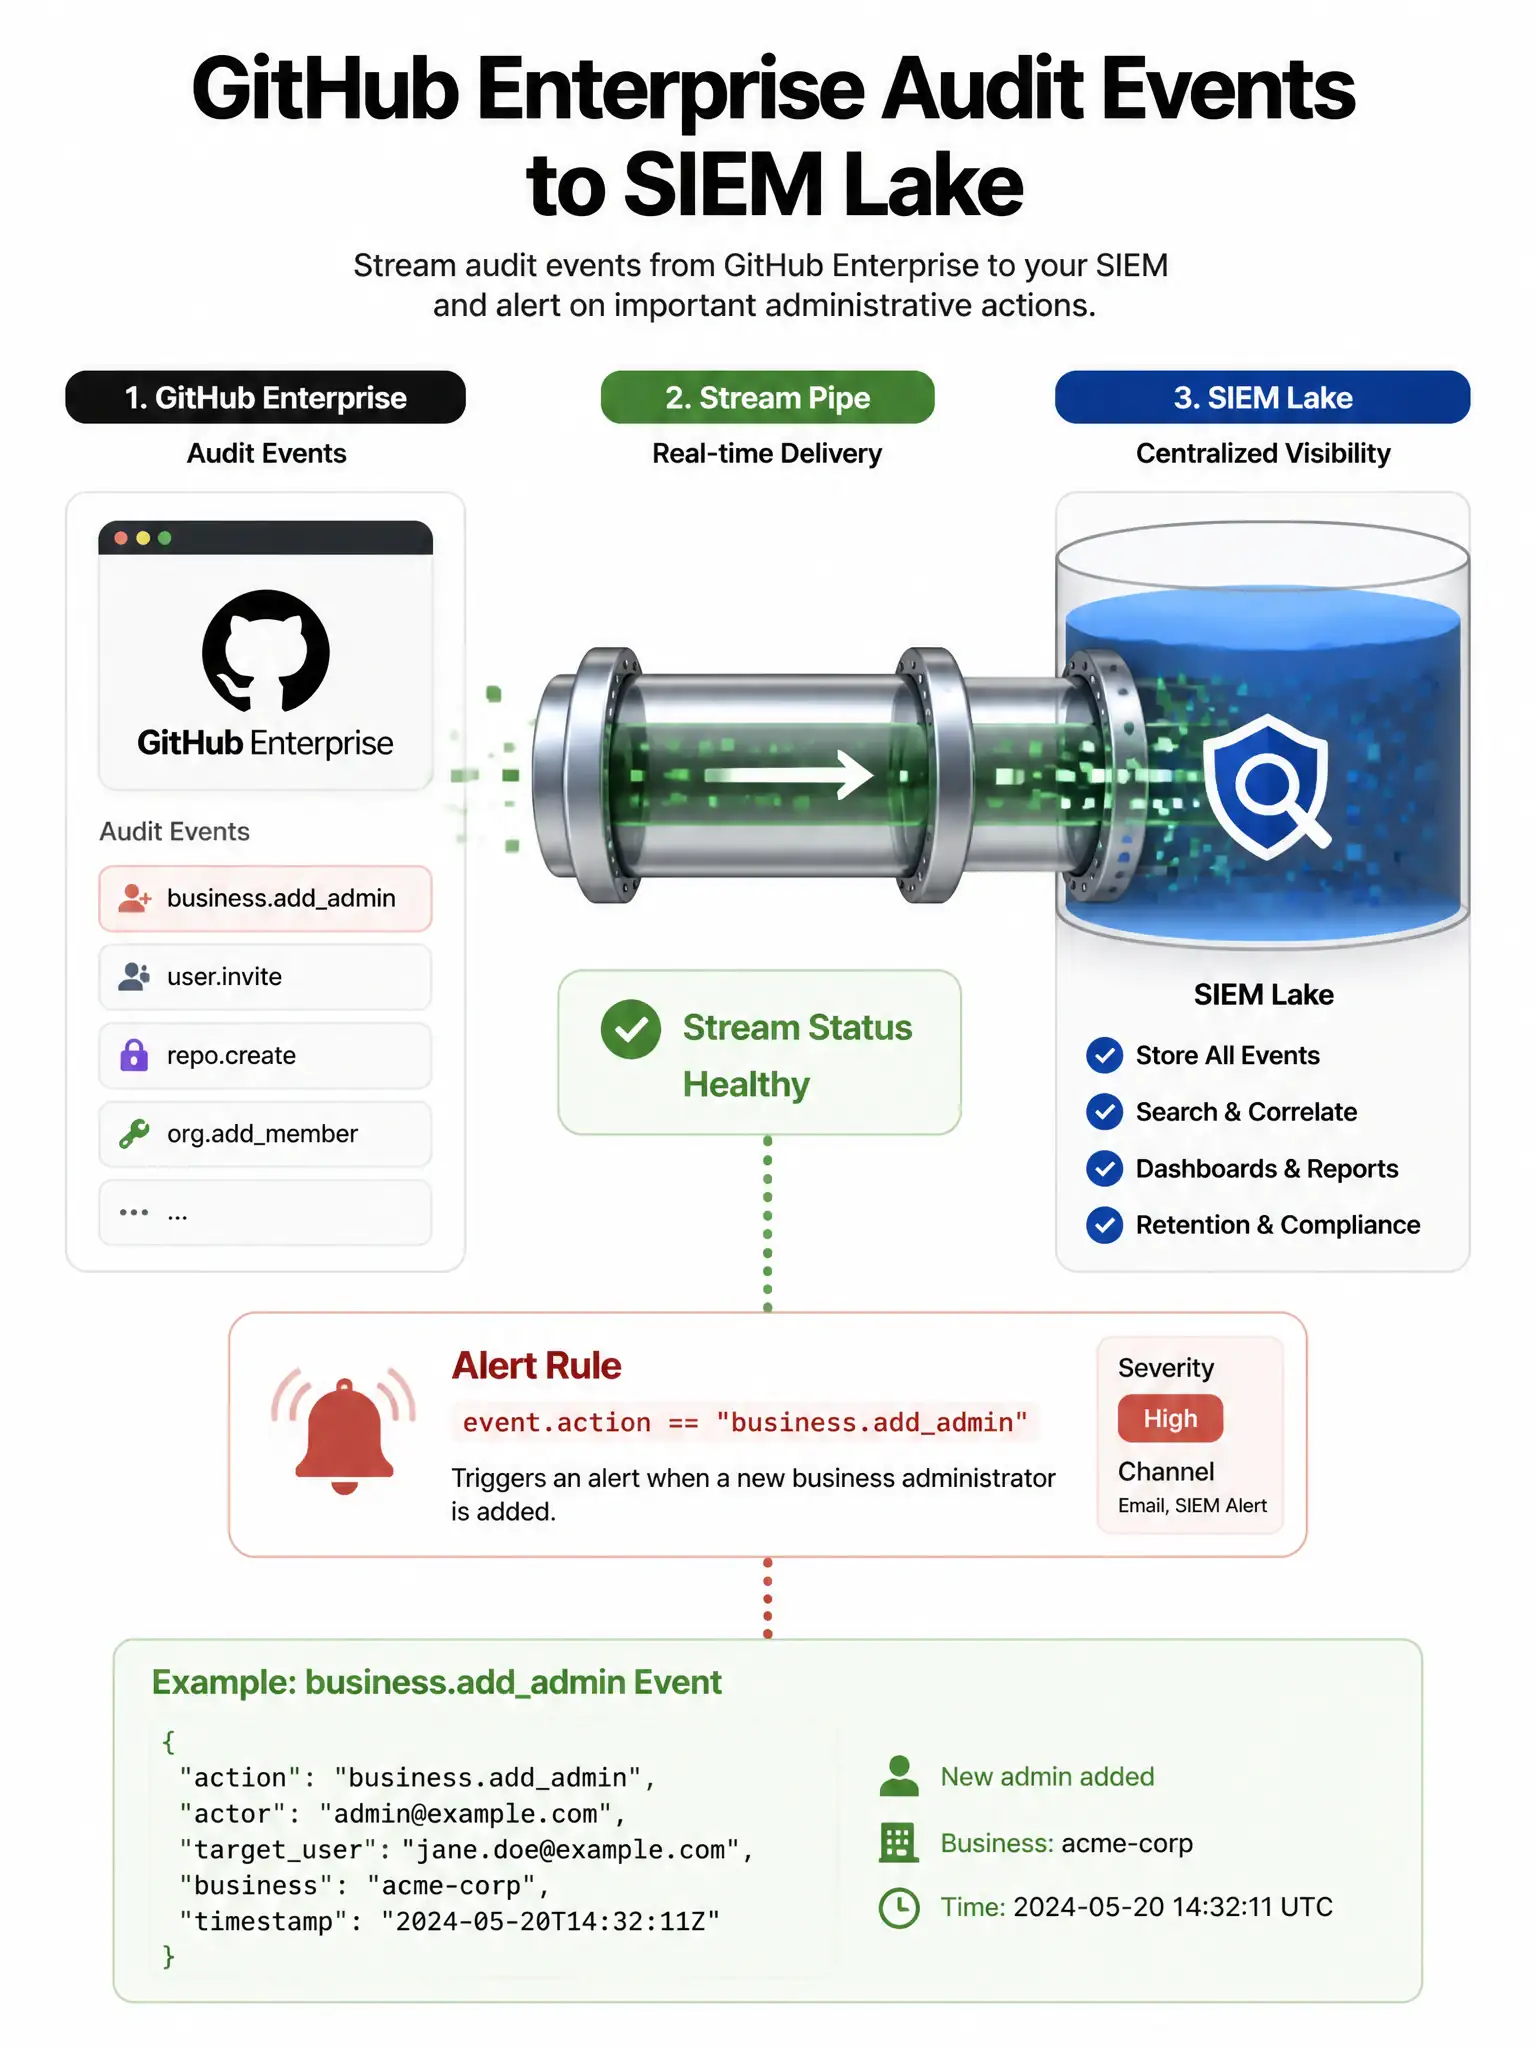
Short Explanation
Streaming pushes audit events to your SIEM or storage system as they happen, so SOC can alert and you keep evidence beyond GitHub's UI retention window. Wire it to Azure/AWS/Splunk/etc., monitor stream health, and don't treat streaming as a way to erase evidence or elevate privileges.
Full Explanation
The correct answer is near real-time delivery of audit events to SIEM/storage for detection and longer retention. Audit log streaming complements in-product audit search with enterprise SOC workflows. It avoids leaving logs only in GitHub's UI retention window. Wire it to Azure/AWS/Splunk/etc. and monitor stream health. Automatically deleting all audit events older than five minutes undermines compliance. Disabling MFA for enterprise owners is false. Granting every user enterprise owner through the stream is false. Validate destination credentials, encrypt in transit, alert on stream failures, and map critical events (org policy changes, permission grants, repo visibility) to detections. Streaming does not replace access reviews or break-glass procedures, but it is how mature enterprises keep GitHub administrative activity inside their detection stack beyond native retention limits.