
When should an administrator store a value as an Actions secret rather than a configuration variable?
Select an answer to reveal the explanation.
Short Explanation
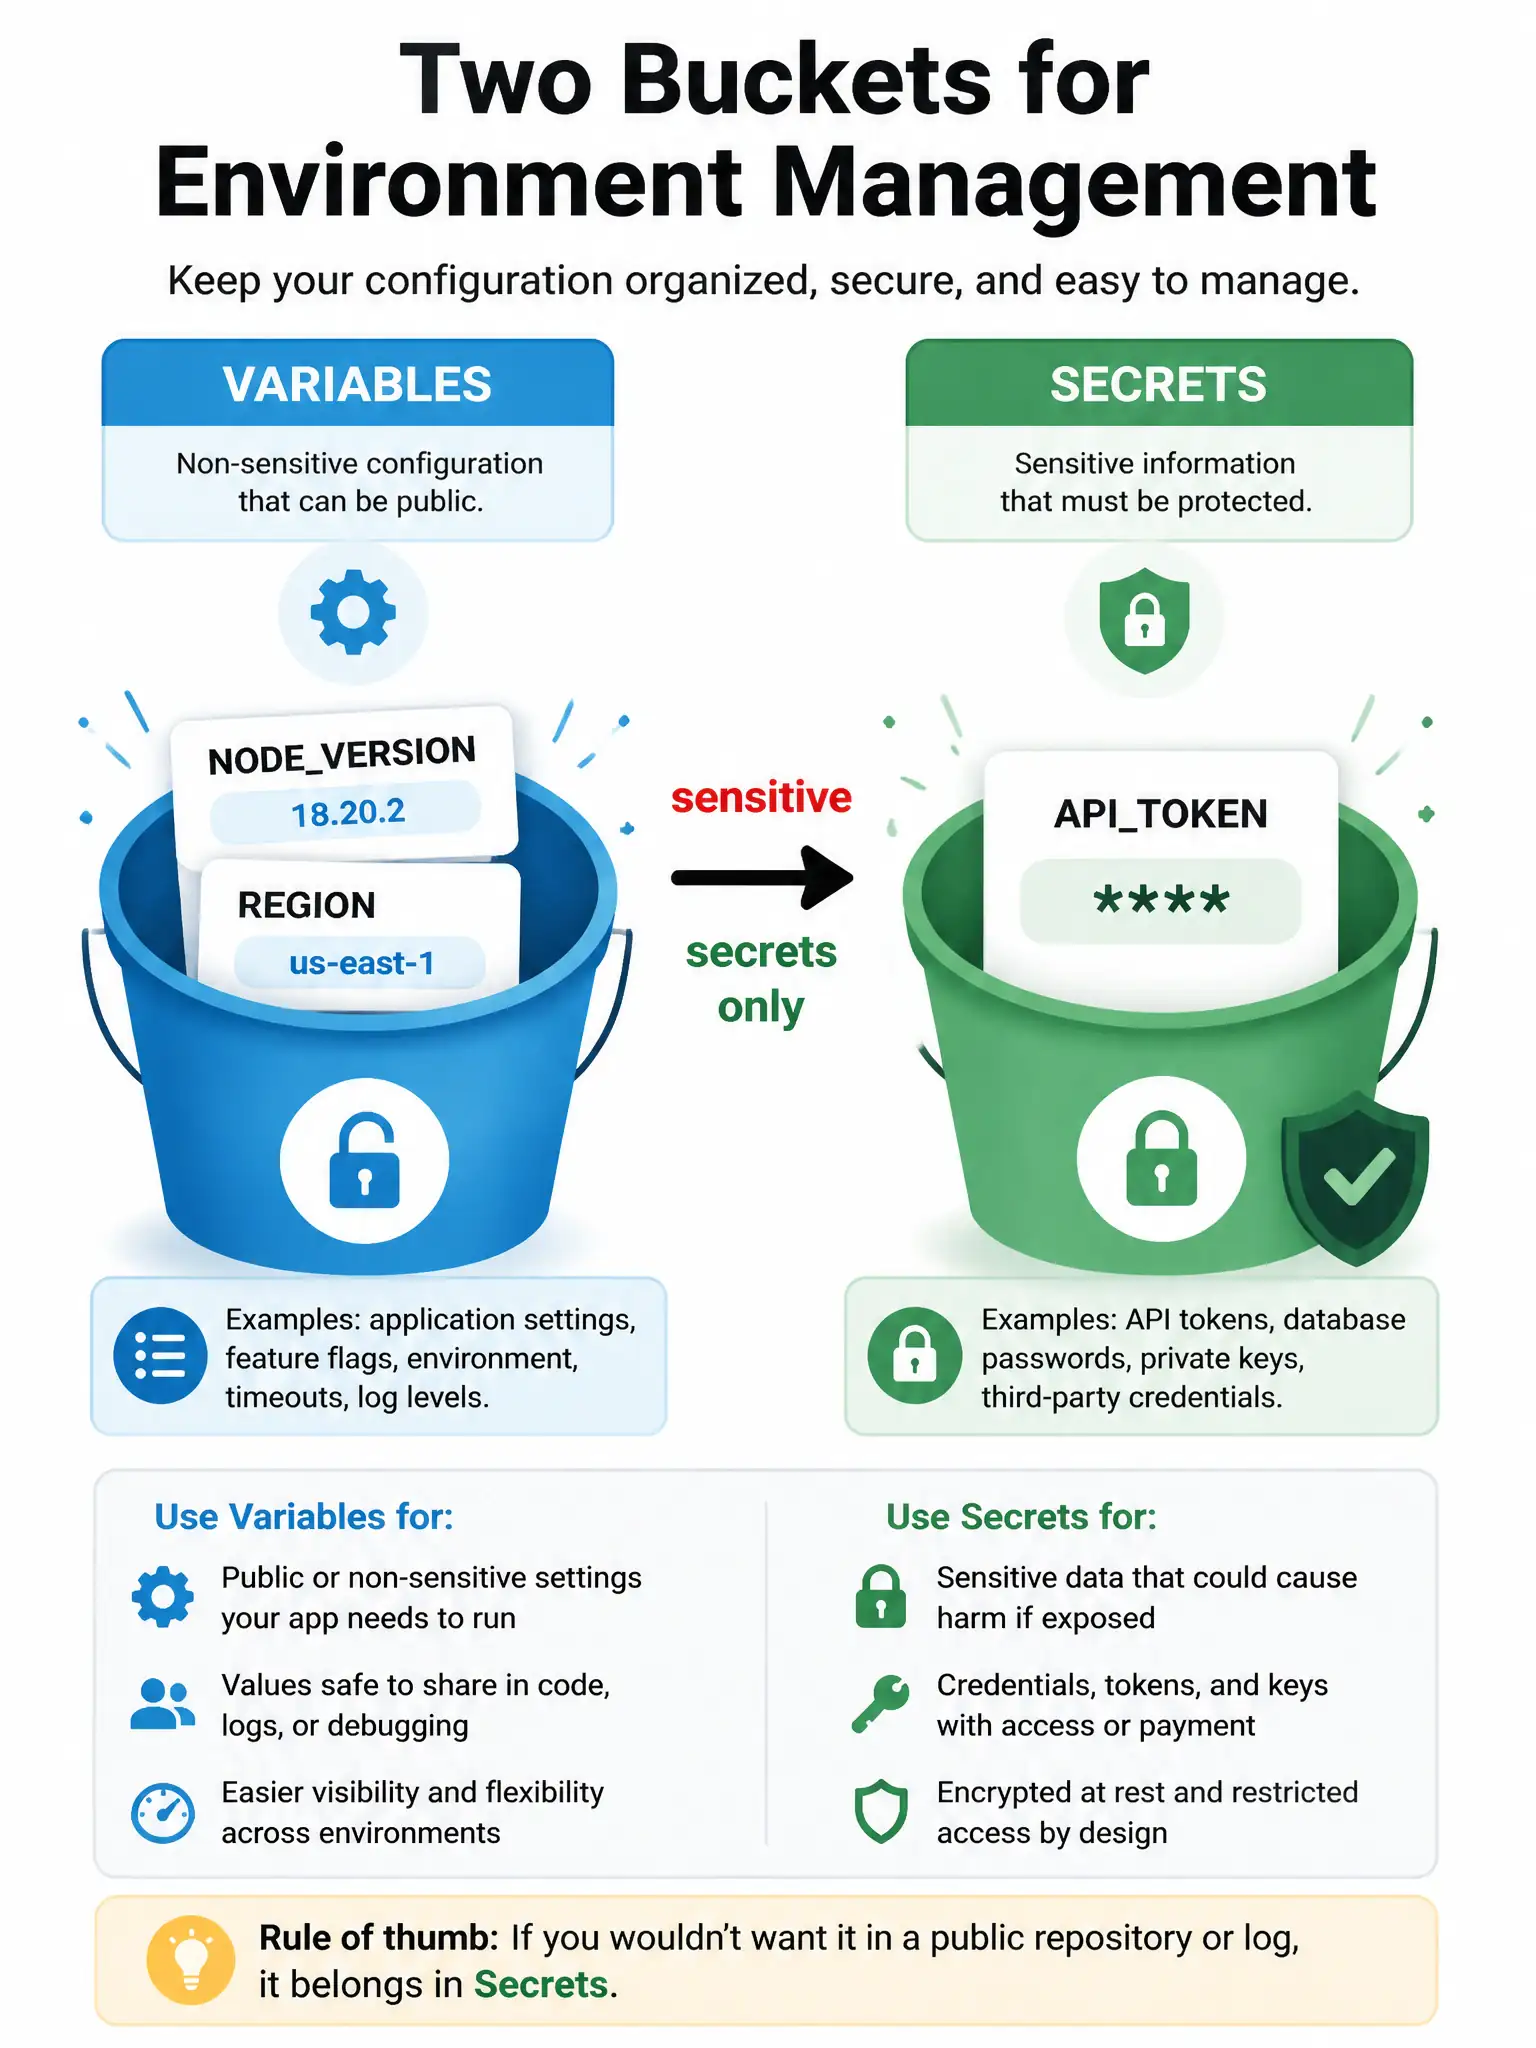
Secrets are for sensitive stuff — tokens, passwords, private keys — while variables are for boring config like NODE_VERSION=20. Don't put credentials in variables 'because it is easier,' and don't print secrets to logs. Org/env scoping still applies to both.
Full Explanation
The correct answer is storing credentials and sensitive material as secrets. Secrets are encrypted at rest, masked in logs when properly referenced, and permissioned differently than plain configuration variables. The non-sensitive default region name used only for display should be a configuration variable because region names are not credentials. The value that must appear in plaintext in pull request logs for convenience is insecure because plaintext logs defeat the purpose of secrets. The public repository description is public metadata, not a secret. Use environment secrets for production, rotate regularly, limit who can read secret values in settings, and prefer OIDC over long-lived cloud secrets when possible.