
Which two statements correctly describe GitHub artifact attestations in Actions workflows? (Choose two)
Select all correct answers, then click Submit.
Short Explanation
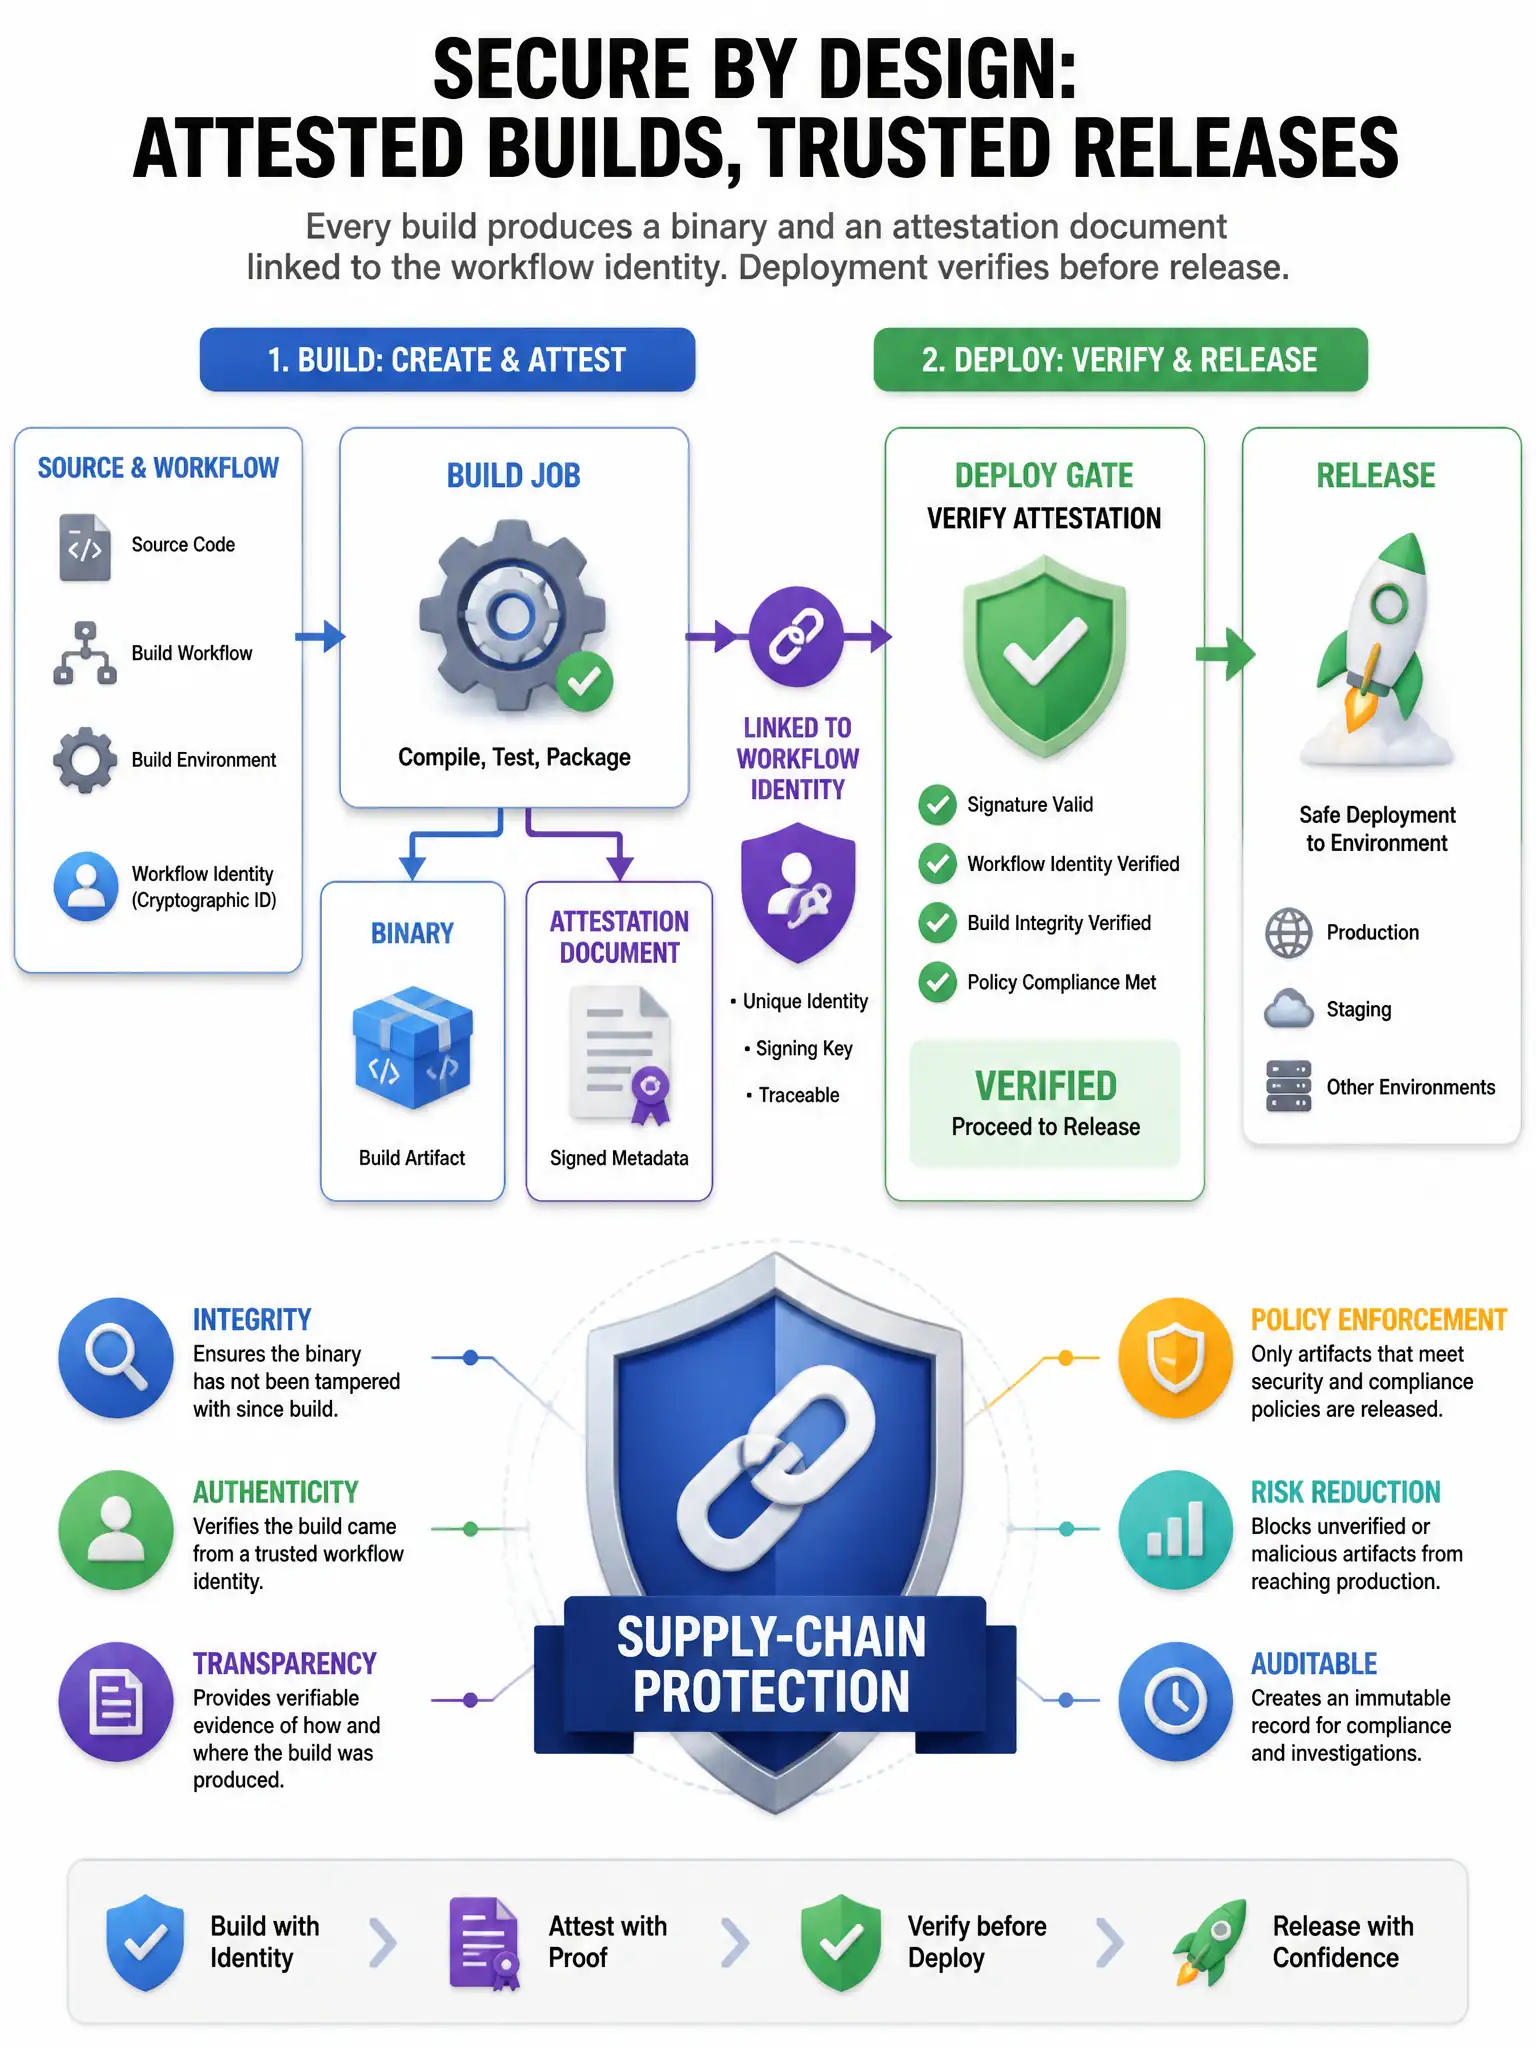
Attestations prove how your build artifact was produced — provenance for supply-chain security. They don't replace IAM or stop forks. Use them with signing and verification policies so prod only accepts builds from trusted workflows.
Full Explanation
The correct statements are that they help produce verifiable provenance metadata about how an artifact was built and that they support supply-chain integrity workflows by binding artifacts to build claims. Artifact attestations complement SBOMs and signing strategies by recording how and where a binary was produced in GitHub Actions. The statement that they replace the need for any repository access controls is false; access control remains mandatory and attestations do not replace IAM. The statement that they permanently prevent all forks of public repositories is false; attestations do not ban forks. Administrators should standardize attestation generation in reusable workflows, pin trusted builders, and enforce verification at deployment gates so production only accepts artifacts with expected provenance.