
What can push rulesets help prevent at the repository or organization level?
Select an answer to reveal the explanation.
Short Explanation
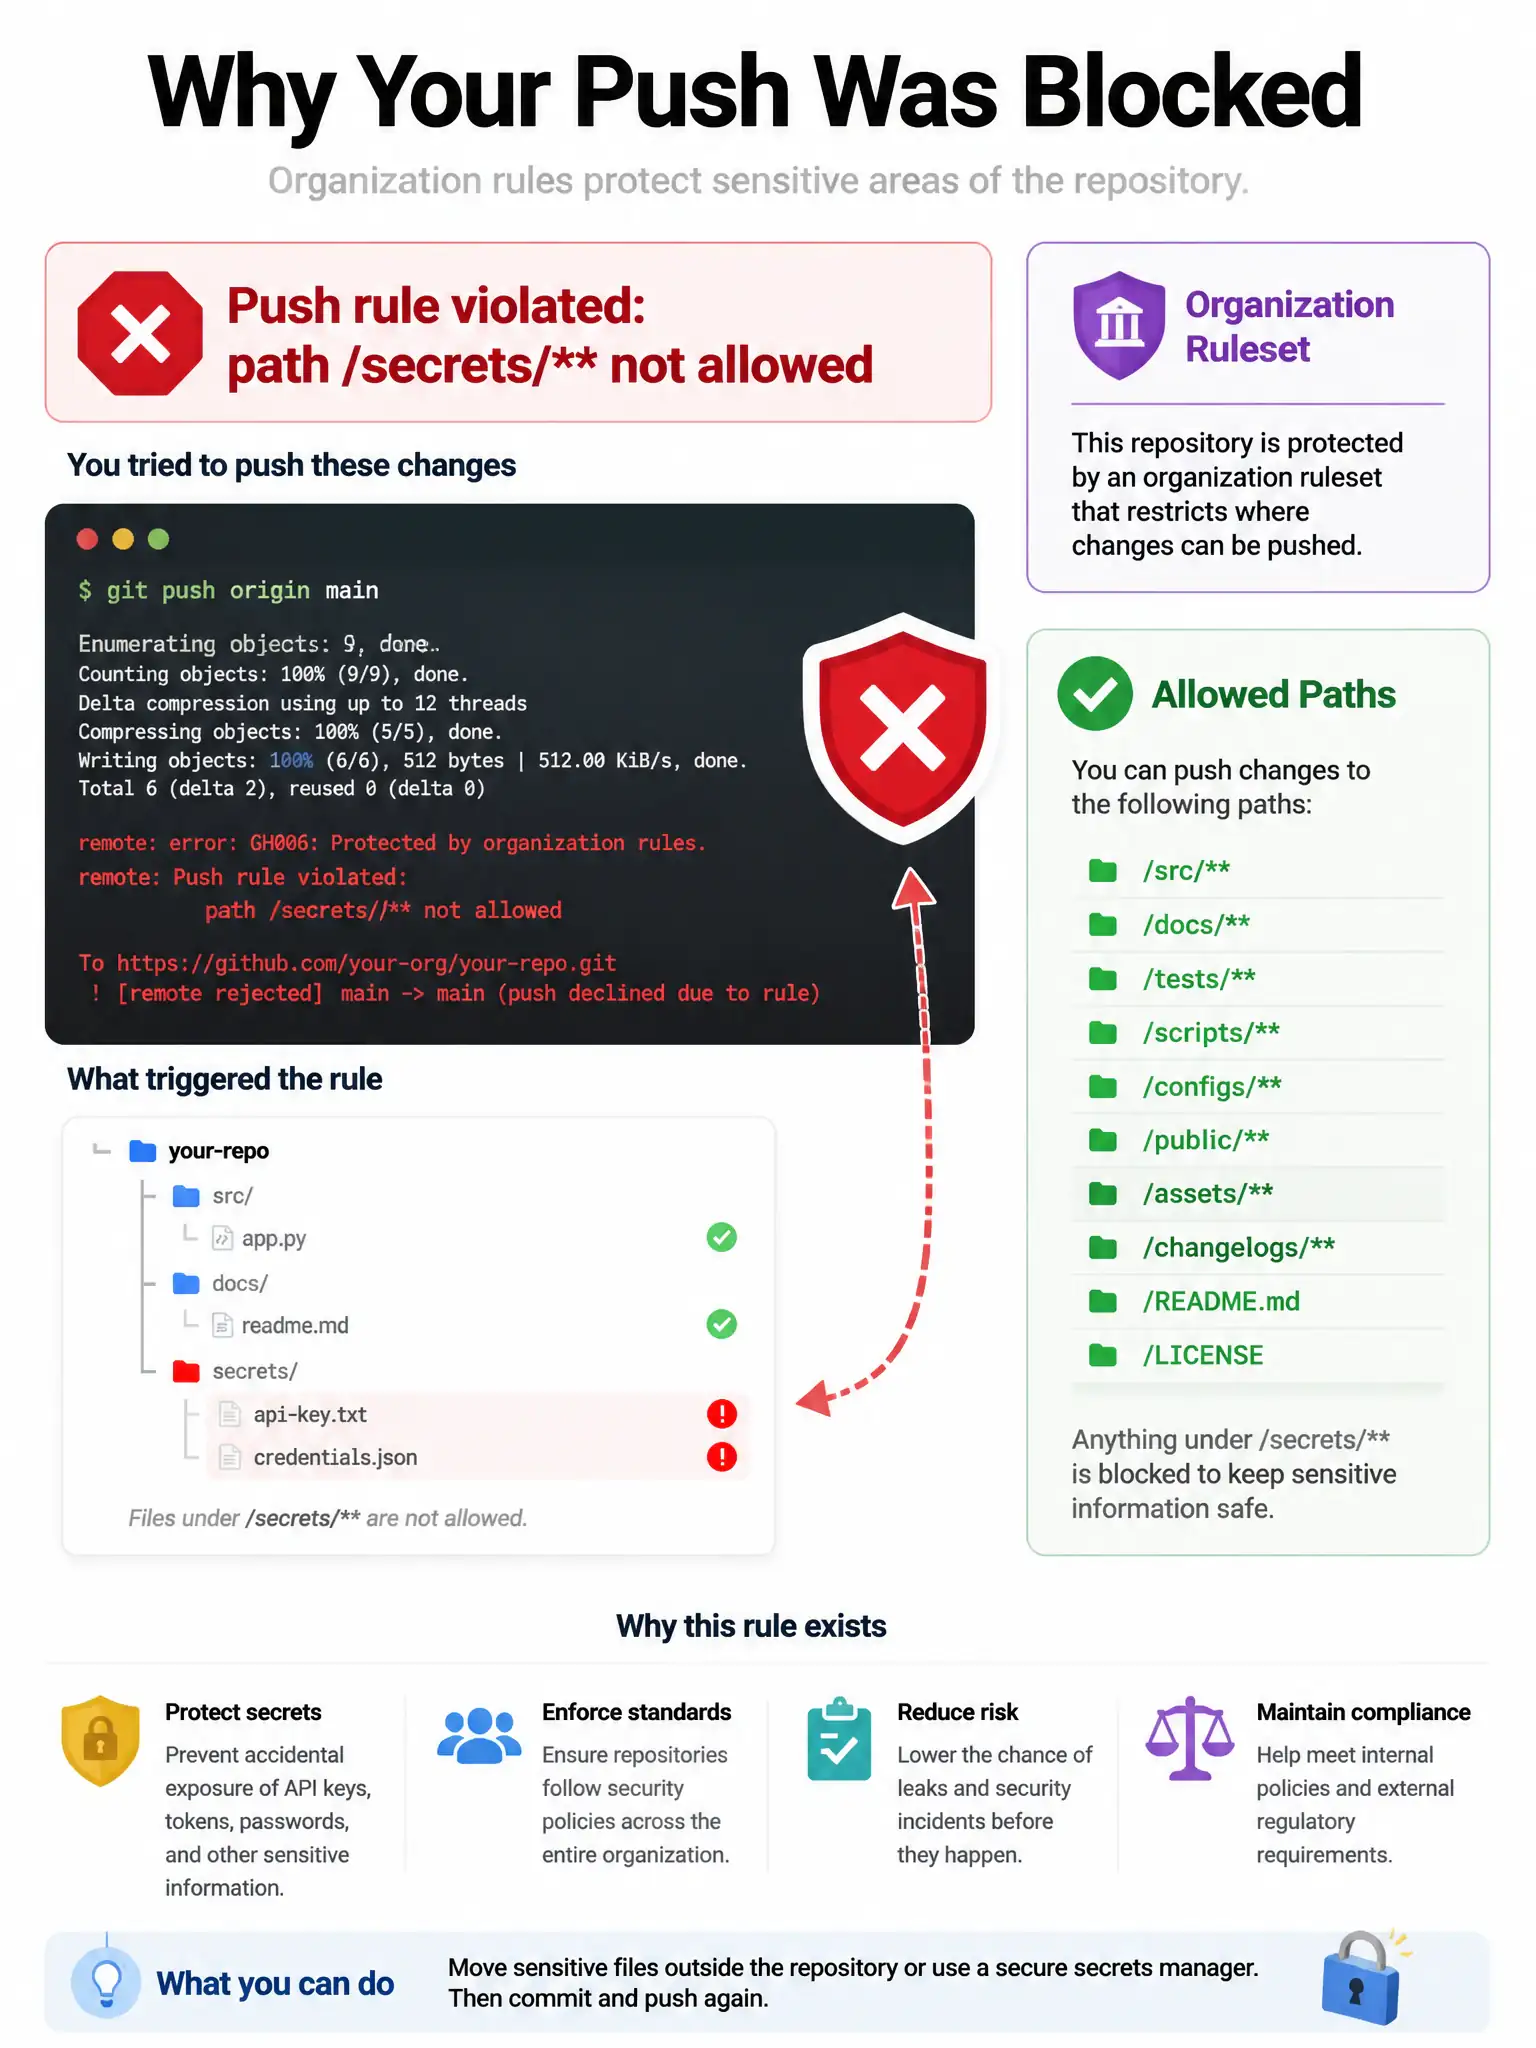
You use push rulesets to put guardrails on what lands in Git—paths, file sizes, file extensions, and other push-time constraints depending on configuration—before bad content becomes history everyone clones. They’re about push compliance, not banning people from reading docs or filing issues.
Full Explanation
The correct answer is preventing unauthorized or non-compliant pushes, such as changes that violate configured push constraints. Push rulesets extend policy beyond classic 'who can push to main' into content-oriented or push-time controls useful for enterprises, for example restricting sensitive paths or file types when configured. The option about blocking all reading of public documentation websites is unrelated. The option about preventing creation of GitHub Issues exclusively is wrong; issues are a different permission surface. The option about blocking billing manager invitations only is unrelated to push policy. Combine push rulesets with CODEOWNERS, required reviews, and secret push protection for defense in depth.