
Which two uses of repository custom properties are valuable for enterprise administrators? (Choose two)
Select all correct answers, then click Submit.
Short Explanation
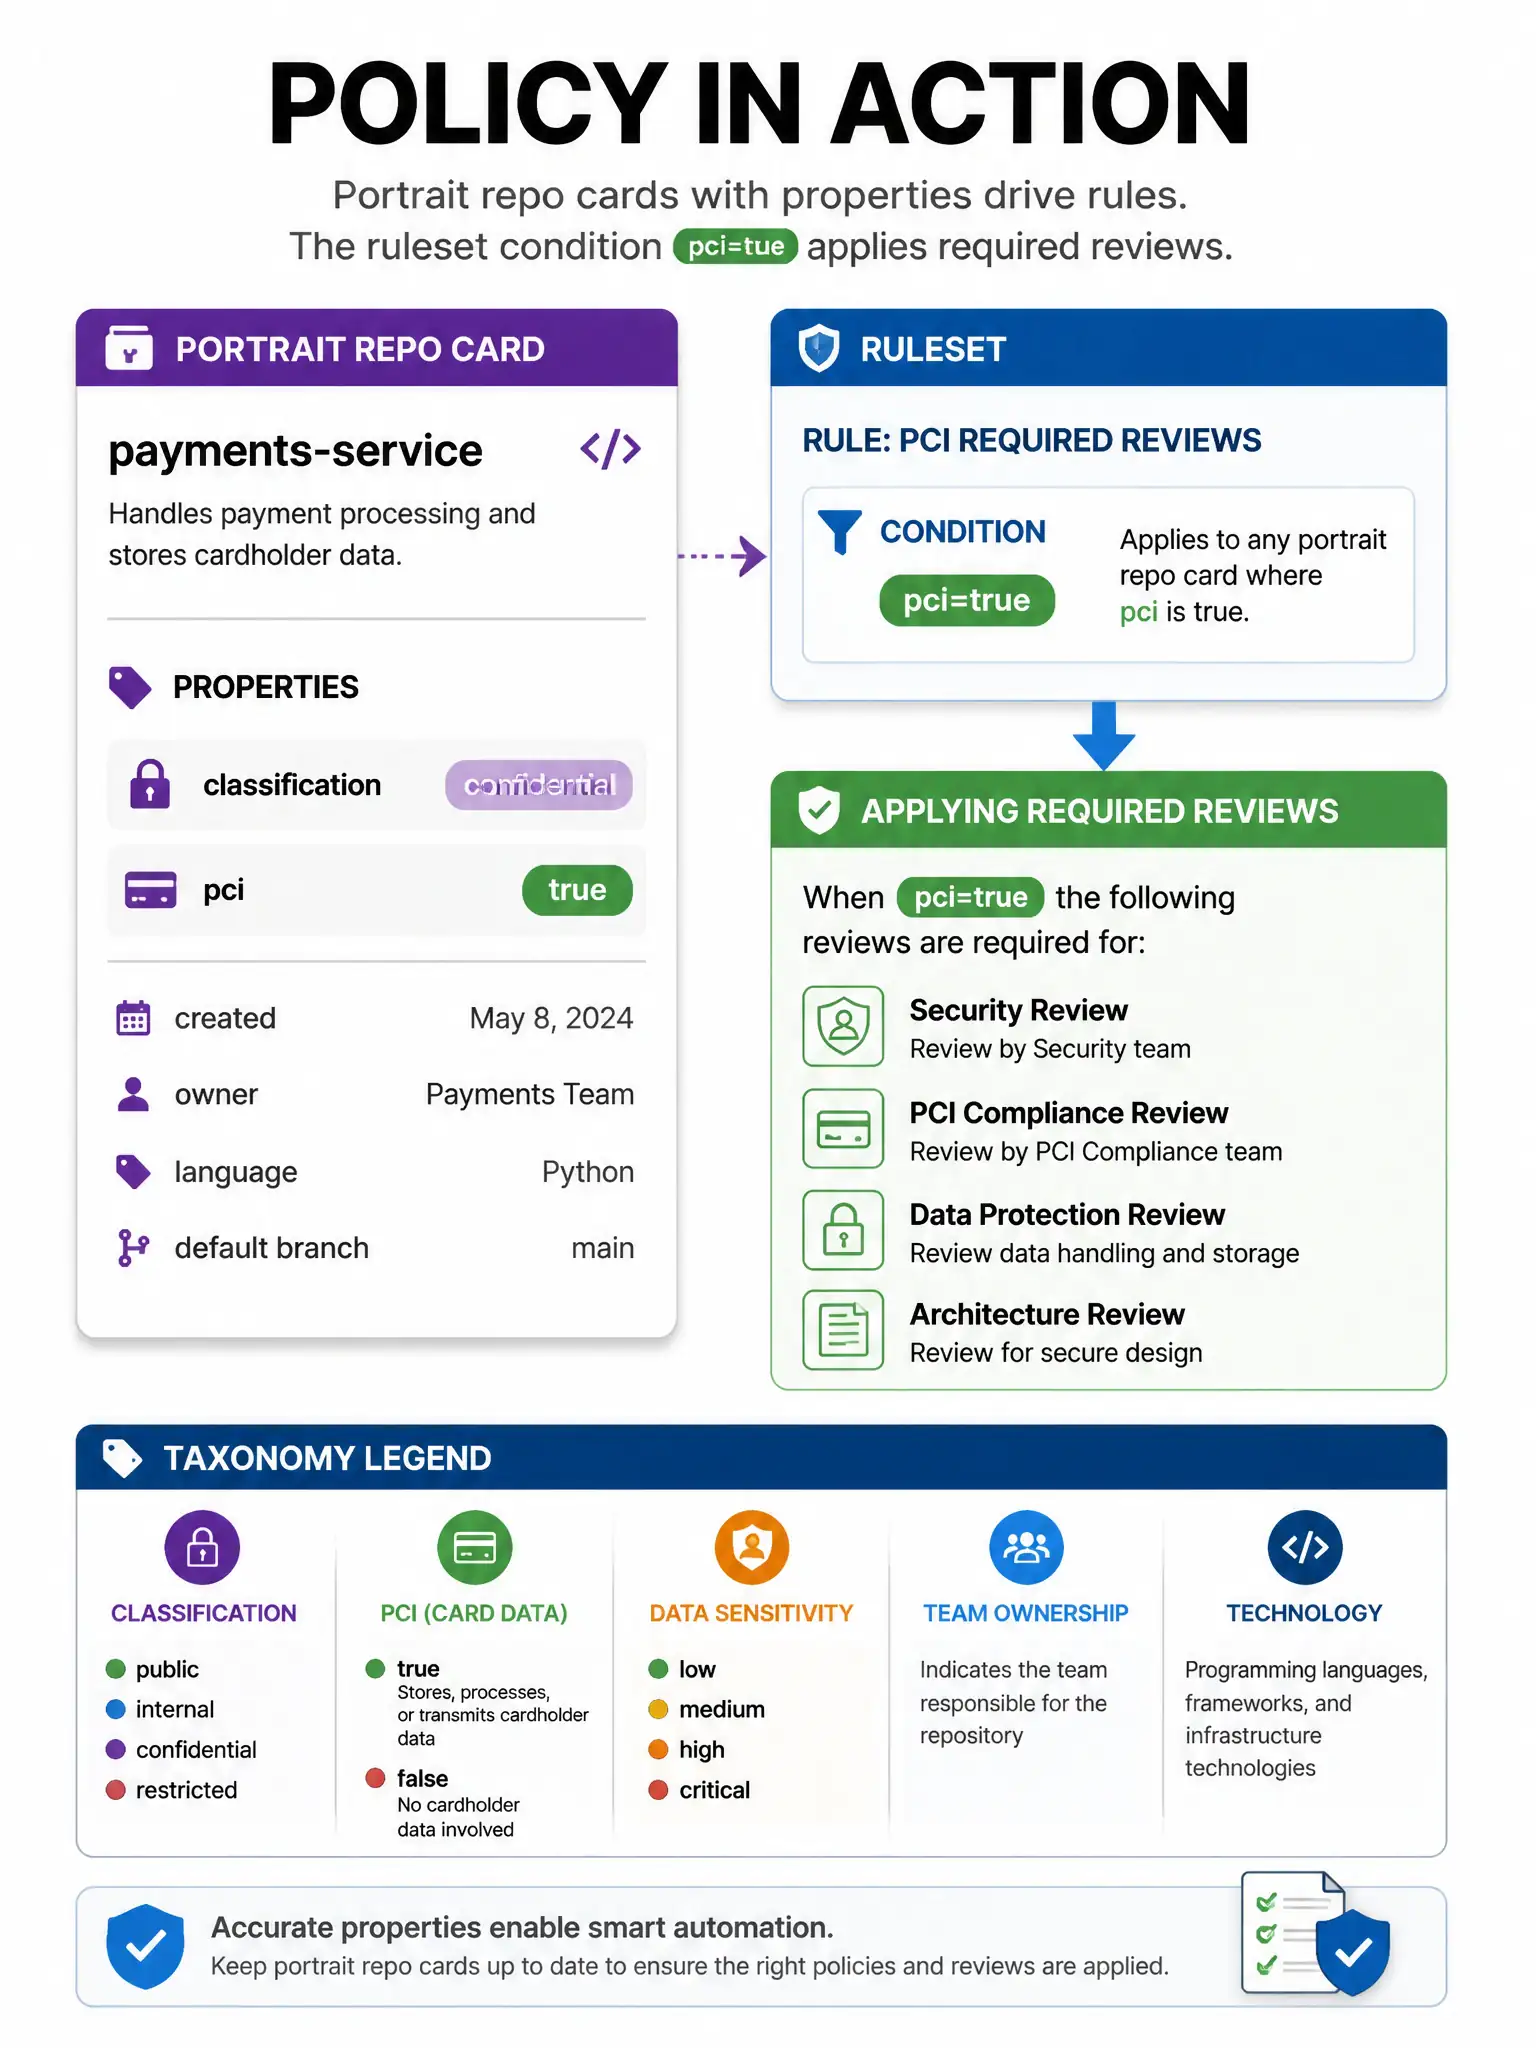
Custom properties are structured labels on repos — think compliance tier or criticality=high — so you can find them and aim rulesets at the right population. They don't rewrite Git objects or turn off HTTPS per repo. Get a property taxonomy agreed with security/compliance before you invent fifty free-text fields nobody maintains.
Full Explanation
The correct uses are metadata tagging with compliance tier or data classification, and organization ruleset targeting by property values. Custom properties provide governed metadata on repositories that scales better than ad-hoc topics alone for policy engines. The claim about replacing Git commit SHAs with property values is false; Git object identity remains commit SHAs. The claim about disabling HTTPS for selected repositories only is false; HTTPS access is not toggled per repo via custom properties. Define allowed property values centrally, require properties on new repos where possible, and align security configurations and rulesets to those values.