
An organization requires approval for GitHub App installations. What does this control achieve?
Select an answer to reveal the explanation.
Short Explanation
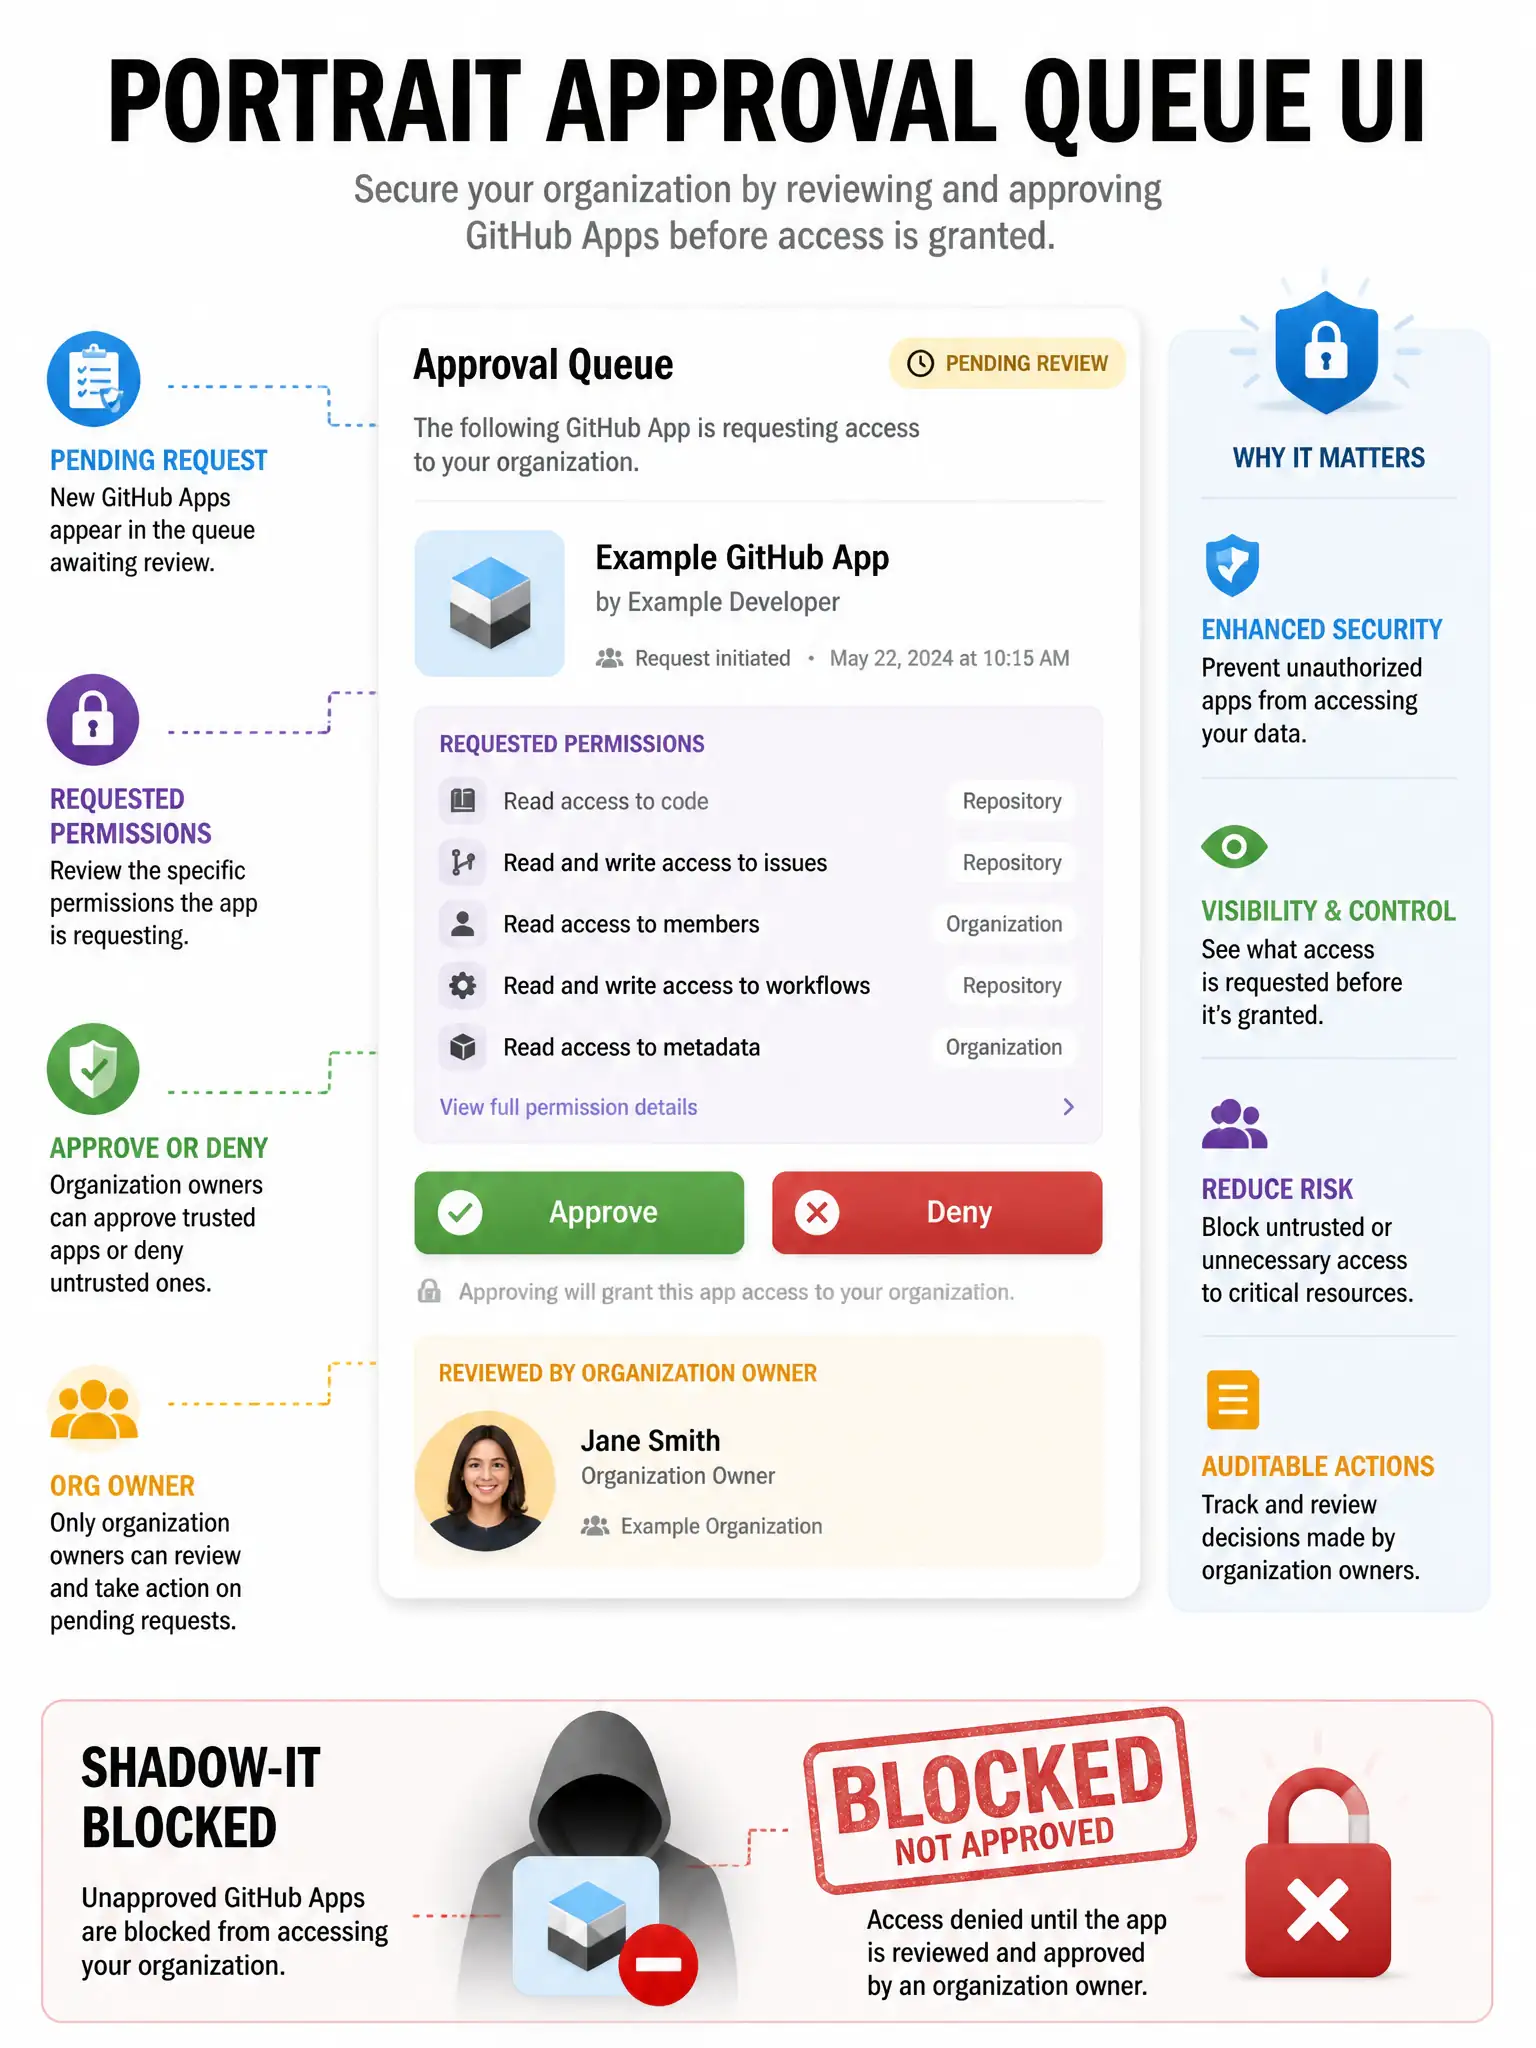
This control puts organization owners in the approval loop before a GitHub App can touch org resources. It stops unvetted integrations from grabbing private repo data, and it doesn't ban PATs or publish your code.
Full Explanation
The correct answer is that organization owners review and approve GitHub App installations before apps access organization resources. This reduces shadow IT integrations, stops random 'helpful' browser extensions and SaaS tools from wiring themselves into private repos, and enforces least privilege on app permissions. The claim that it prevents any use of personal access tokens permanently confuses App install policy with PAT policy. The claim that it automatically publishes private source code to Marketplace is false. The claim that it converts OAuth Apps into enterprise owners is false and insecure. Pair installation approval with IP allow lists, allowed app policies where applicable, and periodic access reviews of installed apps and their permission grants.